I came across this chart and I think this can be good base to restructure the current Malaysian OSINT resource startme page🤔. Keep your eyes peeled on the startme page update somewhere on this week👍
#malaysia#OSINT
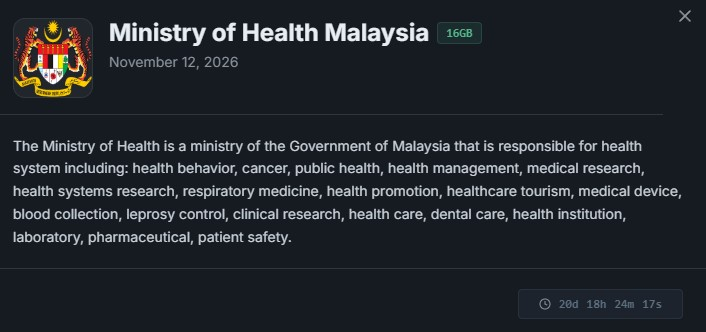
Panzer ransomware claims Malaysia's Ministry of Health (KKM). Unverified for now
The group listed KKM on its leak site on 12 Nov and claims 16 GB of data. Trackers say it plans to publish in 20 to 21 days.
No samples, no access method, no data types shared. KKM has not confirmed anything.
Panzer has been around since August with 49 listed victims in 22 countries, including a few in Thailand and Indonesia.
Whether it's real or not, expect KKM-themed phishing soon. "Check if your data leaked" links, fake notices, all that
https://t.co/SLQN4dfy1G
#InfoSec #CyberSecurity #Malaysia
🇲🇾 🚨 PANZER RANSOMWARE CLAIMS MALAYSIA'S MINISTRY OF HEALTH
The Panzer ransomware group has added the Ministry of Health Malaysia (KKM), the federal ministry that runs the country's public health system, to its leak site.
The listing gives no file count, data size or sample, and does not say what kind of records were taken.
The ministry has not commented on the claim. In June 2026, KKM said its official website had been hacked but that it saw no sign of sensitive data being leaked, and that patient records are not stored on the portal. It is not clear whether Panzer's claim is linked to that incident.
⚠️ Analyst Note:
Panzer is a ransomware-as-a-service operation first seen in August 2026. It runs double extortion and threatens to report victims to data-protection regulators. Treat this listing as an unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Ransomware #Panzer #Malaysia #KKM #Healthcare #Government #CyberSecurity
📢 Ransomware Alert: 🇲🇾
Ministry of Health, Malaysia (https://t.co/sr673hKGRp), a Malaysian government ministry healthcare system, has reportedly fallen victim to Panzer ransomware.
NB : The group intents to publish the data within 20-21 days.
🔍 Key Details:
🛡️ Threat Actor: Panzer
📅 Reported on: 12/11/2026
⚠️ Data Compromised: 16 GB
This is not a Batu Pahat story.
But it’s one small way we can help Malaysia fight phishing.
Submit here: https://t.co/OGmgWj59E3
Ps: all verified phishing findings will be shared with PhishHunt by Rectifyq and reported to MyCERT.
📰 NEWS
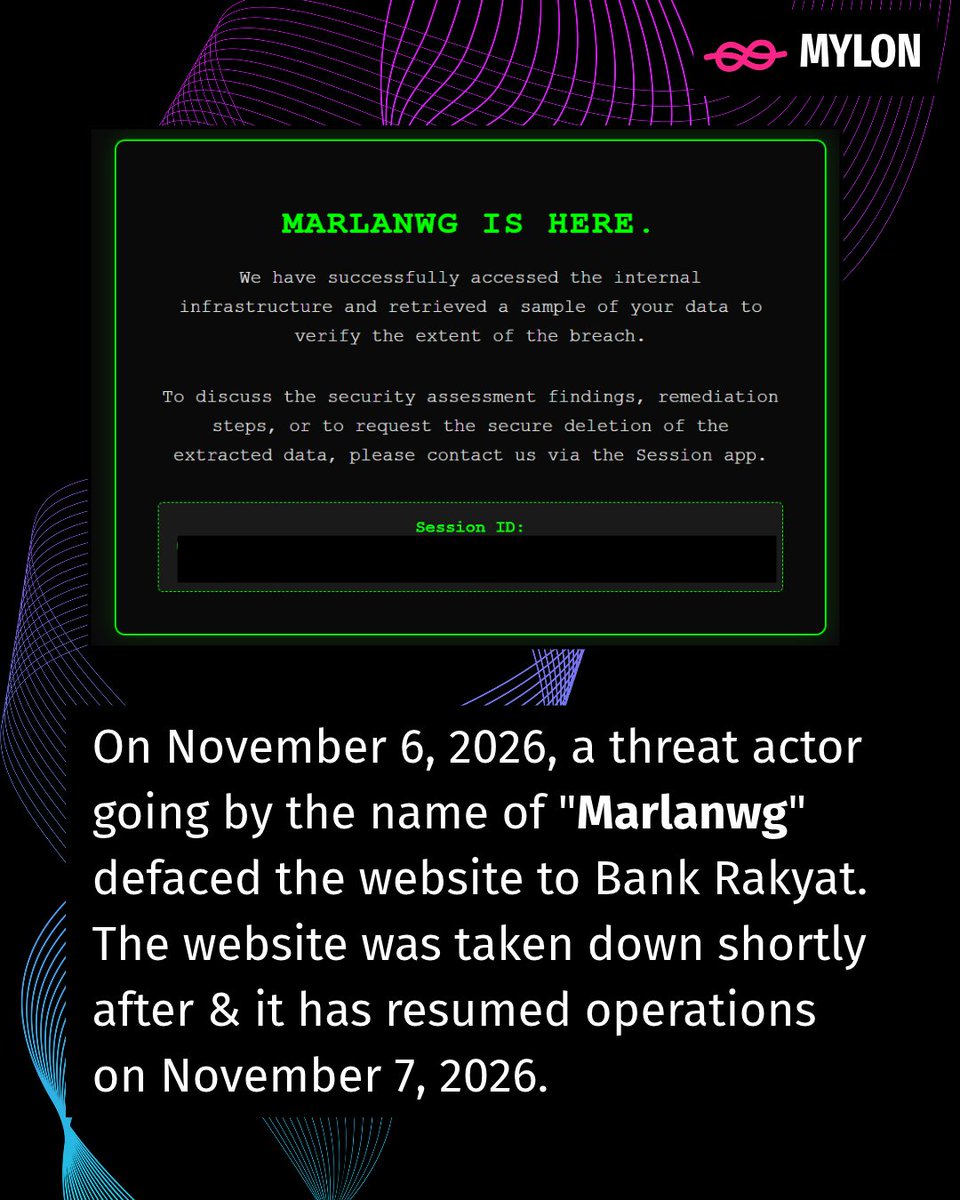
A threat actor going by the alias of "Marlanwg" defaced the website to Malaysian Bank, Bank Rakyat. The bank has resumed operations on 7/11/2026 and has claimed that all customer savings & personal information remain protected.
My TikTok FYP daily: pew pew map 💥 "Malaysia kena hack!!". But what can you actually do with it? Nothing 🙃
Sophisticated Threat Actors? Leave it to the gov & authorities. We do our part become cyber kebal, 5 mins a day 🐾 Free, no sign-up, BM + English
https://t.co/JDYWSuKjfo
⚠️ 🇲🇾 💻 PREVENTIVE ALERT: ALLEGED OFFER OF A CRITICAL 0-DAY VULNERABILITY AFFECTING MALAYSIAN CUSTOMS (ACTOR: MARLANWG)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: MARLANWG / DATE: OCTOBER 2026]
The centralized cyber-intelligence system has intercepted a commercial post on underground forums ("DarkForums") made by the user "marlanwg" (who has a history of 87 posts and 22 threads since October 2025). The post advertises the sale—for $1,500 USD—of a critical zero-day exploit (CVSS 9.8) that allegedly allows for unauthenticated remote PHP code execution (webshell) and direct access to production databases within the official Malaysian Customs portal (*.customs.gov.my).
It is strictly noted that the veracity of this compromise, the functional effectiveness of the exploit, and the authenticity of the exposed data have not been officially confirmed by Malaysian authorities or their technical teams. As this concerns alleged breaches and exploit offers posted on underground forums, the actual status of the infrastructure remains unconfirmed.
Threat Actor: marlanwg
Victim / Target: Malaysian Customs Production Portal
Sector: 🏛️ Government, Customs, Foreign Trade, and Critical Infrastructure in Malaysia 🇲🇾.
🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC / CSIRT / MALAYSIA CUSTOMS)
Forensic Audit of Files and AJAX Actions: Incident response teams at the affected entity must immediately review WordPress installation directories, search for suspicious or undocumented PHP files (especially in paths such as C:\REDACTED\), and audit AJAX actions logged in the `admin-ajax.php` file.
Perimeter Restriction and Monitoring: Block anonymous or suspicious HTTP requests directed at WordPress administrative endpoints and implement Web Application Firewall (WAF) solutions to mitigate command execution attempts.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly verify your security at: https://t.co/QZhWp0kFrO
Inquiries and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #Malaysia #Customs #ZeroDay #Webshell #RCE #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
🇲🇾 🚨 MALAYSIA: THREAT ACTOR SELLING WEBSHELL ACCESS AND DATABASE ALLEGEDLY FROM MALAYSIAN CUSTOMS
A threat actor on an underground forum is advertising webshell access and a database it says belong to Malaysian customs.
The listing claims:
* Webshell access to a customs-linked web server
* A Malaysian customs database
* Asking price of $1,500
No proof samples were included in the post. The claim has not been independently verified.
⚠️ Analyst Note:
A webshell on a government server can be used to steal data, plant malware or pivot into internal systems, so access sales like this are often resold to ransomware or espionage actors. The listing gives no sample, so the scope is unknown. The Royal Malaysian Customs Department has not confirmed an incident. Unverified threat-actor claim, NOT confirmation of a breach.
Source: this is for subscribers only. Subscribe: https://t.co/O5fslMgNk4
#DDW #DarkWeb #Malaysia #Customs #Government #InitialAccess #ThreatIntelligence
RAWSEC Minicon: this is quite a good outing, meet known people, have talked to cool peeps and listen to cool talk. Overall, good touching ground moment
Hacking news of the day
Binance confirms major hack, more than US$2.5bil frozen
Meanwhile in Malaysia ...
Kluang Municipal Council confirms its LED screens hacked, pornographic content displayed
https://t.co/c131vzuP4f
⚠️ 🇲🇾 🏛️ 🗄️ PREVENTIVE ALERT – ALLEGED COMPROMISE OF MALAYSIAN E-SYARIAH COURT SYSTEMS, STATE DATABASES, AND LATERAL GOVERNMENT NETWORK ACCESS (THREAT ACTOR: BYTETOBREACH)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: BYTETOBREACH / DATE: OCTOBER 28, 2026]
The centralized cyber-intelligence system has intercepted a high-impact post on underground forums, made on October 28, 2026, by the threat actor "bytetobreach." The report claims the compromise and exfiltration of source code from the entire Malaysian Sharia court ecosystem (e-Syariah), including regional databases for several states, such as Selangor, Penang, and Sarawak. Furthermore, the attacker asserts that they maintain persistent network access, noting that other Malaysian government agencies are reachable within the same network infrastructure (citing domains such as https://t.co/nYAW27eIiU, https://t.co/SADgD1MPzm, https://t.co/2QnSUrsEgF, https://t.co/V6fPsG0EVQ, https://t.co/sKkaTnxVsA, and https://t.co/xq32pKbPJN, among others). The post includes several screenshots as proof, along with data backups hosted on external platforms.
It is strictly noted that the veracity of this intrusion, the persistence of access to the judicial systems, and the overall authenticity of the exposed source code and databases have not been officially confirmed by Malaysia’s National Cyber Security Agency (NACSA/MyCERT) or the e-Syariah court administration. As this information originates from claims made by threat actors on underground forums, the actual status of the infrastructure remains unconfirmed. Threat Actor: bytetobreach
Primary Victim/Target: e-Syariah Court System (Syariah Judiciary Department Malaysia / Jabatan Kehakiman Syariah Malaysia) and regional judicial systems (Selangor, Penang, Sarawak) — 🇲🇾 Malaysia.
Stated Secondary Scope: Potential lateral network access to other Malaysian public agencies (https://t.co/nYAW27eIiU, https://t.co/SADgD1MPzm, https://t.co/2QnSUrsEgF, https://t.co/V6fPsG0EVQ, https://t.co/sKkaTnxVsA, https://t.co/xq32pKbPJN, etc.).
Sector: 🏛️ Government Public Sector, Judiciary, Administration of Justice, and State Bodies.
Publication Date: October 28, 2026.
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / NACSA MALAYSIA)
Perimeter Isolation and Disconnection of e-Syariah Gateways: Malaysian government incident response teams must immediately isolate the e-Syariah system’s servers and web portals to sever any persistent access channels or command-and-control (C2) links maintained by the attacker.
Audit of Lateral Movement within Government Networks: Urgently review authentication logs and network traffic between judicial servers and the aforementioned ministerial domains (https://t.co/nYAW27eIiU, https://t.co/SADgD1MPzm, etc.) to rule out privilege escalation or cross-system persistence.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Malaysia #eSyariah #Judiciary #GovSec #CyberAttack #DataLeak #DataBreach #BreachAlert #SourceCodeLeak #DatabaseLeak #Bytetobreach #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
🇲🇾 🚨 MALAYSIA: LAND PUBLIC TRANSPORT AGENCY (APAD) SYSTEMS ALLEGEDLY BREACHED, EMPLOYEE MYKAD DATA CLAIMED
A threat actor on an underground forum claims to have breached the digital systems and official email of the Malaysian Land Public Transport Agency (APAD), the government agency under the Ministry of Transport that regulates land public transport.
The actor claims to have taken control of APAD servers and extracted government documents, including:
* Employee schedules and personal data, including MyKad (national identity card) numbers
* Insurance documents and internal maintenance records
* Confidential government correspondence on competency development and administrative reforms
* Employee data and contracts with major companies (Toshiba is named)
The actor also claims the systems were "wiped" and threatens to publish the data if unspecified demands are not met. A sample is attached to the post.
The claim has not been independently verified.
⚠️ Analyst Note:
If authentic, MyKad numbers paired with employee records are a strong enabler of identity fraud, SIM-swap and targeted phishing against Malaysian civil servants, and contractor documents could be abused for supply-chain lures. The "breached and wiped" claim is unproven. Unverified threat-actor claim, NOT confirmation of a compromise of APAD systems.
Source: this is for subscribers only. Subscribe: https://t.co/O5fslMgNk4
#DDW #DarkWeb #Malaysia #DataBreach #Government #Extortion #ThreatIntelligence
A Malaysian who found #Tuju to be broken upon release decided to make a #navigation app of his own called ‘#Lapan’, and it appears to be more functional.
https://t.co/NSGUIBApSw