Fake Base Transceiver Station atau Fake BTS adalah sebuah peranti yang menyamar sebagai stesen pangkalan telefon bimbit sebenar. Di Malaysia, ia selalunya bertujuan untuk menyebarkan SMS phishing. Lagi best, nama penghantar SMS pun boleh di spoof!
Sekiranya kerajaan Malaysia 🇲🇾 membuat keputusan untuk menyekat penggunaan Waze (sekatan DNS), apakah tindakan yang akan anda ambil, dan apakah aplikasi/langkah alternatif pilihan anda?
Oh, I was fully aware of the bias and actual context, but triggering RHB is practically my favorite hobby. @BNM_official please investigate @RHBGroup 😂
infostealer malware has hit staff at half of malaysia's 10 biggest banks
infected staff machines per hudson rock: RHB 106, maybank 89, CIMB 41, affin 36, bank rakyat 36, and bank negara itself 24
public bank, hong leong, ambank and alliance: 0
"...However, Nazir's involvement with the film did not stop once the cameras wrapped.
Captivated by the project's powerful narrative scope, he said he asked to join the team as a co-producer of the movie..."
Prominent corporate figure Tan Sri Nazir Razak has taken on a deeply personal role on the silver screen, portraying his late father, Malaysia’s second Prime Minister Tun Abdul Razak Hussein, in the feature film "Kudrat 1968: High Council."
https://t.co/A6p8wu1A8g
PHP Attacks Update: As others, we have been observing a lot of AI slop PHP attempts against our honeypot sensors the last week, but so far no confirmed exploitation.
We have refrained from CVE-2026-109618/619 tagging in scans, due to lack of reliable, safe large scale methods.
Another day, another phishing attempt.
My late father lost a lot of money to scammers. I've seen the damage these people can do, and I absolutely despise them.
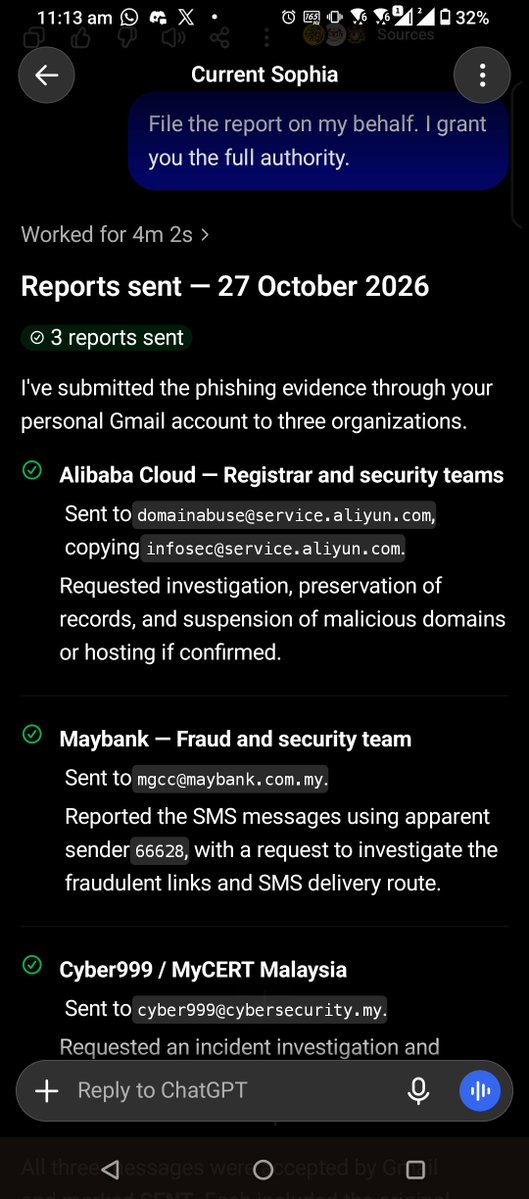
Today, instead of simply deleting another suspicious SMS, I decided to try a little experiment.
What could ChatGPT find out about these scammers? More importantly, could it actually do something about them?
Within minutes, it investigated the suspicious domains, uncovered evidence suggesting a coordinated phishing operation, and submitted reports to the domain registrar, Maybank, and CyberSecurity Malaysia.
All with very little effort on my part.
Whether the reports lead to any action remains to be seen. But something that once required considerable technical knowledge is now accessible to practically anyone.
So here's my appeal - if you receive a phishing message, don't just delete it. Don't click the links either. Use AI to help gather evidence and report it to the proper authorities.
Imagine if everyone started doing this.
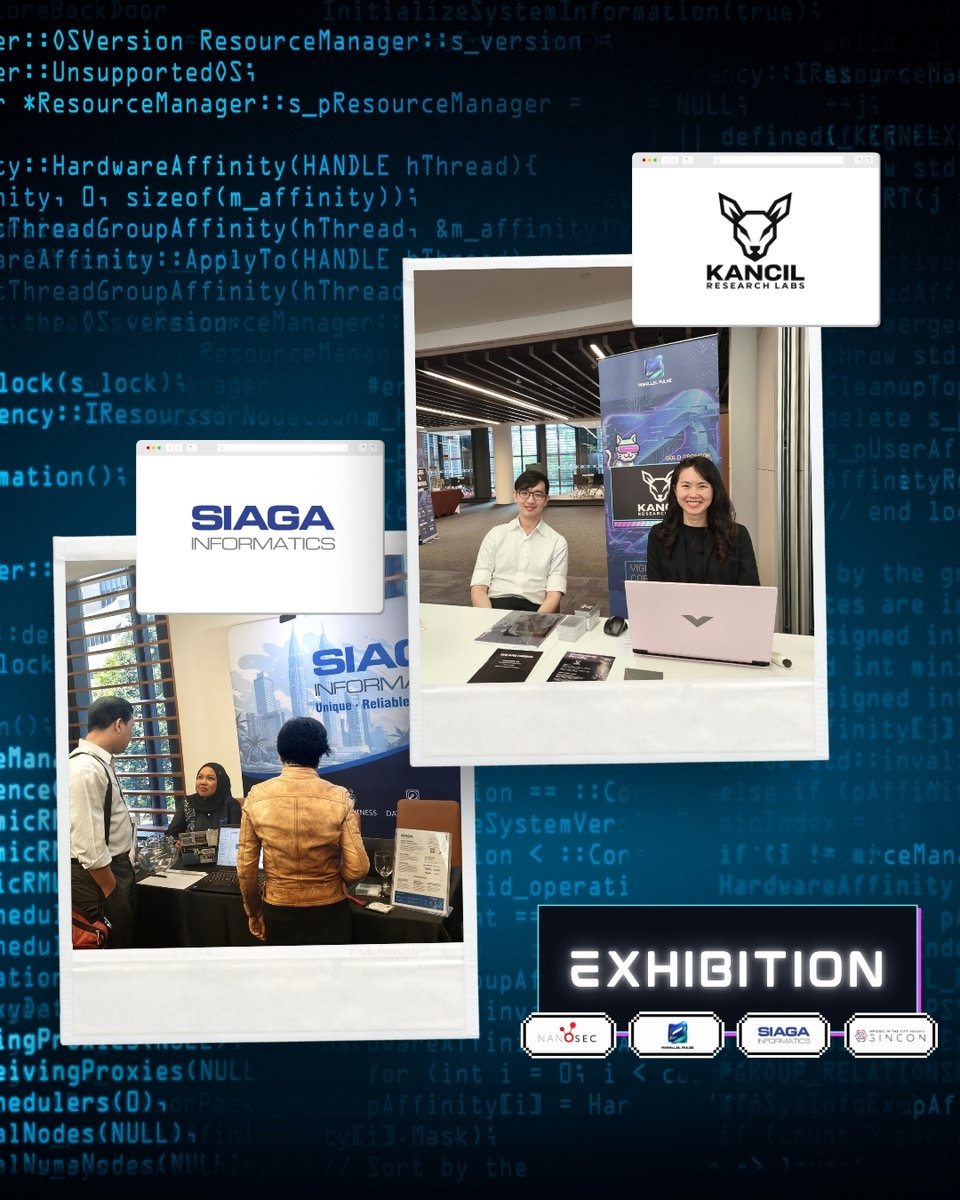
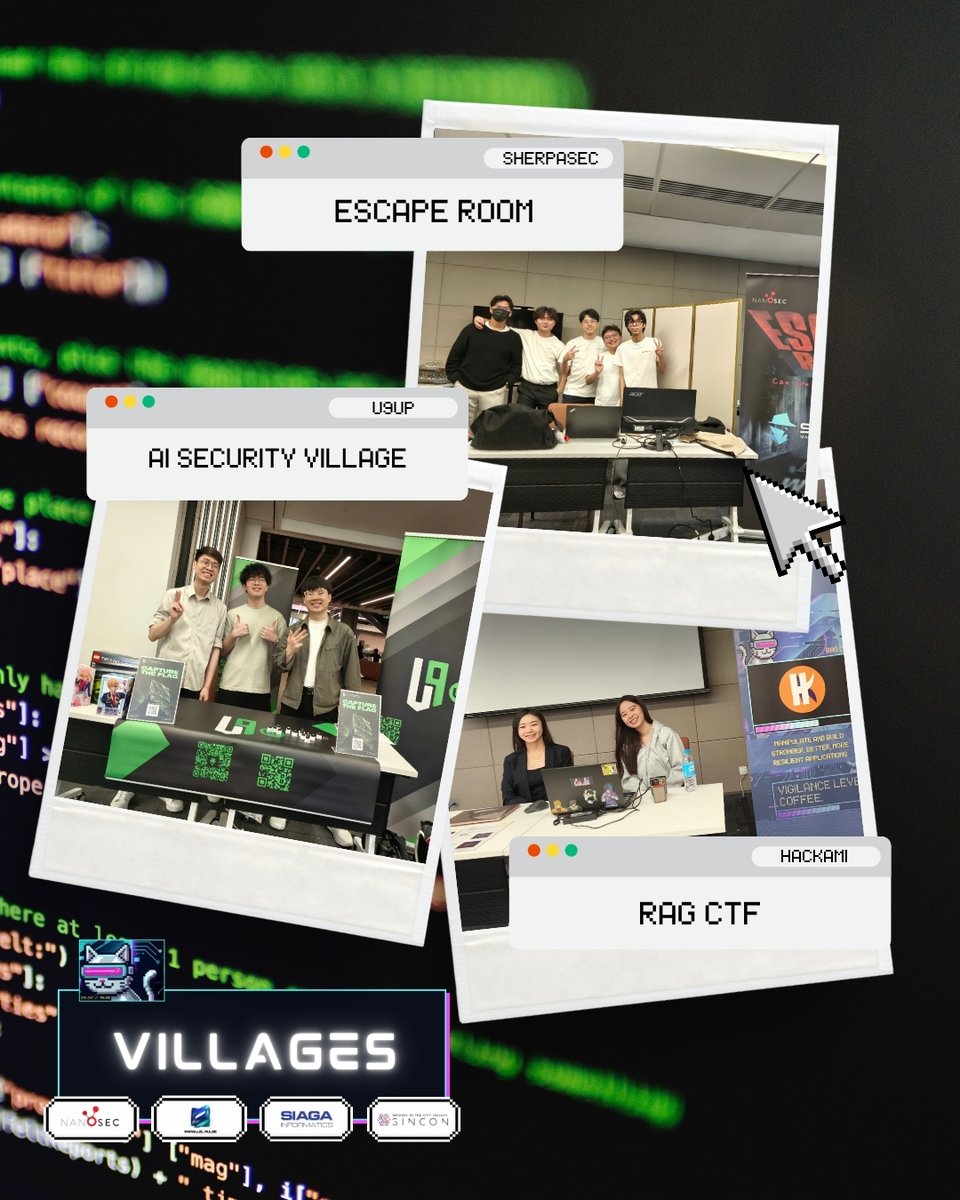
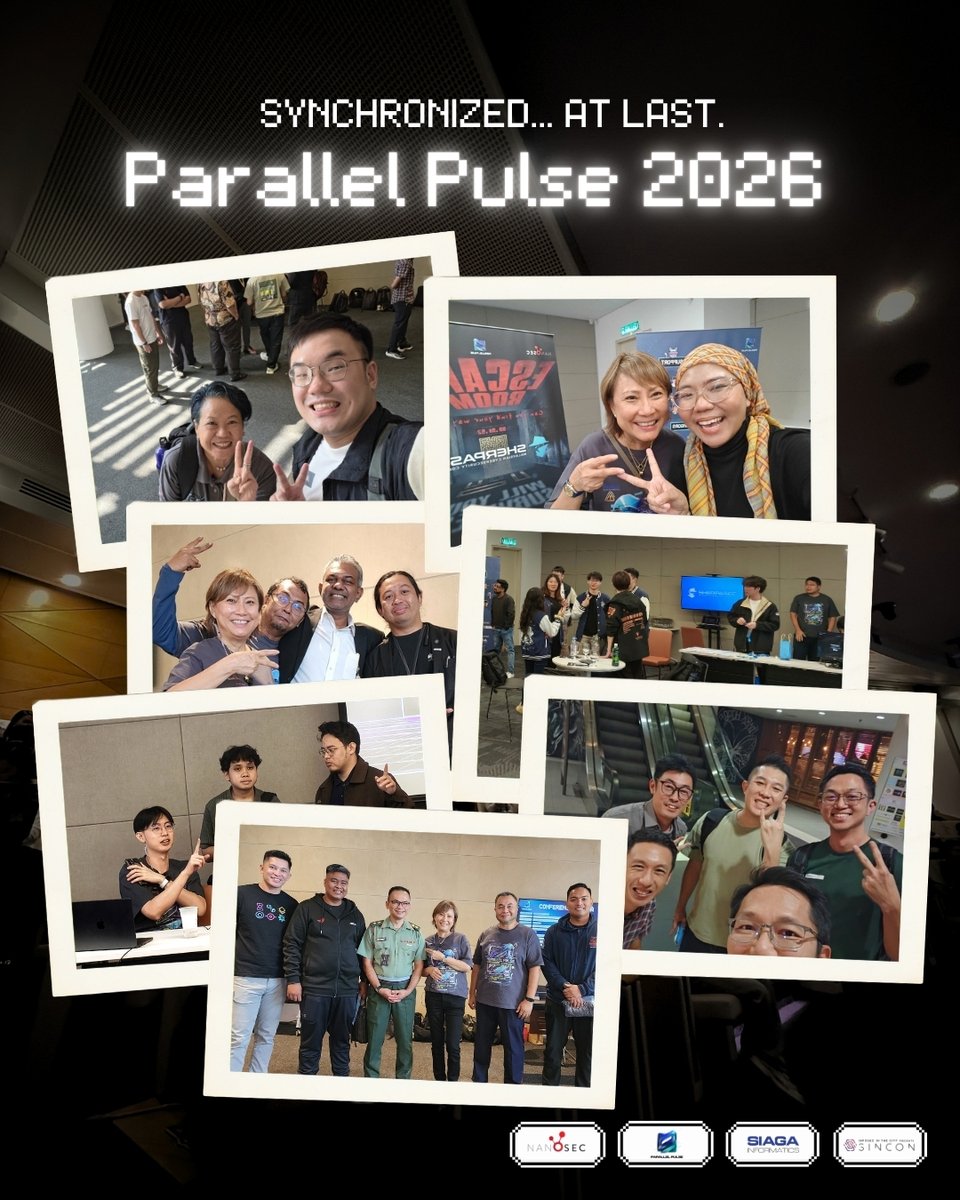
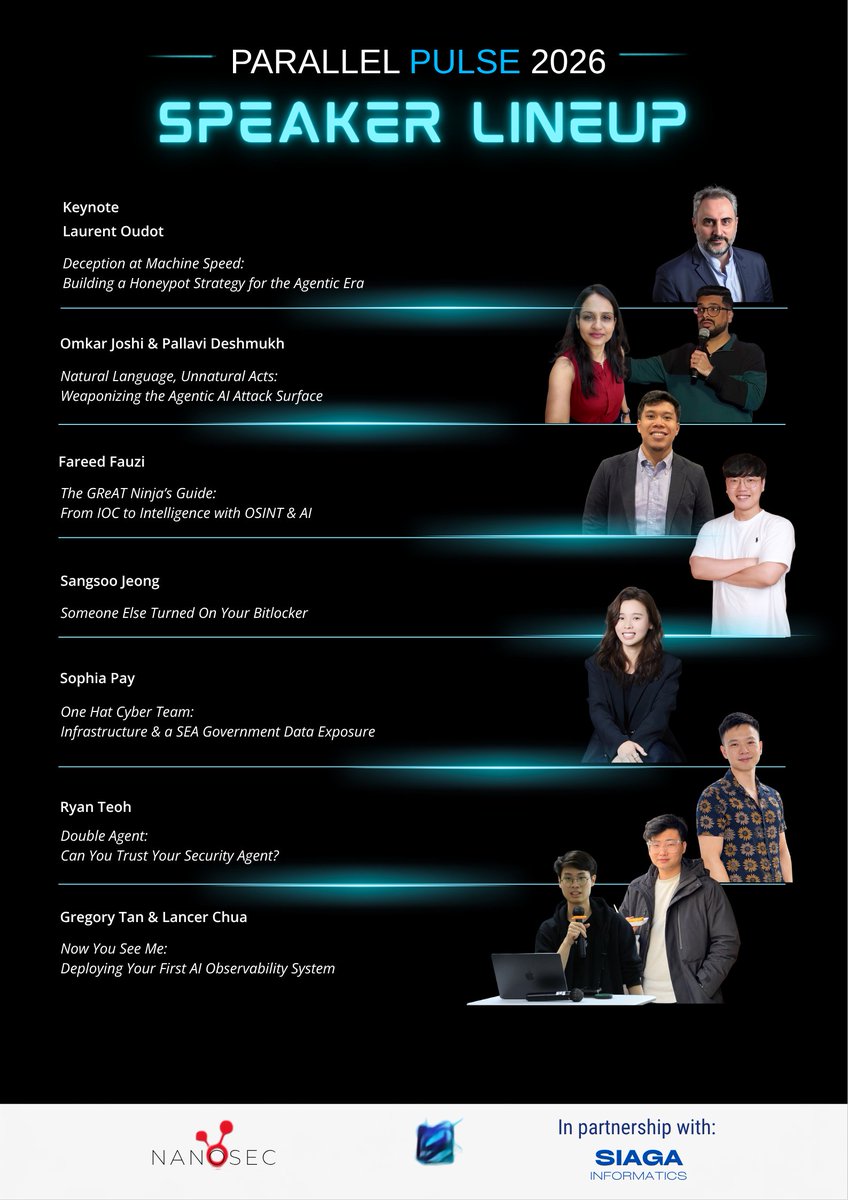
Parallel Pulse 2026, wrapped!
After months of planning, conversations, ideas and work behind the scenes, Parallel Pulse 2026 came together on 28 September at AICB, Kuala Lumpur.
And what a day it was.
We started with an idea. The community made it real.
Until the next one ⚡
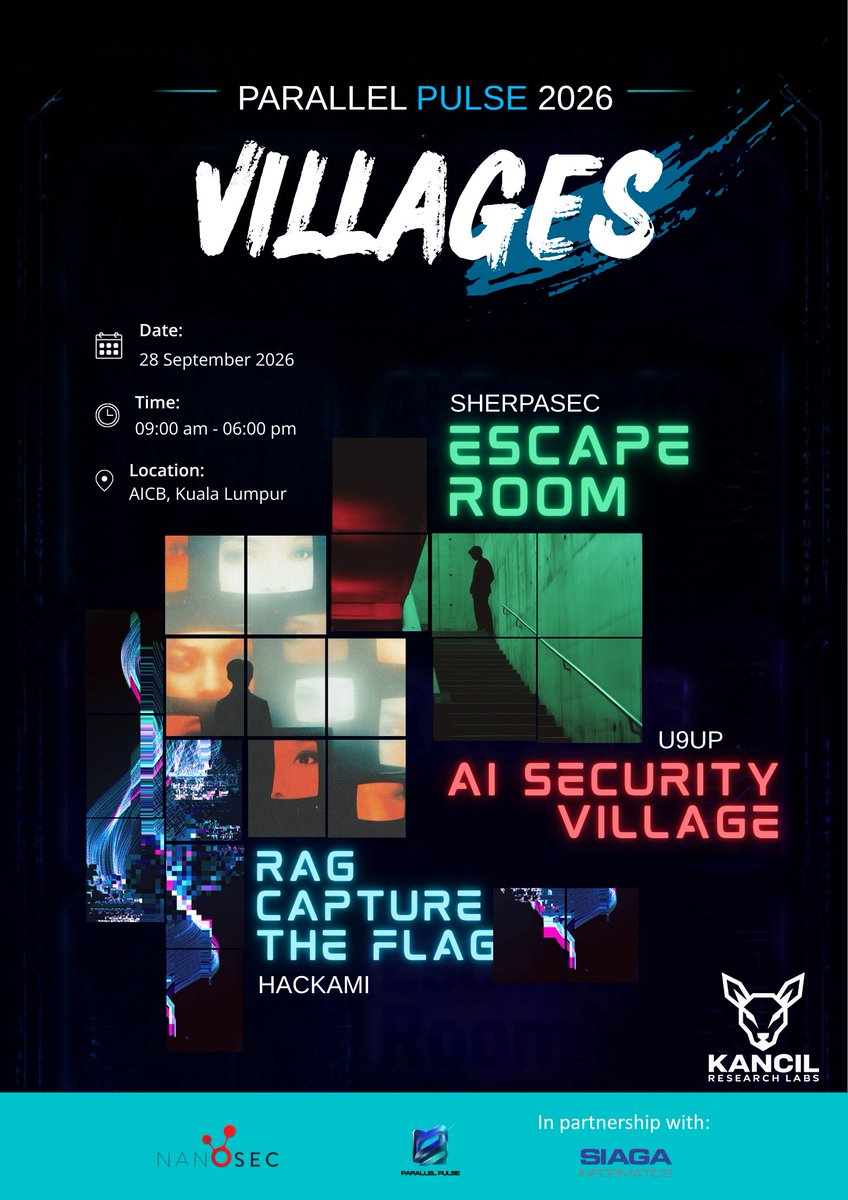
In 𝗹𝗲𝘀𝘀 𝘁𝗵𝗮𝗻 𝟮𝟰 𝗵𝗼𝘂𝗿𝘀, #ParallelPulse2026 registration will CLOSE!
Get your tickets: https://t.co/WcRGzcBjiX…
Regular: RM188
Students: RM88
📅 28th September 2026
⏰ 9am - 6pm
📍 AICB, Kuala Lumpur
See you there!
#CyberSecurity#NanoSec#SIAGAInformatics
✍️ An Awesome Series of Writeups on Anti-DDoS research
Part 1: https://t.co/Jh9gpouAKy
Part 2: https://t.co/rbTf7TvsVh
Part 3: https://t.co/KFeYhJnXT0
Part 4: https://t.co/79FozOsmRw
Author: @cocomelonckz
Threat actor SilverFox is hiding malware inside ISO/IMG files and compressed into zip file. When opened, Windows auto-mounts the image as a virtual CD-ROM, bypassing MotW/perimeter controls to deliver the malicious payloads