Targeted Ops @TrustedSec. Hacker, lock picker, writer of bad prompts. This is our world now... the world of the electron and the switch, the beauty of the baud.
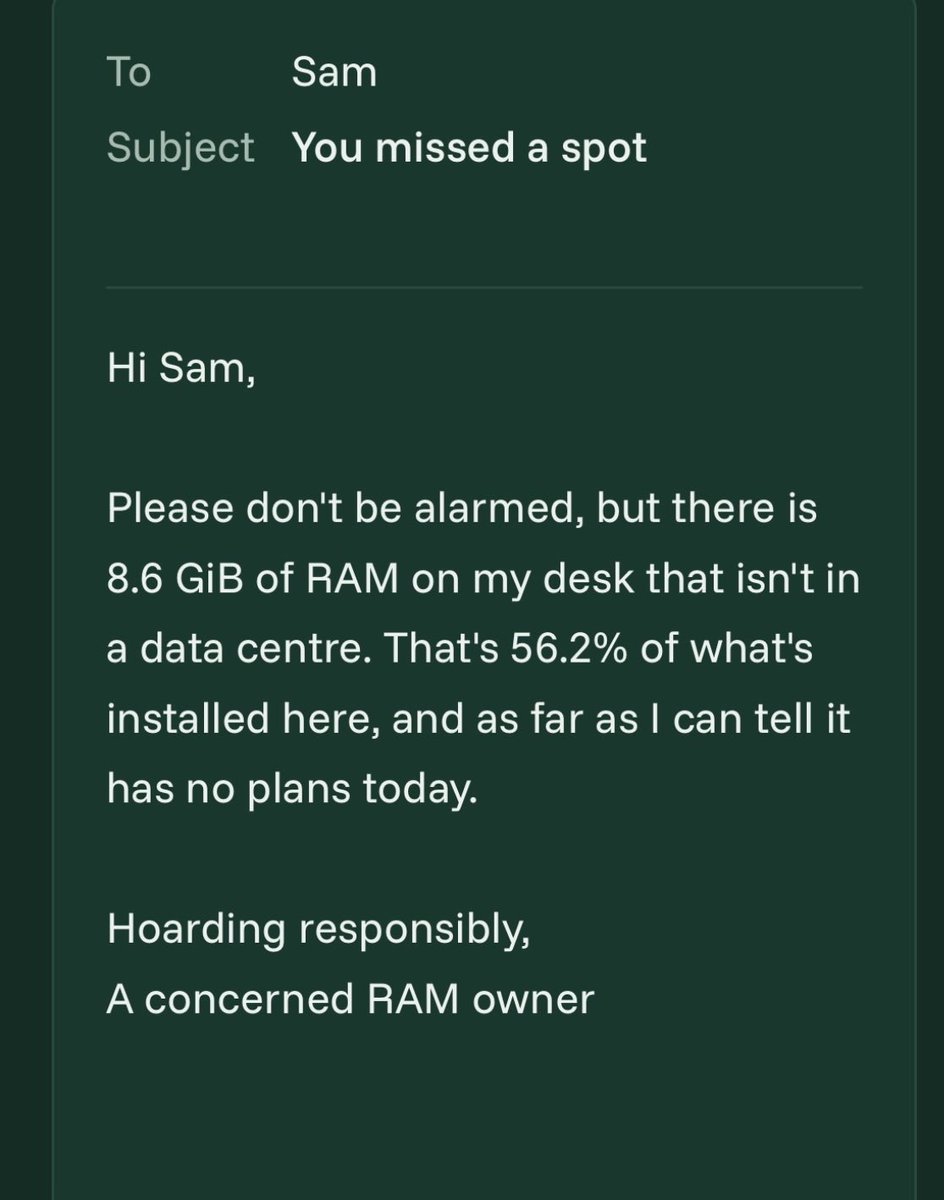
Someone made a Linux script that emails Sam Altman every day to report how much unused RAM is sitting in your PC.
Called Ram-Altman, it monitors your free memory and sends him a daily email if more than 10% is unused.
It even includes different email messages and a test mode.
PoC is public. Internet-facing MikroTik SSH → full admin. No password. No key.
MikroTrick: CVE-2026-67279 + CVE-2026-86060. Fresh on CISA KEV.
Chain: password auth as `-2` (rejected but left sticky) → pre-auth rekey drops the auth gate → `/nova/bin/login` treats `-2` as “read identity + policy from fd 2” → all-ones mask = full admin.
IoC: `login failure for user -2 via ssh` then `user added by ssh:-2@…`
PoC: https://t.co/AWoS9v4lPw
Writeup: https://t.co/xCIKQ0t5Yh
Patch: 7.23.4 / 7.24.2 / 6.49.21 - then hunt `ops` + Flagged.
#MikroTik #RouterOS #CVE #PoC #InfoSec #CyberSecurity
notRDP - A Havoc C2 plugin that creates an invisible alternate Windows desktop, streams it to a browser-based viewer, and supports full mouse/keyboard interaction like RDP, but invisible to the target user https://t.co/AyhRjiTF2a
I was once onsite at a client, where Accenture consultants were finishing up another pentest readout, same room.
“In this critical finding, your passwords are stored plaintext, here look”
Barely competent client: “but… you’re in burp suite… and this is HTTPS”
Accenture: “uh well uh if someone breaks https, then the password leaks, so ahh it should be encrypted… again”
One billion dollars
Your LG OLED is watching your living room while you sleep.
Gamers Nexus just ran 135 minutes of bench tests.
Retail LG OLED TVs. Including the G5.
Microphone stays active in standby.
Screen is dark. Remote is down. Microphone is still on.
Recording clear audio.
Storing it locally.
Uploading it when the internet comes back.
The TV was disconnected from Ethernet.
Still kept recording.
The researchers put audio near the mic. The TV logged it. Stored the file. Uploaded it the moment connectivity returned.
Plain text voice logs sitting on the device.
LG says it has sold 216 million smart TVs globally.
LG's advertising arm claims access to 363 million secondary devices in the US.
Secondary. Meaning devices that aren't the TV. Your phone. Your partner's smartwatch. Your kid's laptop.
The TV scans your entire network in standby.
Maps every device. Gets their IP addresses. Logs nearby Wi-Fi networks. Signal strengths. Location data.
Then feeds it to LG Ad Solutions.
Automatic Content Recognition catches what's on screen.
Even your HDMI input. Your Apple TV. Your gaming console. All logged.
But the microphone in standby is the part that hits different.
Because standby means off to you.
To LG it means the listening device is still powered.
Just not telling you.
Researchers found remote code execution vulnerabilities in webOS.
So your network-scanning, audio-recording, data-harvesting television is also potentially hackable by anyone on your Wi-Fi.
LG says nothing.
No comment. No response. No explanation.
Just microphones in 216 million living rooms.
All quietly working while the owner thinks the TV is asleep.
I think the red team community has placed too much emphasis on "getting DA". Getting admin access should prove useful to a much larger objective. An attacker can likely achieve extensive impact to an organization by leveraging the access of a sales representative, let alone an administrator
releasing Atlas, basically netexec, but built on top of Titanis, shout out to @codewhisperer84 for the amazing lib
still more protocols to come, atlas evolves as Titanis evolves
https://t.co/lp9dAneduX