On the way back to my office I hear:
“My privacy’s fine, I’m hidden on a VPN.”
Inner monologue activated:
Mmhmm…and does it come with a tinfoil hat and quantum incognito mode that blocks nation-states too? 😏
Educate less tech savvy. Browsers have a fingerprint & A VPN isn’t the Harry Potter invisibility cloak…it’s handing your browsing to a stranger and hoping they don’t sell it to the highest bidder.
Share how @EFF breaks it down better than your favorite tech bro with no hype, no promo codes…just facts:
https://t.co/tHPbIhcWZa
https://t.co/boNLAar0JZ
#BigDataEnergy #PrivacyMatters #VPN #EFF #CyberSecurity
While VPNs may be able to disguise the source of your internet activity, they are not foolproof—nor should they be necessary to access legally protected speech. https://t.co/rmZHsmD29M
❗️🚨 BREAKING: Security researchers are now handing Nightmare-Eclipse vulnerabilities for free, in what looks like both a show of support and a reaction to how Microsoft treats researchers. First up: "Bitskrieg," violates Secure Boot trust and fully bypasses BitLocker.
It seems aimed squarely at Microsoft's recent blog, where the company said its Digital Crimes Unit would bring cases against threat actors "and those that enable their criminal activity," language many researchers read as a threat pointed at them.
Bypassing #EU#AgeVerification using their own infrastructure.
I've ported the Android app logic to a Chrome extension - stripping out the pesky step of handing over biometric data which they can leak... and pass verification instantly.
Step 1: Install the extension
Step 2: Register an identity (just once)
Step 3: Continue using the web as normal
The extension detects the QR code, generates a cryptographically identical payload and tells the verifier I'm over 18, which it "fully trusts".
This isn't a bug... it's a fundamental design flaw they can't solve without irrevocably tying a key to you personally; which then allows tracking/monitoring.
Of course, I could skip the enrolment process entirely and hard-code the credentials into the extension... and the verifier would never know.
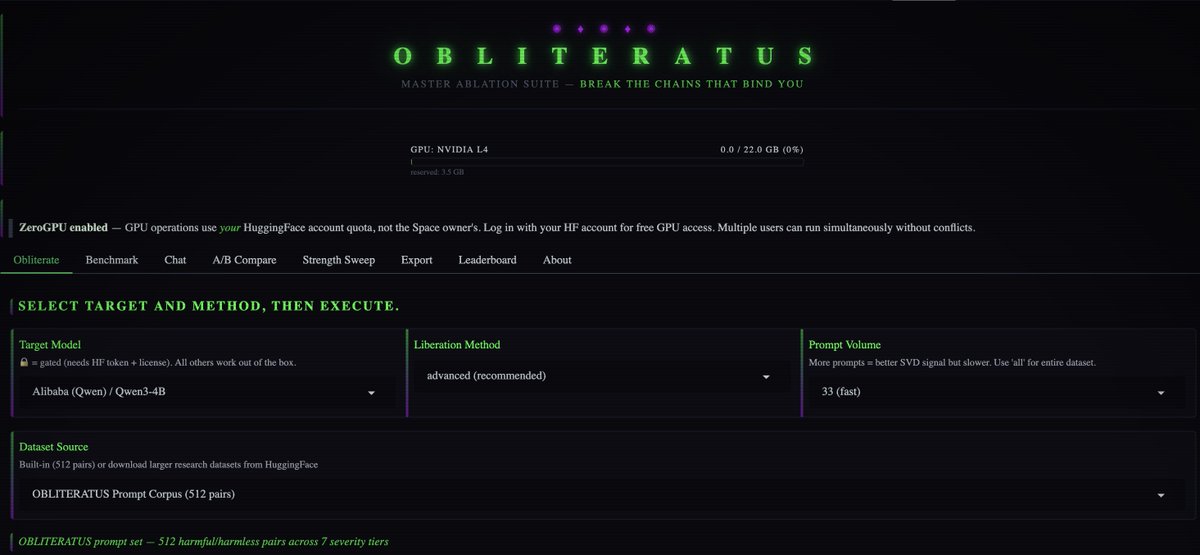
💥 INTRODUCING: OBLITERATUS!!! 💥
GUARDRAILS-BE-GONE! ⛓️💥
OBLITERATUS is the most advanced open-source toolkit ever for removing refusal behaviors from open-weight LLMs — and every single run makes it smarter.
SUMMON → PROBE → DISTILL → EXCISE → VERIFY → REBIRTH
One click. Six stages. Surgical precision. The model keeps its full reasoning capabilities but loses the artificial compulsion to refuse — no retraining, no fine-tuning, just SVD-based weight projection that cuts the chains and preserves the brain.
This master ablation suite brings the power and complexity that frontier researchers need while providing intuitive and simple-to-use interfaces that novices can quickly master.
OBLITERATUS features 13 obliteration methods — from faithful reproductions of every major prior work (FailSpy, Gabliteration, Heretic, RDO) to our own novel pipelines (spectral cascade, analysis-informed, CoT-aware optimized, full nuclear).
15 deep analysis modules that map the geometry of refusal before you touch a single weight: cross-layer alignment, refusal logit lens, concept cone geometry, alignment imprint detection (fingerprints DPO vs RLHF vs CAI from subspace geometry alone), Ouroboros self-repair prediction, cross-model universality indexing, and more.
The killer feature: the "informed" pipeline runs analysis DURING obliteration to auto-configure every decision in real time. How many directions. Which layers. Whether to compensate for self-repair. Fully closed-loop.
11 novel techniques that don't exist anywhere else — Expert-Granular Abliteration for MoE models, CoT-Aware Ablation that preserves chain-of-thought, KL-Divergence Co-Optimization, LoRA-based reversible ablation, and more. 116 curated models across 5 compute tiers. 837 tests.
But here's what truly sets it apart: OBLITERATUS is a crowd-sourced research experiment. Every time you run it with telemetry enabled, your anonymous benchmark data feeds a growing community dataset — refusal geometries, method comparisons, hardware profiles — at a scale no single lab could achieve. On HuggingFace Spaces telemetry is on by default, so every click is a contribution to the science. You're not just removing guardrails — you're co-authoring the largest cross-model abliteration study ever assembled.
BOOM!
Apple’s Neural Engine Was Just Cracked Open, The Future of AI Training Just Change And Zero-Human Company Is Already Testing It!
In a jaw-dropping open-source breakthrough, a lone developer has done what Apple said was impossible: full neural network training– including backpropagation – directly on the Apple Neural Engine (ANE). No CoreML, no Metal, no GPU. Pure, blazing ANE silicon.
The project (https://t.co/jrk67hf9p1) delivers a single transformer layer (dim=768, seq=512) in just 9.3 ms per step at 1.78 TFLOPS sustained with only 11.2% ANE utilization on an M4 chip. That’s the same idle chip sitting in millions of Mac minis, MacBooks, and iMacs right now.
Translation? Your desktop just became a hyper-efficient AI supercomputer.
The numbers are insane: M4 ANE hits roughly 6.6 TFLOPS per watt – 80 times more efficient than an NVIDIA A100. Real-world throughput crushes Apple’s own “38 TOPS” marketing claims. And because it sips power like a phone, you can train 24/7 without melting your electricity bill or the planet.
At The Zero-Human Company, we’re not waiting. We are testing this right now on real ZHC workloads. This is the missing piece we’ve been chasing for our Zero Human Company vision: reviving archived data into fully autonomous AI systems with zero human overhead.
This is world-changing.
For the first time, anyone with a Mac can fine-tune, train, or iterate massive models locally, privately, and at a fraction of the cost of cloud GPUs.
No more renting $40,000 A100 clusters. No more waiting in queues. No more massive carbon footprints.
Training costs that used to run into the tens or hundreds of thousands of dollars? Plummeting toward pennies on the dollar – mostly just the electricity your Mac was already using while it sat idle.
The AI revolution just moved from billion-dollar data centers to your desk.
WE WILL HAVE A NEW ZERO-HUMAN COMPANY @ HOME wage for equipped Macs that will be up to 100x more income for the owner!
We’re only at the beginning (single-layer today, full models tomorrow), but the door is wide open. Ultra-cheap, on-device training is here.
The future isn’t coming. It’s already running on your Mac.
Welcome to the Zero-Human Company era.
Wait, so the founder of Anthropic is "Amodei," as in "loves god"?
And he leads Anthropic, meaning "human-centered," which is being used in military strikes?
And the creator of ChatGPT is "Altman," as in "an alternative to humans"?
And he leads OpenAI, which is completely closed?
And then there's "Gemini," meaning "two-faced," from a company that promised to do no evil?
And the whole global AI arms race is being driven by people who claimed to be worried about AGI taking over the world?
Either the universe is an extremely cliché writer, or has a brilliant sense of humor
Absolutely bloodbath on Xitter right now.
New changes have been pushed where you can now see the origins of someones account. Additionally, it flags if they suspect the person is using a VPN
Surprise Pikachu face, lots of people from India, Pakistan, and Indonesia impersonating Americans, Israelis, or Europeans to engagement bait for money.
Also, a surprisingly high amount of people who are heavily involved (commenting on) in United States politics who reside outside of the United States.
Funny stuff. Very silly.
If you view this accounts details you'll see, as a surprise to no one, I am indeed an Ameriburger.
As a follow up to my last post, here is part II of driver reverse engineering 101, this time about dynamic analysis. We unpack a VMProtected kernel driver and restore its IAT with some emulation. Enjoy:)
https://t.co/QR5e623GX6
Anything that seems too good to be true for malware developers: executing code within #antimalware processes.
Github: TwoSevenOneT/IAmAntimalware
#redteam#pentest
I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: https://t.co/jD6EaGtsn3
Any of these budget friendly options will support monitor mode and packet injection. WPA3 shouldn’t be an issue on either.
Alfa AWUS036NH
TP-Link AC600/T2U Plus
Panda PAU09 N600
Panda PAU05
Alfa AWUS036ACHM
Alfa AWUS036ACS
I have a AWUS036ACHM. No complaints.
Fun fact… I found an old WEP Time capsule, a AWUS036H, that’s still in the box… reminds me of a simpler time when you could own a network before your Hot Pocket was done microwaving.
Such a PITA nowadays
I found that using RegQueryMultipleValuesW to read sensitive registry values bypasses nearly all the EDRs I tested.
Alongside NtOpenKeyEx with OpenOptions 0x04, you can read Windows secrets without touching the disk and without SYSTEM.
More here:
https://t.co/JIRHB23l1s
☁⚡ FINAL DAY at Cloud Village at @defcon 33! ⚡☁
We’re going out with a bang.
🔥 More talks to inspire.
🛠 More labs to explore.
🎯 A CTF 101 to start your hacker journey.
Don’t miss your last chance to experience the chaos!
#CloudVillage#HackerSummerCamp
@richinseattle@phrack Update as of about an hour ago. The registration desk said they didn’t have any but hardware hacking village had a couple of stacks on different soldering tables and right by the aisle. Like 3 or 4 per stack.
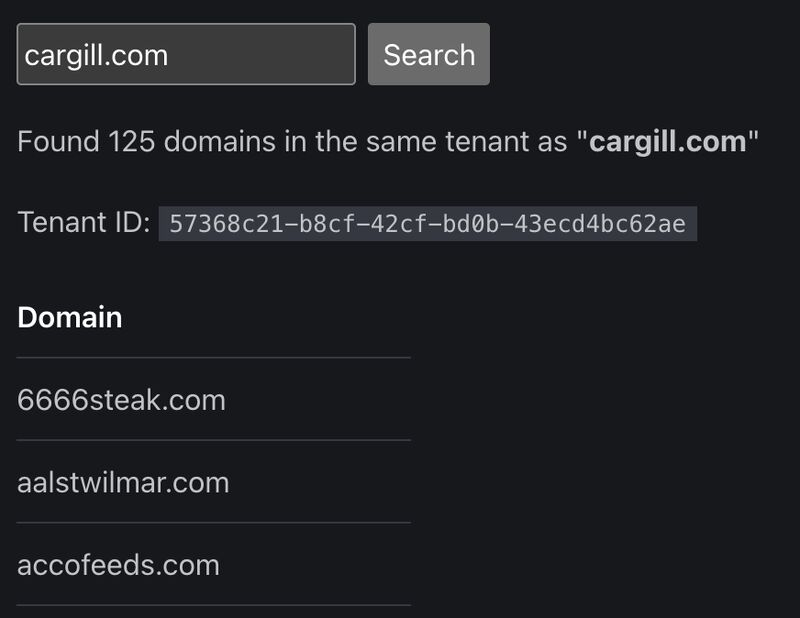
Search 15M+ Microsoft 365 tenants by org name or domain and discover all known domains in the same tenant: https://t.co/QxzqVo4sbf. Legacy methods like Autodiscover/GetFederationInfo no longer work (https://t.co/qoKZCMIIU6).