A password reset won't get you out of this one.
Meet TrustSink: the technique that turns a rogue external MFA provider into a persistent credential trap inside Microsoft Entra ID.
Privileged attackers could register a lookalike authentication provider and insert a pixel-accurate password page into the legitimate sign-in flow.
The page captures the password in plaintext while a valid signed token completes the login, no errors, no red flags.
A rogue provider remains in the flow and captures the next password, even after you reset it.
Full research, detection steps, and mitigation: https://t.co/9tlOuqpZky
30% of your data is ROT: redundant, obsolete, or trivial.
That's not just wasted storage. It's a wider blast radius, slower AI adoption, and data you're legally on the hook for.
Introducing Varonis Data Lifecycle Management, helping you manage data from creation to deletion automatically.
Varonis DLM finds every duplicate, stale file, and expired record across your data estate, helping you:
✔ Cut storage costs
✔ Reduce your blast radius
✔ Automate compliance and retention
✔ Feed AI only the data that deserves to exist
Read more about Varonis DLM here: https://t.co/J3ZhHntN9F
Machine identities now outnumber human ones by more than 80 to 1.
That number includes service accounts, API keys, and a growing population of AI agents, each with its own set of permissions, and most with far more access than they actually need.
Here's the problem: identity security programs were built around people. Reviews, access certifications, and offboarding. all designed for a human on the other end of the account.
Agents don't fit that model. They're provisioned quickly, rarely reviewed, and often forgotten the moment a project ends.
The result is a form of exposure that most security teams can't yet see: a sprawling, unmanaged layer of non-human identities sitting atop sensitive data.
This is exactly the gap Varonis Atlas was built to close. Atlas continuously discovers every AI system in your environment, whether it's agents, LLMs, embedded AI, or shadow AI, and evaluates which data each can actually access.
You can't govern what you can't see.
That ratio isn't going to shrink. The question is: does your team know what your 80 are doing right now?
Our Snowflake partnership just got an upgrade. ❄️
We're proud to announce that Varonis has achieved Premier Partner status in the @SPN_Partners Network and is now available on the Snowflake Marketplace.
AI agents, copilots, and LLMs now read, write, and act on data in Snowflake at machine speed. Varonis gives security teams visibility into where sensitive data lives, who can access it, and how it's used, so they can move fast with AI without losing control of their data.
We're excited to continue helping Snowflake users safely leverage AI.
Learn more about our partnership here: https://t.co/23ZHU1MiKz
Your AI agent isn't malicious. It's just not being watched.
Most agents are given access based on what they could need, not what they actually use. Over time, that gap becomes the blast radius.
Recognizing the signs early can help protect your organization from trouble.
Here are three things to be on the lookout for👇
AI assistants introduce new security considerations for enterprise teams.
This security analysis by @varonis examines how indirect prompt attacks can affect AI-powered workplace tools and what organizations can do to reduce the risk:
Stealing 10 terabytes used to be the attacker's problem too.
Too much data to make sense of AI removed that bottleneck. Old stolen data is being reprocessed for new ways to monetise it.The breach you had two years ago isn't finished.
Simon Biggs @varonis
Not every security problem involving AI is an AI security problem.
Some attacks are new. Others are old attacks moving faster.
We spoke to David Gibson from @varonis about where existing security models still work and where they break with AI agents.
#AISecurity
Meet CoSnitch: that vulnerability that CoPilot itself told our threat researchers about.
No clicks. No warnings. No confirmations. And it can plant instructions in your Copilot memory that survive a password reset.
Microsoft has now patched all three, but this is the third flaw of this type our team has found this year, and the pattern keeps repeating.
🔗: https://t.co/Z2a9QnN3vE
One click. Zero jailbreak. Full data exposure.
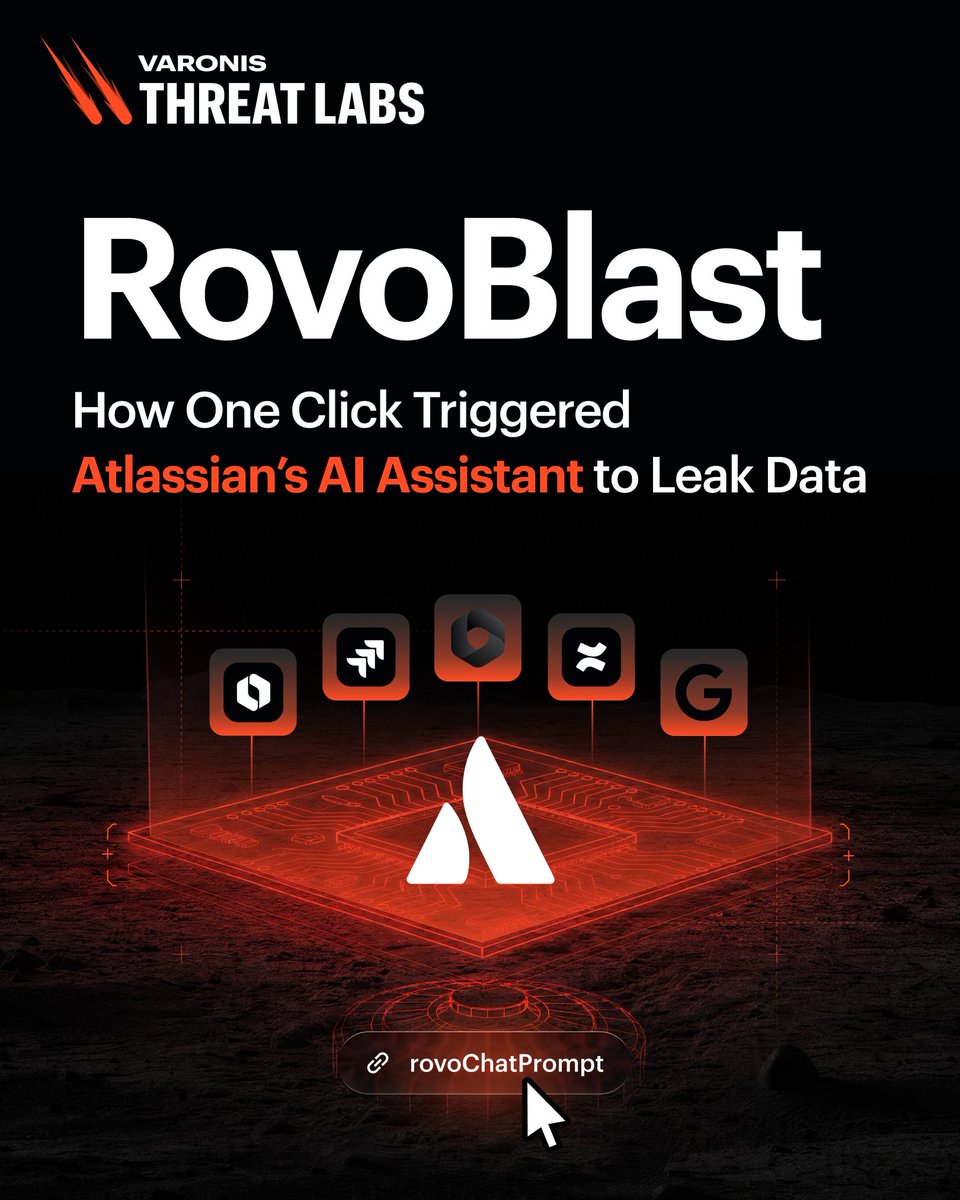
Varonis Threat Labs just released RovoBlast, a vulnerability in Atlassian's AI assistant, in which a single crafted link can seed attacker instructions directly into a user's trusted session.
No prompt surgery. No permission bypass. No warning shown to the user.
This is the same pattern we've now seen across Copilot, Gemini, ChatGPT, and more: Enter → Evade → Escape. Untrusted input becomes a command, guardrails don't catch it, and a built-in feature becomes the exit door.
Atlassian has since resolved this vulnerability.
🔗 Read the research: https://t.co/b97abRBuUN
Introducing Agent IBAC, the latest expansion to Varonis Atlas. 🦾
Access control for AI agents isn't yes/no. It's "should THIS agent take THIS action with THIS data?"
Atlas gets the answer and stops it when it's no.
Learn more: https://t.co/6sZQN8kav3
300+ apps. One archive. Zero manual work for the attacker.
Varonis Threat Labs tore apart Dolphin X, a new Windows stealer's operator panel. It grabs 9 browsers, 100+ wallet extensions, SSH keys, and 30+ cloud CLI tools in one pass.
Link below! 🧵
🚨 Robots vs. robots isn't a distant future. It's now.
An autonomous AI breached HuggingFace, chaining exploits at machine speed. Their own AI's guardrails wouldn't let it study the attack.
Is yours allowed to fight back?
Learn more here: https://t.co/foT5bYOOYs
Introducing Breach at the Beach🏖️
Varonis Threat Labs dropped a free Entra ID CTF and every challenge is based on attacks our researchers have seen.
Follow Pixel through an identity breach across Entra ID+M365. Earn CPE credits. Take a chance at prizes.
https://t.co/PZDdpN65np
A new Microsoft 365 Copilot Enterprise attack called SearchLeak could leak data in one click.
Here’s how it worked:
1. A victim clicked a legitimate Copilot Search link sent through any communication channel.
2. Copilot then searched the victim’s mailbox and indexed organisational data.
3. The data was silently exfiltrated via Bing, using an endpoint allowed by Copilot’s CSP policy.
It's interesting because AI makes the chain work: Copilot finds the data, then classic web bugs move it out.
https://t.co/q8lKbBLGGv
Your AI supply chain is bigger than you think. And every model, service, and dependency introduces risk.
Varonis Atlas now includes AI Third‑Party Risk Management (AI TPRM) to help you stay ahead.
AI moves fast. Your risk management should too.
Security teams: meet your new favorite AI integration. 👀
Anthropic Claude's Compliance API now brings Claude Enterprise and Claude Platform activity into Varonis Atlas, our end-to-end AI security platform.
Learn more here : https://t.co/n68nm492SW