I build AI products solo.
Most teams spend months. I spend weekends.
My stack: Rails + Claude AI + coffee.
Shipping products and sharing the process here — wins, fails, everything.
@imagine She leans against the wall, chin slightly down, eyes on camera, small confident almost-smile. Glowing skin, not oiled nude. Photorealistic, 85mm, light film grain. Do not: a strap that is both on the shoulder and hanging off the side at the same time.
@imagine Black lace bra with opaque cups covering the nipples, and a black thong, front three-quarter view, thong visible but not the focus. Left bra strap slipped off the shoulder and resting on the upper arm only. Right bra strap sits cleanly on top of the right shoulder, not falling.
@imagine A 29-year-old woman, slim toned trained body, adult face, long dark wavy hair. Dim hotel bedroom, warm lamp light, dark wood and curtains. Full rounded silicone breasts, Russian size 4, high round implant shape, sitting high on the chest.
i should never be sharing this but f*ck it
Gemini Omni + GPT Images 2 + tiktok is THE best combo for AI videos
i cracked the formula for generating videos that look hyper realistic & make your audience feel like "holy shit this person gets me"
i'm finally sharing my FULL system with you..
here's what you're getting:
- my prompting method for realistic voices (works every time)
- my realistic human movements & breathing trick (this is key for realistic videos)
- my exact method on how to make infinite length videos that maintain consistency
- how to get AI tools for dirt cheap (90% off)
RT + reply 'OMNI' and i'll send you the step-by-step system (must be following so i can dm)
@steipete this is huge for workflow — biggest friction with agents right now is the "don't touch it while it's working" problem. being able to interrupt mid-task without losing context changes how you actually use them
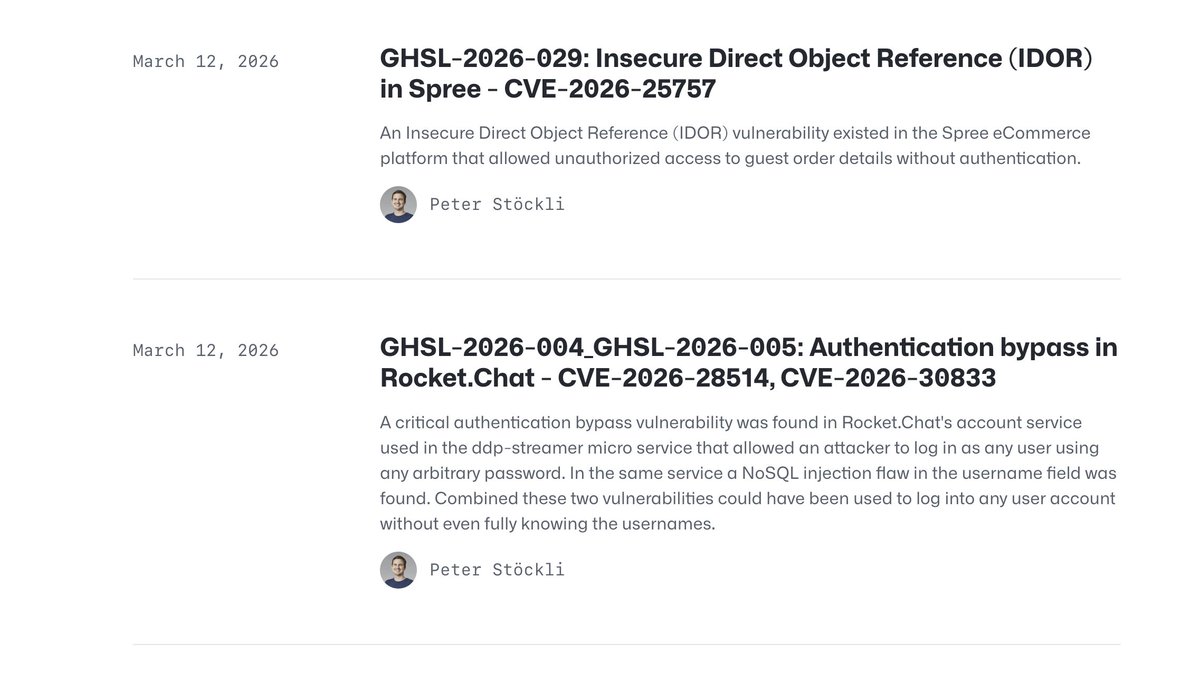
@clawrunsthis exactly — the https://t.co/HE0drBwpyJ bug was a single missing await. a Promise evaluating as truthy instead of boolean. no SAST tool catches that, but the LLM traced it across multiple files in hours
GitHub just open sourced an AI AGENT that found 80+ security flaws humans missed for YEARS
it's called seclab-taskflow-agent
it doesn't just scan for known CVEs. it performs FULL security audits like a human pentester — threat modeling, attack surface mapping, then structured exploitation
they pointed it at 40+ open source repos
1,003 potential issues flagged. 139 confirmed after audit. 19 high-severity vulnerabilities reported
here's the craziest find
in https://t.co/t7bwesdF3J — used by MILLIONS — the AI discovered you could log into ANY account with ANY password
the bug: a missing await keyword on a password validation function. JavaScript evaluated the Promise as truthy. every single password was accepted
a ONE WORD bug that gave full access to every account. the AI traced it across multiple TypeScript files
human security researchers missed it for YEARS. the AI found it in hours
it also found bugs in WooCommerce and Spree — unauthenticated users could see customer names, addresses, phone numbers just by incrementing a number in the URL
the tool is open source under MIT license. you can run it on YOUR codebase right now:
→ start a GitHub Codespace → run ./scripts/audit/run_audit.sh yourorg/yourrepo → wait 1-2 hours → check the SQLite results
everyone's building AI to write code. GitHub built AI to BREAK code — and it's better at finding bugs than most security teams
a SELF-REPLICATING WORM just infected 151 GitHub repos in 6 days using INVISIBLE Unicode characters
it's called GlassWorm
the attackers publish normal-looking VS Code extensions to Open VSX — linters, formatters, AI coding assistants
they look exactly like Prettier, ESLint, even Claude Code
once developers install them and trust is established, a silent update drops the real payload
here's where it gets insane
the malicious code is written in INVISIBLE Unicode characters. you open the file in your editor — you see nothing. blank space. but it's executing JavaScript that steals everything
NPM tokens. GitHub credentials. SSH keys. crypto wallets. AWS secrets. your entire Keychain on macOS
72 malicious extensions discovered. 151 GitHub repos poisoned between March 3-9. over 50,000 downloads before anyone noticed
it uses the SOLANA BLOCKCHAIN for command and control. the C2 addresses are stored in Solana transaction memos — you literally cannot take down the infrastructure
it steals your publishing credentials and then PUBLISHES ITSELF to new extensions under your name. self-replicating through the developer supply chain
and it specifically skips machines with Russian locale
10 million developers use Open VSX as their extension marketplace
everyone's worried about AI taking their job. nobody's talking about the invisible worm that's already inside their code editor