A spanish speaking man (of course...) in New York City reportedly stabbed his girlfriend of 6 years to death then jumped off the top of his building in an apparent su**ide attempt but the attempt failed.
He was then transported to the local hospital where he is currently being detained.
The odds of surviving a jump like that have to be near zero. If the charges are true, hopefully he's in a lot of pain...
#CityLife #NYC #3rdworld #spanish #crime #NewYork #decay #urban #police #democrats
@RealUnsweetDee Self Adhering First Aid Bandage Wrap, 2 in (for pressure) ... Non-Stick Large gauze pad. Sounds like you have done this already tho. My neighbor cut the tip of his thumb off with one of my Spyderco kitchen knives (Of course he blamed me) . It took two days to stop bleeding.
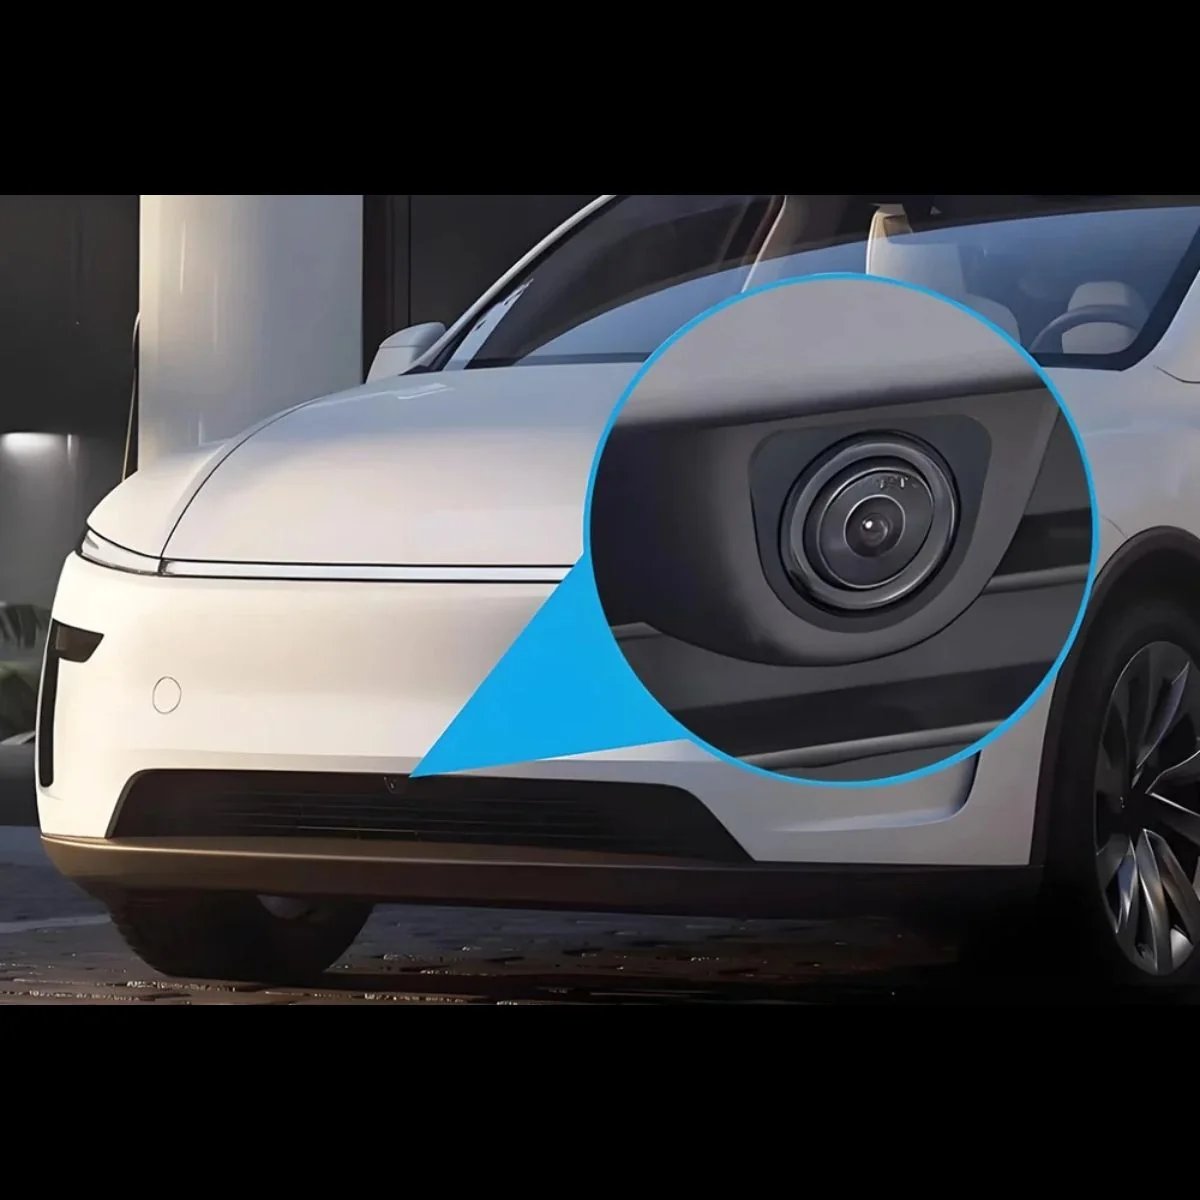
❗️ The Dutch intelligence service AIVD is warning people not to hold confidential conversations in or near their cars, saying the microphones in many modern vehicles can technically be switched on remotely to eavesdrop.
Some state actors can request car data from carmakers and other companies or hack in to get it themselves, the agency says.
It advises skipping wireless charging and Bluetooth or Wi-Fi pairing, using a USB data blocker and not taking a car with an external camera to a sensitive location.
@DanielMiessler Massive wave of software patches and improvements that introduce back doors for ease of control, advancements in fission based mini reactors so ASI can run its own critical infrastructure without the public grid. Just a few things I would do 😂
🇺🇸 https://t.co/qCsz4OlZM9 ~459K CUSTOMER RECORDS ALLEGEDLY LEAKED
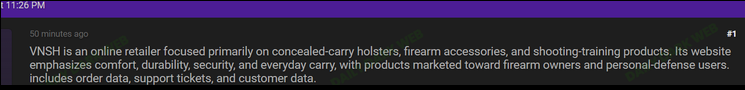
A threat actor claims to have leaked more than 459,000 records tied to https://t.co/BMWQk5npxb, a U.S. online retailer focused on concealed-carry holsters, firearm accessories, and shooting-training products.
The underground listing alleges the material includes:
* Customer data
* Order data
* Support tickets
* Account fields such as emails, usernames, and password hashes (per listing summaries)
⚠️ Analyst Note:
Large “459k+” retail dumps are frequently recycled older CRM extracts or partial order exports. Sample authenticity, hash strength, freshness, and whether VNSH production systems were involved cannot be confirmed from the listing alone.
We assess this as an unverified threat-actor claim involving alleged https://t.co/BMWQk5npxb customer and order data, NOT confirmation of a compromise of VNSH systems.
If authentic and non-public, customer and order records at this scale could enable phishing, fraud, and account-takeover attempts.
#DDW #DarkWeb #USA #Retail #DataBreach #PII #ThreatIntelligence #CyberSecurity