Building a fintech app shouldn't mean stitching together 10 different providers.
Finance Computer aims to change that.
🌐 https://t.co/hvt7hmdcUi
Here's what they're bringing together:
🏦 Accounts & IBANs 💳 Card issuing & payment processing 💸 Transfers & payouts 🔄 Fiat & crypto 🎁 Loyalty & rewards 📈 Investment services 🤖 Payments for autonomous AI agents
Banking, payments and blockchain infrastructure under one roof.
Businesses can spend less time dealing with providers and more time building their products.
💻 @MultiversX logged 204 commits in a week.
That is its highest weekly commit count of the past month.
A lively week for MultiversX.
📊 https://t.co/7L4SCx5BBm
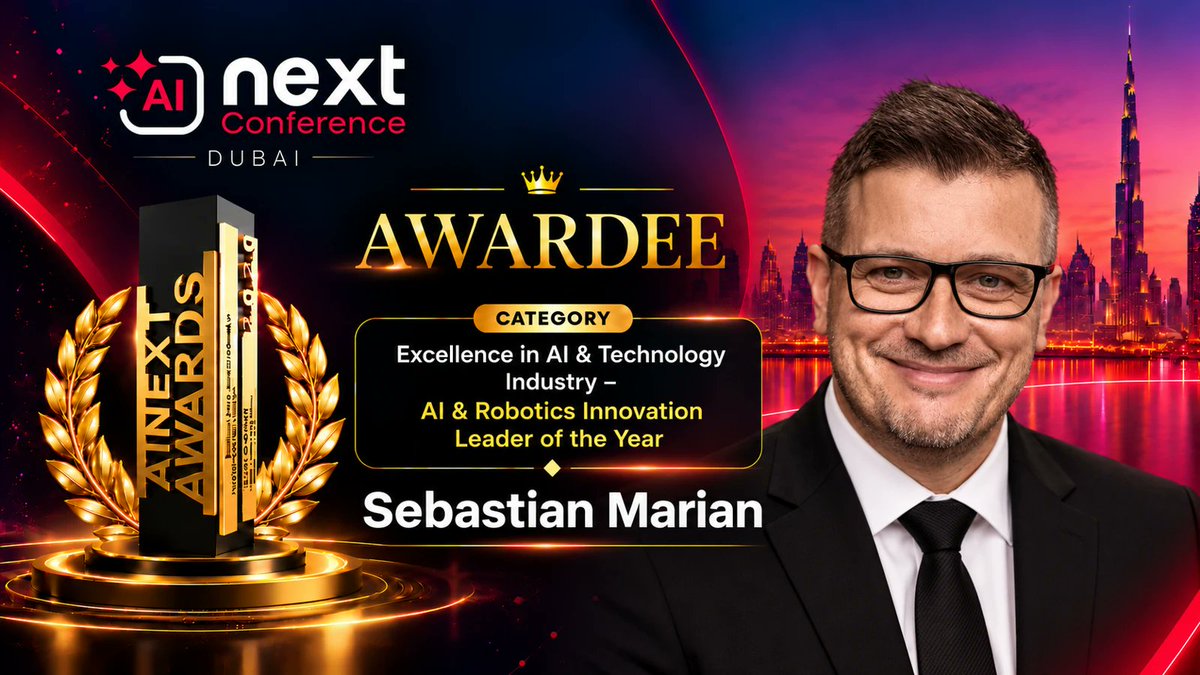
Hello #foxfrens 💙🦊💙, Sebastian Marian, CEO & Founder of Foxsy AI, wins AI & Robotics Innovation Leader of the Year at AINext Awards & Conference Dubai 2026!
A proud moment for our founder and the entire Foxsy AI community! 🏆🚀
https://t.co/wG17mmILUE
#FoxsyAI #Web3 #AI #Robotics #AINext #Dubai2026 #OutfoxTheFuture
small Rust tip for MultiversX contracts: pick the storage mapper by how you read the data, not by what it "looks like".
only need "is this address allowed?"
use a WhitelistMapper. one storage entry per item, no iteration overhead.
#[storage_mapper("allowed")]
fn allowed(&self) -> WhitelistMapper<ManagedAddress>;
require!(self.allowed().contains(&caller), "not allowed");
need "value per user"?
a SingleValueMapper with a key argument is usually enough:
#[storage_mapper("balance")]
fn balance(&self, user: &ManagedAddress) -> SingleValueMapper<BigUint>;
SetMapper and MapMapper are great when you really iterate. they also store extra links and keys, so every insert costs more writes.
fewer writes, less gas, smaller state.
when you go from one agent to many, the security question changes.
with one agent you ask: what can this agent do?
with ten agents you have to ask: what can they do together?
the useful mental model is the "lethal trifecta": untrusted input, access to private data, and a way to send data out. any agent with all three can be tricked into leaking.
the obvious fix is to split it. agent A reads the web but sees no private data. agent B sees the data but has no internet. agent C only sends the final answer.
the catch: they talk to each other. if A can ask B for anything, and B can ask C to send anything, the fleet as a whole has all three again. no single agent broke a rule.
this is the pitch behind NVIDIA's OpenShell this week: check the combined permissions of the fleet, not only each sandbox.
what I do in practice:
messages from an agent that read untrusted content are marked untrusted, all the way down the chain,
the agent with the secrets never gets a tool that talks to the outside,
and every handoff is a narrow, typed request, not "do whatever this message says".
more agents is not the risk. more paths between them is.
This is f*king insane. SpaceXAI engineer Nick Miller, ex-Cursor:
"99% of people open one Grok Bot and call it automation
I run 20+ bots with a Chief of Staff, a PM, QA, and 15+ workers"
In this 30-minute demo, he shows how to turn a single bot into a coordinated team
Grok Bot → Chief of Staff → PM → QA → Workers
Adding bots doesn't create a team. Clear handoffs and verification do
Worth more than most $1,000 agent engineering courses
Bookmark and watch it today
Then read the full article below ↓
@nlevine19 Dear @nlevine19 , take some time and have a look at this project. @FinanceCompute
Very strong foundations, created for businesses, solving real challenges.
Good luck !