@galnagli@Hacker0x01 I completely agree. I've been paid numerous times for reporting new CVEs, which clearly demonstrates that programs find significant value in these types of reports. HackerOne, please reconsider.
We’re just one month away from #H165!
We’re partnering with the Salesforce security team to help protect their users as they focus on robust and comprehensive security. 🙌
Dust off those scanners, and get ready to hack! We’re excited to see the results. 💪Who’s taking MVH?
It's finished! First LHE in Romania organised by @SuperbetRomania! We have the winners, congrats @iustinBB & @nytr0gen_ 😍 Also a big thank you for all the participants! See you next year! Thank you @Hacker0x01 for helping us organising the event #BugBounty#hackerone
Cache-Key Normalization: What could go wrong?
I'm excited to finally release my first write-up. It presents a new Cache Poisoning DoS technique which shows how the normalization of the cache-key can be abused:
https://t.co/Yi5S1yZd76
If you want to find domains associated to an organization, you can explore DuckDuckGo's tracker-radar.
It's a publicly accesible dataset that stores web tracking information, including domains operated by an organization.
https://t.co/uQUT5My8ud
@Nishantbhagat57 The CDN needs to be configured to cache 400 errors.
Akamai, cloudfront and cloudflare are not vulnerable by default anymore.
https://t.co/GMohHeusWL
Akamai used to store 400 errors, but they changed it in Q2 2023.
"As of Q2 2023, 400 error responses are no longer cached from origin"
Cloudfront only caches 400s if there's a cache-control directive. I found this on a few hosts which were using less popular caching servers
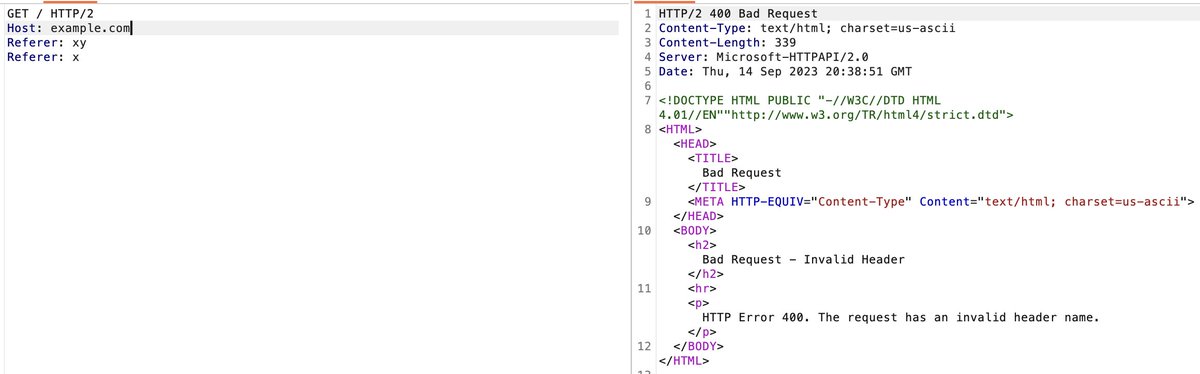
https://t.co/ygzJ6XdEH0 responds with a 400 bad request on all requests containing two referer headers. This can be used to acheive cache poisoning DoS if the cache stores 400 response errors.
Akamai used to store 400 errors, but they changed it in Q2 2023.
"As of Q2 2023, 400 error responses are no longer cached from origin"
Cloudfront only caches 400s if there's a cache-control directive. I found this on a few hosts which were using less popular caching servers
@rez0__@pxmme1337 looks like @rs_loves_bugs already answered for Romanian :P . but yeah, chatgpt is masculine and AI is feminine . not sure about croatian though haha
Chameleon v1.1.0 is now live with new features 🎉
- JSON output
- Fuzz using multiple HTTP methods
- Save output to a file
- Minor bug fixes
https://t.co/YItYcNkJo6
Hey! You!
Yea, you!
Does the idea of protecting billions of assets seem interesting? Are you a junior to mid-level #AppSec engineer that knows how to code? Are you authorized to work in the United States?
Then you sound like a perfect fit for Robinhood's Appsec team!
#Hiring
New blog post detailing some findings from auditing the Next.js ecosystem:
"Exploiting Web3's Hidden Attack Surface: Universal XSS on Netlify's Next.js Library"
Huge thanks to @infosec_au and @bbuerhaus for helping explore this!
https://t.co/1FJ3JjkC7a
@InvisibleFr1end When you first install the tool, it will also download a list of wordlists. Some of the wordlists were taken from https://t.co/F6BvwDK84M.
I'm excited to release the first version of a context-discovery tool I've been working on. https://t.co/4d7IEAvk7z - Chameleon can automatically detect the technologies running on a host and adapt to a calibrated wordlist.
https://t.co/VIMWwvmDxm