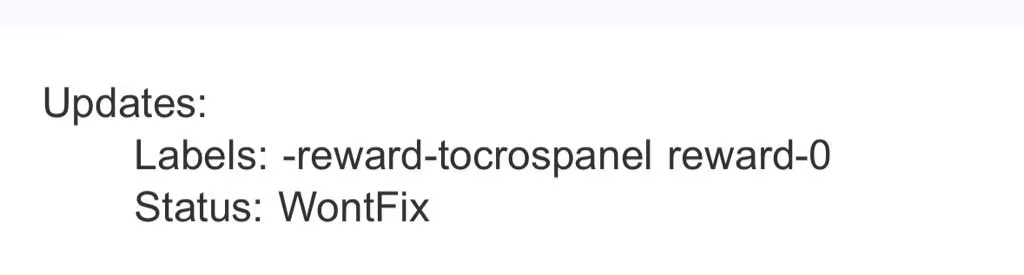
After reporting multiple UAFs to Chrome VRP, I received my first reward-0. According to my previous experience, I should have received my reward a month ago. But now it's 0. The difference is that this decision was made by Chrome OS VRP, not Chrome VRP. This is frustrating.
We're excited to share some OSS-Fuzz program news, including a revamped rewards program and several new initiatives. Happy fuzzing! https://t.co/CTzZT0KfSL
Thx. My experience of reading and contributing souce code of Chrome extension API several years ago helped me a lot. I didn't do bug hunting in the past two years. Luck money. :)
Thanks to the author of the original report and Google VRP.
Great variant analysis by @zhchbin. I also looked for variants of https://t.co/foUmrbpBO9, but didn't think about using other APIs to reach the same OS behavior.
Vulnerability that made us 30 000$ richer (and we still submit reports) - XSS in Swagger-UI related to a bug in DOMPurify - many people waited for this writeup so here you are. Article by @kannthu - happy hacking! https://t.co/dVxqCxhWDS