AI Cyber Challenge Semifinal Competition results are in! Congratulations to the top seven scoring teams who will advance to finals, and to all the competitors who worked to help safeguard the code that underpins critical infrastructure. More: https://t.co/LktjU8rBB5
Introducing ARTIPHISHELL! An LLM-Based Cyber Reasoning System made by @shellphish that autonomously finds and patches vulnerabilities for the @DARPA AIxCC competition (https://t.co/4dcUPR6SnI)
@zolutal has cinched it! After 6 nights of presumably procrastinating academic research into groundbreaking kernel pwning to instead focus on groundbreaking kernel pwning itself, he earns the first ever 🥇 badge on https://t.co/yjFhiLYJXt! GREAT JOB! 🥈&🥉 are still up for grabs!
A weakness 23 years in the making: binaries and libraries built with an older toolchain act as timebombs against ASLR under "recent" Linux kernel and glibc changes.
Users: Check your exposure!
Developers: Rebuild binaries to achieve full ASLR benefit!
https://t.co/t4hmBdWcZ6
@HaskRay yeah the compiler should probably at least give a warning if p_align is 2MiB, especially for 32-bit...
for file size, its pretty much just that thp_get_unmapped_area does huge page alignment for sizes >=2MiB and the loader maps the whole >2MiB library file
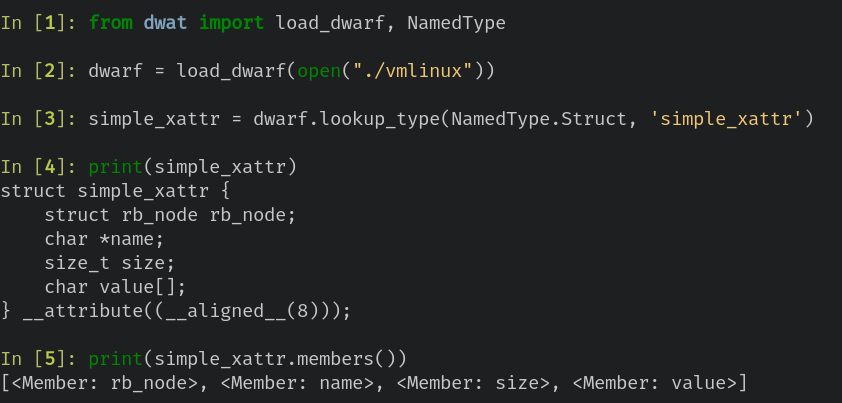
I taped my dwarf parsing work onto weggli to be able to pattern match object allocation sites of specific sizes for linux heap exploitation
it needs some work (threw it together last night) but it works pretty well from what I've seen:
https://t.co/bhfFU3XyD8
Using a vmlinux based on ubuntu 23.04's source tree and filtering for kmalloc-96 sizes, the original has a runtime >1hr, the version using my library has a <6s runtime!
and it being a library rather than CLI tool means adding more specific filters on the output is way easier
I was disappointed with most of the existing libraries/tools for analyzing type info from DWARF so I've been developing my own (in rust), check it out:
https://t.co/MAioN7C4Pp
As a little demonstration, I rewrote this bash script which parses pahole output to find kernel objects of particular sizes:
https://t.co/8CVCaMDTTu
As a cargo script on top of my library:
https://t.co/AUvkiURiPX
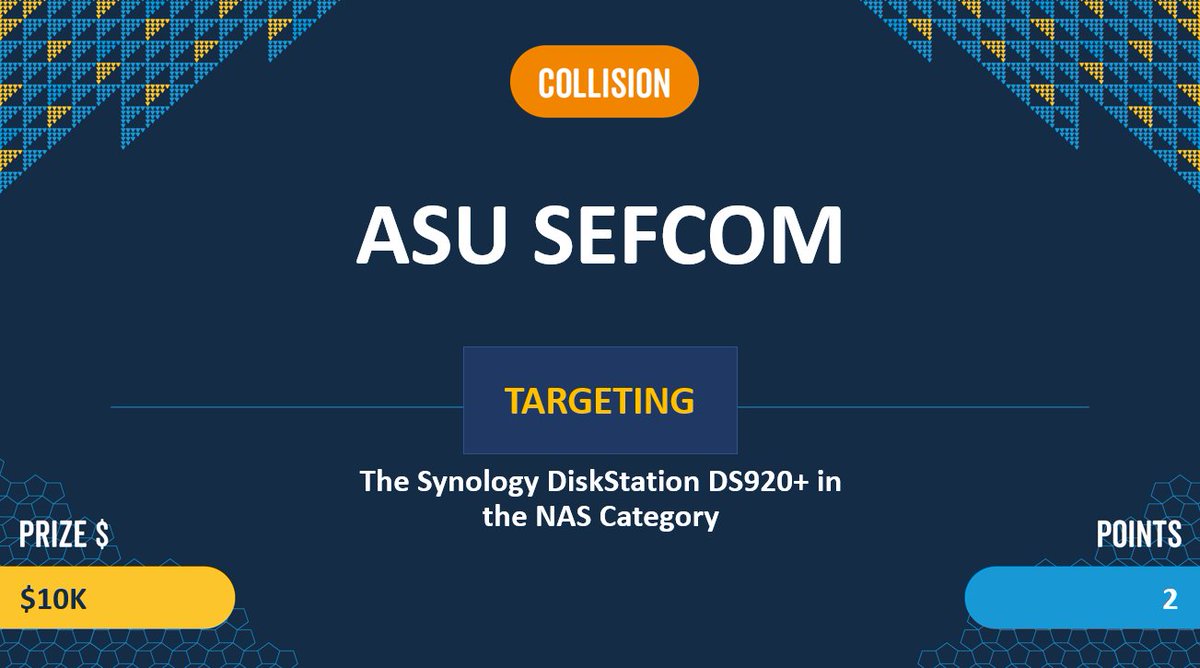
ASU SEFCOM was able to execute their OOB Write attack against the Synology DiskStation DS920+ in the NAS category to gain code execution. However, one of the exploits they used was already publicly known. They still earn $10K and 2 Master of Pwn points. (repost) #Pwn2Own