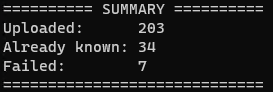Many congratulations to Edoardo Giuggioloni, Christiaan Beek and Jindrich Karasek of Rapid7 Labs, who are the winners of this year's Péter Szőr Award for "BPFdoor in Telecom Networks: Sleeper Cells in the Backbone".
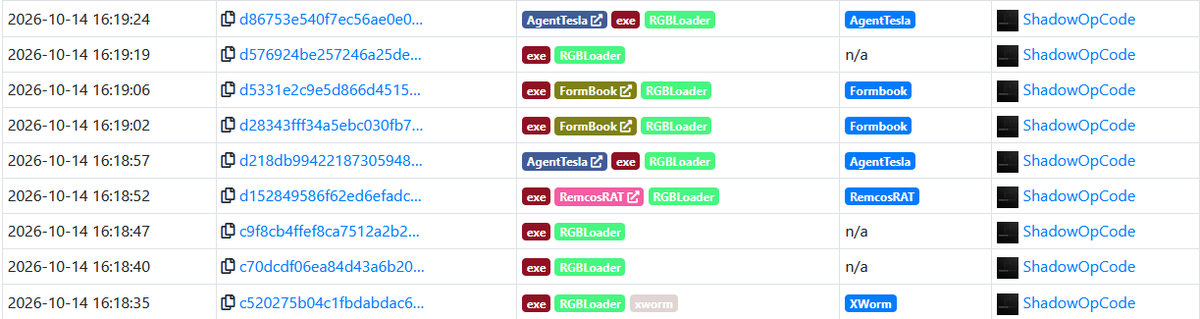
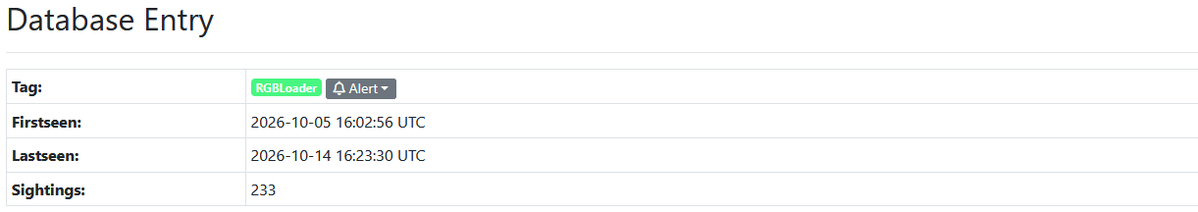
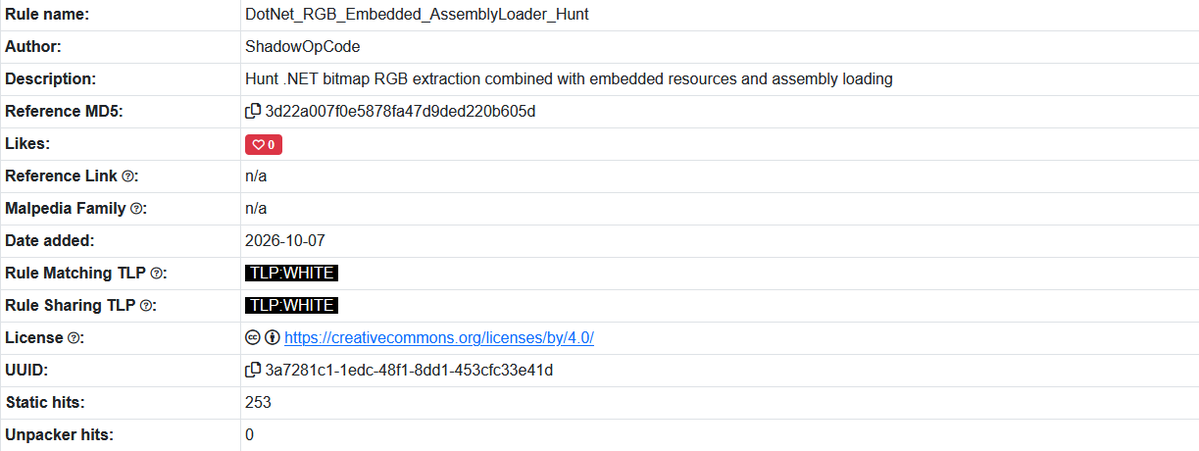
Just uploaded 203 #RGBLoader samples to MalwareBazaar, all discovered through hunting with my custom #YARA rule! 🔬
The samples are now available to the malware research community under the RGBLoader tag.
🔗 https://t.co/k8IZ5lJ8q0
#MalwareAnalysis#ThreatHunting
‼️🇬🇧 Deloitte has been named by The Gentlemen ransomware.
🇬🇧 Deloitte - A global professional services organization providing audit and assurance, consulting, financial advisory, risk advisory, tax, legal, technology, and cybersecurity services.
I believe Microsoft silently patched ShieldCrash without releasing an advisory or CVE, recent changes in mpengine.dll shows how the vulnerability was patched.
I think a patch was released long before this Tuesday since Defender doesn't have to follow the patching schedule.
New episode of Behind the Binary is live!
🎙️Joined by @L0Psec to break down macOS security, ClickFix social engineering, InfoStealers (AMOS/MacSync), DPRK developer targeting, and the evolution of obfuscation.
Plus, we talk about how AI is shifting reverse engineering and the inevitable future state...
🎧 https://t.co/8SlDtgWs55
Appreciate @jstrosch for the invite on the podcast! macOS malware is at an interesting place. Also, getting to talk about how reverse engineering workflows are changing with AI was fun/therapeutic. I wasn’t crying I promise. 😂