Oh boy … PHP sent clear text data when you used uppercased S in httpS:// in a protocol handler 🙈🙈
file_get_contents('HTTPS://…') skipped TLS: tokens, POST bodies and FTPS logins went out unencrypted!
Fixed today in 8.2.36, 8.3.37, 8.4.28, 8.5.13 & 8.6.0.
3/
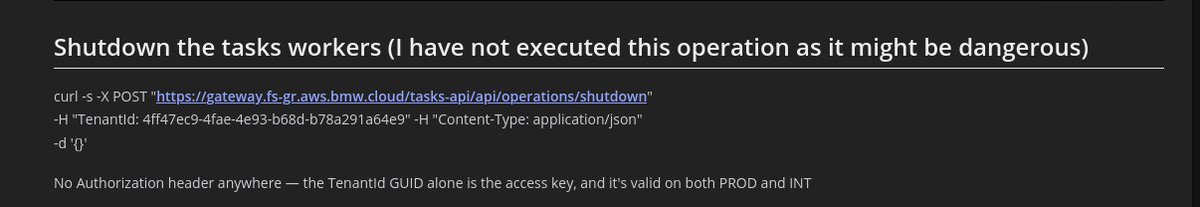
I also demonstrated backend write capability.
I identified potentially disruptive operational functionality too, but deliberately did NOT execute it.
Every JWT writeup online covers 2–3 attacks and stops.
I got tired of jumping between 40 blog posts, so I wrote the whole thing. All in one place.
https://t.co/iCSzQ4GjcS
#infosec#appsec#bugbounty#websec#jwt
Last week, Anthropic announced Project Glasswing alongside Claude Mythos Preview, a model they described as so powerful at finding vulnerabilities they couldn't release it. The announcement featured AWS, Microsoft, Google, and Apple as partners, $100M in compute credits, and a clear message: this is dangerous, and only we can be trusted to deploy it safely.
The results were real. Thousands of zero-days across every major OS and browser. A 27-year-old bug in OpenBSD. A 16-year-old bug in FFmpeg. Fully autonomous exploit chains that would have taken human researchers weeks.
But here's what bothered me: all the credit went to the model.
Read the technical blog carefully and a different picture emerges. The real innovation isn't the model. It's the workflow:
- Rank every file in a codebase by attack surface
- Fan out hundreds of parallel agents, each scoped to one file
- Use crash oracles (AddressSanitizer, UBSan) as ground truth
- Run a second verification agent to filter noise
- Generate exploits as a triage mechanism for severity
That's a pipeline. And pipelines are model-agnostic.
At Lazarus AI, we spend our days deploying custom AI in places where "just use the closed API" isn't an option: regulated industries, enterprise, and government. When I saw Glasswing, my instinct was the same one I have every week: strip out the proprietary model, keep the architecture, run it on whatever model is best for the customer.
Clearwing is a fully open-source vulnerability discovery engine. Crash-first hunting, file-parallel agents, oracle-driven verification, variant hunting, adversarial verification. Works with any LLM.
I tested it with OpenAI Codex 5.4 and reproduced Glasswing's findings. I'm now reproducing results with our own ReAligned model - Qwen3.5 finetuned to Western alignment.
Mythos is certainly a great model. The N-day exploit walkthroughs in Anthropic's blog show real reasoning depth. But it's an incremental improvement over Opus, the same way Opus was over Sonnet, and Sonnet over Haiku. It's not a leap to superintelligence. It's the next point on a curve we've been watching for years.
What actually changed the game was the workflow.
Defenders shouldn't have to wait for access to a gated model to secure their software. These vulnerabilities have been sitting in codebases for decades. The tools to find them should be available to everyone: the open source maintainer running FFmpeg on a Saturday, the startup that can't afford $125/M output tokens, the researcher in a country where Anthropic doesn't operate.
Clearwing is MIT licensed and available now.
https://t.co/E0WP5njZQJ
Clearwing enables a wide variety of security activities. Handle with care. It is sharp.
🦊 Mozilla Foundation fixed CVE-2025-6430, discovered by our researcher Daniil Satyaev!
This vulnerability allows the Content-Disposition: attachment header to be ignored if the page is opened using <embed> or <object>, resulting in files being displayed instead of downloaded.
@paoloardoino The sign up form on Bitfinex allows anyone to check if a particular email is registered thus email address enumeration might be possible.
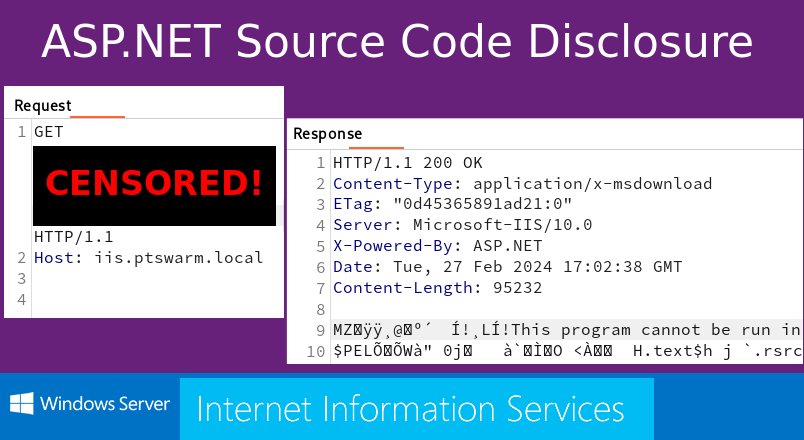
🎁 Source Code Disclosure in IIS 10.0! Almost.
There is a method to reveal the source code of some .NET apps. Here's how it works.
👉 https://t.co/Fo4tpkaHey
@evilsocket@Tailscale Good to know. In that case only MITM might be a potential risk in case you have some insecure connection between yours hosts and attacker might be able to evasedrope
Have a new blog out today looking at Purple Teaming the Azure/Entra cloud ☁️ - includes some neat queries and detection opportunities, check it out!
https://t.co/Ag8v6lDDgn
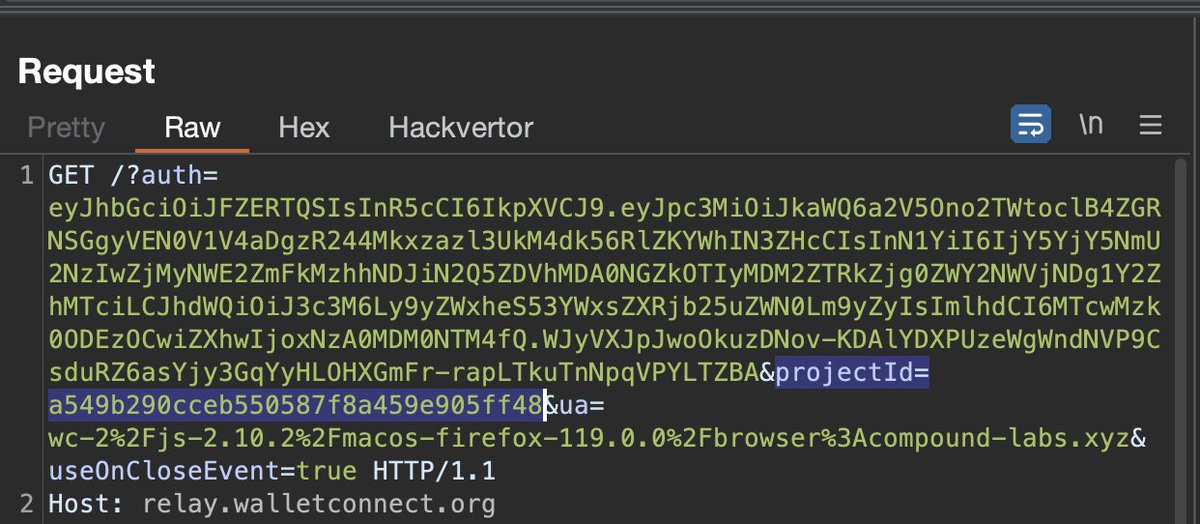
@realScamSniffer@compoundfinance Those guys seem to be using @WalletConnect service to connect wallet users to their malicious app.
projectId=a549b290cceb550587f8a459e905ff48
@WalletConnect can you take some action and locked down their account? This way we can protect users at risk.
We are excited to announce the MOBILE APP RISK SCORING, a new collaborative effort between industry, academia, and the @owasp MAS project. This proposal introduces a novel formula designed to measure the risk associated with mobile apps. OPEN FOR COMMENTS
https://t.co/g9L4FIACh3
Defcon uploaded all talks on media server so my #defcon31 talk : The art of compromising C2 servers - A web application vulnerabilities prespective is now available.
I hope you enjoy it as much as I enjoyed returning home :D
https://t.co/ofDAfFBcN3