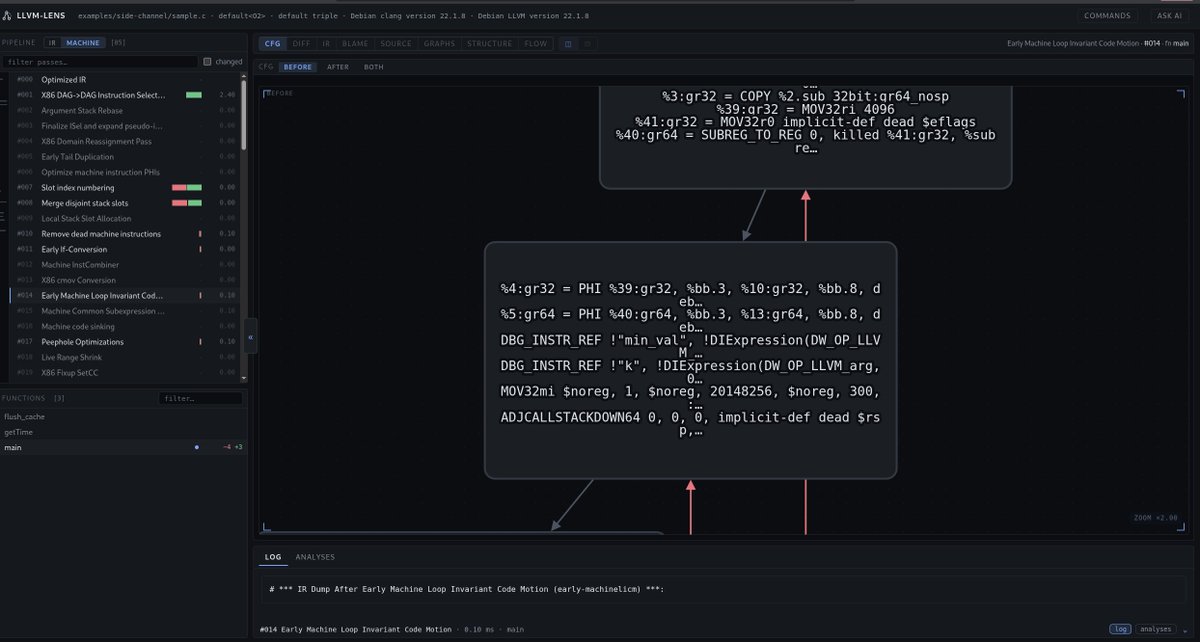
@0xn4utilus@0xP0ch1ta, @D3LET3_57 and I developed LLVM-Lens, an LLVM Pass Transformation Analyzer that helps visualize the compilation pipeline for C/C++ code.
For each stage in the pipeline, users can view changes to the LLVM IR, the analyses that are run and invalidated, the CFG, and other compilation graphs.
In addition, we have added support for Machine IR. Users can visualize the Machine IR pipeline in a similar manner to the LLVM IR optimization pipeline. Physical register allocation and register spills can also be viewed. Every line of IR and Machine IR can be mapped back to the corresponding C/C++ source code using debug information.
Comes with AI integration to help users understand pass details and transformations.
GitHub Repo: https://t.co/TgvZZ5ci5L
Had an insightful discussion with Hon'ble Minister @AshwiniVaishnaw about launching a strategic initiative to bring together Indian-origin AI researchers from around the world. Indians have made significant contributions to modern AI, from the early Transformers paper, to teams behind leading models like OpenAI’s GPT, Anthropic’s Claude, Google’s Gemini, and Meta’s Llama. We're collaborating with the best minds to build foundation models that will power India’s AI future.
A key challenge in building foundation models for India lies in the lack of internet-scale data, unlike the US or China, combined with the country’s immense linguistic diversity. To truly democratize these models, our approach will focus on the unique conversational style of Indians, which often involves heavy code-switching between languages and dialects. We plan to use synthetic data generation and reinforcement learning to train LLMs, and are committed to open-sourcing essential components, including frameworks and code, reinforcement learning data, and model weights for select models.
We’re looking to hire exceptional AI Engineers to join us on this mission.
👨💻 FTE: ₹40L Base + ₹40L ESOPs
🧑🎓 Intern: ₹1L/month
📍 Location: Virtual
Know someone who’d be a perfect fit? Tag them!
If you’re interested, comment below, and we’ll get in touch.
*** Internship Opportunity ***
@TurboML is hiring! Join us in building a Machine Learning Platform Reinvented for Real-Time.
Open Roles:
1. Software Engineer
2. ML Engineer
3. Video Editor
4. Marketing Freelancer
💰 Stipend: ₹1L/month
🗓️ Start Date: Summer 2025 (or January onwards)
📍 Location: Virtual
🚀 Career Path: PPOs for top performers
If you're interested, reply below! We’ll follow up with a brief, hands-on challenge as the next step.
InfoSecIITR is thrilled to announce the return of BackdoorCTF 2024 on 22nd Dec 2024.
Don't miss out on this chance to test your hacking skills and win big!
Register now at https://t.co/DrFWrWscqH for more details.
Happy hacking and see you there! 🔥
#ctf#infosec
3 members of InfoSecIITR @sl4y3r__07@PTRACE_TRACEME@21verses completed the flare-on challenge. They successfully solved all the 10 challenges during the given timeline. We congratulate them for their achievement.
Once again members of InfoSecIITR performed extremely well for CSAW CTF Finals achieving a Global rank of 7th and 1st in India. The legacy continues… #CSAW#CTF
We're proud to announce that we finished 1st nationally and 13th globally in CSAW'24 Qualifiers! Additionally, we successfully solved all the challenges with 8 hours to spare.
Huge thanks to our dedicated members for their outstanding effort!
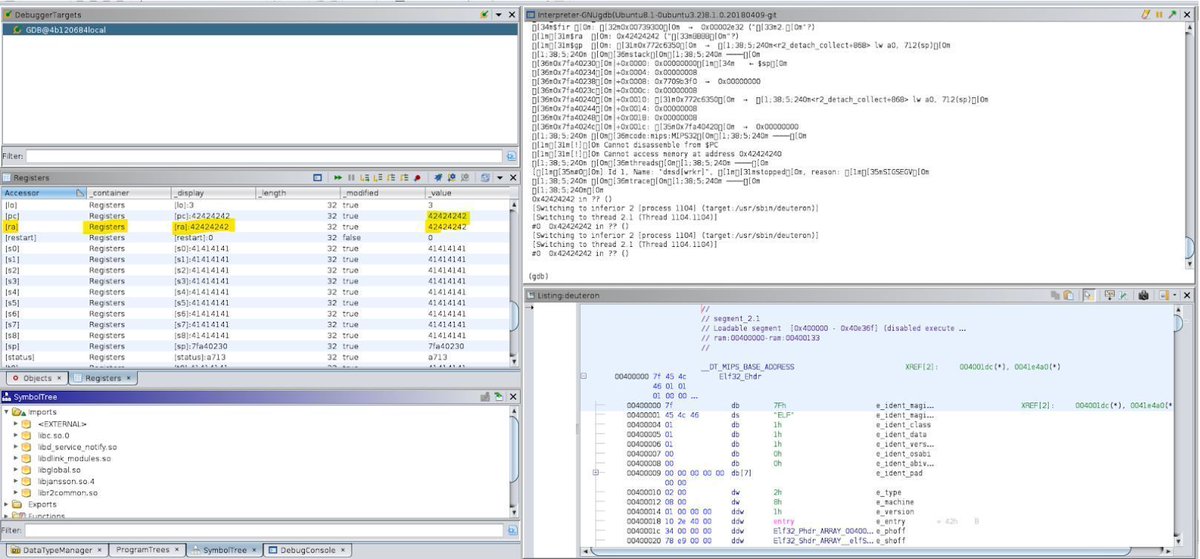
Security analysis and reverse engineering of IoT devices and debugging with Ghidra
Excellent series by @ArtResilia
Part 1: https://t.co/PHqvcuai0f
Part 2: https://t.co/kGorAPkgTJ
Part 3: https://t.co/FDFXKAFARc
Part 4: https://t.co/OxzlaYO0vI
#iot#cybersecurity
This is the weirdest of them all - a WiFi-capable device that can inject into the targeted... Android devices via WiFi? The device is said to be portable, plug and play, supports 3G and 4G. After a successful injection, it can get device info, GPS, SMS, contacts, call log, files
Members of InfoSecIITR participated in Hackday CTF 2024, securing the 7th place and earning a spot in the offline CTF in Paris. We are seeking sponsors to cover the travel costs for our team members. Kindly email us at [email protected] for the same.
PoC to takeover Android using another Android by exploiting critical Bluetooth vulnerability to install #Metasploit payload without proper Bluetooth pairing (CVE-2023-45866)
It still affects Android 10 and bellow
https://t.co/4pRreGazUM
#NetHunter
Great tutorial by Nicolas Fabretti on Linux kernel exploitation using CVE-2017-11176 as example
Part 1: https://t.co/9dvQOGgpeG
Part 2: https://t.co/JsvFkbr9iQ
Part 3: https://t.co/PANcb1P6In
Part 4: https://t.co/2qEPjbier7
#Linux#kernel#exploit
Internals of compilers, linkers, JITs and assemblers with focus on software security hardening)
Low-Level Software Security for Compiler Developers:
https://t.co/7tIZD6zFwP
#infosec#compilers#cybersecurity