@Goglin zrób sobie laby na wersji burp community lub ewentualnie caido bo on nie ma ograniczonego intrudera (automate) na darmowej wersji, a na sam egzamin odpal 30 dniowy trial wersji burp pro :D
@KacperSzurek Ja po prostu przestawiłem YT na angielski. Angielskie wtedy są po angielsku a polskie tytuły po polsku (nie tłumaczy na angielski automatycznie)
Badacze https://t.co/KyZIxxk0se zaprezentowali odkryty atak na łańcuch dostaw celujący w projekty napisane w Golangu ⬇️
▶️ Zespół bezpieczeństwa odnalazł fork zarchiwizowanego projektu BoltDB, który zawierał złośliwy kod łączący się do serwera C&C.
▶️ Projekt trafił do cache serwującego kod bibliotek, a złośliwe zmiany zostały usunięte z repozytorium, aby utrudnić wykrycie ataku
▶️ Biblioteka, pod którą próbowano się podszyć – BoltDB, jest zależnością w prawie 9000 projektów
https://t.co/ulgjR59ze0
@witkowskimich@offsectraining I'm working on creating my blog, when I'm done there will definitely be a post about OSCP.
For now, I already have my website https://t.co/UGiEMLrW5o and a hacker wiki project (I will add new notes soon)
PL: https://t.co/iPfcxPObPd
EN: https://t.co/jw6l0QMNJ3
Just passed the OSCP/OSCP+ exam from @offsectraining ! 🚀
After months of preparation and an intense 24-hour exam, I’ve reached this incredible milestone.
Thanks for this challenging journey!!!
https://t.co/sZBjPMy2fQ
#oscp#offsec#cybersecurity#pentesting#security
TLDR: Massive Supply Chain attack had been happening on the highly popular JS Library lottie-player since ~2 hours ago that populates attackers Web3 wallet connection pop-up on legitimate websites.
I'll write here what we know, what can be done and how to detect it in the wild.
You can track the entire conversations and remediation through https://t.co/lTIjfsJHXh - just to give a timeline of events
3 Hours ago, lottie-player end-user created the linked issue ^ on GitHub, specifying that while seamlessly including the lottie-player library on his website, it populated a Web3 wallet connection:
Simple inclusion of
https://t.co/cPHDOw8tLu
or
https://t.co/oYbMAyfPxT
Led to:
Users were experiencing the same on popular websites all across the internet, like @tryhackme and it seems that the original attack intent was to target major crypto websites who utilize the library.
1 Hour ago, VP of Engineering at Lottie was tackling the issue within the GitHub thread
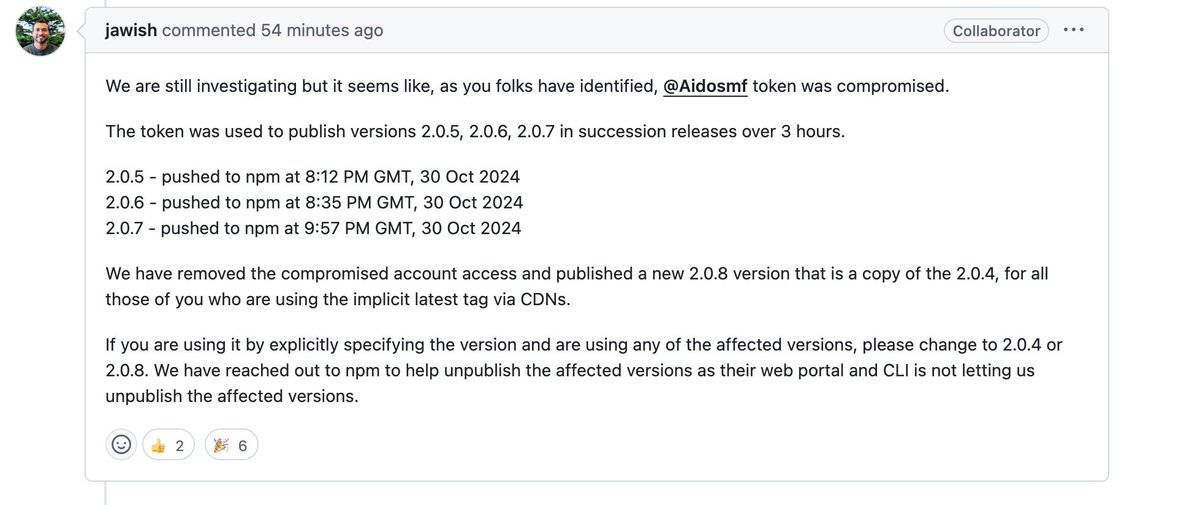
As some users who investigated already came to speculations, it seems that one of the maintainers accounts tokens - https://t.co/BjF2MRza1U had been compromised and allowed attackers to plant malicious code on ~3 versions across NPM
https://t.co/d8kWUMUHo3
2.0.5 - pushed to npm at 8:12 PM GMT, 30 Oct 2024
2.0.6 - pushed to npm at 8:35 PM GMT, 30 Oct 2024
2.0.7 - pushed to npm at 9:57 PM GMT, 30 Oct 2024
As of the latest update 20 minutes ago, seems that the original infected package was removed from NPM and most of leading CDNs, however websites who directly reference the affected versions are probably still vulnerable and need to either backport to 2.04 or update to 2.08
"The affected versions have now been removed from https://t.co/ZXBI6z2nC6 (2.0.5, 2.0.6, 2.0.7)."
Another GitHub user has included a gist with reference to the malware itself
https://t.co/qrRMeLTLJN
If you'd like to probe your web assets and see which one of them are using one of the still affected versions, you can use the following Nuclei Template:
https://t.co/G2RRPGUAny
I'll update the thread if anything new comes up.
Just two days left until the first hearing in Newag's lawsuit against us (Dragon Sector members) and SPS. In case you've missed it, we're being accused of infringing upon Newag's intellectual property and unfair competition.
More details: https://t.co/DCRWe6Yzsq
👀 Tak to już jest, że zawsze w oceanie znajdzie się jakaś większa ryba. Gdy na liście ofiar cyberszpiegów są partie polityczne, ambasady, prezydent Stanów Zjednoczonych, FBI i NSA, Pentagon czy NASA, a to jedynie mały wycinek listy, to brzmi tak abstrakcyjnie, że aż niewiarygodnie.
Zapraszam do dzisiejszego odcinka ⬇️
https://t.co/phU3cvAQcZ
OpenAI discourages "GPT" in the name of bots, so I have renamed "SecGPT" to "Arcanum Cyber Security Bot."
ACSBot is by far the best GPT on the GPT Store to use as a security buddy.
I have put hundreds of hours into its prompt engineering.
Enjoy!
https://t.co/NpSTyjhJJ4
Wprowadzenie do cybersecurity dla dziennikarzy (free szkolenie z pokazami na żywo).
☑️ Infekowanie telefonów
☑️ Przejmowanie kamer - czy to jest możliwe?
☑️ Fakty vs mity cyberbezpieczeństwa
☑️ Wycieki
☑️ Podstawy anonimowości w sieci / OSINT
Byłbyś zainteresowany? Polub.
Atak cold boot na żywo, skutkujący odzyskaniem danych z zaszyfrowanego laptopa. Tak, taki atak z zamrażaniem kostek pamięci.
Ktoś zainteresowany takim pokazem/szkoleniem na żywo u nas? Polub.
🔴Alert prywatnościowy. Twitter wprowadził ostatnio nową opcję (rozmowy audio/video), ale:
❌domyślne ustawienia pozwalają namierzyć Twój adres IP (wystarczy nawiązać do Ciebie połączenie audio lub video; mogą to zrobić konta, które obserwujesz plus z którymi wymieniliście minimum jedną wiadomość).
Tutaj sprawdzisz jakie masz ustawienia oraz kto może zainicjować połączenie do Ciebie:
✅Ustawienia -> Prywatność i bezpieczeństwo -> Prywatne wiadomości
Aby nie mieć problemu z możliwością ujawnienia adresu IP:
✅Wyłącz połączenia audio i video.
✅Ewentualnie włącz opcję: "zwiększona ochrona prywatności"