@vxunderground Currently going through the exact same thing with my baby, always funny seeing someone going through the same motions as yourself across the world.
I hope you get a good nights sleep and hope that you have an abundance of cold teething toys stocked in the fridge to get through!
⚠️ Giveaway ⚠️
Want to learn modern reconnaissance and hacking skills?
Join The Bug Hunter's Methodology Cohort 5!
October 2nd, 3rd, 4th -
https://t.co/DvozzsLYiE
Like and retweet this post for a chance to win a free seat! Five winners will be announced on Sept 1st!
After months of work, I have finally updated my Bug Bounty course with a massive focus on hands-on labs through @hackinghub_io!
More info here 👉🏼 https://t.co/yhUhrKRYYw
Use code UPDATE50OFF to get 50% off!
I also have some free codes! RT/Reply for a chance to win!
🚨 I am giving away 1 seat each of our June Red team (CRTP) and Azure (CARTP) bootcamps. 🚨
Repost, like and reply to this tweet to participate. I will announce the winners on Monday (27th May).
https://t.co/sKR2ZXihOI
#redteam#pentest#giveaway
Not a #KNOXSS Pro user yet?
Here's a 5% COUPON!
🤩👏
KNXHUNT05
5% OFF for our One Time Payment plans!
(3, 6 or 12 months)
➡️ Like and share this one to get a chance to win a 100% OFF coupon next week! #GIVEAWAY🤯
Sign up now!
😎👇
https://t.co/nNqODwzUC0
#XSS made easy.
GIVEAWAY of my 60hour Hacking course from scratch to intermediate level to 5 people who like and retweet this tweet.
winners will be picked on saturday this week
https://t.co/XOkRpEDf83
#infosec#hacking#cybersecurity#redteam
CVEs!!! 🤩
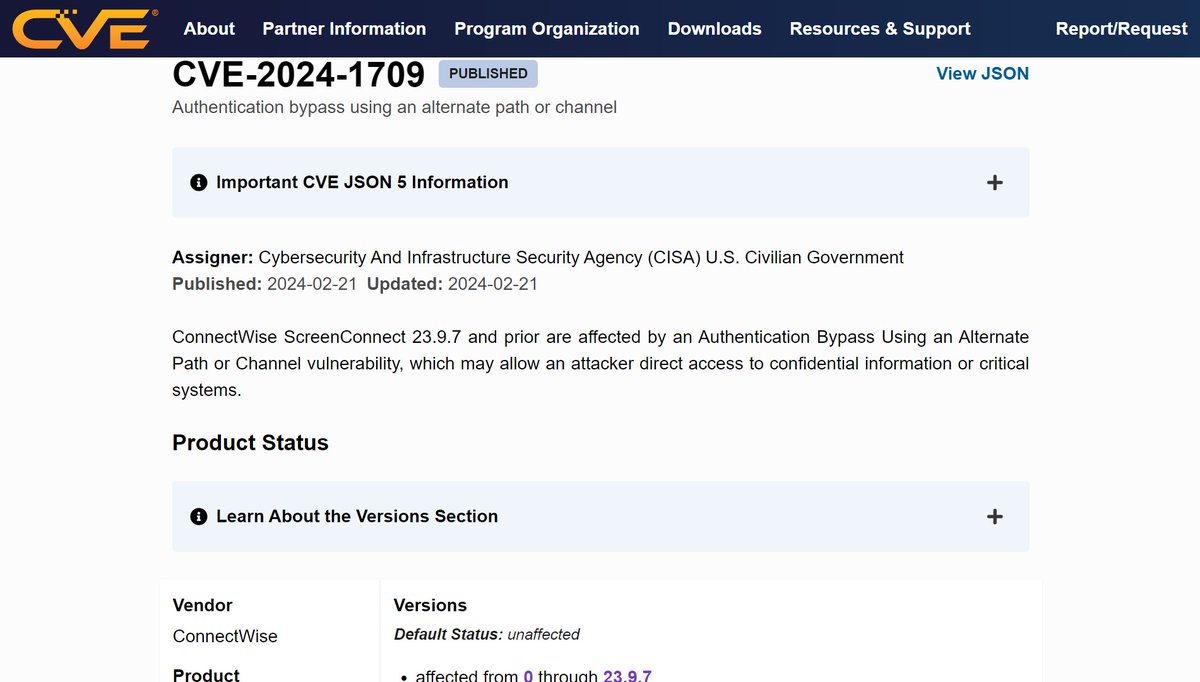
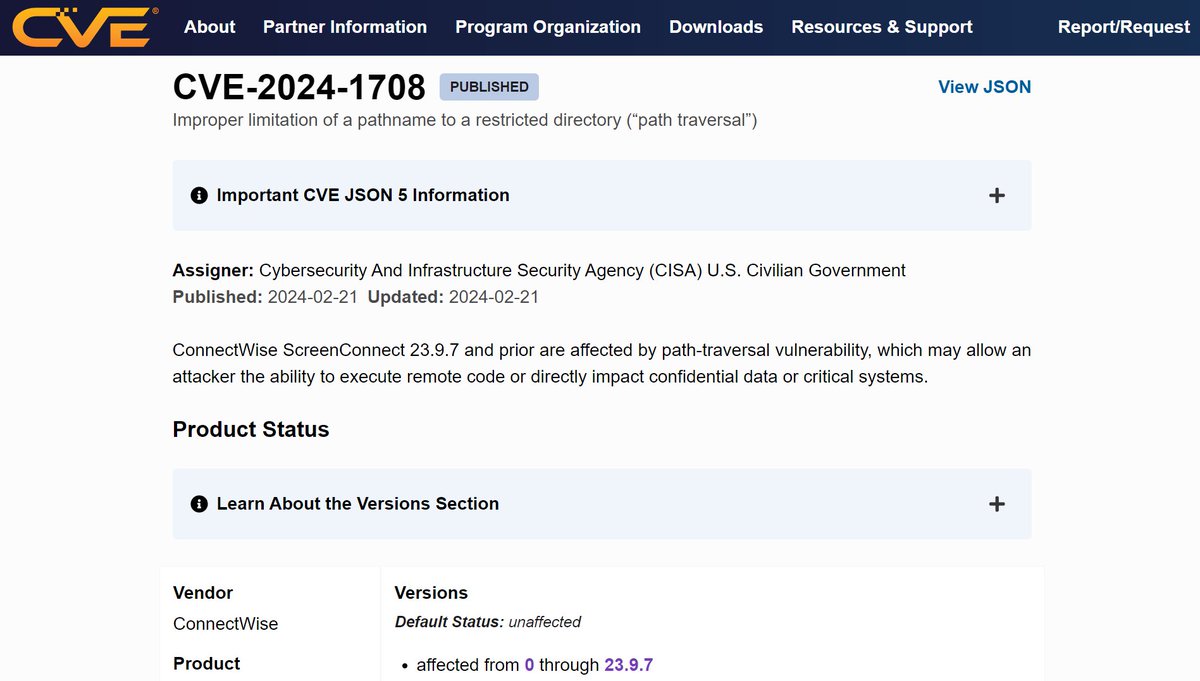
CVE-2024-1708 and CVE-2024-1709 assigned for the #ScreenConnect vulnerabilities.
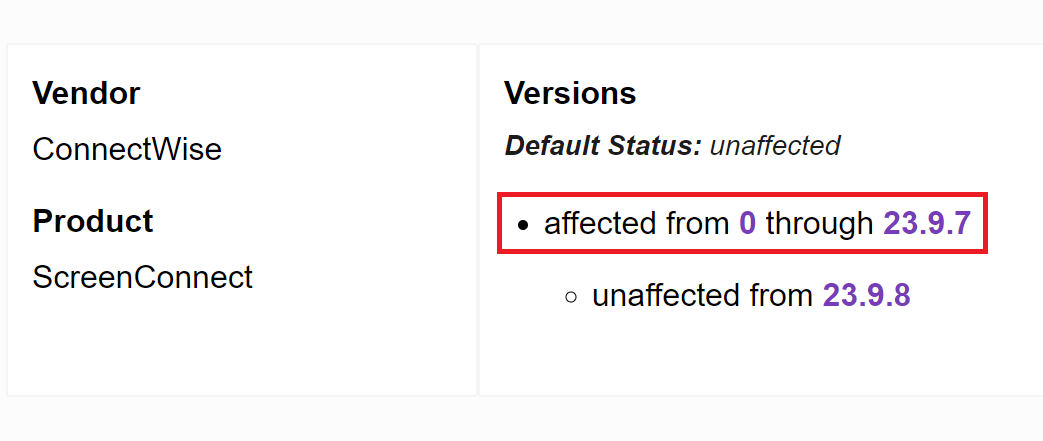
.... and ah, the words 'affected from version 0' are pretty brutal 😅😅
@3lOr4cle@cyb3rops@thor_scanner@_JohnHammond Another approach could be to exclude new accounts from triggering the rule i.e an expected domain belonging to your company, thus allowing you to catch any non-business related new accounts, ex. Gmail, Outlook etc.
Introducing usernames and phone number privacy on Signal! We’re making it possible for people to connect with each other without having to share phone numbers. Now launching to beta users, available for everyone soon. https://t.co/YcBEyD1AIA
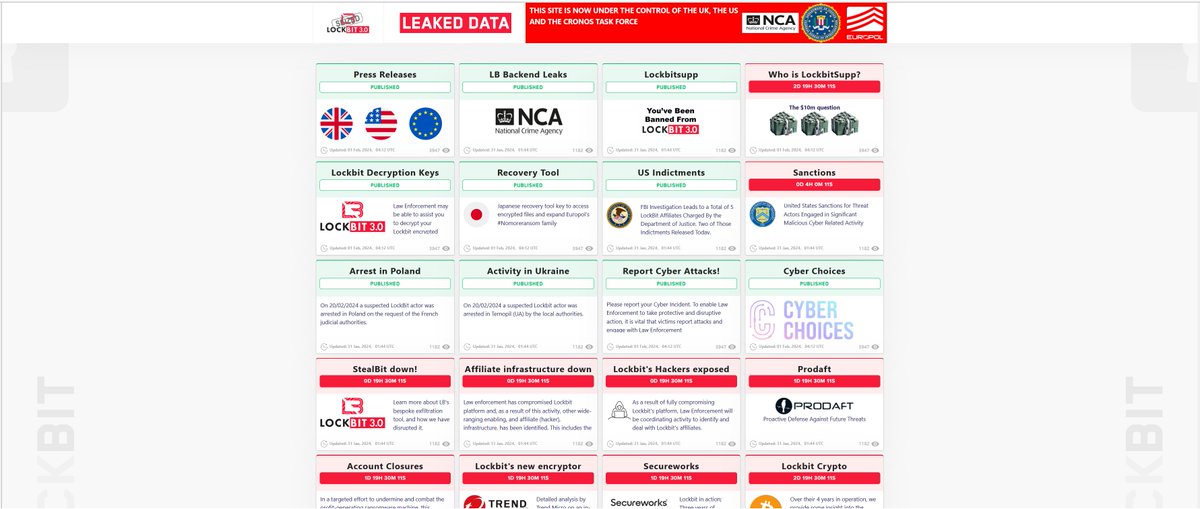
Since LOCKBIT’s first entry into the cybercrime ecosystem, we at PRODAFT have been assisting NCA, FBI and other partners of #OpCronos to better comprehend and disrupt this large criminal enterprise.
Researching this ill-famous cybercrime syndicate has been challenging, but our investigations led us to identify over 28 affiliates and uncover all decryption keys for their ongoing campaigns.
The research enabled us to gain in-depth visibility into each affiliate’s structures, including ties with other notorious groups such as FIN7, Wizard Spider, and EvilCorp. We diligently shared our findings with authorized law enforcement agencies to ensure meticulous deconfliction.
Our key findings provided an essential contribution to:
- Mapping out unique TTPs of LOCKBIT affiliates
- Obtaining visibility on the affiliate infrastructures
- Obtaining source code and other -sort-of keys
- Monitoring of initial access brokers
- Notifying and warning all affected parties in advance
Our investigation of LOCKBIT presents a significant milestone. Thanks to this extensive research and collaboration with law enforcement agencies, we have contributed to continuous protection of our clients and to the timely notification of critical national infrastructures at risk across the globe.
Shortly, we say "Thank u, next"
@Europol@NCA_UK@FBI@KapoZuerich
One of the interesting things from that LLM MSFT blog is that MS was able to track all those prompts. 👀
Copilot and all these prompts people are typing thinking they're private :)
Interesting
If you like coding and art, you should know that there's a whole culture of people using javascript to code art. It's called #p5js. And I love disconnecting, putting on some good music, and coding up something wild. Here's one of the doodles I made.