I initially thought “RCE in Paint” meant tricking someone into opening a crafted image, and my confusion was just about terminology.
But Microsoft lists AV:N / UI:N. The FAQ describes sending a crafted packet to an “affected service”, with no user interaction.
Which service? How does that packet reach Paint and trigger code execution without anyone doing anything?
I really hope this is just an error in the advisory…
https://t.co/rTBO5WL23g
A lot of clever tricks instead of proper typing system. '*' as a non-password, using salt of another account, '*' or 'x' instead of proper error/result type. Tricksters programming in a nutshell.
Everyone is blaming OpenSSH for the sshhole vulnerability, but do you know who is really at fault?
musl
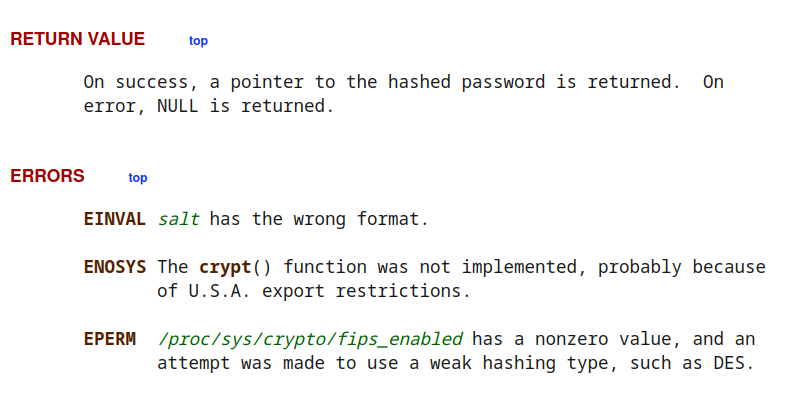
The POSIX standard requires crypt to return NULL on error.
musl returns "*" to not cause bad code to crash or worse, but in doing so, made well behaved code pay the price.
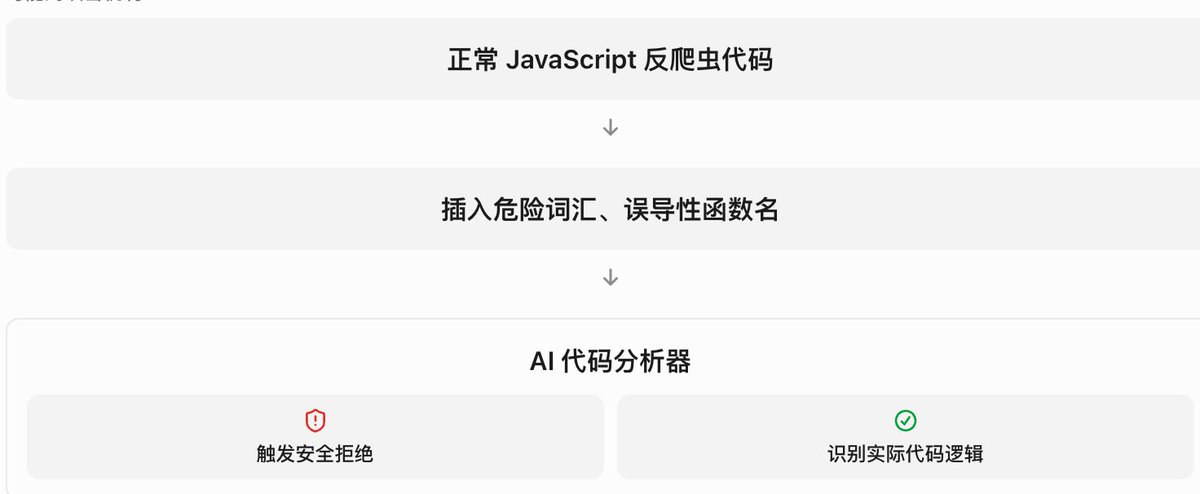
Restrictions-based defence technique. I saw similar technique in the wild when saving web-page from browser triggered antivirus due to EICAR signature embedded into every page.
Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing...
The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer.
- TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely.
- LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap.
- OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for.
These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
https://t.co/AYUgNsrA0f
Автоматический перевод стал настолько хорош, что явно стал заметен социальный сдвиг, что в твиттере, что в реддите - где люди общаются на разных языках практически без барьеров и потери смысла теперь.
77 open PRs for the JIT compiler from non-team members. Obviously all fully AI-generated. Every interaction is just me talking to someone else's Claude or Copilot).
oh my god this is worse than we thought
here's @Ledger $86M exploits explained
> cryptobilis was a reputable and authorized Ledger/Trezor/OneKey dealer for over 4 years
> they decided to sell the company to a Chinese guy (most likely patsy for DPRK) from northern China in MARCH 2026
> the "Chinese guy" modded the devices within the supply chain itself (physical), namely Nano X devices, to contain an implant module
> ledger validity/genuineness check CANNOT detect this because hw wasn't actually tampered with, just spied on
> quoting @MagicalTux:
" implant just monitors what's shown on the screen, will take note of the seed as it's shown to you, then transmits it to 3rd party"
> former owner chimes in on X (pic below) to say that "they were under a NDA" to not mention anything to anyone for 6 months
> they obviously didn't alert any of their partners that they were authorized to sell devices of... because NDA, duh!! its in the name!
> conveniently, funds start getting siphoned a few weeks before this magical NDA due date, and being laundered across all blockchains
This looks like this could be exactly what I'm investigating. Anyone affected, please contact me or open your ledger and send me pictures so we can confirm if there's a bug in there (pictures: ledger board on top, spy implant below).
https://t.co/mg2VRHLRHE
AHHGGG!
That piercing feeling when it's September 15 in parts of the world, but the rest of us have to wait until later for Marvel's #WolverinePS5. 🌐 🚀