📢Update on Video Pitch Submission
The Google Form for submission will be available on:
🗓️ 21st September, 7PM WAT
📌 Submissions will remain open until 9PM WAT, 21st September.
CC: Dr. @ireteeh
Signed: @An_gelos_07@NaphisaYakubu
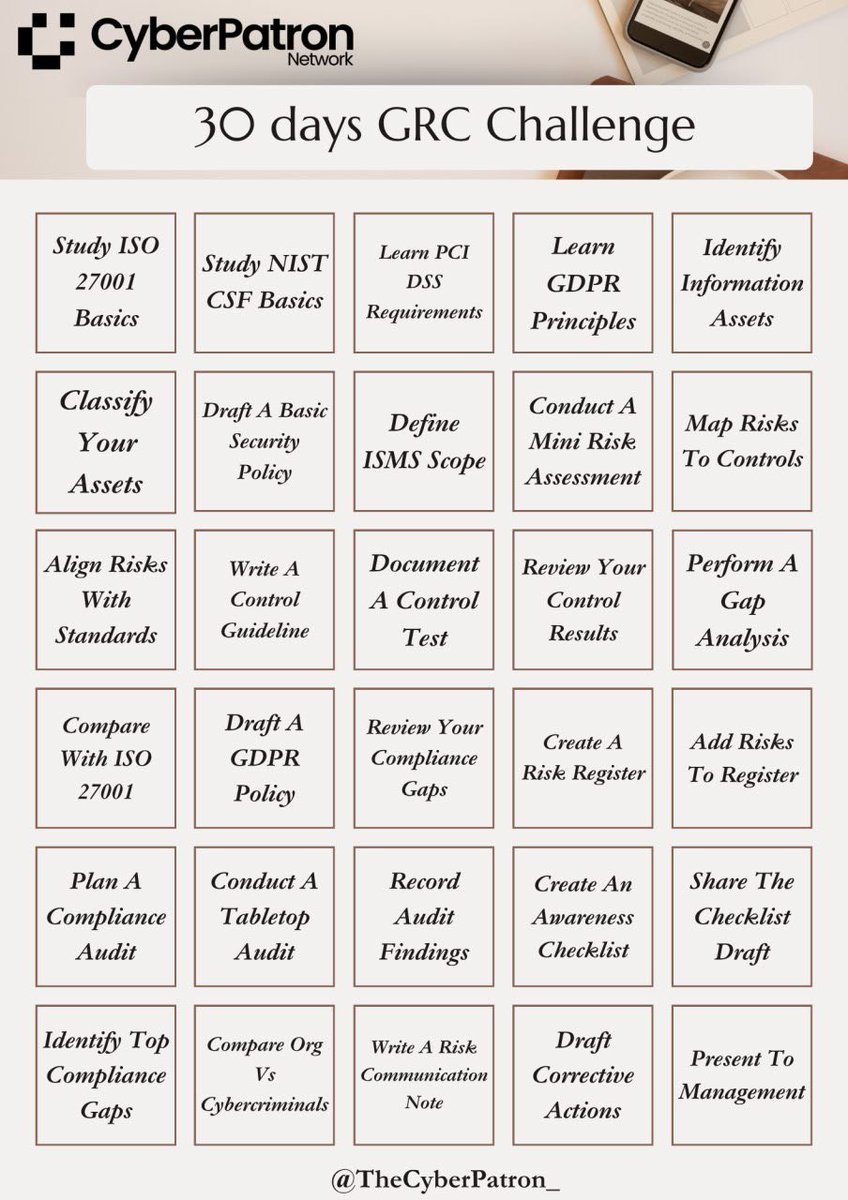
For those into GRC (entry-level and enthusiasts) here’s a challenge to help you study for 30 days.
Document your journey, share your daily tasks with me so we can review how well you’ve done and make necessary adjustments where possible.
Keep winning
Day 3/31 — When a City Went Dark (St. Paul (Minnesota, 2025)
It started like a whisper on the network, a flicker in logs that became a blackout. In late July 2025, St. Paul’s digital heartbeat stuttered.
The city systems went offline, public Wi-Fi and library services failed, bill-pay portals stopped working, and employees found themselves locked out of the tools they use every day.
The city shut down chunks of its IT estate to contain the threat.
The ransomware group “Interlock” claimed credit for the attack. The attackers were described as a “sophisticated external actor.”
The attackers published 43GB of data online after the city refused to pay ransom. This intensified the pressure on recovery teams scrambling to rebuild.
St. Paul chose to contain, rebuild and restore rather than reward the attackers.
Community Challenge
St. Paul chose not to pay the ransom. Was this the right call? Why or why not?
Day 2/31 When Airports Stood Still: A Cyber Wake-Up Call. (London Heathrow, Brussels, Berlin, Dublin 2025)
Last month, passengers at four European airports were stranded in long queues. Flights were delayed/cancelled and bags were unclaimed.
At first, it was dismissed as “technical issues.” In reality, it was a ransomware attack on Collins Aerospace’s MUSE system, the software that powers check-in, boarding, and baggage handling.
With systems down, the airports were forced to use manual approach. The incident exposed a hard truth, aviation doesn’t just run on engines and runways. It relies on secure systems; and when the system is vulnerable, the industry stalls.
The planes are flying again. But the warning is clear.
Community Challenge
Which element of the CIA triad was hit the hardest? Give reasons
Day 1/31 “When Innocence Was Exploited”
Kido International - 2025
A cyber-attack hit an institution built on care, where trust is everything.
Few days ago, a criminal group calling itself Radiant claimed to have breached Kido International (A nursery chain with 18 UK sites and additional sites overseas). The group reportedly stole personal information of about 8000 children.
The attackers published profiles of 20 children on a darknet leak site, and private data of employees. They contacted some parents and carers, threatening to post more information, unless Kido pays a ransom.
The stolen data includes children’s names, photographs, DOBs, home addresses etc. Multiple reports indicate the breach involved third-party systems.
Community Challenge
The attackers claimed they "deserve to be compensated for their pentest”
Was this truly a penetration test? Explain why or why not.
Thinking about joining the mentorship train?
With Dr. @ireteeh, it’s more than just career growth, it’s family.
Meet my family and co-hosts for the upcoming Space!
@An_gelos_07@Emmanuel_cysafe@AyobamiTo
@SymoneCapone Part of my goal for the year is to be certified to comptia security, this will be an opportunity for me and for growth. Thank you in advance 😍
🚨🇺🇸 Labor Day Giveaway 🇺🇸🚨
I’m giving away a CompTIA Security+ voucher! 🎉🎉
How to enter:
• Like & RT this post
• Comment or tag a friend
Winners announced this Friday!
Good Luck!
@NaphisaYakubu@AyobamiTo are the other gifts from Dr. @ireteeh's mentorship. They have held my hand, cheered me on. We have also whined each other but we will not panic 😅
Almost three years and going strong. This friendship must finally leave the watsapp chat 😅 Amen 🙏 2/2
GRC Project Ideas
Here are some Governance, Risk, and Compliance (GRC) project ideas that are ideal for students, beginners, or early-career professionals looking to build experience or portfolios:
1. Create a Risk Register for an Organization
Identify and categorize risks (technical, operational, compliance, etc.)
Use a spreadsheet to track:
Likelihood
Impact
Mitigation plans
Tools: Excel or Google Sheets
2. Policy and Procedure Documentation
Draft a complete Information Security Policy or Acceptable Use Policy
Include sections like purpose, scope, responsibilities, enforcement
Align with standards like ISO 27001, NIST, or COBIT
3. Compliance Gap Assessment
Choose a compliance standard (e.g., GDPR, HIPAA, PCI DSS)
Map the current state of a system or simulated environment
Identify gaps and recommend remediation steps
4. Third-Party Risk Assessment Project
Evaluate vendors or partners for security risks
Create a simple vendor risk questionnaire
Rate their security posture and suggest controls
5. Create a Governance Framework for a Startup
Define key roles (e.g., CISO, Data Protection Officer)
Set up reporting structures, escalation paths
Include security governance models and change management workflows
6. Build a GRC Dashboard
Use Power BI or Excel to visualize:
Risk levels
Compliance scores
Open vs resolved incidents
Automate report generation (if possible)
7. Simulated Internal Audit Project
Perform a basic audit of a department or system (even if fictional)
Draft an audit plan, checklist, and report
Include findings, severity, and recommendations
8. Privacy Impact Assessment (PIA)
Choose a web app or system and perform a privacy audit
Document how it collects, stores, and shares data
Make recommendations for GDPR/CCPA alignment
9. Security Awareness Training Project
Create a basic awareness program for staff (email phishing, password hygiene)
Include posters, presentations, and a quiz
Evaluate effectiveness with simulated phishing
10. Business Continuity & Disaster Recovery Plan (BC/DR)
Build a simple DR plan for a small organization
Include recovery objectives, roles, communication plans
Simulate a tabletop test scenario (e.g., cyberattack, power outage)
follow @elormkdaniel for more
Those of us that has turn chatgpt as our therapist and trusted friend that we share our personal identifiable information and sensitive personal identifiable information.
I hope you will think twice after reading this.
Hello Cyber Friends, today, I feel moved to share a few things that have set me up for success in this field 👇🏾
Invest in building your skills and deepening your knowledge.
Stay curious. Always be hungry for knowledge.
Your soft skills are as important as your technical skills. Don’t neglect one for the other.
You must have great work ethics to thrive in Cybersecurity.
Bring your A-game to the job. A right attitude is everything.
Learn public speaking. Practice makes perfect.
Master the art of research. In Cybersecurity, this keeps you one step ahead.
Consistency is key. Be known for the value you constantly deliver.
Apply for opportunities. Don’t be afraid to knock on doors.
Build relationships! Build relationships!! Build relationships!!!
The right connections can open the right doors.
When I started my career in Cybersecurity, I was afraid of public speaking, but I made a conscious effort to overcome that fear.
Within a year, I travelled to three universities in Nigeria to talk about Cybersecurity. I also conducted awareness sessions for several organizations.
To every aspiring Cybersecurity professional, please learn the art of public speaking. Don’t shy away from speaking up in meetings, meet-ups, or seminars.
Doing great work is important, but being able to confidently communicate and showcase that work is very important.
We are excited to announce Blessing Ehinomen Ebare as one of our speakers for the #CyBlack2025 conference.
Blessing is a senior technology consultant with over 7 years of experience in technology resilience and digital risk management, regulatory compliance,
1/5
It was fun and insightful co-hosting the cybersecurity and data privacy panel discussion for @ireteeh mentees with
I judged group 1: GDPR vs NDPR and I’m proud to say they won.
Well done guys and thank you for this opportunity @Angelos_07 and my mentor @ireteeh
https://t.co/e4USpDHHmZ
We have our results 🥳🥳
2nd runner up : group 2 - Much Ado about third party risk management
1st runner up: group 3: GRC and AI?
Winner group 1: GDPR vs NDPR
Thank you so much for joining our space