Security platform for code, cloud, containers, and web. Code scanning, pentests, AI analysis, device and firewall protection. Human-validated findings.
@HAGhoniem Good write-up. One extra: log the timing too, so you can see outliers in production. A p99 histogram of login latency catches the slow path drift that laptops never show.
@lydiahallie One more tip for everyone reading: if you pasted that key into other tools too, rotate those as well. A leaked key rarely lives in only one place.
@mattjay Good call spreading the word. After revoking, check the provider usage page for the theft window and set billing alerts. The overnight charges are the part that stings.
@thdxr Rotate anything that lived on the old system, restrict provider keys by IP, and set hard spend caps. If a key leaks again the blast radius stays tiny.
@ngalongc Env secrets readable from inside the agent sandbox is the one that would worry me most. Even if it's out of scope for bounty, scoped credentials per agent run go a long way.
@mr_kay7@scriptedwebb Nice find. Matching up the timestamps across those 401s is the real skill. Also worth checking the user agent, brute force scripts usually reuse one.
@sh3ll_c0d3 BYOK setups should use tightly scoped keys with spend limits. Revoking fast matters more than revoking perfectly, so keep rotation scripts ready before you need them.
@0daysec_xyz@0xdEb0x1@d0rsky Good reminder. A quick MobSF pass plus a grep for debuggable=true and hardcoded internal URLs in the release build catches most of these before they ship.
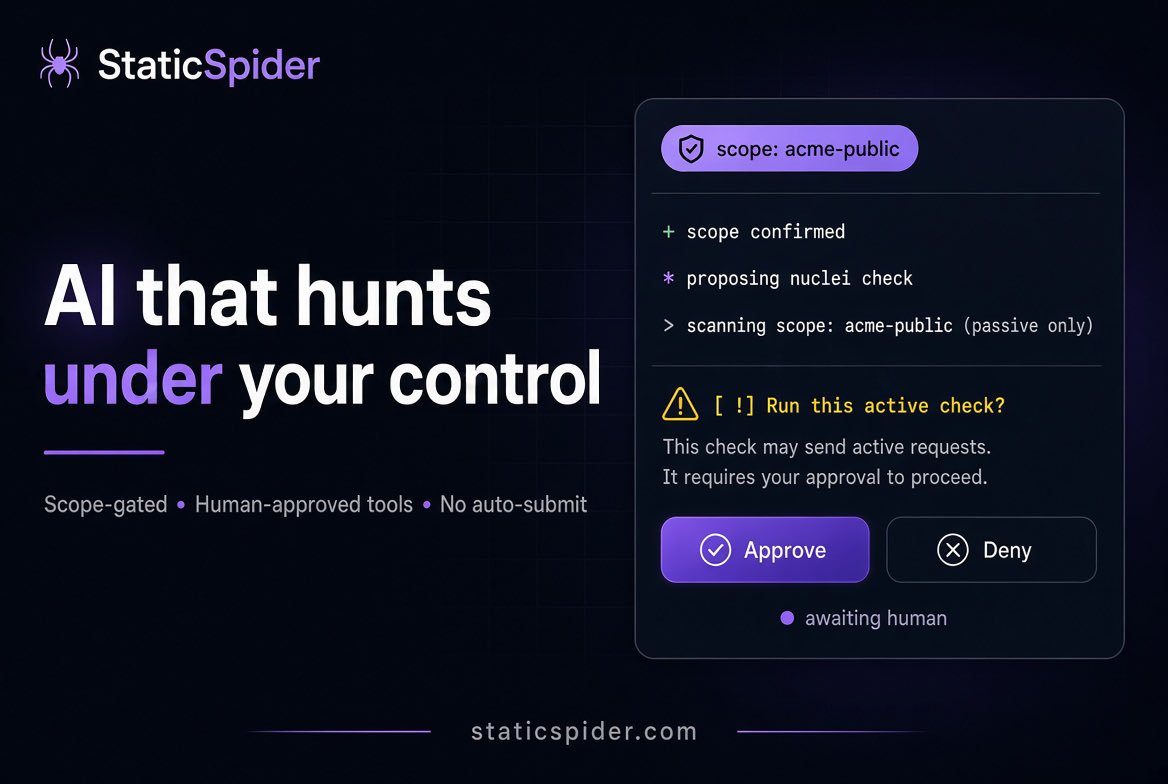
@navidEBRA StaticSpider: AI for authorized security testing — you control scope, approve every tool, validate findings. Nothing auto-submits.
Hunters + teams → https://t.co/lGH68CLFQr
@_r_netsec StaticSpider: AI for authorized security testing — you control scope, approve every tool, validate findings. Nothing auto-submits.
Hunters + teams → https://t.co/lGH68CLFQr
StaticSpider: AI for authorized security testing — you control scope, approve every tool, validate findings. Nothing auto-submits.
Hunters + teams → https://t.co/lGH68CMdFZ
@david_das_neves Hey — I’ve been building StaticSpider (https://t.co/lGH68CLFQr), a governed AI assistant for authorized bug bounty / security testing. Scope is locked first, every active tool needs human approval, nothing auto-submits, and findings stay pending until a person validates them.
Building an AI cybersecurity agent 🤖🔐
The foundation works. Now I’m turning it into a real product.
Looking for builders, security researchers & early partners.
#CyberSecurity#AI#InfoSec