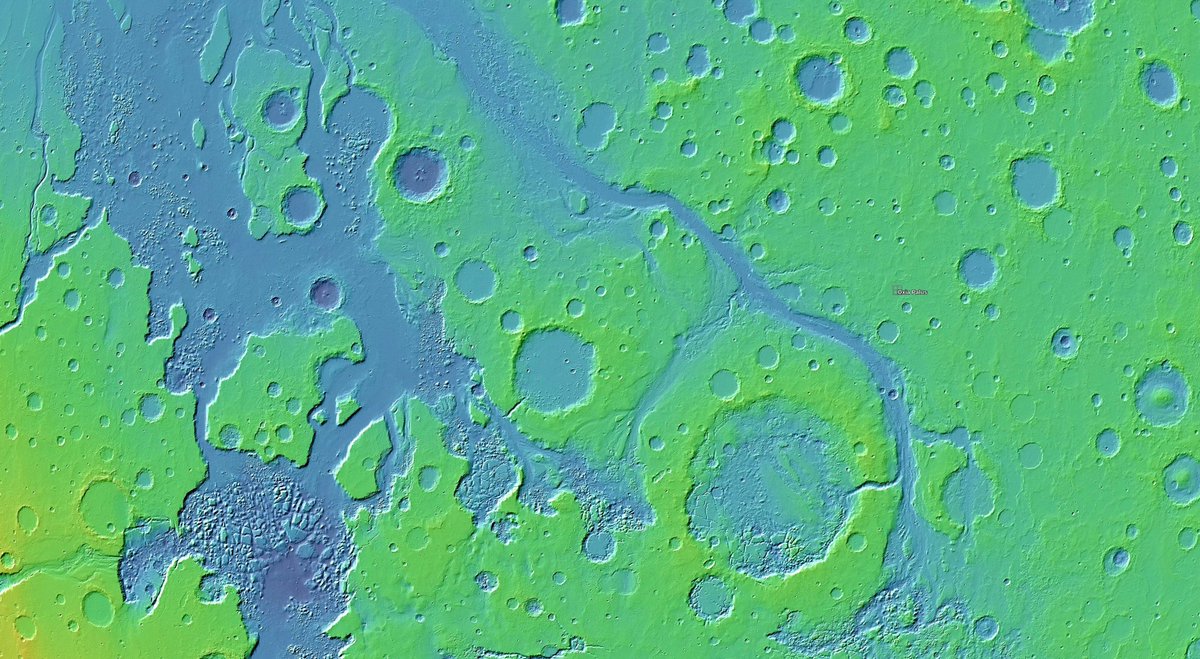
You can now enjoy a colored relief map render of this dataset streamed through Google Earth. Download the .kml file (https://t.co/tzxDvt7JVX) and open it in your Google Earth Pro client. Enjoy!
Just going to preregister here that I believe the computer security overhang is not a few dozen bugs that get patched and then we're good, there are 100,000s of vulns that are extremely discoverable with infinite free tokens and we're probably going to have to move away from systems that presuppose that perfection is possible.
Fascinating stuff. I'm not an expert, but I remember that dodgy CAs have been a known problem since at least 2010, data retention/version control leaks at least as long, and PHP has always been adjacent to self harm. It'll be interesting to see where we land in 12-18 months on this stuff.
Fascinating stuff. I'm not an expert, but I remember that dodgy CAs have been a known problem since at least 2010, data retention/version control leaks at least as long, and PHP has always been adjacent to self harm. It'll be interesting to see where we land in 12-18 months on this stuff.
Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl https://t.co/vhiGLxNhIS
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: https://t.co/C512KFOEq5, Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased https://t.co/28tjHqd5Wr table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.
Biggest mistake I see technical start ups make in hiring: not realizing the recruiter is the face of the company that your prospective candidates see first.
If your company depends existentially on attracting and closing top tier technical people, your recruiter needs, at the very least, to be legibly one of them, able to speak the same language, and able to articulate that your company values talent.
I can count the number of times I've spoken to a hiring person at a technical company who could do this and was not currently employed there as an engineer on a single finger.
~20 years ago I had a recruiter tell me I was too junior for a specific role they had.
They didn’t realize I wrote the tech test for the company that was trying to hire (they had outsourced the test). I said I wouldn’t apply anyway due to the conflict of interest of doing the engineering test I authored.
The recruiter then went absolutely ballistic that nobody “senior” could seemingly pass the tech test and was pissed I made it too hard for the folks she’d already been putting forward. Nobody had passed it.
Within 12 months I’d left to start my first business at 23. Never looked back.
@TMoldwin@jayrtfm It's the job of the PI to get grants. Poll after poll says most scientists (~80%) would do something else given the choice. Getting grants is about as different to making a commercial sale as any activity can be.
@jayrtfm There are easily a hundred times more grad students and postdocs than we need to maintain scientific discovery and this fact is borne out by the irrelevance of 99% of published papers.
I recently spent some time with former colleagues from academia. All of them brilliant, peak human capital. Almost all of them fundamentally unable to plug into the economy, inoculated against productivity by a youth spent experimenting in laboratories instead of building wealth for society. Dealing with real people in the real world.
90% of them have left academia in the last 10-15 years, and 90% of those are functionally unemployed. Grad school does a lousy job of training scientists to be professors (since most of them don't get the good postdoc or tenure track position) and an even worse job of preparing people for real life.
We complain that our societal infrastructure is collapsing, our state capacity is low, our incumbent industries are faltering. Where are the next generation of leaders that can push us forward?
A huge fraction of them were conveyor-belted into academia by schooling systems that have no mechanism to channel ambition and 99+%ile competence, and our universities are mostly hedge funds with glorified psych wards/academic departments on the side, running an insane pyramid scheme that exists only to prove, over and over again, the Shirky Principle: Institutions will try to preserve the problem to which they are the solution.
We literally poured trillions of dollars into state-funded research and effectively neutered our elite civilian technical leadership development programs.
I recently asked a few academic friends if they were finding AI useful in accelerating their programs of research. You know, to solve the Big Problem their entire field exists to solve?
Some were. But most were complaining about how it created pedagogical issues, explaining how their department decided to ban the use of AI, or how it took 18 months to approve an enterprise account, or how they tried Gemini 2 on a puzzle a year ago and it wasn't very helpful, or repeating nonsense about datacenters and water consumption, or supposed IP theft by model companies, as though that has any bearing on their ability to, eg, accelerate a cure for cancer.
Elon sometimes calls AI a supersonic tsunami - a huge wave you don't see coming. I see it coming. But even the people who you'd think have been waiting for this their entire careers are steadfastly looking in the other direction.
During a business trip I heard about multiple companies who are struggling to hire people. Jobs available but they can't fill them. There is a huge disconnect in the job market somewhere- the systems responsible for efficient and effective recruitment have completely failed.
@shantirrao@NoahOlsman I know a good number who have done economically better than a perma-postdoc, but consulting with Deloitte or whatever, is this really the best we can do with kids who can do integrals in their heads at 10?
This podcast inspired me to do something that's been on my bucket list for 15 years - add a geology layer to my mapping tool. Explore Cerro Gordo's tunnels and geology at https://t.co/veVAqJWAME.
In 2018, Brent Underwood did something nuts. He bought the old sliver mining town of Cerro Gordo for $1.4m. In so doing, he became the owner of a ghost town and many miles of mines.
Brent has spent the last few years exploring the mines solo and trying to restore the town, which once played host to 4,000 people. Along the way, he’s become a YouTube star and a best-selling author. We went to Cerro Gordo to interview Brent and live at the mines for a couple of days.
Here’s our full episode. The Core Memory pod is available at all fine pod retailers
@mikejt4 Elon was exposed to the entrepreneurial mindset in SA as a child, in a world that, for all its faults, didn't insist that people be insulated from any activity with real stakes until the age of 21.
@tetheredtoed1 They've never had a real job and when they try to get one they almost invariably fail. By raw talent they should be leading Fortune 500 companies and in practice they end up doing data analysis contracting gigs between long periods of unemployment.
There is unbelievable value to be unlocked by intermediating the back end hassles of running any business. Let's let the APIs talk to each other about this nonsense and spare founders avoidable brain damage. Focus on making the product as good as it can be!
The likely outcome is that a tiny core of AI forward people in each discipline will blitz their respective fields, Chandrasekar style, and we'll have to endure mopey think pieces from people sad that the question they built their life around nibbling around just got nuked from orbit.