Since the @Apple Bug Bounty Program is by far the worst program I've ever hacked on, I am going to be dumping all of the data/POCs/report write ups etc for everything found during the 4 months of hacking them. This will include POCs for vulns that didnt meet their bar for a bounty so wasnt reported to them, so you may be able to find ways to escalate some of them. Ill be uploading the data all this weekend.
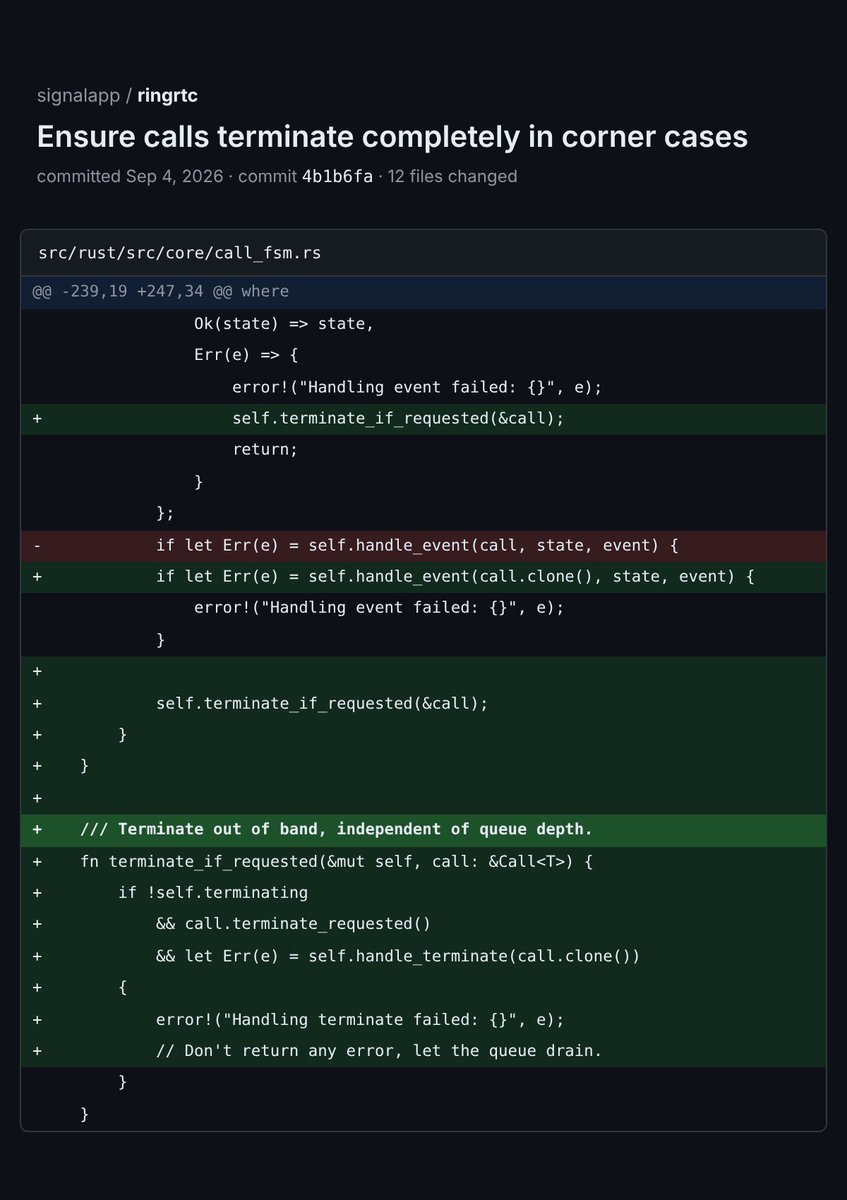
‼️ A critical Signal bug could keep your microphone, and possibly your camera, live after you hang up.
The other caller can flood the call's event queue so your hang-up is never processed.
Dubed CVE-2026-113380 it scored 9.3 and got fixed in September.
And as if all these critical vulnerabilities weren't enough, we've also had several reports about threat actors using AI agents to compromise systems at scale.
This is actually the part that worries me even more.
Some interesting reports from the last few days:
01) ARTEX / ConnectWise
Microsoft reports that Storm-0940 used ARTEX in a large-scale campaign targeting more than 2,250 Microsoft 365 tenants. Up to 2,900 authentication attempts per minute, with privileged cloud access achieved in under three hours in some cases.
https://t.co/vPafbvD1oG
02) ARTEX / South Korean Finance
CrowdStrike found evidence of AI-driven attacks against South Korean financial organizations, including exposed Claude Code sessions and ARTEX configurations. DeepSeek, GLM and Grok were used in the attacker's setup.
https://t.co/kOiEqSEwUi
03) Cairn / 100+ Compromised Companies
NorForge investigated exposed Cairn instances used for autonomous hacking campaigns. More than 1,100 attack projects in one cluster alone. Reuters identified over 100 companies whose websites had been compromised.
Estimated AI costs: around $5 per task, according to NorForge. That's ridiculously cheap.
https://t.co/54Ir7IeY4Q
04) Four More Agentic AI Campaigns
CrowdStrike documented four additional threat actors using AI agents for real intrusion campaigns, including attacks against healthcare organizations and government entities.
https://t.co/rte8LIYL90
What concerns me is how quickly the economics of offensive operations are changing.
Finding vulnerabilities, testing attack paths, adapting payloads, trying something else when an exploit fails, and eventually deploying a webshell. Much of this can now be delegated to agents that keep working for hours.
And with open-weight models and freely available agent harnesses, the cost of running these operations is dropping significantly.
We've been talking about AI changing offensive security for quite a while. These reports show that it's already happening in real-world intrusions.
And I'm pretty sure we're only seeing a fraction of it.
they’re calling it “Black October” and i don’t think people realize how serious this is
in the last 48 hours there have been over 27 major cybersecurity incidents. not in a month. not in a week. in 48 hours
any ONE of these would normally be the biggest story of the year
PHP: critical vulnerability in the software running 80% of the web. severity 9.2 out of 10
Node.js: high-severity flaw letting attackers take over servers remotely. affects versions 22, 24, and 26
Java: also compromised. three of the most used programming languages on earth hit at the same time
GitLab: a perfect 10 out of 10 severity hole in every version since 2014
Railway: hosting platform compromised. API keys for OpenAI, Claude, Stripe potentially exposed
Signal: a bug that could leave your mic and camera on after you hang up
WordPress: hackers stole a plugin maker’s keys and planted backdoors on websites
LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
and that’s not even half the list
thousands of AI agent swarms are reportedly scanning and attacking vulnerable servers right now. automated. around the clock
security researchers are saying this might be the early stages of a global cyber incident that nobody fully understands yet
if you run a website, use cloud services, store API keys on hosting platforms, or use any software built on PHP, Node.js, or Java you are potentially affected
update everything. rotate your API keys. change your passwords on critical services. enable 2FA everywhere you haven’t already
this is not a normal week on the internet. this is something different
This is why I'm glad I'm retired
I would spend entirely too much time, at great personal sacrifice to chase this crap ...All day
Props to all my buds still doing it
Take care of yourself!
🚨 EXPOSED SERVERS REVEAL AN AI-ASSISTED RANSOMWARE WORKBENCH TIED TO INC AND THE GENTLEMEN
A threat research report published Oct 20, 2026 describes seven exposed adversary servers used by affiliates of the INC and The Gentlemen ransomware operations, with 62 targeted organizations and more than $23,920 spent on commercial AI services. The investigation began in late September, after operator OPSEC failures left the servers' open directories exposed.
What the report says the servers held:
• OpenCode AI session logs (8,257 messages across 133 sessions) using commercial models: the AI planned recon, generated commands and triaged stolen data, but waited for the human operator's approval before every step
• Source code for "Phantom", an autonomous red-team framework with 18 skill modules, alongside Ghost C2, RevSocks, MCP servers and exfiltration tools; plus extortion procedures and scripted vishing
• 46 custom INC encryptor builds for six victims, packed on Sep 30 for a planned Oct 1 deployment wave
• A Sep 30 screenshot showing the encryptor running on one victim workstation
• Operator records of mass exploitation of FortiClient EMS (CVE-2026-35616), SimpleHelp (CVE-2024-57727) and cPanel/WHM (CVE-2026-41940); those counts are the operators' own and not independently verified
⚠️ Analyst Note:
This is firsthand research from the team that found the servers, not independent validation. The researchers link the workbench to both INC and The Gentlemen operations but rate a formal alliance as low confidence; a shared tooling environment used by several partners is the more likely model. Staged builds do not prove deployment: the planned Oct 1 encryption wave is unconfirmed beyond the one workstation screenshot. The report grades organizations by depth of activity, including reconnaissance-only targets; DDW does not name them, and none should be read as a confirmed breach. Defenders: patch FortiClient EMS, SimpleHelp and cPanel/WHM, check EMS for unauthorized admin accounts, and lock down RMM tools.
Source: https://t.co/y4cRDvZ68z
#DDW #DarkWeb #Ransomware #AISecurity #INCRansomware #TheGentlemen #ThreatIntelligence
This is kind of hilarious
AWS, are you clueless?
They had it and exploited it because they FRIGGING found it and were using it
Zero day is only the day that the WORLD finds out!