Because sometimes you need AES keys from latest Unifying dongles (fixed 12.11) 🥝
"Fun" fact, you need to plug the dongle to a *non* AMD/ASMedia USB controller 🤷
cc: @FMehault ;)
Two new logical flaws in Kerberos just dropped at Black Hat. Low-privileged user to full domain takeover, including domain admins.
If you're doing Active Directory pentesting, Kerberos attacks, red teaming, identity security, or detection engineering, read this.
KerberLoss (CVE-2026-25177) and ResetNightmare (CVE-2026-27912). Both are logical bugs, not memory corruption. Described as surprisingly easy to exploit.
https://t.co/dgJC3JHjOf
#Infosec #RedTeam #DetectionEngineering
If you haven't patched yet.
Your Active Directory is currently indefensible.
https://t.co/sbhYArMTNh
🤷♂️
Join @techspence and I @ @wpninjasus in Jan as we dig into what this means and what you can do...
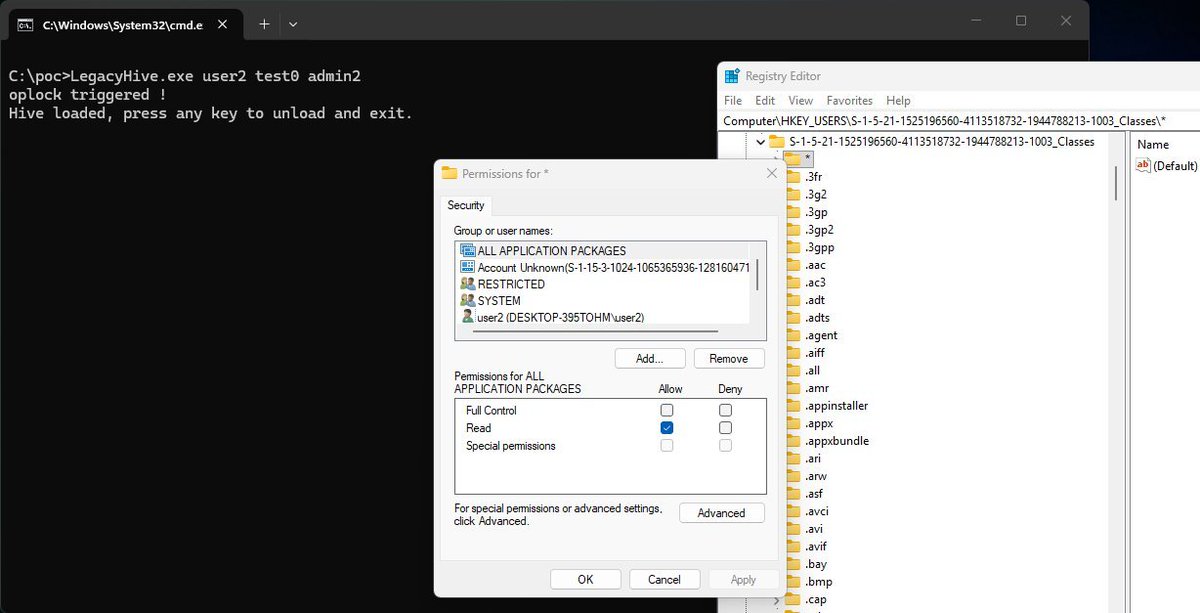
‼️ Nightmare-Eclipse just dropped "LegacyHive," a new Windows privilege-escalation zero-day PoC that targets the Windows User Profile Service, the component that loads a user's settings during sign-in.
The PoC reportedly uses a carefully timed path-switching trick to make Windows mount another user's Registry file, potentially an administrator's, under a standard "helper" account.
Nightmare-Eclipse claims it works across supported Windows desktop and server builds patched through July 2026.
Nightmare-Eclipse says a private version could load arbitrary Registry hives, but that broader version has not been published.
Interestingly, Nightmare-Eclipse previously told us that vulnerability names are inspired by random events in his life. "LegacyHive" appears to break from that convention.
Deja vu: Microsoft patched this broad ProfSvc trust-boundary failure in 2015 as CVE-2015-0004, which also loaded another user's hive. LegacyHive appears to use a new path-swap to revive that bug class.
As of writing: no CVE, no Microsoft advisory, no comment.
Windows DNS Client RCE -- CVE-2026-41096 POC -- qdcount=0, a DNS OPT resource record (type 41), and 0xff bytes via example response -- https://t.co/wzSIXuCLPo
Just pushed a minor update to #mimikatz 2 🥝(no - it's *NOT* the version 3) to support specific GMSA DPAPI passwords in LSA secrets to be able to to decrypt Masterkeys
> https://t.co/UNUIxSOhtS
Only for @topotam77 convenience ;)
Another zero day exploit released by some nerd (can't remember name right now) because they're annoyed with Microsoft. It's been confirmed by other nerds. It is yet another legit zero day. Whew.
https://t.co/Zllhns1ztn
🛠️ Fritter - a heavily modified fork of Donut shellcode generator
✅ It generates position-independent shellcode for in-memory execution of VBScript, JScript, EXE, DLL, and .NET assemblies, but with a heavy focus on evasion and signature resistance https://t.co/AUZbMAwLjw
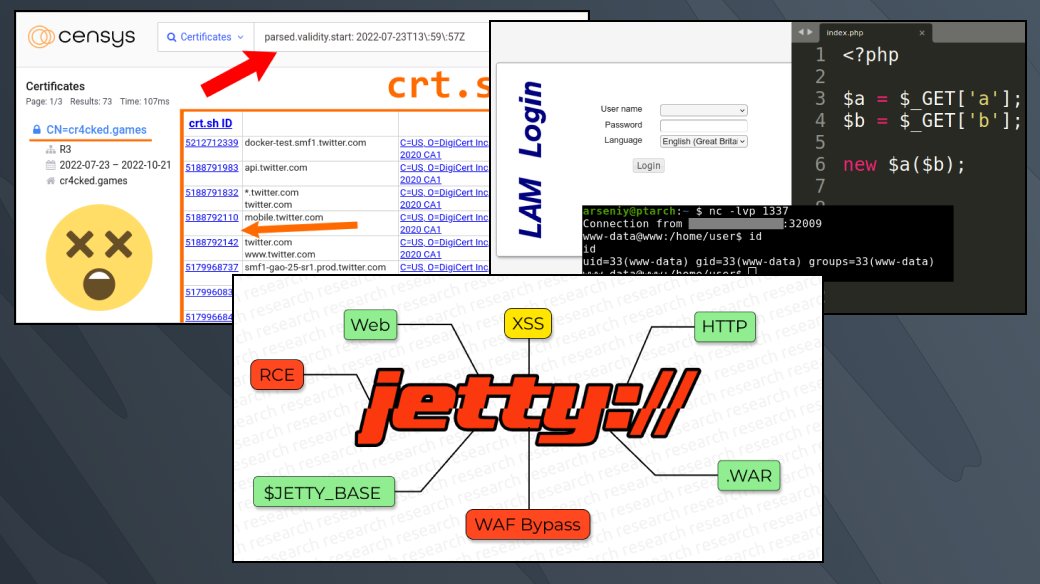
🏆 Our nominees for @PortSwigger Top 10 of 2022!
1️⃣ Jetty Features for Hacking Web Apps
2️⃣ Exploiting Arbitrary Object Instantiations in PHP without Custom Classes
3️⃣ Discovering Domains via a Time-Correlation Attack on Certificate Transparency
Vote here:https://t.co/yOyXA5bQJ3
Actuellement en train d'implémenter "Impersonate" de @Defte_ présenté à @_leHACK_ sur l'outil #CrackMapExec (cc @mpgn_x64). Merci encore pour vos travaux respectifs 😉! #CME