do you realize how insane this is?
- we can solve crimes
- we can locate people who need rescuing
- we can expose fake location claims
and the gov can spy on us even more :)
@TheCoolestCool@ahrefs Maybe a hot take, but i feel impressions always mattered. Obviously, clicks are best, but if your impressions aren't going up, your SEO is probably not working...
2027 will be an incredible year for you if you’re technically gifted, neurologically forked and have access to exogenous focus enhancers
2027 for everyone else will be, idk, just be there for them
(nothing changes for the amish)
BREAKING: OpenAI says it found a critical flaw in Brotli, a widely used compression library built into software like Node.js, Bun and Envoy.
The bug could let an attacker take over a system just by sending it malicious compressed data, with no login needed. That works both ways: a hacker could hijack an unpatched server, or a malicious server could hijack an unpatched user’s device.
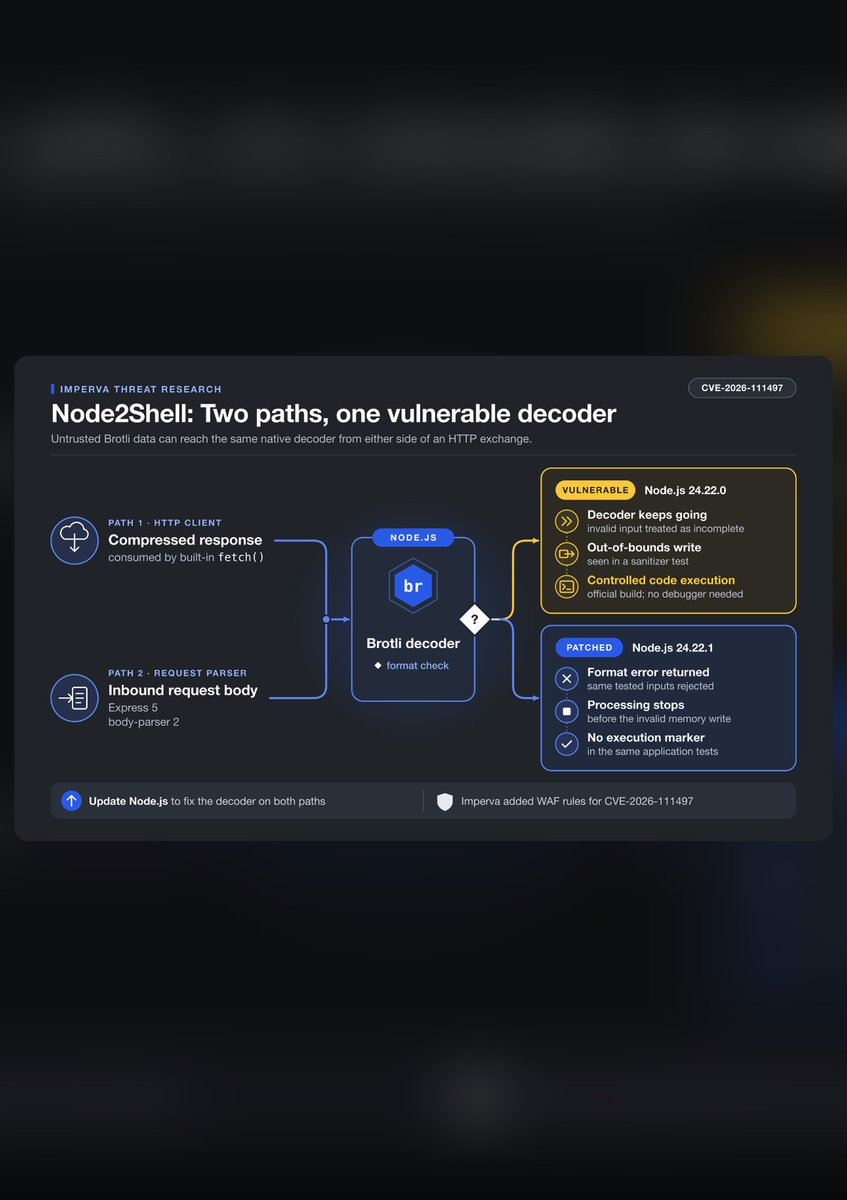
‼️ After PHP2Shell comes Node2Shell, a critical bug found by OpenAI's Codex Security that can let attackers run code in Node.js apps.
It was successfuly demonstrated on the official Node.js 24.22.0 image.
Node 20, 23 and 25 (all EoL) get no fix.
Node.js Security Advisory: a high-severity RCE flaw in Node's Brotli decoder affects Node.js 22, 24, and 26.
Vercel WAF rules are live for every project and block known exploit patterns.
https://t.co/JtfEshHnOC
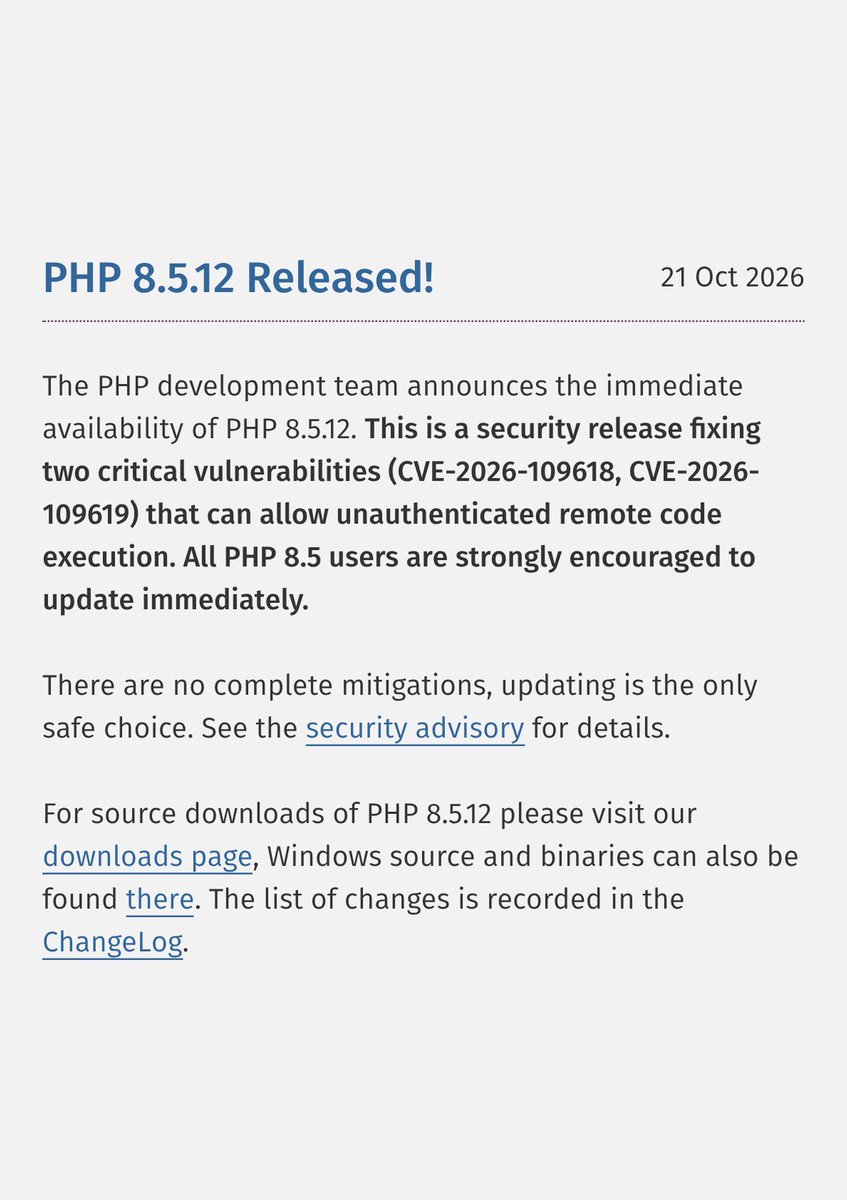
‼️BREAKING: PHP has released its fix for the two leaked flaws, which can let attackers run code on servers without logging in.
"There are no complete mitigations, updating is the only safe choice," PHP says.
Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now.
PHP says Apache with mod_php is most at risk, with a demonstrated exploit that fires before any application code runs.
PHP 8.1 and older get no official update, though PHP has published source backports for 7.4, 8.0 and 8.1.
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.