Día 1 creando una app desde 0 hasta subirla en las stores.
Normalmente todos mis trabajos, tareas o proyectos siguen un plan, en este caso al ser una app desde cero, voy a seguir este proceso:
Descubrir -> Diseñar -> Desarrollar -> Testear -> Lanzar -> Iterar
Che, ayer en Telefe estaban pasando Los Simpsons y CORTARON la parte donde cuentan que invadieron las Islas Malvinas.
Busqué el capítulo original e hice una comparación para que vean. Se sabe que no pasaban el capítulo donde nombran a Perón, pero y ahora? Qué pasó acá?
Tenemos 4 juegos más para jugar directamente desde navegador con online:
Resident Evil 4
Tekken 4
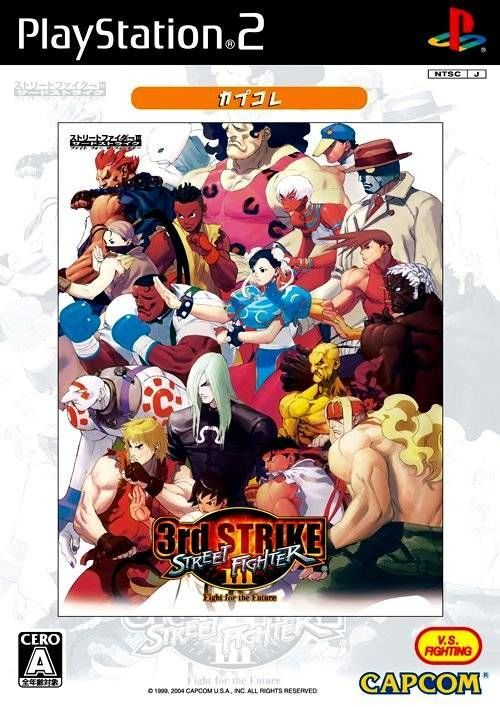
Street Fighter III 3rd Strike
NFL Street
The Warriors
Madden NFL 08
SSX3
Enlaces debajo (y en mi perfil)
First of Kind: The @rauchg interview
Season 3 starts now. I sat down with Guillermo in San Francisco to talk about layout shift, random acts of AI, and a dragon painted in a single stroke.
00:00 Human Effort Is Still Underrated
00:44 Chief Executive, Chief Designer
02:33 Two Bets: Software and English
05:15 Gmail Was My Siren Call
11:06 Exposure Hours
14:49 Layout Shift / One Stroke Dragon
17:10 No Random Acts of AI
25:17 Can Agents Have Taste?
30:15 Software Factories and Manufacturing Agent Customers
34:59 Everything Is Communication
38:04 A New American Story
41:52 Lifemaxxing
Guillermo Rauch is the founder and CEO of @vercel. Growing up in Argentina, he taught himself English in order to teach himself programming, then went on to create @nextjs and other foundational technology for the real-time web.
In our conversation, Guillermo explains why he designed Vercel’s first command line before writing any code, why layout shift erodes trust, and why his company won’t commit any “random acts of AI.”
G is not just a chief executive. He’s a chief designer.
—
Guillermo Rauch: One Stroke Dragon
First of Kind, S3:E01 @firstofkind
Hosted by @soleio and produced with @room3nyc
Powered by our sponsors:
@framer@noondesign@bot@tryramp@vercel@meetgranola@profound
Día 11 creando una app desde 0 hasta subirla en las stores.
Terminé de diseñar en Figma algunas pantallas, principalmente de los flujos de Onboarding (splash screen) y Accesos (welcome, login y sign up)
Tenemos 9 juegos más para jugar directamente desde navegador, todos con online:
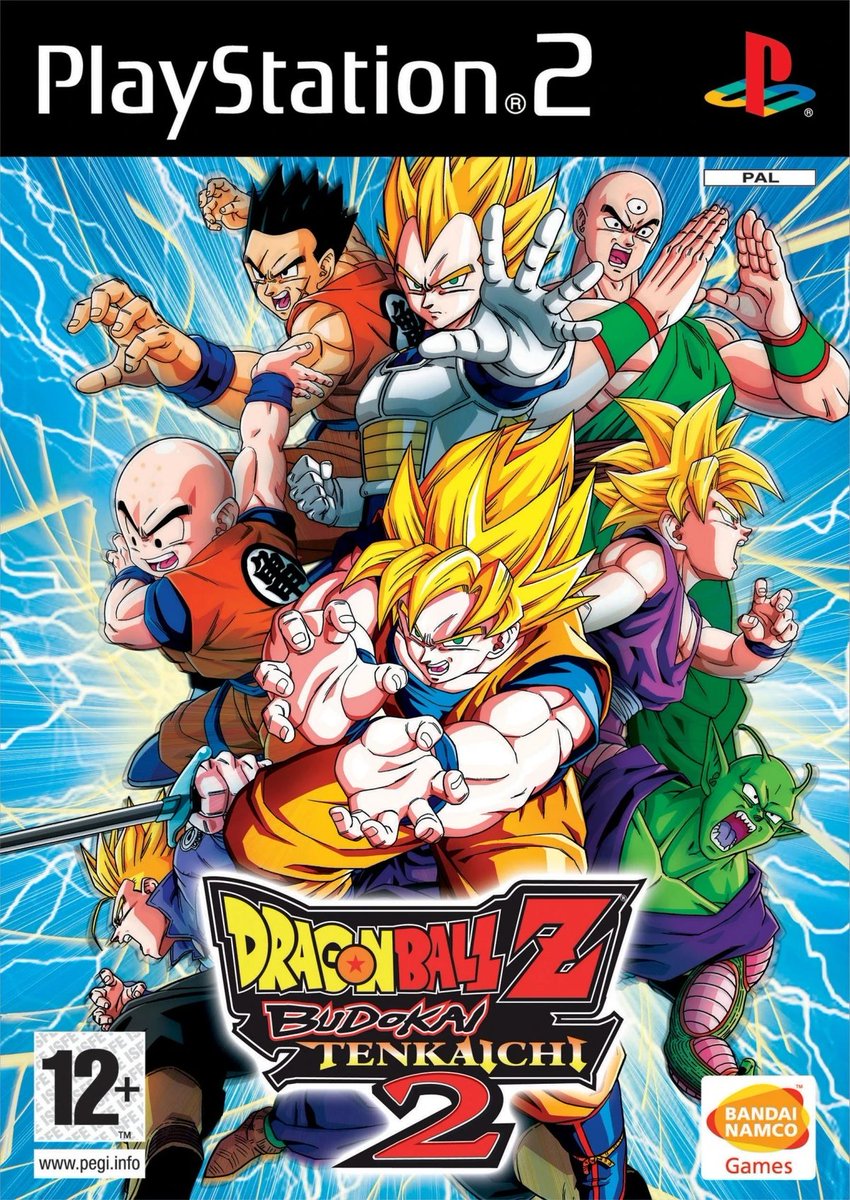
DBZ Budokai Tenkaichi 2
DBZ Budokai 3
Marvel vs. Capcom 2
Street Fighter Anniversary Collection
FIFA Street
FIFA 11
FIFA 12
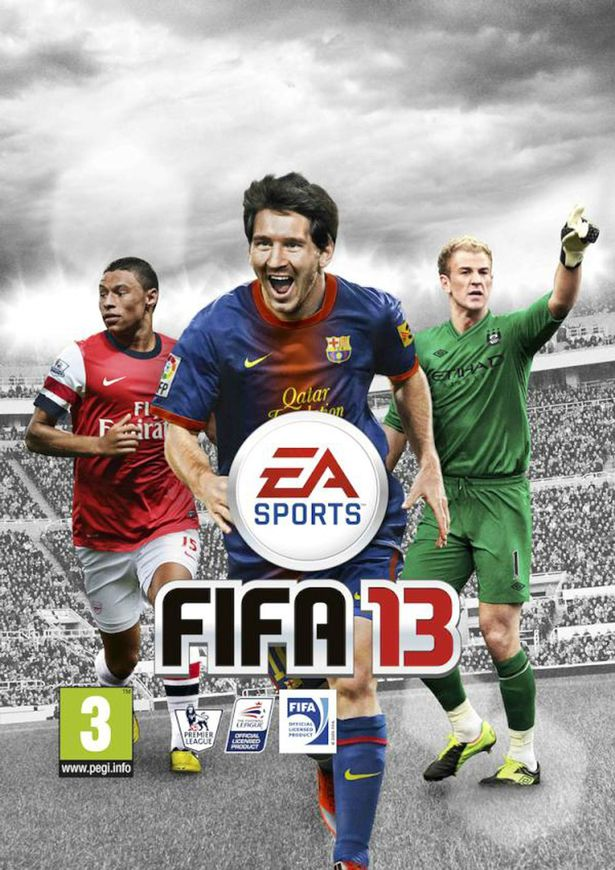
FIFA 13
Battle Stadium D.O.N
Enlaces debajo (y en mi bio)
Recap por si te lo perdiste:
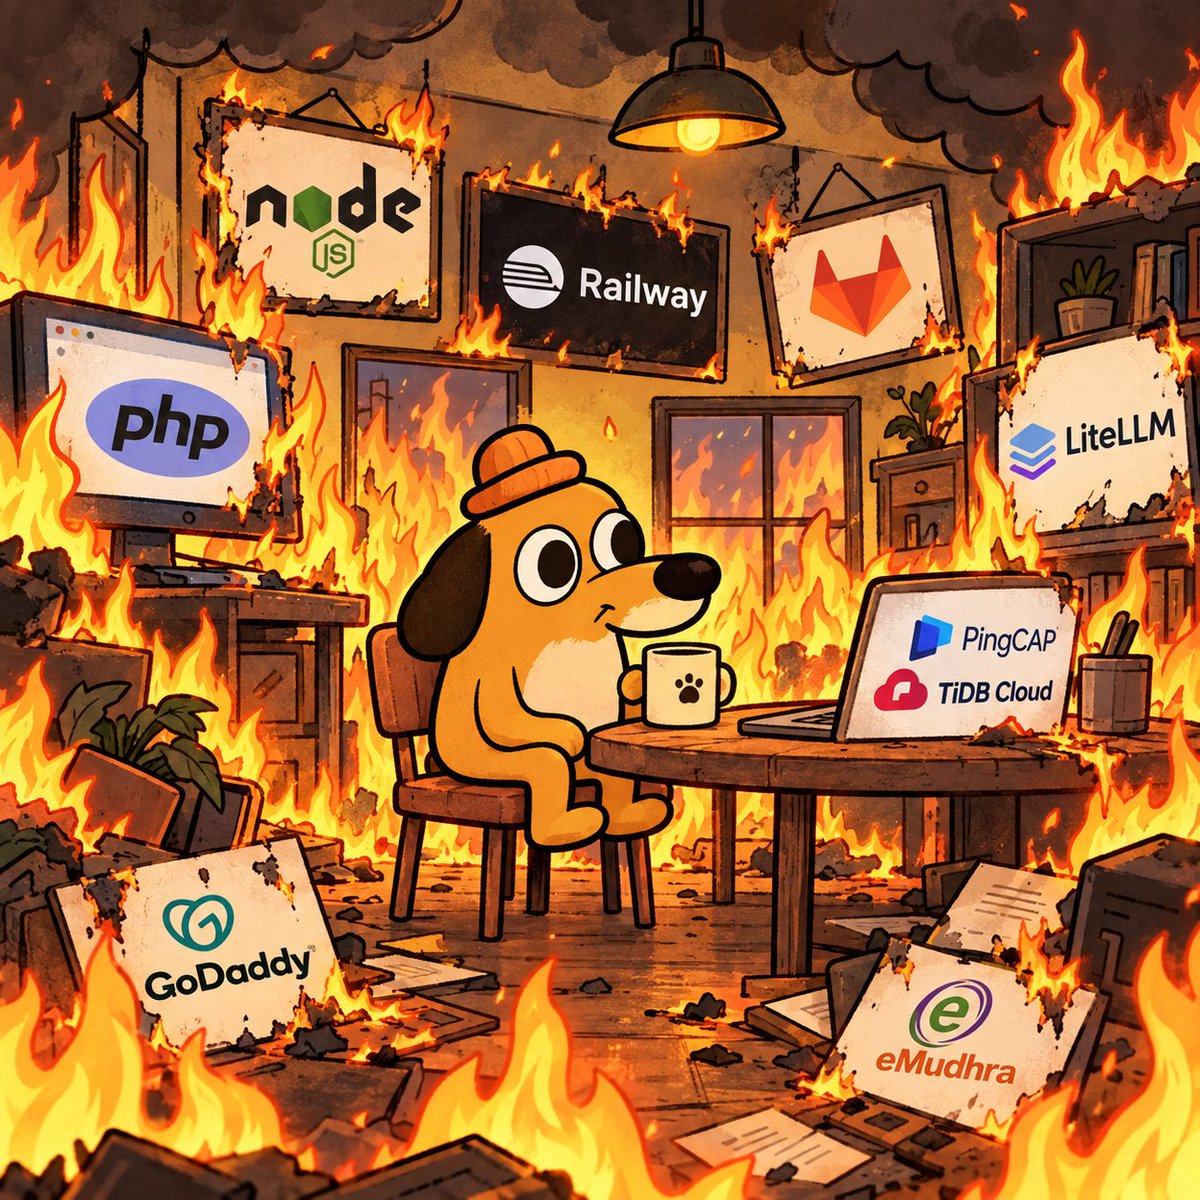
> RCE crítico en PHP
> RCE en Node.js (Brotli)
> Railway hackeado
> GitLab: CVSS 10.0
> LiteLLM comprometido (otra vez)
> PingCAP/TiDB Cloud hackeado
> GoDaddy revoca 400k certificados
> eMudhra: llaves de CA comprometidas
Todo en ~72 horas.
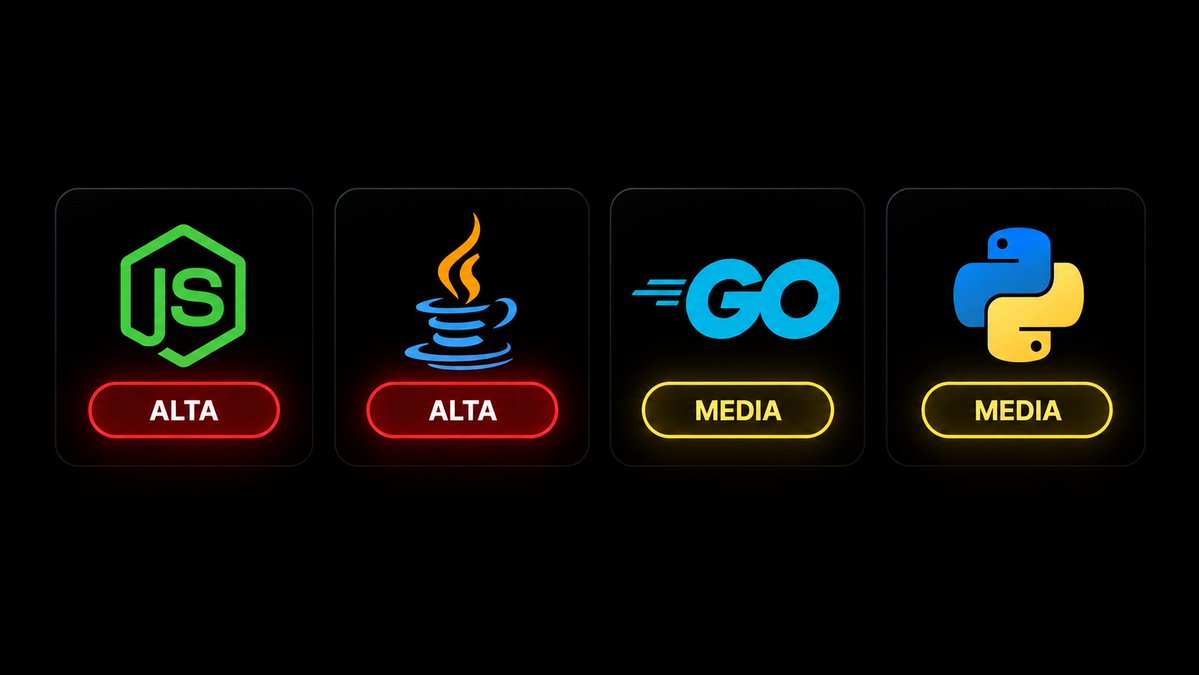
¡Semana complicada para la seguridad de lenguajes de programación! No solo PHP ha tenido problemas.
Tenemos parches también para:
- Node.js (Alta) Ejecución remota de código y fallos TLS
- Java (Alta) 49 fallos explotables en remoto sin auth
- Go: Certificados comprometidos
- Python: Certificados comprometidos
¡Si tienes apps en producción, toca revisar y actualizar!
Hecha en Argentina, para devs argentinos 🇦🇷
API oficial de WhatsApp de Meta: REST, webhooks y MCP, docs en castellano y soporte humano.
Plan fijo, 0% de recargo sobre lo que cobra Meta. 10 días gratis, sin tarjeta.
PHP’deki güvenlik açığı ciddi. ChatGPT’ye iş belgelerini ya da ailesiyle ilgili konuları danışanlar için bilgi sızıntısı riski gerçekten büyük.
Hemen yapabileceğiniz bazı ayarlar var:
Not just PHP. Node.js has also announced security releases for October 21, with HIGH-severity vulnerabilities affecting its 26.x, 24.x and 22.x release lines.
If you run either stack in production, keep an eye on official advisories and apply patches promptly.
Security maintenance doesn't stop at your application code. Your runtime matters too.
Node.js advisory: https://t.co/rmgw4sOnqU
🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗 https://t.co/W4kfzx5lxz
#NodeJS#Security