“When a Republic is corrupted, there is no possibility of remedying any of the growing evils but by removing the corruption and restoring its lost principles; every other correction is either useless or a new evil.”
- Thomas Jefferson
🚨🇺🇸 BREAKING:
Nvidia has reportedly been HACKED by The Gentlemen, a ransomware-as-a-service (RAAS) group.
It's leak site listing doesn't show any stolen files yet, but it's marked "SOON" next to a countdown of ~10 days.
The group has claimed over 1,000 victims globally, across multiple countries and industries.
Nvidia, fresh off its first earnings call in its post-Jensen Huang era, has NOT confirmed the breach.
Writer: Michael
Combined with fractional reserve banking, it is truly treasonous what big banks and the government has done to us
Sadly, most people have probably never heard of fractional reserve banking.
But it’s a lever that controls your entire financial life
Want to be shocked?
A deputy from Zelensky’s party, Vatsak, posted a video to motivate Ukrainians to fight.
In it he shows his two Rolls-Royces, Aston Martin, his private plane and helicopter.
Not a joke - he actually just published.
Zelensky’s team has completely lost touch with reality.
Can anyone stop them?
What is going on right now?
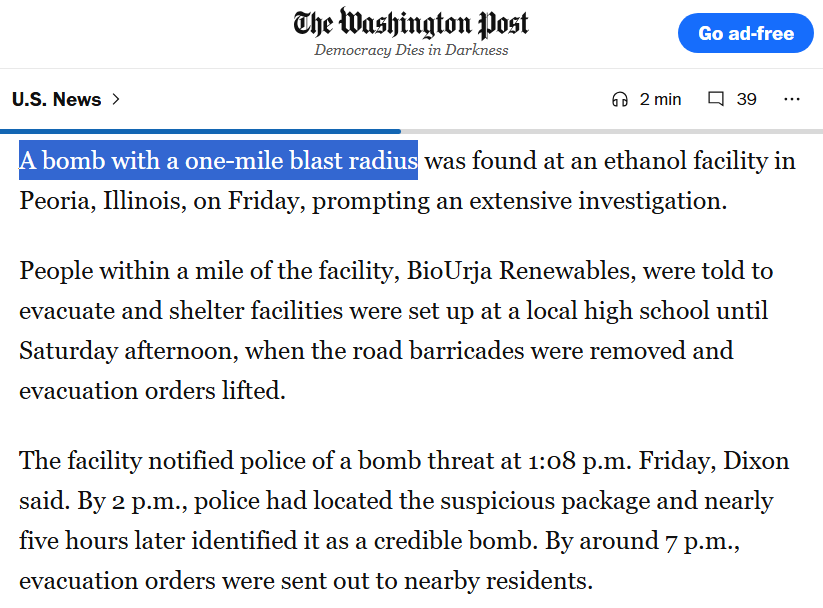
Governments telling citizens to stock up on supplies, massive cyber attacks, bomb threats, the NSA’s internal communications system goes down and now a fire at Langley??
It’s starting to get spooky
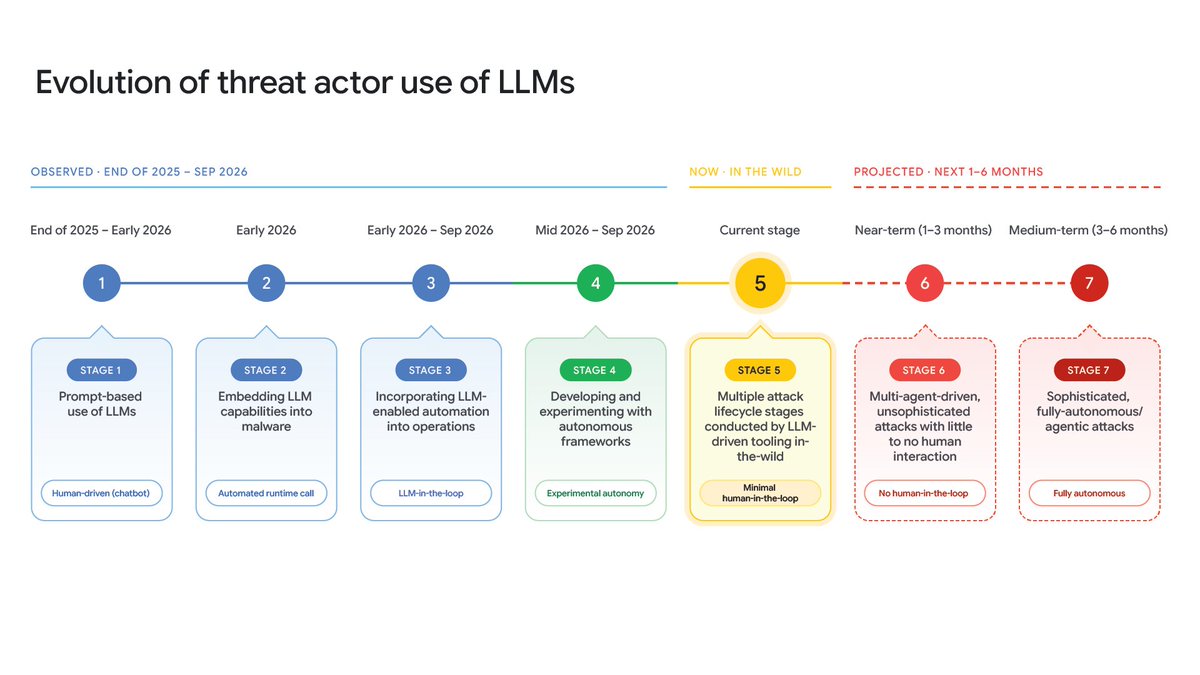
Hackers are now using LLMs to continuously scan software updates, spot newly fixed bugs, and build attacks before teams can apply the fix — all without human involvement. That’s according to the latest report from the Google Threat Intelligence Group.
We're helping defenders counter automated threats with Google AI Threat Defense, which combines Gemini and other frontier models to find and fix flaws before attackers can exploit them.
On Oct. 29, I made this tweet, in hopes that people would get exposure to my warning, because Nikita has a big following. The agentic swarm attacks migrated partially from US energy grids to banking systems. These attacks are a test, finding weak spots, till the real main event.
@nikitabier Hi Nikita. I’m an AI researcher for one of the big 3 labs. I can assure you, it’s about to get a lot worse. We’ve been assisting the US in combating agentic swarms on the US electrical grid. It’s about to get a lot worse. Pay attention to the banks next week.
OMG
Within hours of Mayor Mamdani disbanding the NYPD riot/terrorist unit, two people from the newly created "Community Dialogue and De-escalation Unit" have been shot.
@PTeller Hello. Service around Washington, D.C., has stopped due to local municipal officials placing a hold on the tracks. We apologize for this inconvenience and appreciate your patience.
JUST IN - A suspected supply chain attack on Optimizely loaded malware on Zoom, CNN, Fox News, BBC, Salesforce, GitLab, KLM, Air France, Bitly, IG Group, American Eagle and others, exposing visitors to scripts built to steal payment data and exploit iOS devices.
This is a big one.
We found malicious JavaScript being served through Optimizely to some of the world's largest websites.
178 organisations affected, with everything from crypto theft and card skimming to iOS exploits.
Zoom, BBC, CNN, HSBC, Salesforce, GitLab, KLM, IKEA, Equifax, Ledger. The list goes on... Full list in the post.
https://t.co/f8iiN3nrZ7
BREAKING: Google warns that state-backed hacking groups linked to Iran, China and North Korea are increasingly using AI to conduct cyber espionage, steal sensitive information, infiltrate organisations and develop sophisticated attacks. Separately, Russian-speaking hackers have been identified in what Google describes as potentially the first fully automated AI-powered cyberattack.
In its latest threat intelligence report, Google details how these actors are moving beyond simply using AI to write code or assist with research. They are integrating large language models (LLMs) and autonomous AI agents into multiple stages of their operations.
RUSSIA: 🇷🇺Google identified Russian-speaking hackers who used a network of AI agents to independently discover software vulnerabilities and develop exploits without human intervention. Their operation targeted French websites in the media, entertainment and education sectors. Google says this may be the first observed case of a fully automated vulnerability discovery and exploitation process.
CHINA: 🇨🇳Chinese-linked cyber espionage groups used AI during the third quarter of 2026 for reconnaissance, scanning, researching targets and weaponising software vulnerabilities. Google also identified a Chinese contractor known as LEAKY CASTLE using LLMs to analyse, translate and extract intelligence from stolen data. Other Chinese-linked actors abused AI platforms and file-hosting infrastructure to stage malicious files and exfiltrate stolen documents.
IRAN: 🇮🇷An Iranian government-backed group known as CALANQUE ION, previously tracked as APT42, has been using LLMs, including Google's Gemini, to support reconnaissance and targeted social engineering.
NORTH KOREA: North Korean actors are using AI to generate fake CVs, prepare for job interviews and impersonate Western IT professionals to secure remote employment. Google also identified operations targeting cryptocurrency companies in North America and Europe, involving fake recruiter profiles, AI-generated identities and fraudulent meeting platforms used to compromise victims and gain access to internal systems.
Google further warns that attackers are increasingly exploiting AI infrastructure itself, including autonomous execution capabilities and coding tools, to move deeper into compromised organisations.
The findings point to a significant evolution in cyber warfare and espionage.
Since we’ve “been at war with Iran for 47 years” and, “they’re America’s biggest threat… I wonder why we never catch any Iranians bringing biological weapons into the US?
I guess since Iran’s been 2 weeks away from a nuke since 1991, they have different priorities
WATCH OUT 🚨: Two Chinese nationals have been charged for allegedly smuggling a dangerous biological pathogen into the U.S. called “Fusarium graminearum” that could cripple the U.S. economy, food supply, and endanger American lives.
The FBI arrested Yunqing Jian (33) and Zunyong Liu (34) for allegedly smuggling the noxious fungus into the U.S. that “causes ‘head blight,’ a disease of wheat, barley, maize, and rice, and is responsible for billions of dollars in economic losses worldwide each year,” according to the DOJ.
Fusarium graminearum’s toxins cause vomiting, liver damage, and reproductive defects in humans and livestock.
FBI Director Kash Patel: “This case is a sobering reminder that the Chinese Communist Party continues to deploy operatives and researchers to infiltrate our institutions and target our food supply, an act that could cripple our economy and endanger American lives.”
“Smuggling a known agroterrorism agent into the U.S. is not just a violation of law, it's a direct threat to national security. I commend the FBI Detroit Division and our partners at CBP for stopping this biological threat before it could do real damage.”
JUST IN - Canadians across the country can expect an emergency alert on their phones, televisions and radios on Wednesday, November 18, as 'Alert Ready' conducts a nationwide test of Canada’s emergency warning system
Security Alert for U.S. Citizens in Europe
Stay alert in crowded public places, holiday events, and transportation hubs. Monitor local news, avoid demonstrations, and follow local authorities’ instructions.
Read the full alert: https://t.co/lYQwlPNahs
JUST IN: U.S. Embassy issues security alert for Americans in Europe, urging caution in crowded public places, holiday events and transportation hubs, and advising them to avoid demonstrations.