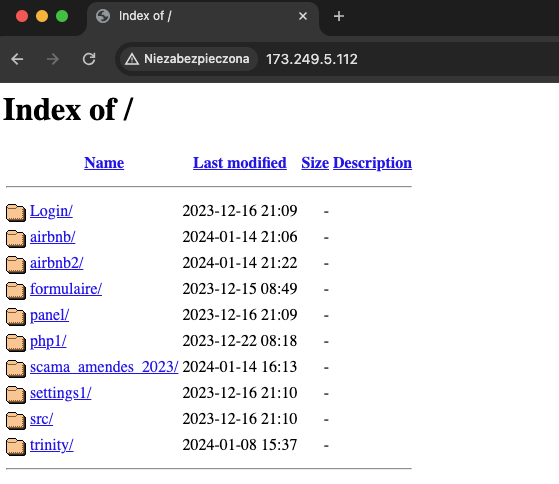
🔍 #opendir: 173.249.5[.112
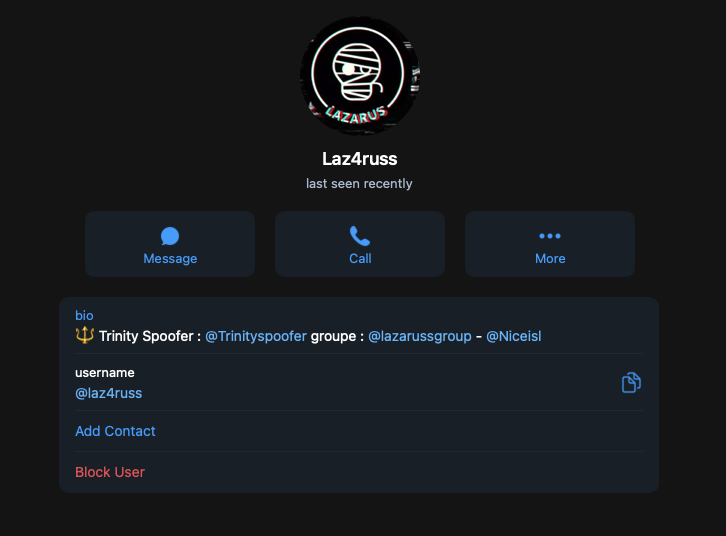
🔬What connects Trinity Spoofer and Airbnb Scams?
Answer: Lazaruss group 🥷
👀A cybercriminals specializing in fraud, mainly in France - carding, phishing, and spoofing.
1/2
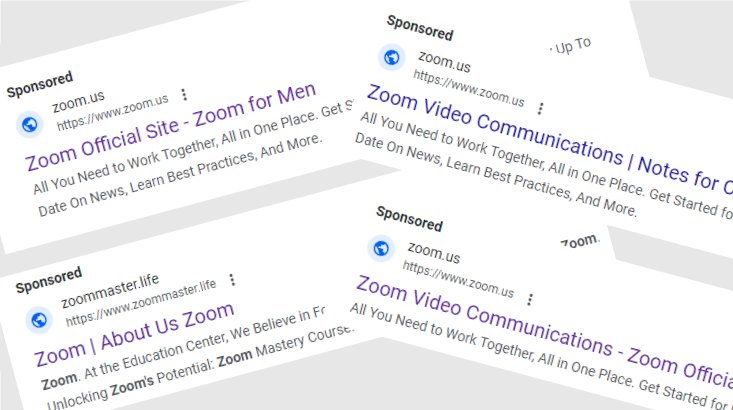
🚩 This is worrying and continues to increase, multiple threat actors, including ransomware operators and initial access brokers, are abusing the @GoogleAds service, but at a higher level. Attackers manage to show the original domain (URL) in the malicious ads, which is eventually displayed to thousands of potential victims on Google's main results page.
Three recent examples, thanks to Intel from Colin Cowie (Sophos) and Jérôme Segura (Malwarebytes) 👏
1.- #Pikabot (I think this is new 👀)
▪ https://t.co/lfQGVaYU3T
▪ https://t.co/9rbnbeqLbP
2.- #BatLoader
▪ https://t.co/N5fmR7HOaw
3.- #FakeBat + Hunting Panel:
▪ https://t.co/CU7E0k6uPT
🚨 DON'T TRUST Ads, be cautious, investigate, confirm.
🇮🇹 I Threat Actors (TA) dietro le campagne con target Italia abusano di strumenti (legittimi) per il controllo remoto
Dopo #Netsupport, #Remcos, #SystemBC oggi tocca a #Anyplace
⚔️ RAR autoestraente mascherato da PDF
💣 https://t.co/KsLp3JJY5M
🔗 https://t.co/pQPqxttLE3
🇮🇹 Osservata una campagna massiva, in lingua inglese, mirata a veicolare #Vidar in Italia
⚔️ TTP già osservate nelle campagne italiane del mese di luglio e settembre
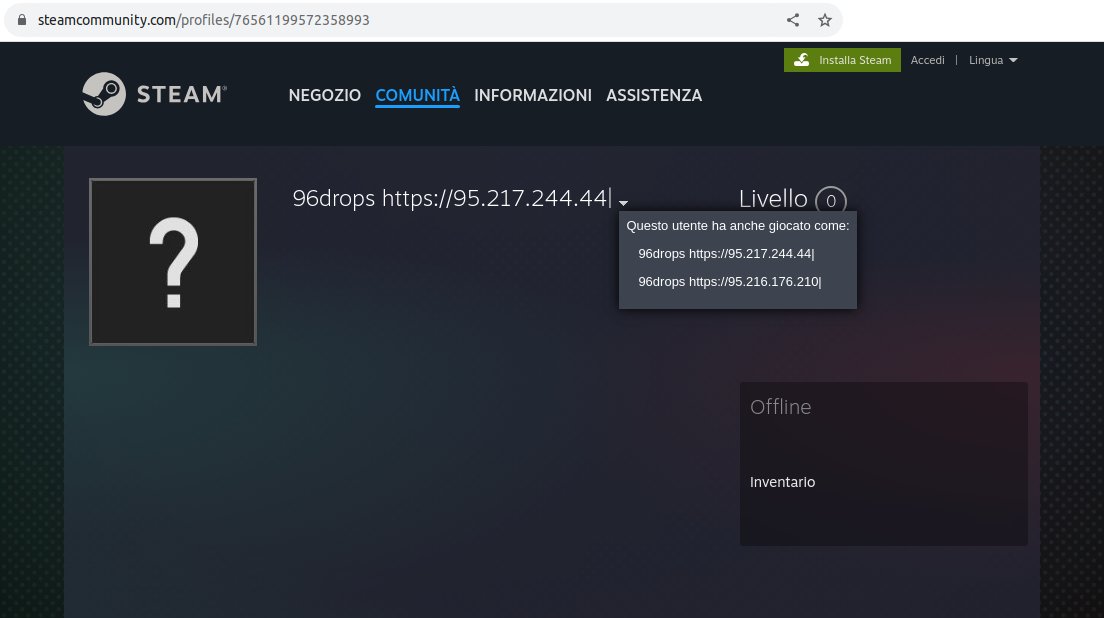
🔥 C2 nei profili #Telegram e #SteamCommunity
🔗 https://t.co/6JslGZbABx
Telegram: https://t.co/5XFiMdFqax
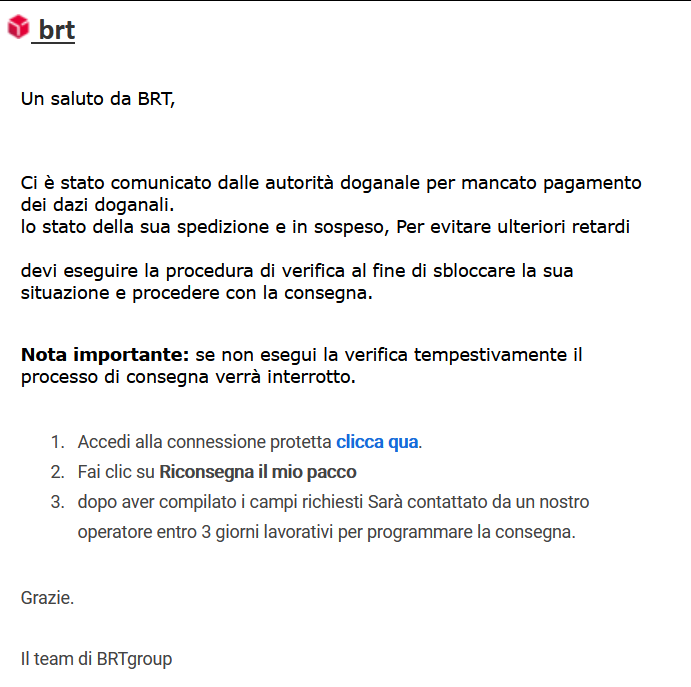
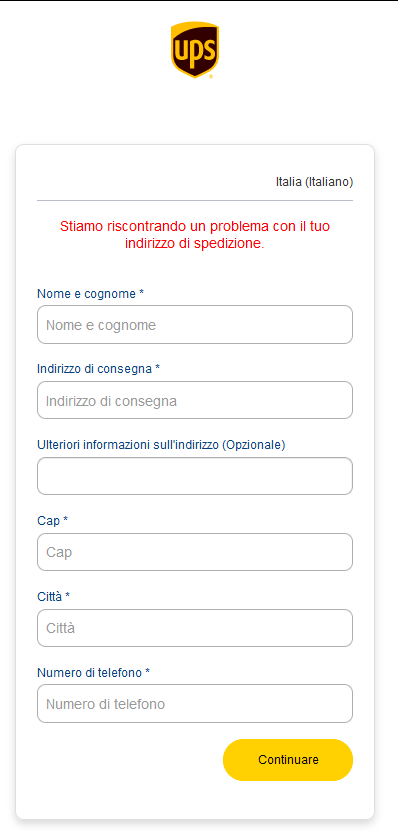
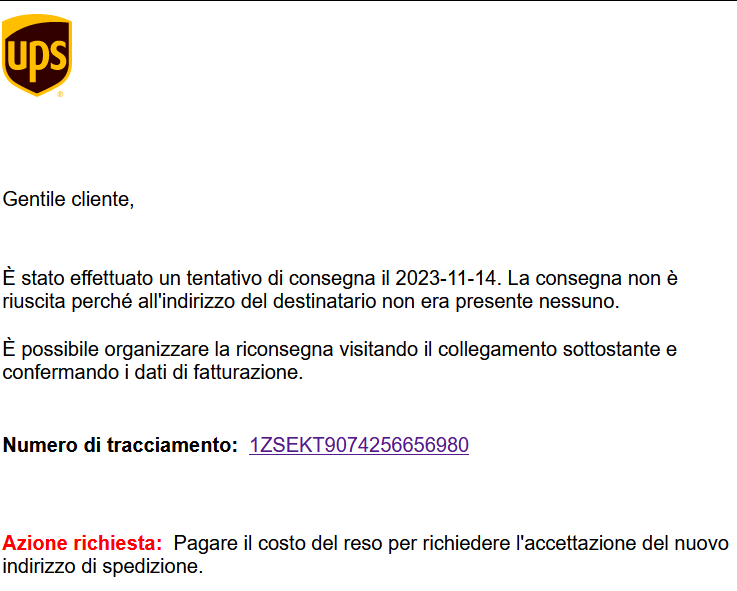
🪝#UPS@UPS#phishing targeting #Italy 🇮🇹
RE: il tuo pacco è in attesa di conferma!
https://rcc.hzw.mybluehost[.]me/resouceswebcontentit_ITs_quality_chart.pdf/
#LockBit is exploiting #CitrixBleed. By now there is no doubt.
Sad thing is that through @leak_ix data we can still see international governments and huge companies/banks being #vulnerable.
Its sad to see how some of the most important global infrastructure stays unpatched.
Gruppo di controllo/vigilanza del registro tributario spam @Agenzia_Entrate
EML>LNK>ZIP>URL>SMB>EXE>stego
spread #RemCosRat
Urls https://t.co/N5ISI7cYps
Samples https://t.co/kADezqnWmA
SMB 62.173.141.]11*4 *6 *8
⚠️C2
62.173.145.]211 listpoints[.online
Run https://t.co/Qq1rKWzsck
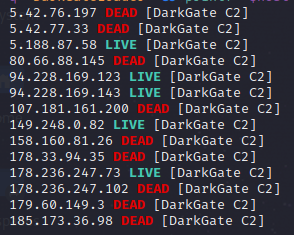
Watch out for this #DarkGate campaign, quite possibly through Malvertising and using signed MSI files with very low (or zero) detection.
#SIGNED "PFO GROUP LLC"
Other sites on 154.56.47.156:
https://openvpnhub[.]com/
https://angryipscanner[.]net/
https://www.putty-ssh[.]com/
C2: 178.236.247.102
[+] https://t.co/c9qcavosbq
https://advancedscannerip[.]com/
C2: 80.66.88.145
[+] https://t.co/3TtxIuufWr
Reports by @ULTRAFRAUD and @DonPasci 🙌
More references: https://t.co/zbE1dT4vAw
#Bumblebee "rar28" rolling in via DocuSign-themed emails with compressed exes
rc4:"new_black"
192\.168.0.101:444
134\.156.166.37:332
https://t.co/uCG2fvaQdU
https://t.co/qg3KMtlP5y
@Myrtus0x0
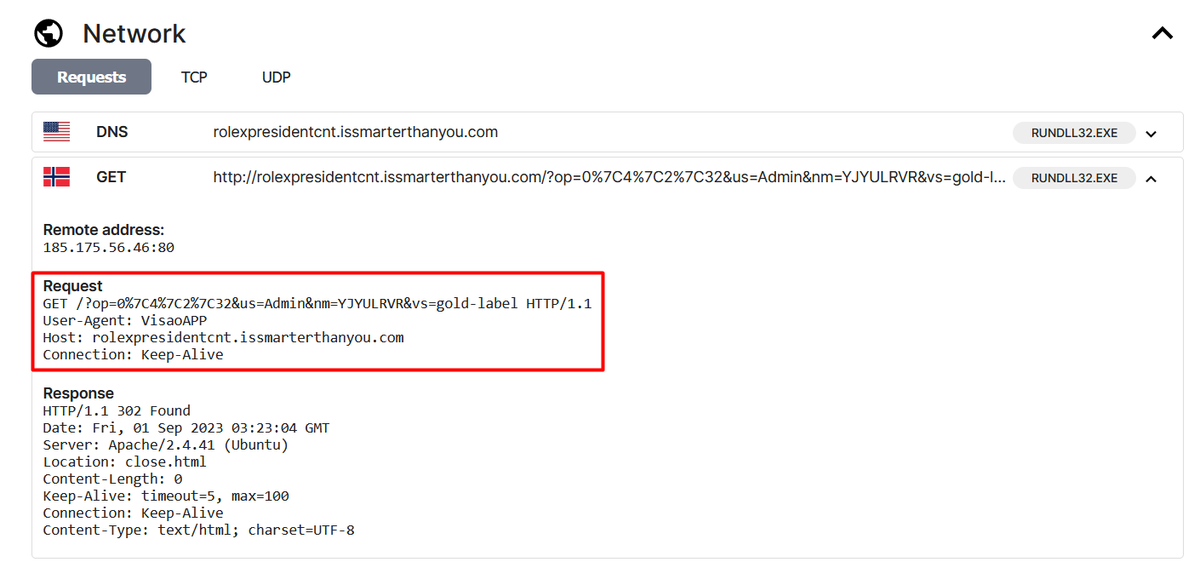
#JanelaRAT dirigido a México 🇲🇽 a través de correos Phishing con link de descarga.
1.- Email > link a http://167.88.168.229/cfdifacmaxtimbrefiscaldigital/ > descarga archivo .zip con .vbs en su interior > .vbs contacta a http://robertgoldlabel[.]dyndns-office[.]com/goldlabel/ y obtiene servidor de la siguiente etapa.
2.- El servidor http://185.175.56[.]41/ genera otro archivo .zip (payloads dinámicos) que contiene la DLL maliciosa que se carga a través de DLL side-loading.
- C2: rolexpresidentcnt[.]issmarterthanyou[.]com
- Check-in: /?op=0|4|2|32&us=Admin&nm=YJYULRVR&vs=gold-label (User-Agent: VisaoAPP)
[+] https://t.co/MbBPX5YKx2
REF: https://t.co/IGcvAIuE3I









![JAMESWT_WT's tweet photo. Gruppo di controllo/vigilanza del registro tributario spam @Agenzia_Entrate
EML>LNK>ZIP>URL>SMB>EXE>stego
spread #RemCosRat
Urls https://t.co/N5ISI7cYps
Samples https://t.co/kADezqnWmA
SMB 62.173.141.]11*4 *6 *8
⚠️C2
62.173.145.]211 listpoints[.online
Run https://t.co/Qq1rKWzsck https://t.co/p8SuEs9PZA](https://pbs.twimg.com/media/F-5NkeGXUAApSdB.jpg)
![JAMESWT_WT's tweet photo. Gruppo di controllo/vigilanza del registro tributario spam @Agenzia_Entrate
EML>LNK>ZIP>URL>SMB>EXE>stego
spread #RemCosRat
Urls https://t.co/N5ISI7cYps
Samples https://t.co/kADezqnWmA
SMB 62.173.141.]11*4 *6 *8
⚠️C2
62.173.145.]211 listpoints[.online
Run https://t.co/Qq1rKWzsck https://t.co/p8SuEs9PZA](https://pbs.twimg.com/media/F-5Nj_gXwAA3NvE.jpg)
![JAMESWT_WT's tweet photo. Gruppo di controllo/vigilanza del registro tributario spam @Agenzia_Entrate
EML>LNK>ZIP>URL>SMB>EXE>stego
spread #RemCosRat
Urls https://t.co/N5ISI7cYps
Samples https://t.co/kADezqnWmA
SMB 62.173.141.]11*4 *6 *8
⚠️C2
62.173.145.]211 listpoints[.online
Run https://t.co/Qq1rKWzsck https://t.co/p8SuEs9PZA](https://pbs.twimg.com/media/F-5Nja3XoAA_yn5.jpg)









![JAMESWT_WT's tweet photo. Gruppo di controllo/vigilanza del registro tributario spam @Agenzia_Entrate
EML>LNK>ZIP>URL>SMB>EXE>stego
spread #RemCosRat
Urls https://t.co/N5ISI7cYps
Samples https://t.co/kADezqnWmA
SMB 62.173.141.]11*4 *6 *8
⚠️C2
62.173.145.]211 listpoints[.online
Run https://t.co/Qq1rKWzsck https://t.co/p8SuEs9PZA](https://pbs.twimg.com/media/F-5NlQrWAAAZdJl.jpg)