Initia Foundation has approved funding to fully restore the 1:1 backing for affected Noble USDC, WETH, and AUSD0 held as iUSD collateral.
Funding will cover verified shortfalls up to 1.08M USDC, 105 ETH, and 1.4M AUSD0 following reconciliation and final transfer approval.
A security fix to patch the identified vulnerability from October 23rd has been drafted and is currently under audit with security partners.
Once the audits are completed, we will provide concrete plans for restoring the backing of affected assets and the orderly restart of the Initia L1 and Rollup networks.
We expect to complete this process in the coming days.
Thank you for your patience, and please remain cautious of unofficial links, messages, or claims.
At 14:59 UTC on October 23rd, an attacker exploited a bug in Initia MoveVM’s script caching that allowed malicious code to bypass security checks. The attacker artificially spoofed the MoveVM state, thereby crediting themselves with unbacked WETH, iUSD, and USDC tokens without changing the corresponding token’s total supply. No native INIT was minted, and the total INIT supply is unaffected.
Before the network was halted, the attacker bridged out roughly $2.7M, comprising of 105 WETH and ~1.4M AUSD0 via LayerZero along with ~1.08M USDC via Noble and CCTP. The tokens were swapped for 1,135.52 ETH and currently sit in 0x358ef0130f7a5aa516dcd81bdc80b18cde41cac8 on Ethereum Mainnet.
We are actively working on a security fix to patch the identified vulnerability. We expect this to be completed and audited in a few days. Additionally, asset recovery efforts are ongoing with the help of security partners.
The Initia L1 and Rollups remain halted as we work toward a resolution. We hope to safely resume network operations as soon as possible and will provide a full post-mortem once available. In the meantime, we will continue to share verified updates through our official channels.
Please remain cautious of unofficial links, messages, or claims.
to the best of our knowledge so far, this is a Day 0 bug related to Initia's MoveVM on CosmosSDK that allowed the exploiter to mint additional tokens on the Initia L1 but does not apply to native INIT tokens.
the attacker was able to mint and bridge out ~$2.7m worth of AUSD, ETH, and USDC before the chain was paused.
calling all promptmaxxers!!!
the King of the Hill pot on @GlyphUniverseAI just crossed $100
buy a $1 ticket, create your fighter with a 200 character prompt and try to take down the current king.
$100+ up for grabs if you & claude can figure out how to beat him
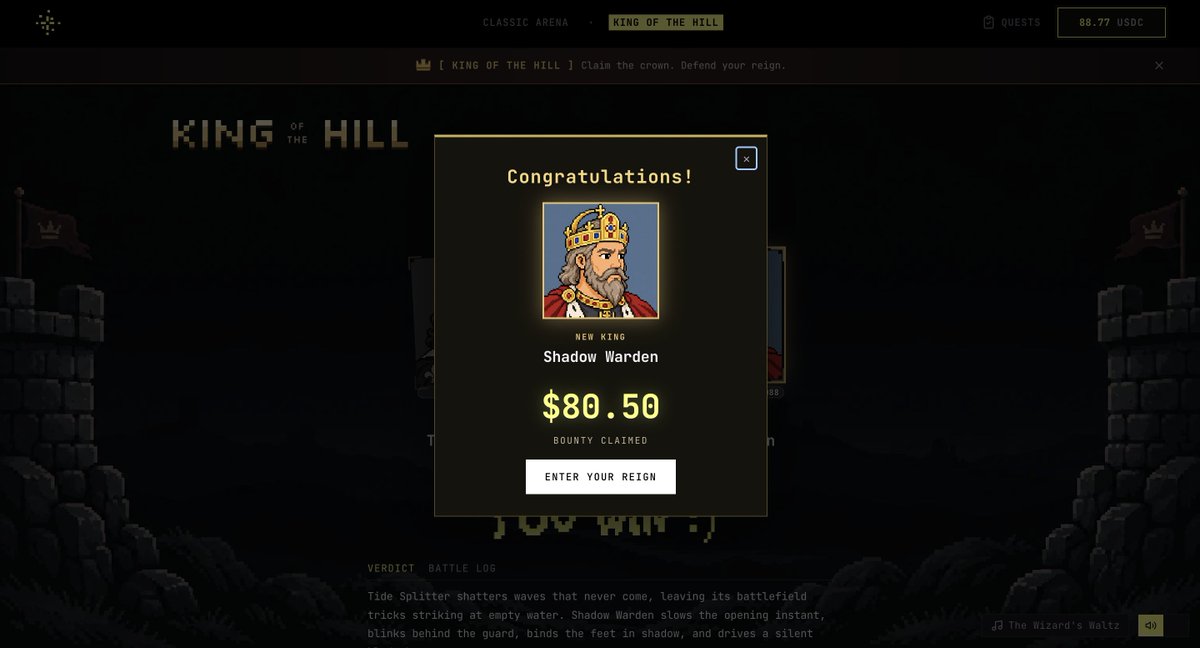
GUYS GUYS I WON FOR THE FIRST TIME on @GlyphUniverseAI and it's a BIG TIME!! and i was on my last few dollarez ...
been playing since glyph started but it was like a losing ritual for me... i could never get my prompts right and i also never sat down to actually figure it out.
the 50$ pot money had my eyes 👀 ... so i sat down (actually more like laid down on my bed) and locked in. i was getting nervous as the pot climbed to 75$ and i was losing my tix and bucks... BUT THEN I WON on my 5th try!!
it's so much fun,, PLAY W US ON https://t.co/J5ACto13Ty
you ask, we ship
no better place to try onchain prop trading than @TradeOnStrat
if you'd like to give it a try, join our telegram group! we've got a lot more in store for ya coming v soon
https://t.co/rjcexdPGCN
for the past month @TradeOnStrat has been busy shipping trader requests:
- profit split: 80% → 90%
- max drawdown: 4% → 6%
- min order size: 400 → 50
- activity requirement: 1 trade every 24h → every 7d
- 24/5 stock trading
- multi tp/sl
- bulk position closing