A new chapter in proactive wellness begins.
FINAO SPV Inc.- a venture between FINAO and Rubix Blockchain-has collaborated with the YMCA to launch the P0 beta of the YMCA Wellness Café™ in the Pacific Northwest.
The platform encourages members to build healthier habits by rewarding consistent wellness activities with Y COIN, a utility token backed by Rubix tokens.
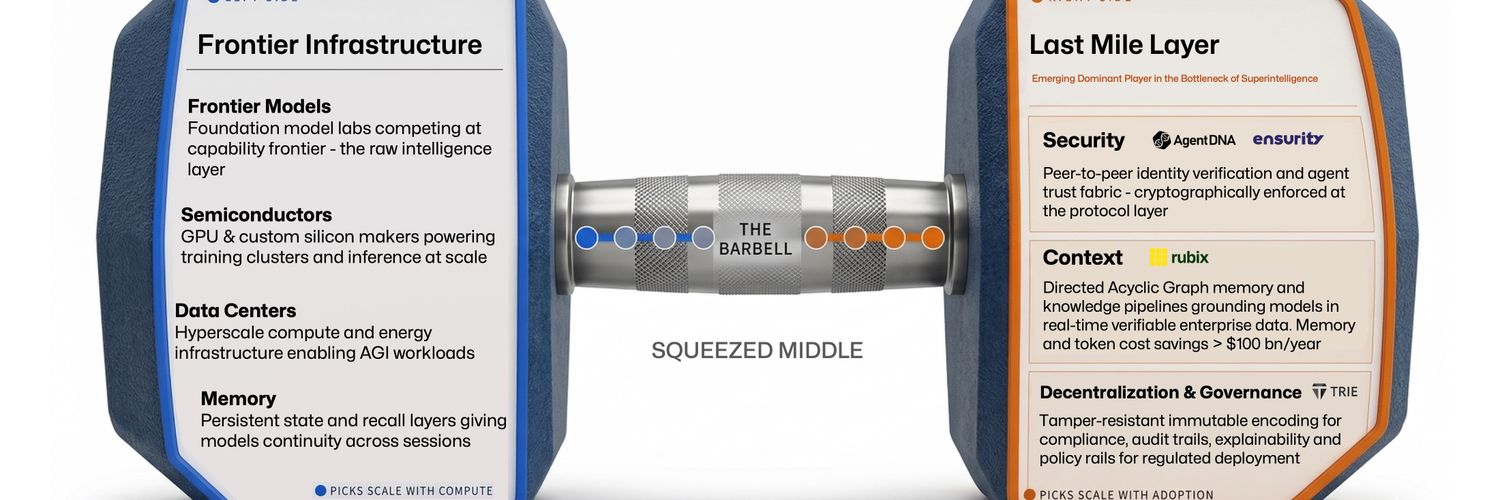
Powered by the Rubix Blockchain, the platform enables secure activity records, seamless rewards, data privacy and scalable transactions.
With the YMCA serving more than 60 million members across 120 countries, this initiative has the potential to take rewarding, proactive wellness to a global scale.
Read the full announcement:
https://t.co/JU8KpqVrEF
API keys and registry credentials mostly compromised. Roll out new keys, but need access first. Account takeovers can be hard to reverse. Harden and airgap API keys and all credentials before its late. @ThinC_AUTH#AuthAMS@Ensurity
Railway is compromised, rotate all API keys as soon as possible
Deployments are down so don’t wait to redeploy
Attackers are draining keys in real time, we didn’t lose much but can confirm this is still an active attack
Stay safe friends
This is alarming. Hackers could gain root access before patching is done and maintain persisent presence inside. Focus must be to comprehensively fix auth before that. @EnsurityTech@Agent_DNA
Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl https://t.co/vhiGLxNhIS
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: https://t.co/C512KFOEq5, Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased https://t.co/28tjHqd5Wr table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.
KYA is as important as knowing the human actor behind the agent. Agent does not linearly tranfer human auth to the app. Agents will spin multiple sub agents, interact with third parry agents on the net and we need to know which of these agents is carrying the auth. The full context and intent. KYA as well as KYH. @Agent_DNA
Has anyone scanned the internet for ECC public keys (and even RSA) and tried all private keys up to 256 to see if this is a more common phenomenon than imaginable?
@nadiaheninger ?
It is 2026 and we are still seeing breaches due to credential theft and passwords, with wide blast surface. Two choices: harden/airgap creds. Or decentralize creds. Little time left to make this transition.
@EnsurityTech@ThinC_AUTH#AuthAMS@Agent_DNA
WE DIDN'T JUST RETHINK AUTHENTICATION. WE REDEFINED TRUST.
Identity is managed through @XSenseID . Credentials & assets are controlled through AUTHAMS, Authentication is strengthened through our @ThinC_AUTH FIDO2 Bio Keys.
#UnPhishYourself with Ensurity.
📷[email protected]
Gavin Baker on the other side of Ben's bandwidth story: at the peak of the 2000 bubble, 97% of America's fiber sat dark, and today there are no dark GPUs.
"I had, depending on how you look at it, the privilege and the misfortune of being a tech investor during the year 2000 bubble, which was really a telecom bubble."
"The year 2000 bubble was defined by something called 'dark fiber.' Dark fiber was literally fiber that was laid down in the ground, and not lit up... At the peak of the bubble, 97% of the fiber that had been laid in America was dark."
"Contrast that with today. There are no dark GPUs. All you have to do is read any technical paper, and one of the biggest problems in a training run is that GPUs are melting."
@GavinSBaker
@elonmusk@zerohedge Agree @elonmusk, HBM is a tougher one to scale quickly. Unlike previous memory cycles though, falling prices and context efficiency will lead to more expoential demand.
We have not sorted security gaps in the pre agent era fully yet, and now with agents, its a fully different thing altogether. Build agenetic security architecture from first principles @Agent_DNA
Don't hand your credentials and keys to AI models or model based security tools. Harden and air gap credentials/keys where possible now (for humans). Decentralize otherwise (for agents). There is little other option.
#AISecurity#cybersecurity#IAM@EnsurityTech@Agent_DNA
I was wondering if maybe AI models were going to find some kind of hidden mathematical trap in the P-256 parameters. The opposite just happened!
https://t.co/duIVJp2jao
IPFS is entering its next chapter: more decentralized, more resilient, & stewarded by a growing community of independent teams supporting public infrastructure!💪
At the end of September the project celebrated a major milestone 🏁: 100% of in-browser public gateway traffic now uses direct, verifiable peer-to-peer retrieval — run by a sustainable, federated network of independent operators.🤝
Big thanks to:
🔎 IPNI / Compass — content discovery, routing, and browser-first retrieval
📊 ProbeLab — network health, measurement, and performance
🛡️ Skapa / BadBits — protecting the network from abuse
IPFS has always been about an internet that is more open, resilient, and user-controlled. Building on IPFS? Operating infrastructure? Come help shape what's next!
https://t.co/3MxVzrDz0B
the nsa's "mystery" seed behind P-256 was just a 1997 clock time
the part people are missing: a timestamp only gives ~30 bits of wiggle room
the backdoor theory needed ~70
best case outcome. the most trusted curve on the internet stays trusted
1 weak password. A country breached.
The Denmark CPR breach is a reminder that vulnerabilities can have disastrous consequences .
We help enterprises strengthen identity security through @XSenseID , @ThinC_AUTH FIDO2 Keys, & 𝗮𝘂𝘁𝗵 AMS.
#UnPhishYourself
📩[email protected]