Digital Forensics & Incident Response (DFIR) Practical Labs
I encourage students, cybersecurity enthusiasts, and aspiring forensic investigators to explore this GitHub repository packed with practical DFIR labs and CTF challenges.
Digital Forensics is best mastered through hands-on practice, not theory alone.
🔗 https://t.co/zpyfhZgCsM
Keep learning, keep investigating! 💚
#DigitalForensics #DFIR #Cybersecurity #HIVEConsult
@IceSolst This could be a great campaign for the OpenSSL folks:
"To properly honor the Number Four's new place in the cryptography ecosystem, please sponsor us for $4/month on GitHub"
Ref: https://t.co/eO52W6LkUv
Defender can restrict exclusions only to certain processes accessing certain folders, triggered by certain reasons. This is almost entirely unused, and opens machines to wide abuse. What if a tool could suggest these exact locked-down restrictions to you? To your admins?
Swiftfender. This and way, way more: Coming soon.
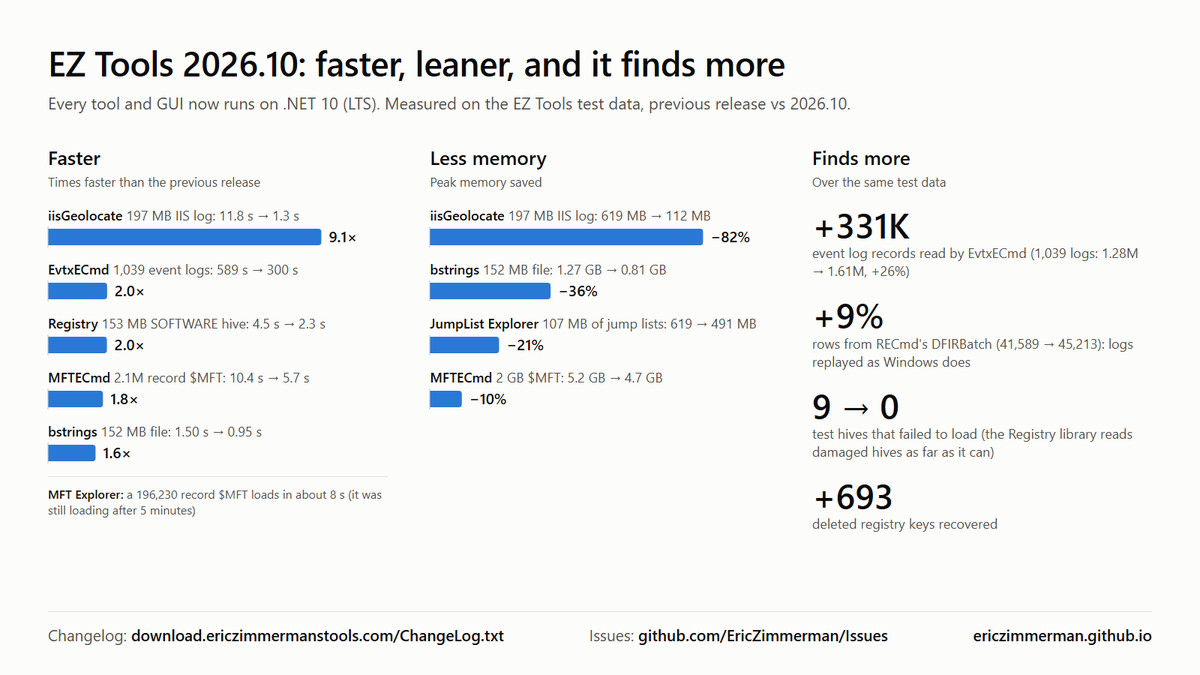
1/ EZ Tools 2026.10 is out, all on .NET 10 (LTS)
✅ More accurate: 331K more event log records, hive logs replayed as Windows does, every test hive loads
⚡ Faster: up to 9x; EvtxECmd and Registry 2x
📉 Less memory: up to 82% less
Update with Get-ZimmermanTools 🧵 #DFIR
📢 I partnered with @13CubedDFIR for another giveaway! 🎁
🏆 1 winner will receive a 13Cubed Investigator T-Shirt + the XPlat Bundle Complete which includes the following four courses:
- Investigating Windows Endpoints
- Investigating Windows Memory
- Investigating macOS Endpoints
- Investigating Linux Devices
Each course comes with a Certificate of Completion as well as Certification attempts.
👕 5 winners will receive 13Cubed Investigator T-Shirts
The T-shirts have the 13Cubed logo on the front and "Digital Forensics Investigator" on the back.
To Enter: Like, Comment, and Repost
On December 7th, entries from across three social media platforms will be combined and winners will be selected.
For more info check out:
XPlat Bundle Complete: https://t.co/3Sx1JWJ9x6
Certification Information: https://t.co/IVM2zdyp62
T-Shirts: https://t.co/021POuAXQL
#DFIR #DigitalForensics #IncidentResponse