Not every detection needs to be fancy, even something basic will help you catch threats:
- Root account usage
- IAM privilege escalation with AttachUserPolicy
- New regions usage
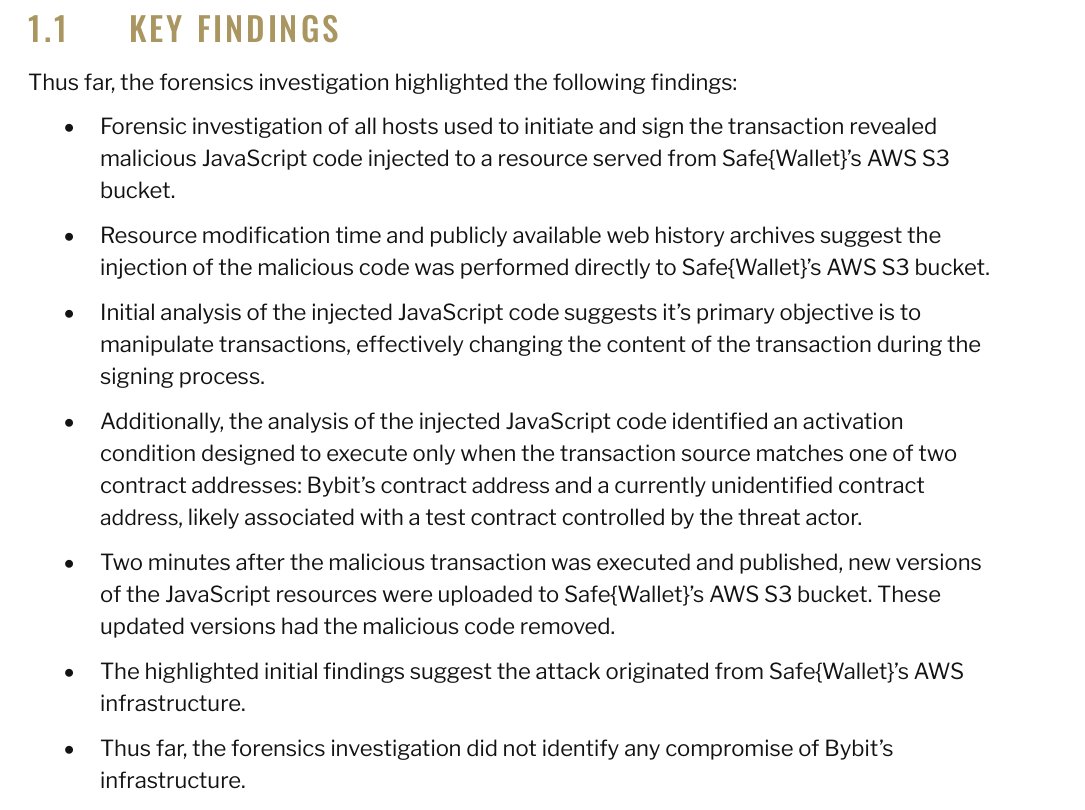
TL;DR: A dev machine of Safe was compromised. This allowed access to AWS and their S3 bucket. A malicious JavaScript was pushed to the bucket and eventually distributed. The malicious JS code targeted specifically the Bybit contract address. The JS code changes the content of the transaction during the signing process.
Bybit shared to investigation reports here: https://t.co/2E9KCeOKPf
lol
The government don’t use SQqqqqlllllllll 🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣🤣
Oh boy 🤣🤣🤣🤣🤣🤣🤣🤣
What else don’t they use? Oracle? Windows? VMware sphere? Come on 🤣🤣🤣🤣🤣🤣🤣🤣
Breaking 🚨: Pelosi has done it again
Back on 1/14, she opened a new ~$100K position into the AI company Tempus AI $TEM
Since her buy, it's up 72%
Never doubt the queen
Estrellas blog is probably my favorite technical blog.
One of my favorite articles of his is his comprehensive guide to packers.
This article dives into how packers work and provides tips on how to unpack packed samples!
You can find the links below! 👇
🤓 Just released the full (not truncated) slides from my @defcon presentation on the XZ backdoor!
I think this is the most condensed (and digest) version of this crazy story! 🤯
Hope you'll find it useful! 👇
https://t.co/zzBCKhuGJp
It’s high time to learn #Rust! Follow our Technical Director @0xdea while he embarks on a journey of theoretical and practical study, in this first installment of our brand-new series dedicated to #OffensiveRust, "Learning Rust for fun and backdoo-rs":
https://t.co/fGNq85pqKX
I just bought Coffeezilla Defense - @CoffeeBreak_YT https://t.co/E9UqYH8kNN,I just bought Coffeezilla Defense - @CoffeeBreak_YT https://t.co/E9UqYH8kNN
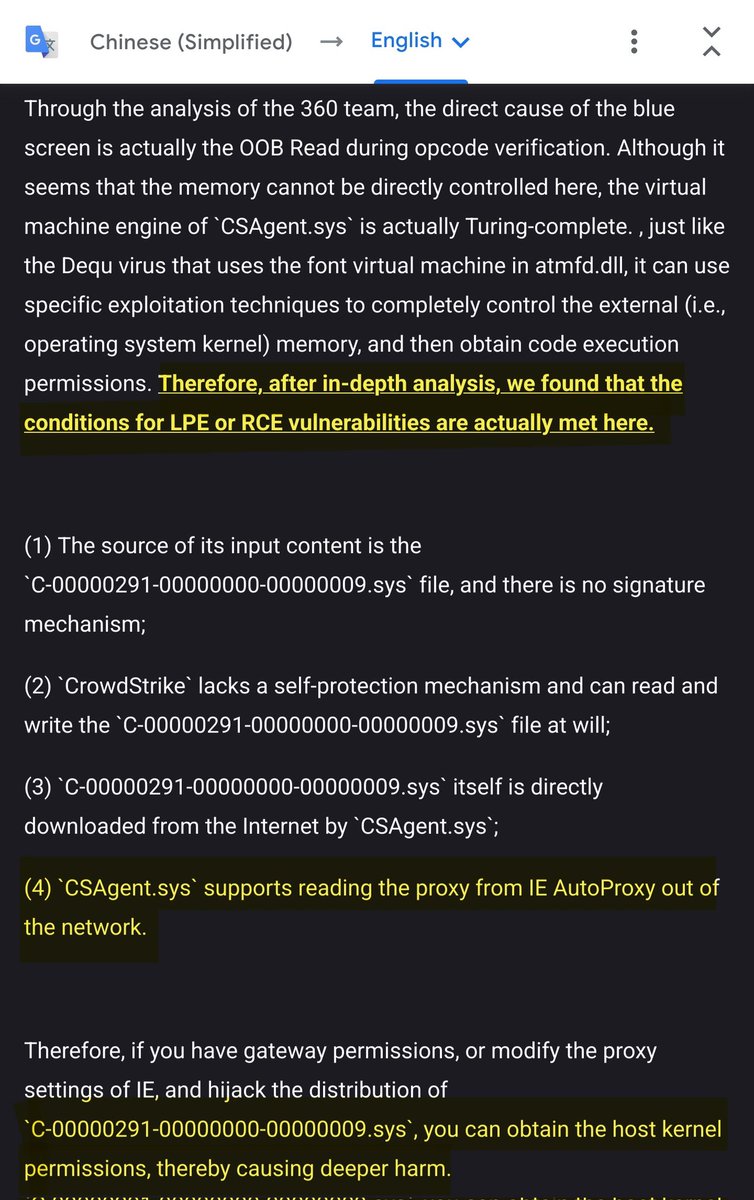
Now that cats out of the bag, Let me state that I've been exploiting the last part (IE Proxy modification) in my last few Red team engagements to deploy a local proxy via BOF which blocks all Crowdstrike traffic and only allows only the ones I've whitelisted 😛. Heres a quick snapshot to identify Crowdstrike traffic (https://t.co/HpFREYRzkj) via local socks proxy 🫢. Might post its BOF later, unless someone beats me to it. #Crowdstrike