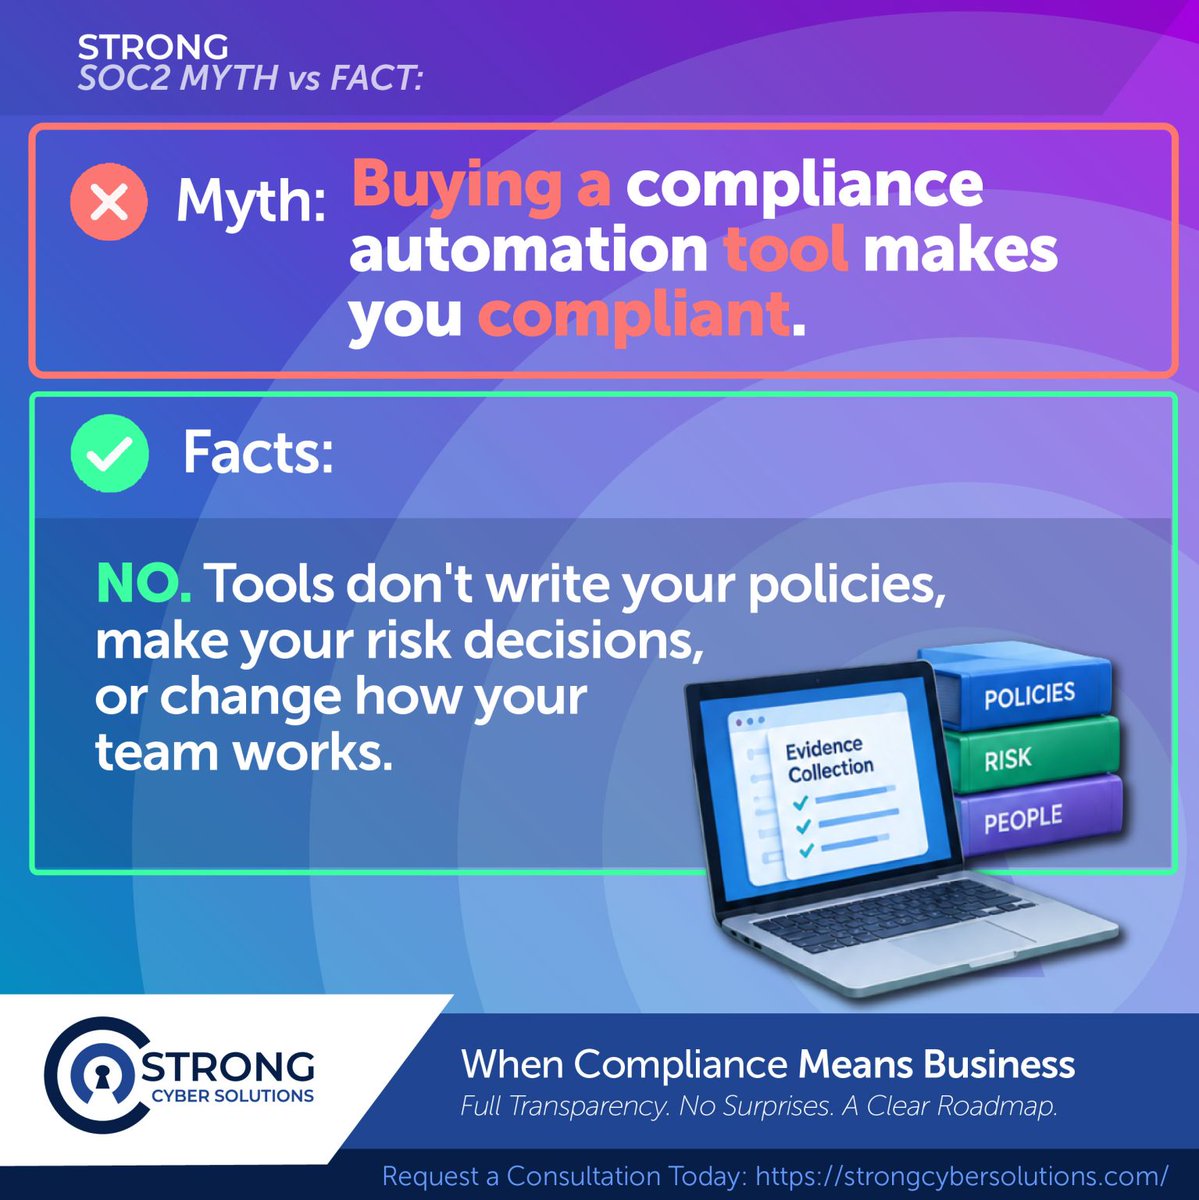
Myth: Buying compliance automation software makes you compliant.
Fact: Tools help collect evidence. They don't write practical policies, make risk decisions or ensure controls work.
Automation supports compliance. People make it work.
#SOC2#GRC#ComplianceAutomation
ISO 27001 Tip: Don't build policies you can't live with.
One of the most common compliance mistakes is creating an impressive collection of security policies that don't reflect how the business actually operates.
That's a problem.
ISO 27001 isn't about having the largest policy manual. It's about building an information security management system (ISMS) that works in practice and continually improves.
Your policies should reflect your actual operations, responsibilities and security controls.
An auditor isn't just interested in what your policies say. They want evidence that you're following them.
The bottom line: Write policies for the organization you actually have, not the organization you think an auditor wants to see.
Need an objective assessment of your ISO 27001 readiness? Strong Cyber Solutions can help.
#ISO27001 #InformationSecurity #CyberCompliance #GRC #StrongCyberSolutions
Your customers may define your compliance roadmap.
SOC 2, ISO 27001 and CMMC requirements often emerge during vendor reviews and procurement.
Don't wait until compliance delays your next contract.
Prepare before the customer asks.
#SOC2#ISO27001#GRC
SOC 2 Myth vs. Fact:
❌ Myth: SOC 2 is only for big enterprises.
✅ Fact: It can be the deal-breaker when you're trying to land your first enterprise client.
If SOC 2 is blocking a major opportunity, it's time to map the fastest path to readiness.
#SOC2#GRC
SOC 2 Myth vs. Fact:
❌ “We're getting SOC 2 certified.”
✅ Technically, there's no SOC 2 certification. A CPA firm examines your controls and issues a SOC 2 report.
The goal isn't a certificate. It's demonstrating that the right controls are working.
#SOC2#GRC
Pursuing ISO 27001? Don't start with the certification.
Start with your risk register.
Your risks should drive the controls, policies and Statement of Applicability — not the other way around.
#ISO27001#GRC
Because I know you know this but sometimes we’re too close to things to see it, I’m gonna say it anyway… two things can be true at once.
Charlie didn’t want war with Iran not because there are zero benefits but because it’s virtually a 80-20 issue that America needs to get out of the trillions in debt.
Charlie also understands Iran doesn’t get a free ride to do what it wants free from American consequence.
Most Americans can agree war with Iran wasn’t the best outcome of a Trump presidency but not passing any Doge cuts or the Save Act or balancing the budget is also not the best outcomes of a Trump presidency but sometimes push comes to shove and Trump made the move because he felt it was the right move. I say since congresss isn’t going to pass the 80-20 issues and the debt is going to continue to rise… might as well go F up some people who want American and western civilization dead.
AI is already part of our everyday workflows.
But who’s accountable when something goes wrong?👀
That’s the governance problem ISO 42001 aims to address
In this video, we break down why it matters & how it works.
Watch here👇
https://t.co/DeuYVN5v1A
On average, DIB contractors spend $100K–$250K+ and 6–18 months on CMMC prep. Most can't afford that.
Today, we launched Secureframe Defense to help any organization go from zero to CMMC ready in 4–8 weeks.
Learn how: https://t.co/WaCtnUJqgP
⬆️ Inhale.
⬇️ Exhale.
🤘 Shred.
Volume up to hear the sound of audit chaos finding its inner peace.
We’re bringing Calm-pliance (and the shredder) to RSAC March 23-26.
See you there? 🧘💜 https://t.co/YzVVB4RiZV
75% of organizations say cyber regulations have improved their security posture.
So why are so many still failing audits?
Because regulations have shifted. NIS2. DORA. PCI DSS. They're no longer asking if you have controls in place.
They're asking if you can prove those controls limit damage when something fails.
Pen tests are now audit artifacts. Evidence of containment beats evidence of detection. The patchwork of mandates keeps growing – the only way to keep up is to stop treating compliance as a checklist and start building it into your architecture.
📖 How to future-proof compliance → https://t.co/tXRvX04yGW
Archive migration can become a strategic opportunity to transform legacy libraries into intelligent, searchable content assets when approached with the right tools.
Read our latest blog about DIVA and Vantage: https://t.co/m1SokmFtdz
#AI#Workflows#Telestream
Audit fatigue is real. So is the pressure to “just handle it.”
What does it take to run a modern security program without constantly having to reset it? On March 19 for Vanta Delivers, we’re bringing together leaders who’ve actually owned that question:
🟣 @jadeehanson, CISO at Vanta
🟣 @alexstamos, CPO at @corridor and former CISO at SentinelOne
🟣 Andrew Becherer, CISO at @sublime_sec
Together, they’ll share how they think about scaling across business units and frameworks to build programs that feel steady, not reactive.
You’ll also hear from our CPO @jeremy_epling, who will walk through new product updates and live demos across Enterprise Control, our Context-aware AI Agent, and Privacy Automation.
Save your spot: https://t.co/tEHTheIUcZ
Stay connected to get practical insights on cyber risk, compliance, and emerging threats from the CISO Global team. Subscribe to our bi-weekly email now: https://t.co/QRSsUbpVFY
#Cybersecurity#SecurityInsights#CyberLeadership