Life-time access is so back!
From now on, individuals can get life-time access to all of our online courses.
Learning how specific TTPs work, understanding coding, debugging and troubleshooting is much simpler with video-based content.
Check it out - https://t.co/j8UbEZWi5j
#redteam #blueteam #elearning #maldev #malwaredevelopment
If you're an attacker with local admin privs, consider storing your malicious files in
C:\ProgramData\Microsoft\Windows Defender Advanced Threat Protection
MS tends to store noisy and shady scripts there, leading many security vendors to eventually exclude that folder
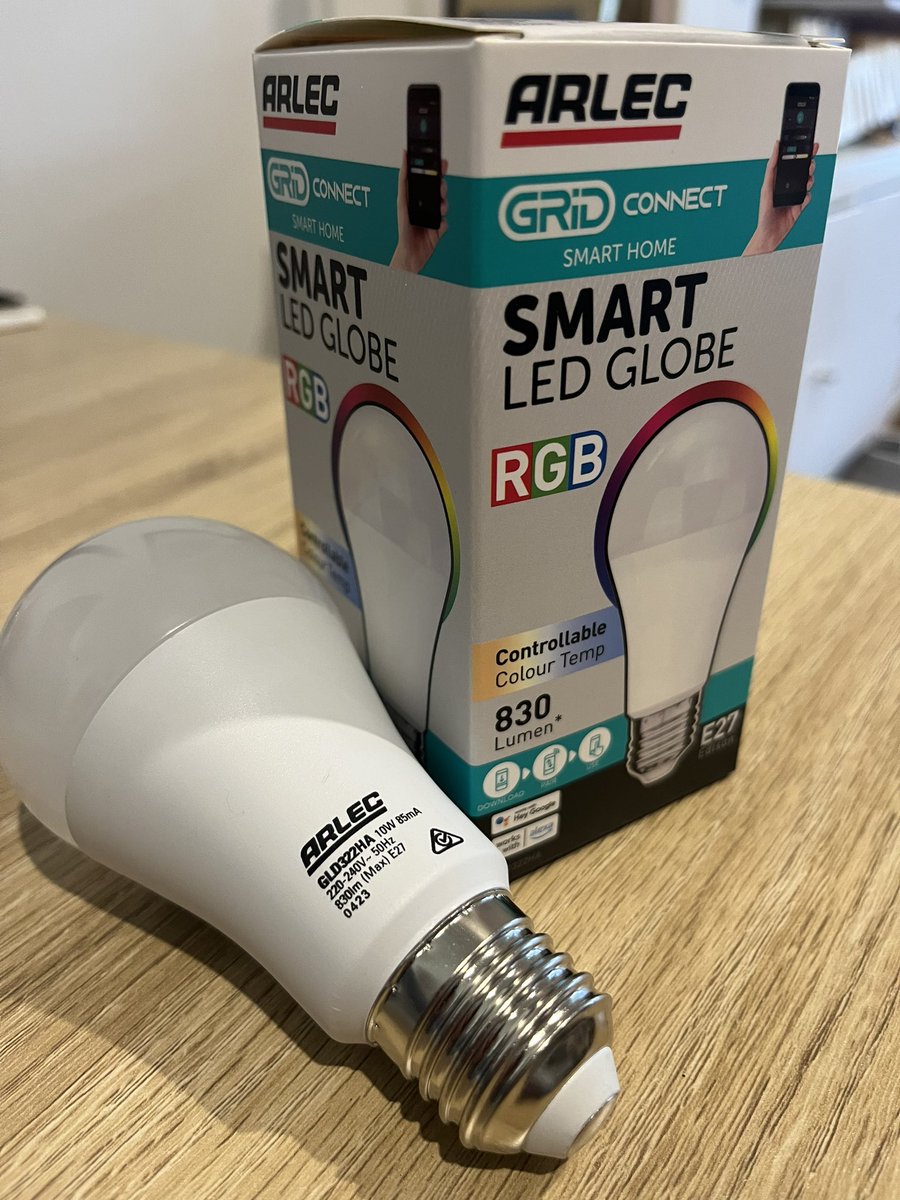
A friend asked me to find out why his connected lightbulb app was asking for his location, so I ducked out to Australia’s favourite hardware store, Bunnings, and grabbed one to check out.
The Android grid connect app has 500k+ downloads.
Let’s take a quick look! 🧵
(1/n)
Hacker gift ideas thread part 2: the books
Let’s GO
* I have read it
+ Someone I trust has read it
^ The community likes it
I usually read epub or audiobook versions
If you want to master SSRF, open this thread!
Server-Side Request Forgery vulnerabilities are attacks that allow attackers to send arbitrary requests from the server often resulting in gaining authorized access to data!🤯
A Thread 🧵👇
A 100% free Computer Science curriculum.
2 years' worth of content if you dedicate ~20 hrs/week.
You can go from nothing to fully proficient without spending money or going anywhere.
https://t.co/vaTqW8FLUv
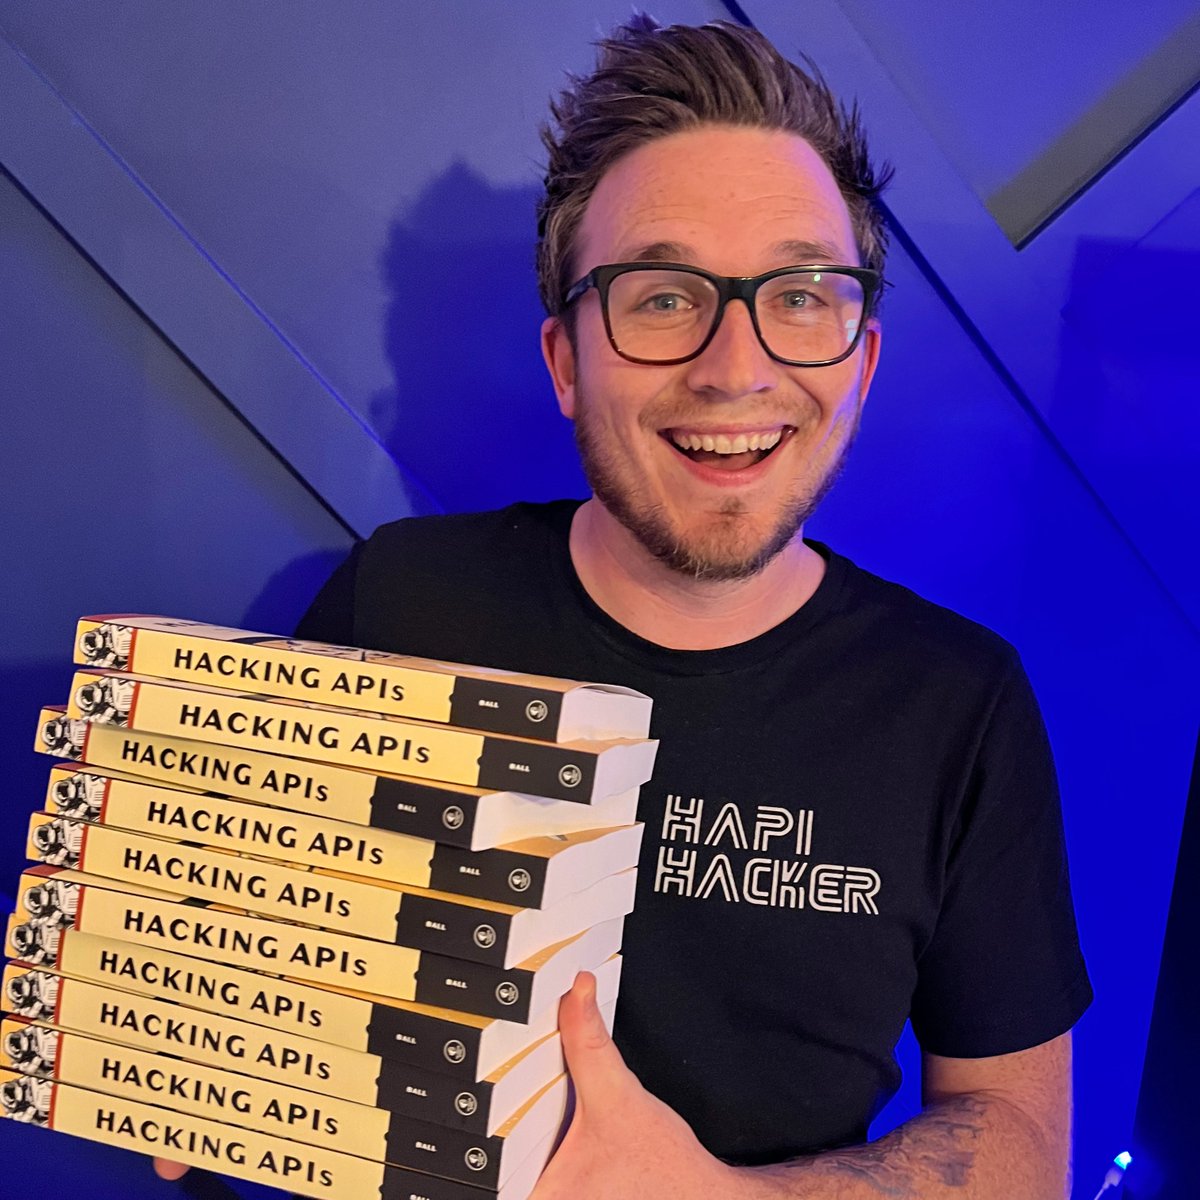
Hacking APIs Book Giveaway sponsored by https://t.co/6QOfGi8FzB! We are giving away 10 print books.
One entry per:
♥️ Like 🔁 RT
👑Bonus entry to anyone who follows @apisec_ai. Ends in 48 hours!
I'm going to <semi> live tweet this Internal Penetration Test. Calling the company Acme
Important notes:
Assumed Breach (Already have a Debian based image, no creds, but solely for the sake of having tools locally)
Landing in the SWIFT gateway network
Flags: DA/SWIFT 1/x
Reverse Engineering For Everyone!
This comprehensive set of reverse engineering tutorials covers x86, x64 32-bit ARM, 64-bit architectures. If you're a newbie looking to learn reversing, or just someone looking to revise some concepts, check it out
https://t.co/gBdB9g3YrP
We've updated vx-undeground.
We have made it easier to find materials and the website is more mobile friendly. If the website looks the same as last time please refresh/clear your cache.
https://t.co/xvJa5yJKws
Want an easy way to transfer Firefox credential files to decrypt elsewhere? Try this simple script (you'll need to compile it to a .exe file to run on Windows machines without Python3 installed). https://t.co/FeX1TWve4g
Friday, October 29th, 2021 we will release the ransomware toolkit we have acquired.
The tools we possess we have confirmed to be used by both Conti ransomware group and BlackMatter ransomware group. They are scripts stolen from TeamTNT - modified to deliver ransomware.
Conti ransomware group has put out a statement regarding the recent REvil activities. We have archived it and placed it on Pastebin.
Title: Announcement. ReviLives.
Subject: Own opinion.
You can read it here: https://t.co/28d1jnUxAv