CVE-2026-88771 - the loaded Citrix footgun went off again, and the screaming noise is back in our ear.
You knew it was coming - enjoy the latest watchTowr Labs blogpost.
https://t.co/cKN1oqLwpK
During a Red Team assessment, @l4x4 discovered multiple vulnerabilities on Ubika WAAP Gateway, including a pre-auth RCE as root.
Technical details are available here ⬇️
https://t.co/72j4rGJ63H
🚨 CRITICAL NEXT.JS RCE DISCLOSED — ATTACKER-CONTROLLED SVG DATA CAN LEAD TO SERVER CODE EXECUTION
Vercel has disclosed a critical remote-code-execution vulnerability affecting the Node.js implementation of ImageResponse in Next.js.
• CVE-2026-94545 / GHSA-vcvr-r3jv-pc5j
• CVSS 9.5 Critical
• Affects Next.js >=16.2.0 and <16.3.6
• Exploitation is network-accessible and requires no authentication or user interaction, but requires an affected application configuration
• Applications are vulnerable when attacker-controlled values reach SVG content, attributes or styles rendered through next/og ImageResponse
• Successful exploitation can lead to remote code execution on the Node.js server
• The Edge implementation of ImageResponse is NOT affected
• Applications that never place attacker-controlled data into generated SVG content, attributes or styles are also not affected
• Fixed in Next.js 16.3.6
• Vercel recommends removing untrusted SVG input from Node.js ImageResponse as a workaround where immediate upgrading is impossible
• No confirmed in-the-wild exploitation has been identified at this time
⚠️ Analyst Note:
The interesting attack surface is dynamic image generation. Open Graph/social-preview images often incorporate URL parameters, usernames, titles or other externally supplied content — exactly the type of data that can become attacker-controlled.
Internet-facing Next.js applications using server-side ImageResponse should therefore review not only their framework version but whether untrusted values flow into SVG generation.
Original Vercel / Next.js security advisory:
https://t.co/Lk1URQhyBT
#NextJS #Vercel #CVE202694545 #RCE #WebSecurity #Vulnerability #ThreatIntel #DDW #DarkWeb
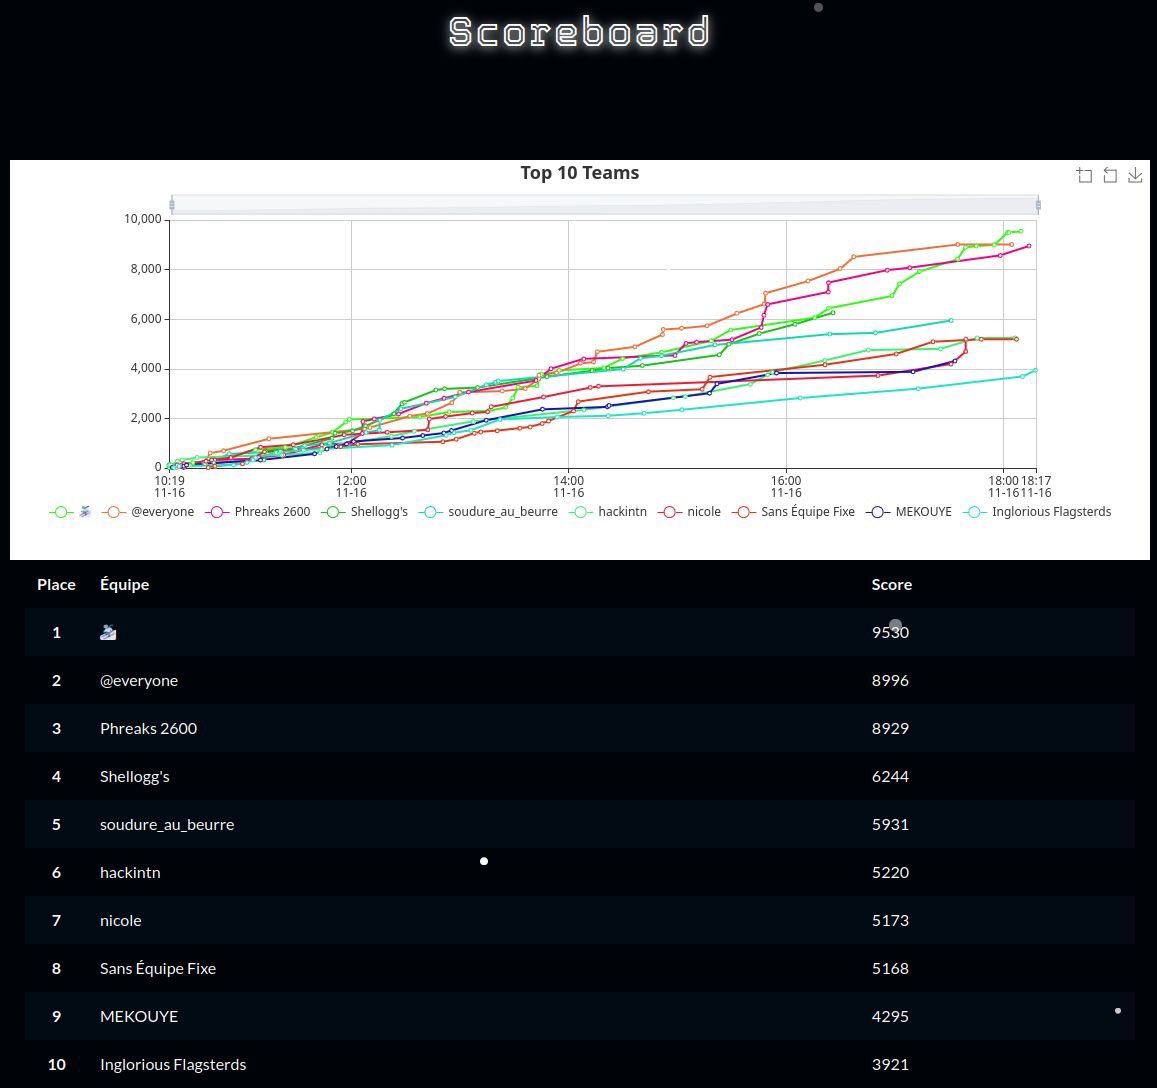
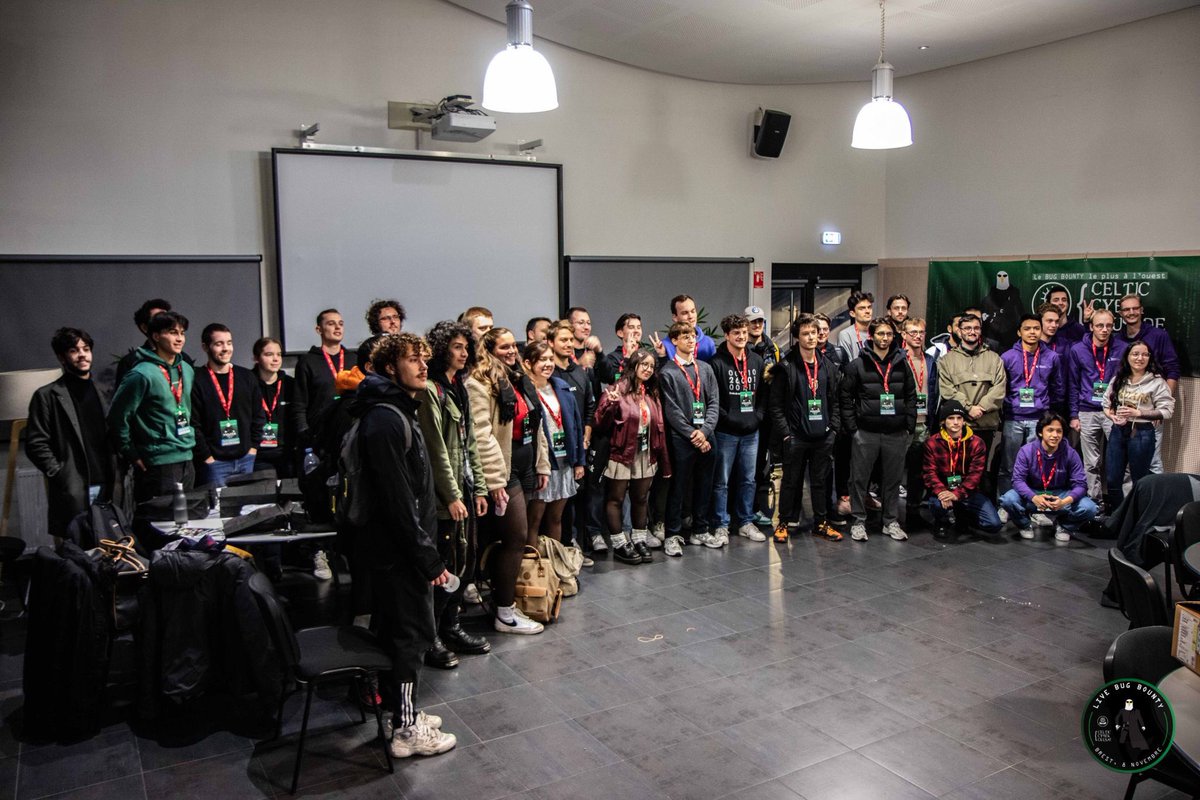
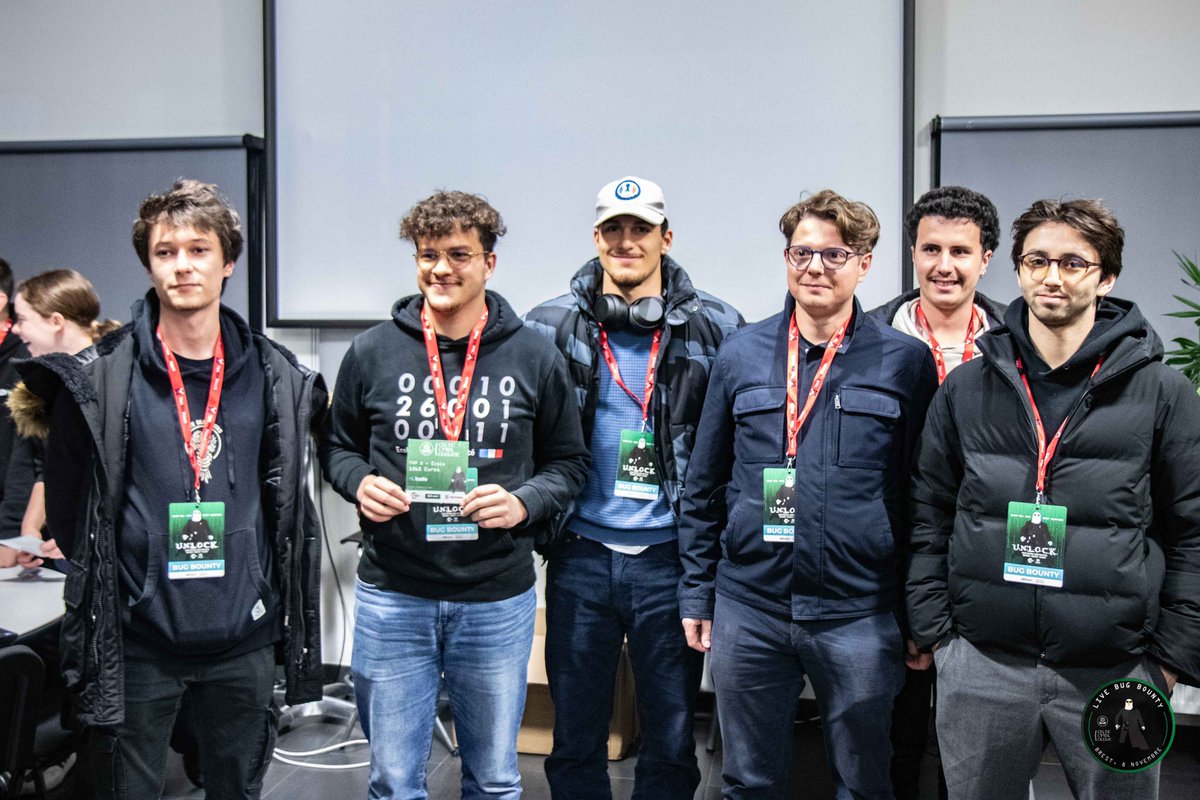
We finished 🥈at @UYBHYS’s LHE organized by @yeswehack and @Bzhunt1
Congrats to @fayred_fr for winning Best Report award and to @rayanlecat for a top🥉individual ranking and the award for the most critical bug! 💥
Thanks to the organizers, can’t wait for the next edition! 🤘
🚨Alert🚨
CVE-2024-29415: Popular Node.js Package ‘node-ip’ Exposes Millions to Potential SSRF Attacks
⚠Widely-used node-ip npm package, which is designed to retrieve a computer’s IPv4 addresses, has been identified to contain a serious SSRF vulnerability.
📊35.6M+ Services are found on the https://t.co/g3tSyh1Boc
🔗Hunter Link:https://t.co/QDmnwIM9UW
📰Refer:https://t.co/8Oo2TJxHNd
👇Query
Hunter: /product.name="Node.js"
FOFA: app="Nodejs"
SHODAN: product:"Node.js"
#NodeJS #SSRF #hunterhow #infosec #infosecurity #Infosys #Vulnerability
🚨Alert🚨CVE-2024-4985 (CVSS 10): Critical Authentication Bypass Flaw Found in GitHub Enterprise Server
🔥PoC:https://t.co/72FanmbkD6
⚠It could allow attackers to bypass authentication and gain unauthorized access to sensitive code repositories and data.
📊248K+ Services are found on https://t.co/g3tSyh1Boc
🔗Hunter Link:https://t.co/vJnaWg6ozp
📰Refer:https://t.co/CeZWFOKec4
👇Query
Hunter:/product.name="Github Enterprise"
FOFA:app="Github-Enterprise"
SHODAN:http.html:"Github Enterprise"
#GitHub #hunterhow #infosec #infosecurity #Infosys #Vulnerability
🚀 The Phreaks have taken flight! 🚀
This week, our players are crossing the Atlantic to take part in @NorthSec_io taking place in #Montreal 🍁
On the program 2 days of conferences and a #CTF that will bring together a hundred teams! 🏆
Wish us luck! 🌟
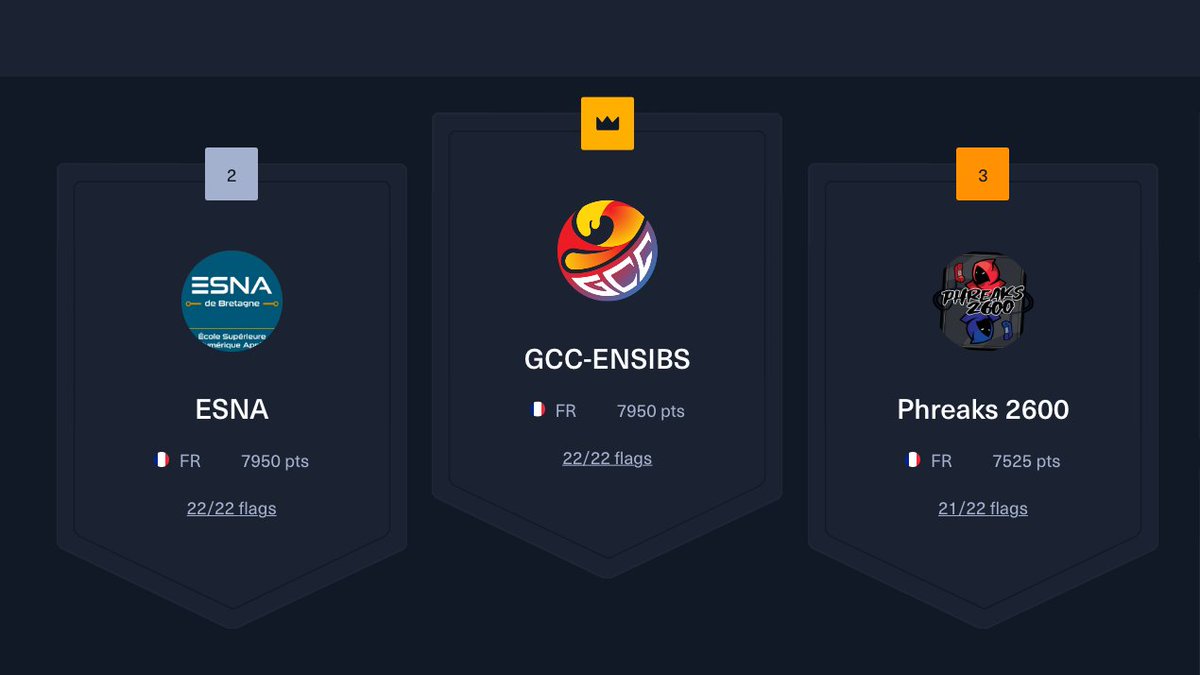
📣 Give it up to the brave survivors of Brains & Bytes 📣
#UniversityCTF23 has come to an end, and these are its champions:
🥇 @GCC_ENSIBS
🥈 @EsnaBretagne
🥉 @Phreaks2600
Thank you, everyone, for participating in the epic #CTF, and of course, stay tuned for more to come 😉
#HackTheBox #HTB #Cybersecurity #CaptureTheFlag
Giveaway time! I have 1 online ticket to giveaway for @ArabConf. Please Retweet and Reply to participate. I will announce winners tomorrow.
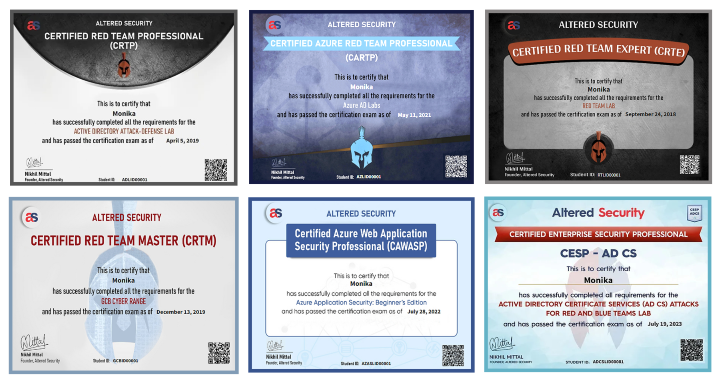
Also, we (@AlteredSecurity) are glad to sponsor our labs as prizes for @ascyberwargames
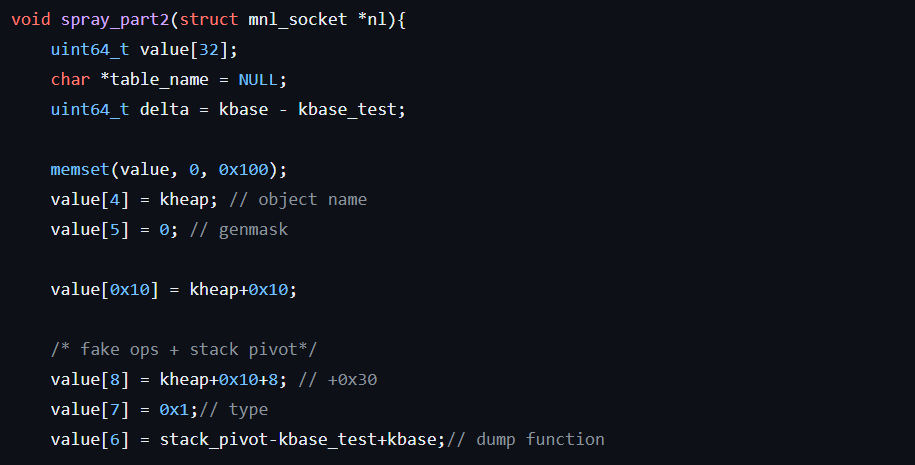
CVE-2023-1829: A use-after-free vulnerability in the Linux Kernel traffic control index filter (tcindex) can be exploited to achieve local privilege escalation.
Poc
https://t.co/o5tCESU91N