Developer Advocate @Snyksec | Prev @Microsoft @Disney | Web dev and app sec things. Here for community, fun and learning. Not for numbers or influencing you.
@auchenberg@code 100% agree and feel this too. Miss you all💙
Glad they all put this documentary together and thoroughly enjoyed the watch. Very well done!
It was amazing being able to knock out 4 PRs while on a plane. Kick off a cloud agent task, go watch a show, get alerted things are done, review, merge, move on to the next one.
@debs_obrien@cursor_ai Yes it’s fantastic! I’ve been really enjoying this flow just typically with Claude. I went to switch to the same with Codex but they dropped this workflow now so I just signed up for Cursor to give it a go there as well. Glad to see it’s a great experience.
I’m really enjoying this workflow especially when I’m on the go but I’m disappointed to see that @OpenAI no longer supports it. Why did they change this?!
Phone → choose code project → delegate task → cloud agent works independently → review results/PR from phone
@wesbos@randyrektor Yes love how Randy and team edit all the content from you all. I definitely take notice to that having dabbled a bit. This one looked pretty meticulously put together. Keep it up!
If your Instagram is public, Meta just enrolled you in something you didn't agree to.
Their new AI tool, Muse Image, lets anyone @-mention your Instagram handle in Meta AI and generate images using your face and photos. launched Tuesday. opt-in by default. no notification when it happens.
→ you won't be told when someone creates an AI image of you
→ opting out only stops future generation; anything already made stays live
→ there's no mechanism to remove images created before you opted out
how to turn it off:
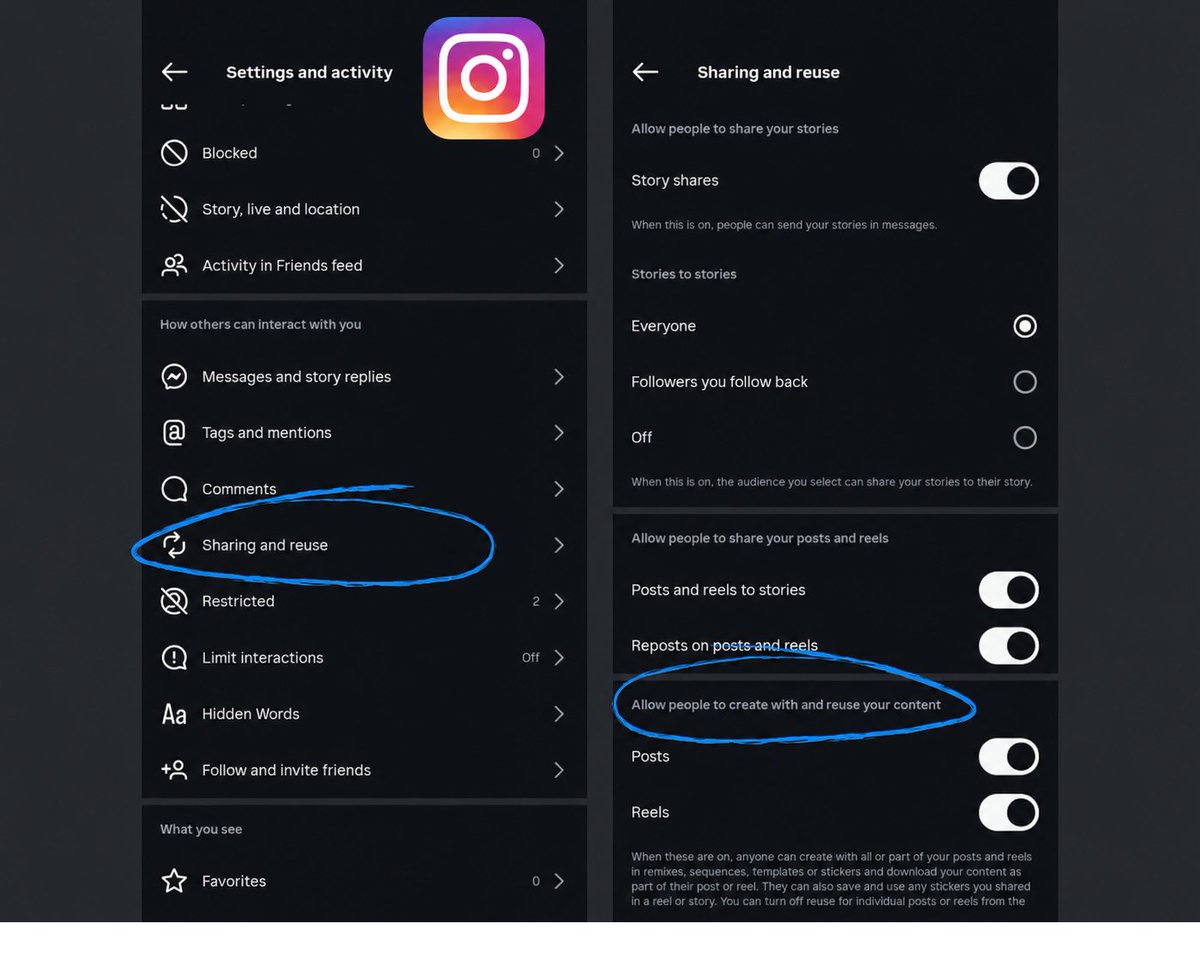
Instagram → Profile → Menu (☰) → Sharing and Reuse → turn off Posts and Reels under "Allow people to reuse your content on Instagram and with AI features at Meta"
note: the setting is still rolling out. if you don't see it yet, keep checking.
if you want the strongest protection right now: go private.
Big banks aren't known for moving fast on new tech. With AI it's a different story. Some are even buying supercomputers to train their own internal models.
Versions of
- laravel-lang/lang
- laravel-lang/http-statuses
- laravel-lang/attributes
- laravel-lang/actions
have been published with malicious versions
Packagist has unlisted the packages, but if you installed any of them between May 22–23, treat the environment as compromised
Your first instinct after getting hit by the TanStack npm attack is to revoke your GitHub token.
Don't.
The malware polls GitHub every 60 seconds. Gets a 401? It runs rm -rf ~/
Here's the right remediation order before you touch a single credential. https://t.co/TNXDfhORa4