Walkthrough of an N-day Android GPU driver vulnerability
Talk by Angus about analyzing CVE-2022-22706 — a logical bug in the Mali GPU driver that allows getting write access to read-only memory.
https://t.co/45QkDRBgOS
week 113, streaming kernel dev right now
topic: kernel threads
continuing with scheduling/kernel threads, working on thread exit, an idle task, and properly mapping stacks instead of using the physmap
see ya 👋
https://t.co/Ecx7QDrkVO
Working on simulating sunset, night and fake lights with only post processing and simple shaders.
Still very rough, next step is to figure out good solutions for the sky!
Wrote up my first Patch Tuesday diff. CVE-2026-20811, type confusion in win32kfull.sys. CMonitorTopology* survives incomplete sanitization in the async path.
Feedback welcome!
https://t.co/jac0MwNu4U
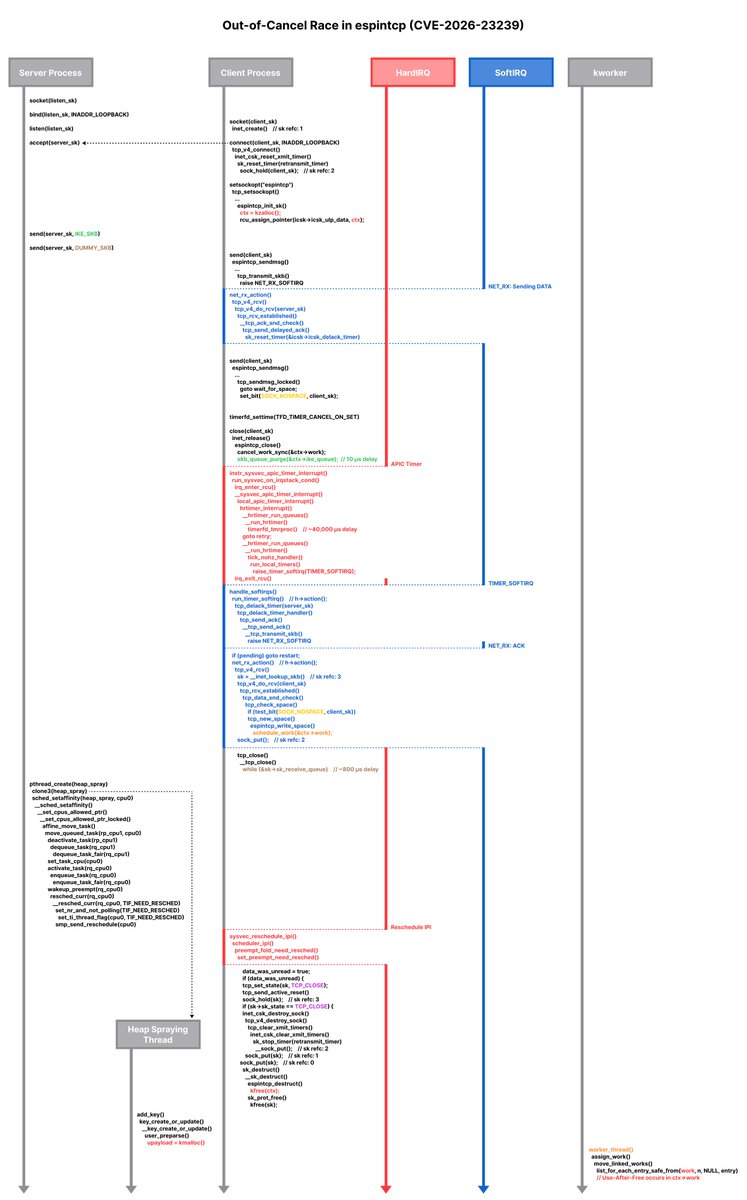
I discovered a race-based vulnerability class in the Linux kernel: "Out-of-Cancel"
A structural flaw where cancel_work_sync() is used as a barrier for object lifetime management, causing UAF across multiple networking subsystems.
I wrote an exploit for CVE-2026-23239 (espintcp). It interleaves Delayed ACK timers, NET_RX softirqs, timerfd hardirqs, workqueue scheduling, and CFS scheduler manipulation to hit a ~Xµs race window.
Blog: https://t.co/980Iv9t4wE
This is the race scenario diagram 😁:
Stealing Salesforce OAuth Tokens via the WAF: A write-up on SFRA context and escalating XSS to Account Takeover using the WAF as a gadget. Hope you enjoy it
https://t.co/vUNKbjUeWk
We previously shared Mono Framework 2.4 running on #ReactOS. 4.0.3 runs and compiles, too!
It has some minor problems: *.exe files don't run without "mono" command (like "mono prog.exe" instead of just "prog") and programs don't compile with gtksharp.
Hi everybody! I did a talk today about pagetable exploitation techniques on x64 Linux. I uploaded the slides to Github
I loved meeting everybody :)
https://t.co/xCb4BrPrNt
ksmbd - Exploiting CVE-2025-37947
Article by @73696e65 about locally exploiting CVE-2025-37947 — a page OOB write in the ksmbd module.
Article: https://t.co/V5LBTtOqxY
Exploit: https://t.co/knpaTnIO2j
Eternal-Tux: Crafting a Linux Kernel KSMBD 0-Click RCE Exploit from N-Days
William Liu @cor_ctf posted an article about exploiting a slab object overflow (CVE-2023-52440) and remote infoleak (CVE-2023-4130) in the kernel SMB3 daemon to gain RCE
https://t.co/kqvwX9NbSK
🚨 New advisory was just published! 🚨
A vulnerability exists in processing IRP_MJ_CREATE requests in driver clfs.sys which could lead to privilege escalation:
https://t.co/YvD8uhaz3c