"It took years — eight years and counting in exile — for me to realize that I was missing the point: we talk about conspiracy theories in order to avoid talking about conspiracy practices, which are often too daunting, too threatening, too total." https://t.co/uMSa2f1uI3
1/ On Julian Assange’s 50th birthday, it’s important to remember his case is not just about Julian Assange. It’s not even just about press freedom. It’s about horrible things being done by the US military that they did not want us to know about.
An ancient alert(1) from 1337 BC was just discovered on Crete:
𐂃='',𐃨=!𐂃+𐂃,𐂝=!𐃨+𐂃,𐃌=𐂃+{},𐁉=𐃨[𐂃++],𐃵=𐃨[𐂓=𐂃],𐀜=++𐂓+𐂃,𐂠=𐃌[𐂓+𐀜],𐃨[𐂠+=𐃌[𐂃]+(𐃨.𐂝+𐃌)[𐂃]+𐂝[𐀜]+𐁉+𐃵+𐃨[𐂓]+𐂠+𐁉+𐃌[𐂃]+𐃵][𐂠](𐂝[𐂃]+𐂝[𐂓]+𐃨[𐀜]+𐃵+𐁉+"(𐂃)")()
https://t.co/hzlo02RHW5
While my Pwn2Own exploit is in the patching, I wanted to share a trivial *no-bug, by-design* full VM escape with persistence PoC for latest Parallels Desktop on Intel and M1. I hope it will wake up a person or two
Writeup: https://t.co/7PwRE4J6nZ
Code: https://t.co/zgFLzKhedl
Our latest blog post explores vulnerabilities and possible Apple copyright violations in Cellebrite's software:
"Exploiting vulnerabilities in Cellebrite UFED and Physical Analyzer from an app's perspective"
https://t.co/DKgGejPu62
I don't tweet a lot.... but when I do, it's a "must read" by @fugueish, "Prioritizing Memory Safety Migrations": https://t.co/obe2RXGRgk, can't decide if the best bit is "mean-spirited packets" or "attacker is able to get at C/C++ attack surface, we must assume they can win."
We just released v1.0 of kCTF our kubernetes based infrastructure for CTF competitions.
Check it out here: https://t.co/Vv5MSeQ4re
With kCTF we tried to address to issues we often heard about:
* no experience with k8s
* worry about introducing security issues
(1/3)
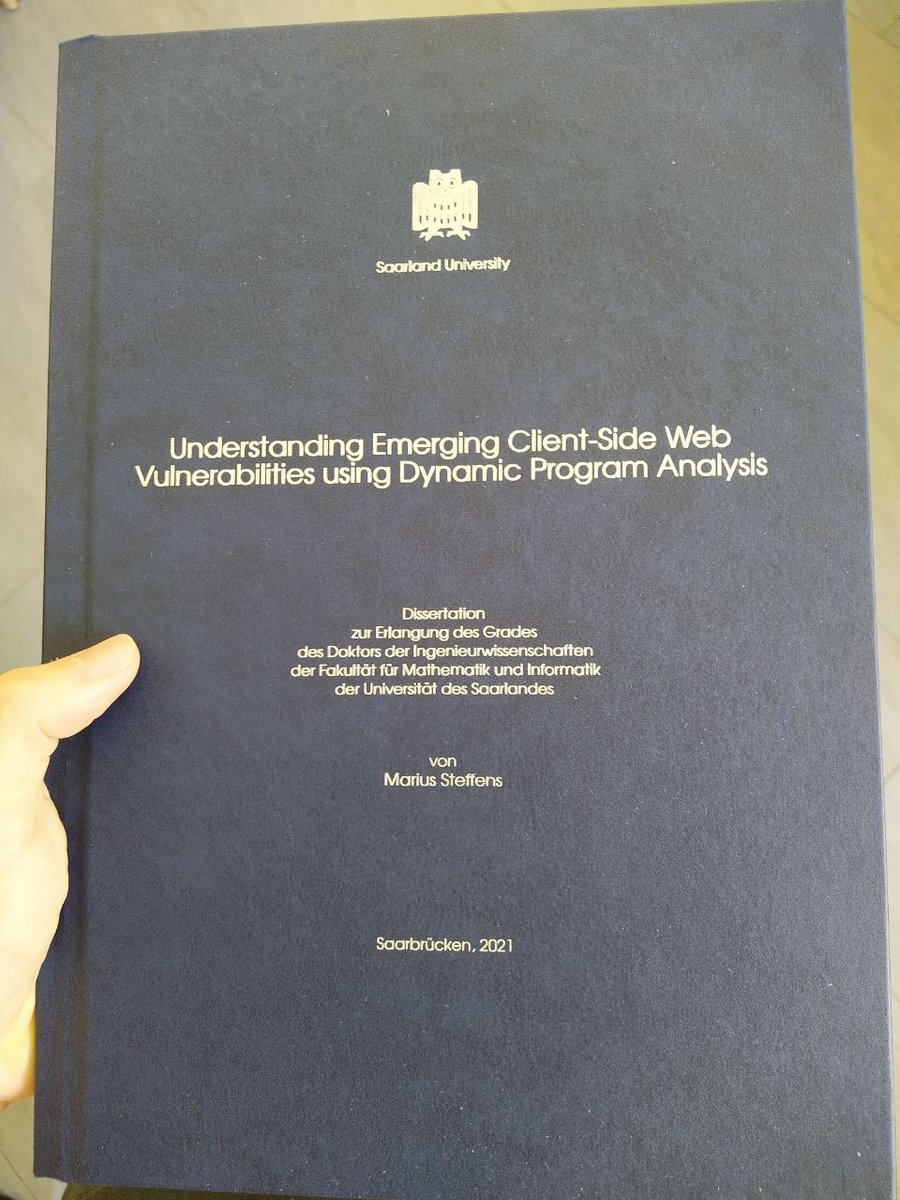
Today I submitted my dissertation "Understanding Emerging Client-Side Web Vulnerabilities using Dynamic Program Analysis". Even though it feels like the end of a journey, I am very excited for the next one waiting just around the corner!
"Unicorn, the underlying Rack HTTP server used in our Rails application, does not create a new and separate env object for each request. It instead allocates one single Ruby Hash that is then cleared (using Hash#clear) between each request that it handles"
https://t.co/gyS79paOMn
Got Prototype Pollution in VueJS?
Here's an XSS Gadget found during zer0pts CTF ->
vuln[.]com/?__proto__[template][nodeType]=1&__proto__[template][innerHTML]=<script>alert(1);</script>
Mike's doc goes into detail on what is necessary for web developers to protect their sites. Read it and share it with your friends. https://t.co/yGf1TIqFOE
We've shipped full state partitioning to the Strict mode of ETP in Firefox! I can't wait until we're able to bring this to all users.
https://t.co/8G52c3achj
Regular reminder that if you are running anything in PHP, you really want to be using Snuffleupagus: https://t.co/wpO8HTZEVU
PHP is still extremely common and this is a cool project!
Earlier today, we released a new version of the Tsunami security scanning engine. We added web app fingerprinting, new detection capabilities, a scanner test bed, and much more. Additional updates are planned for the coming months. @magl22@paradoxengine https://t.co/AafgBgGFHm




")()
https://t.co/hzlo02RHW5 https://t.co/1XqxQ2KM2D](https://pbs.twimg.com/media/E2QjUJQXEAE2-SF.png)