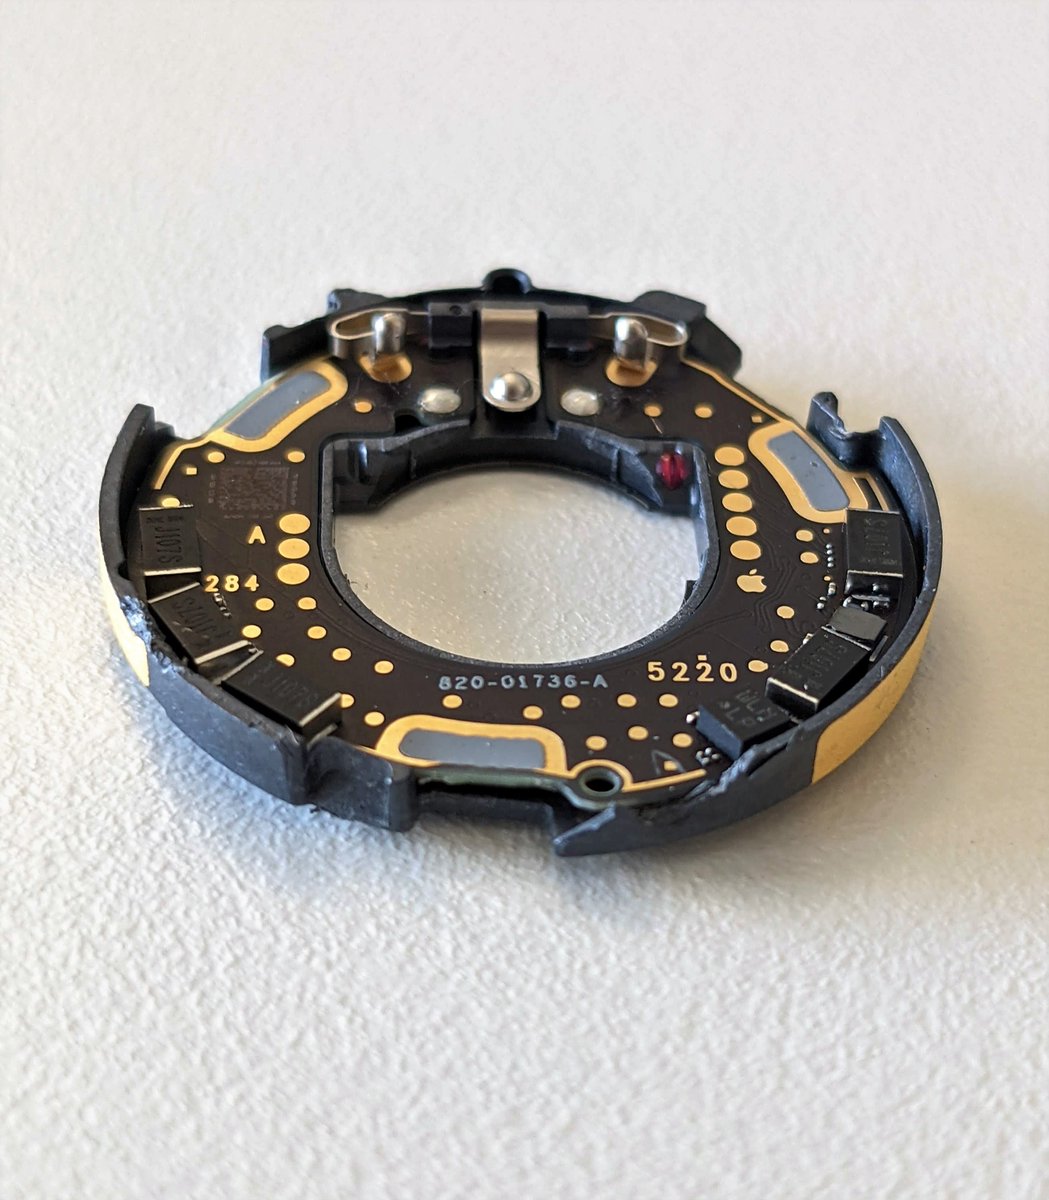
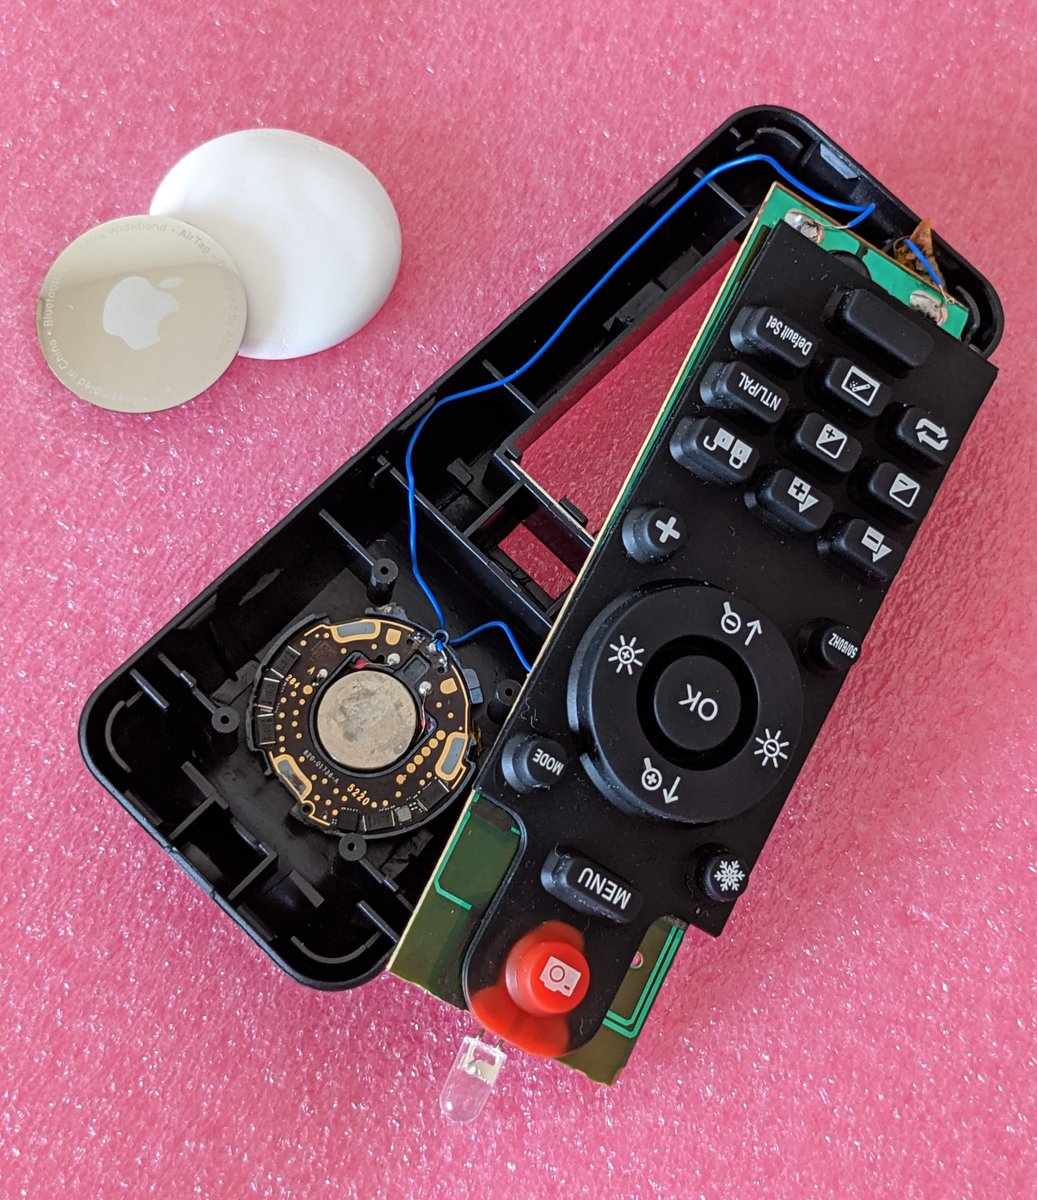
I wrote about AirTag security and privacy issues, hardware design, and how Apple's FindMy network is vulnerable to misuse by design.
https://t.co/fEuDGrY8aE
@0xcharlie@sickcodes Heads up - the link you used populates your work email address (not that it would be hard to guess).
It seems iterating the "elqContactId" URL parameter allows you to enumerate the email of everyone who has signed up. @Automotive_IQ
I wrote about AirTag security and privacy issues, hardware design, and how Apple's FindMy network is vulnerable to misuse by design.
https://t.co/fEuDGrY8aE
@whitequark Thanks for reading!
I think if Apple wanted to ensure the effectiveness of the privacy features they could have easily done a better job. The whole product seems like an unnecessary liability for them.
@RpunktOfficial @LooicC It seems so. @iamcais mentioned no problem with one missing.
Since that original tweet I investigated the circuit further and found those large capacitors are used for the speaker supply while playing audo, around 5V, separate from the microcontroller supply.
Apple AirTag teardown!
Let's find out how Bluetooth LE, UWB, NFC, 3+ antennas, an accelerometer, and a speaker fit into an enclosure barely larger than the coin cell powering it.
1/x
@Iskuri1@fuzz_sh I'm curious how you received NFC as it is below the minimum frequency of an RTL-SDR. Looks like the 2nd harmonic was strong enough to tune to?
@Mr0Inka Thanks! If you can glitch to unlock SWD access you can change the NFC pins to be GPIO in the UICR. Easier might be to physically damage the antenna from the outside.
I'm not aware of a disable pin. What's your use case to disable NFC?
@ghidraninja@LennertWo@p1onk@colinoflynn Would be interesting to try flashing/patching the firmware to run on other hardware such as an nRF52 dev board to speed up testing.
@colinoflynn I found even the U1 chip is powered through VCC1. Measuring with a sense resistor:
https://t.co/uTsLXGm8VD
Maybe VCC2 is indeed just to detect battery presence, to reduce chance of brown out during battery insertion by waiting for a smooth supply voltage from 2 points of contact.
@colinoflynn It only draws power through VCC1 in normal modes. I measure only ~50nA into VCC2/TP5 so it is only sensing voltage there. Although I don't have a way of using precision finding to see if VCC2 supplies the U1 chip.
(BTW TP1 and TP 38 are the voice coil pads)
@ghidraninja You briefly mentioned OTA updates are possible.
Is there no secure update implemented to check the update signature??? Or some kind of protection on triggering DFU mode?
This sound like the bigger story!
@barsteward@colinoflynn At least that is how I believe the FindMy system works. But I agree Apple thought about this so I give them the benefit of the doubt that they made some changes to avoid these threats, so that having complete control of the hardware is not a problem.
@barsteward@colinoflynn You're right about the tag.
But anyone can download encrypted location history from the backend for a given public key. You can use the private key (same one on the owner's phone, shared during setup) to generate all the public keys to request the history and decrypt the data.
@barsteward@colinoflynn It's trivial to clone a valid AirTag broadcast (there is no authentication) so yes custom FW could cycle through recorded public keys.
Also, the lack of device hardening risks being able to extract the master private key from a lost AirTag to decrypt the owner's location history.