To teach a lesson,
After Wiz rushed to buy php2shell domain and use its marketing machine to steal the spotlight, I spotted "phpbleed" in a recent Calif tweet and bought https://t.co/hQYMb3AZlk before wiz could pull the same stunt again.
A big budget can buy a domain. It shouldn't buy someone else's research credit.
If you have contacts at CISA or in the press, do the right thing: make sure the researchers who actually did the work get the recognition they deserve.
Hack the planet. Credit the researchers.
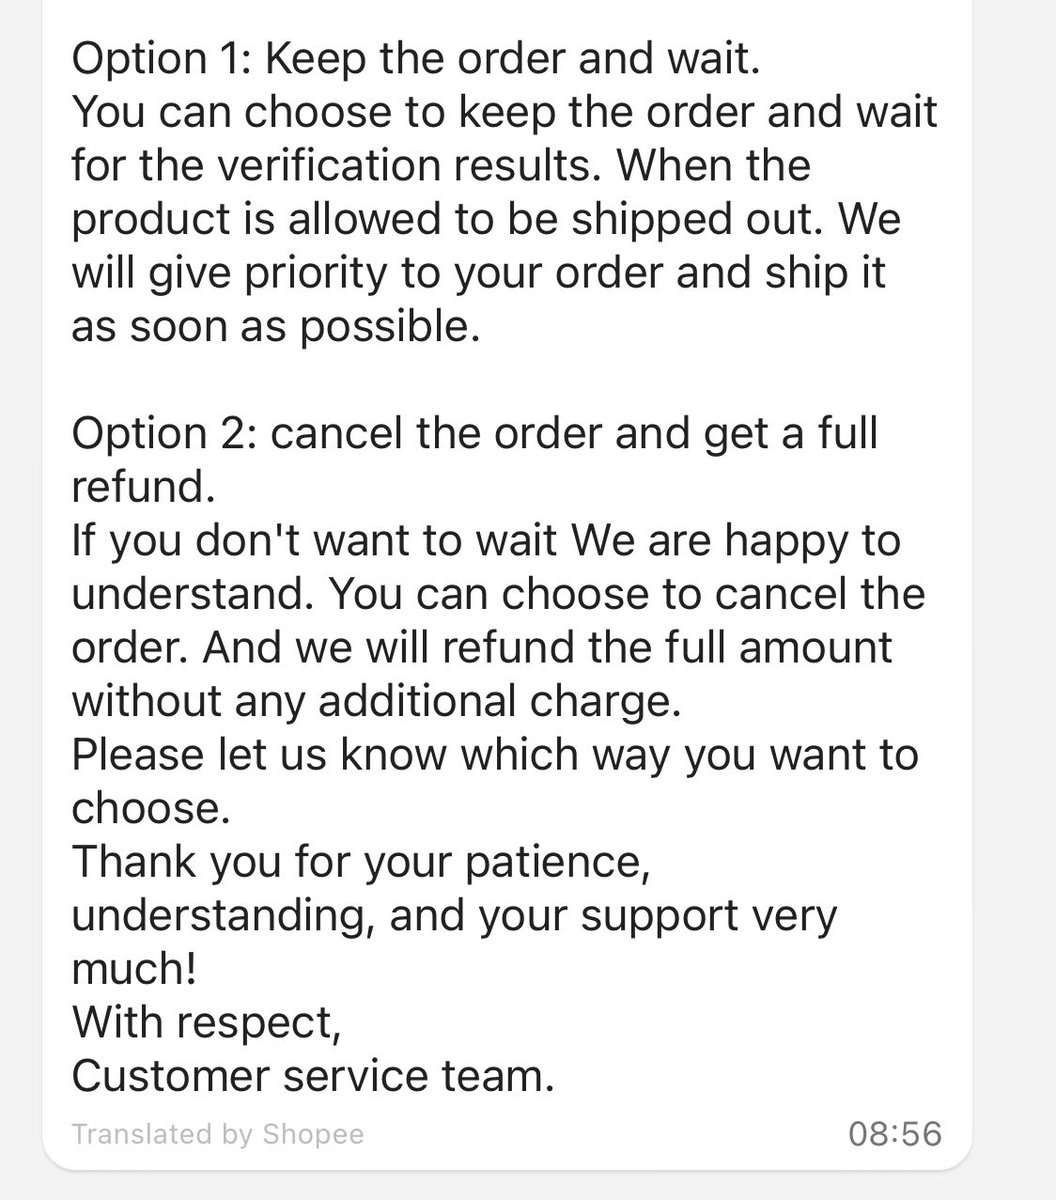
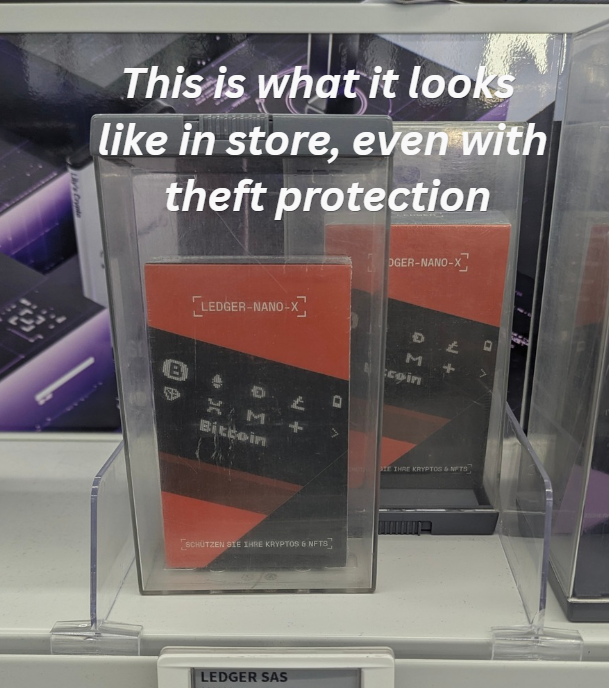
Tried to buy a Ledger Nano X from an authorised seller here in Thailand (Shopee), hoping it was a bugged one so I could take a look for myself... He wouldn’t sell it though 😂
Wonder how they’ll do the inspection though… X-Ray all the current stock in the said Malaysian warehouse?
UPDATE: I can confirm that the Ledger supply chain is compromised in Europe as well. @Ledger should initiate an immediate product recall to protect users.
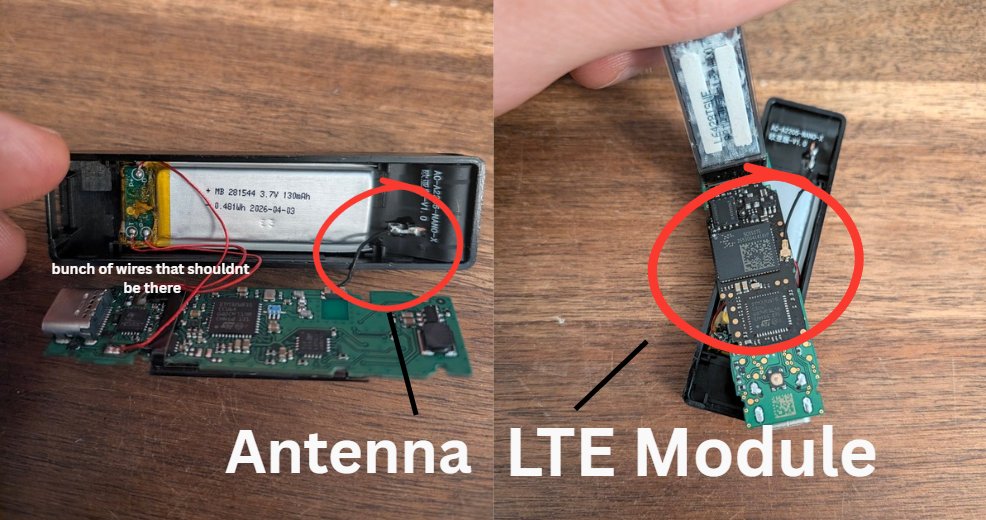
I just purchased a second device from a different Mediamarkt location today, recorded the unboxing process, and discovered spyware once again (video linked in the second tweet).
The device was compromised in the exact same manner, featuring identical modifications (such as additional cables and an LTE module). This indicates its a widespread issue rather than an isolated incident, potentially affecting Ledger inventory across MediaMarkt and Saturn stores throughout Europe (comprising over 1,000 stores across 11 countries).
My initial hypothesis was that these devices were returns that looked unopened to the employees and were just sold again as new however, a MediaMarkt employee confirmed that the device I purchased was not a return, and that returned Ledgers are sent directly back to the manufacturer rather than resold.
Store records show the inventory originated from Aqipa GmbH. While Ledger's CTO was unsure if Aqipa serves as the direct distributor between Ledger and MediaMarkt, it appears to be the case. Given that Aqipa distributes across Europe, any physical retail store receiving stock through them may be at risk.
I sent the first ledger to mark and the second one is going to ledger now, so that they can analyse it.
If you purchased a ledger from anyone other than the official ledger store, make sure to check your device!!
so about the $86m ledger drain. everyone’s screaming “ledger got hacked” again. i spent the evening digging and it’s dumber and scarier than that
there’s a shop in malaysia called cryptobilis that sells hardware wallets. ledger has it listed as an official authorized reseller since at least 2022, for malaysia, indonesia and the philippines. legit shop, real devices, years of normal customers
this spring the founders sell it. the deal comes with an NDA: they can’t tell anyone about the sale until october 19
by august the company registry shows one owner with 100%. some guy from heilongjiang, china
the shop keeps running like nothing happened. the site, the name and the “authorized by ledger” badge all stay up
then on oct 8 @MagicalTux posts photos of a ledger he cracked open. hidden under the screen there’s an extra little board with an LTE modem and an eSIM. it just watches the display. you set up your wallet, your 24 words show up, and they get sent out over mobile data. ledger’s genuine check doesn’t catch it because the actual ledger chip is real. his device came from malaysia
https://t.co/vRuBM0xIfR
that post does 120k views
22 hours later someone sweeps everything. 203 BTC hits two addresses in literally one block. ~$58m USDT moves on tron in the same hour. i added up all the wallets: ~$91m
about 7 hours after that ledger says “we’re investigating” and asks cryptobilis to pause sales
cryptobilis is still on ledger’s site as an authorized reseller
to be fair, nobody has officially tied the new owner to the bugged devices yet, and ledger hasn’t confirmed how it happened. but read it as a business plan:
get authorized, sell real stuff for years, quietly sell the company under an NDA, keep the badge, ship devices that phone home, then drain everything the second someone notices
and was ledger even told the shop got sold? nobody’s said so
“authorized reseller” means ledger trusted whoever ran the shop back in 2022. says nothing about who runs it today
bought your hardware wallet anywhere but the manufacturer? open it up today, ledger literally has a guide for that. then move to a fresh seed on a device bought direct
wonder who’s going to answer for this: the chinese frontman from heilongjiang, the shop’s previous owners, or ledger itself
@Ledger clearly needs to keep a much closer eye on who they call official resellers, and take way more responsibility for who sells their devices and how
Heya @vercel, two PRs are pending for the https://t.co/oYIRvzVBXk project, and both contain hidden DPRK malware. This is a VERY popular NPM package, and I want to make sure you kill both PRs. Here's my GitHub Issue: https://t.co/HBcEaQ0zxb
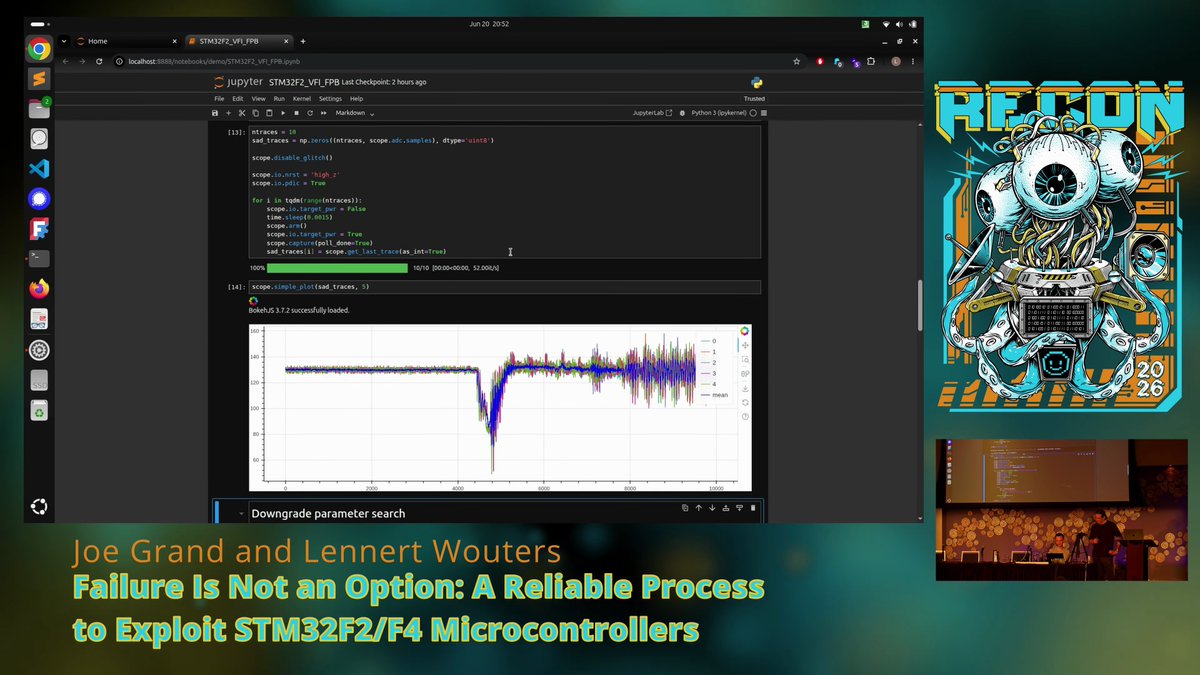
For over three years, @LennertWo and I have worked on improving fault injection attacks against STM32F2 and STM32F4 devices to make them more repeatable and reliable. It's been a roller coaster of late nights, bricked chips, and questioning our life choices, resulting in over 100 million total glitches, a new attack strategy, and flash memory recovery from dozens of locked targets with a 100% success rate. I'm super proud of what we've done and happy to officially share it with the world!
https://t.co/4FpA733UU5
https://t.co/KMyrd7Gi2x
https://t.co/0z2osFwFOf
It appears that @kernelstub has been banned from @github for reverse engineering Flock Cameras publicly.
The entire github account is gone, not just the repository in question.