Advanced Binary Analysis workshop material is now on @GoSecure_Inc 's GitHub account! https://t.co/YdMI4RZxxU I'll be taking the VPS offline shortly, so if you wanted to try the workshop on your own, clone this :) -- Monitor @NorthSec_io to know when the videos are live
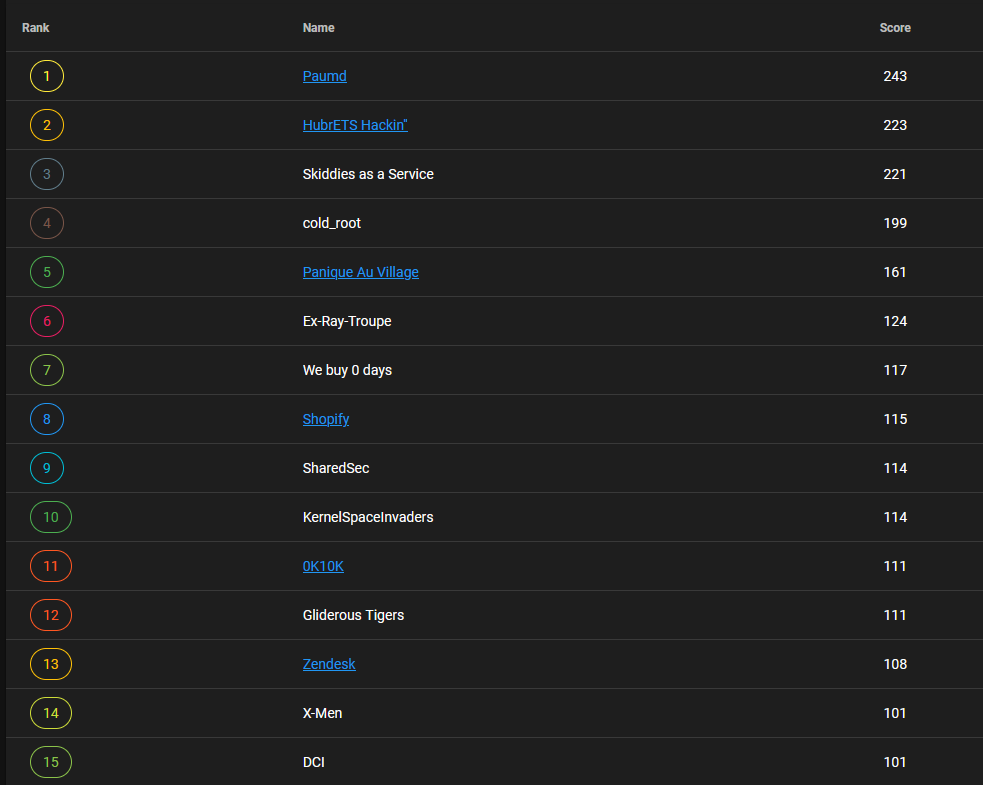
Achieved first blood jackpotting the ATM at @NorthSec_io#nsec2023 CTF this weekend! The most insane and thrilling hack I've pulled off at a CTF so far, it certainly caught the eyes of everyone in the room and the event organizers, describing it "straight out of a movie"!
🔥 WARMUP 2023 💪
All challenges are now released! You have until May 7th to complete them!
Tous les challenges sont maintenant disponibles! Vous avez jusqu'au 7 mai pour les compléter!
👉 https://t.co/37vmO6rJuD
The hardware badge is back! Here's a sneak peek of our [naked] prototype. Don't miss out, secure your badge now before we run out! Early bird tickets are available until Feb 17th.
https://t.co/mOVIQn5FxB
#ctf#conference#training#cybersecurity#infosec
There is still time to apply for one of our trainings in cyber-security! NorthSec is pleased to announce its high-quality training sessions, given by the absolute best experts in their field. https://t.co/oFYX9z0b6p
@el_d33 My personal approach to exiting vim has always been throwing the laptop out of the window and getting a new one. You don't wanna know what happens when I accidentally open vim in a DC blade. (... /s)
#GivingTuesday
NorthSec Volunteers share with you today: https://t.co/Qb8TPD7c7a
A great CTF platform to sharpen your skills. You will also be able to practice previous NorthSec CTF Challenges!
Why don't you take some time during this Thanksgiving weekend to learn how to attack the RDP protocol? Watch this 40 minutes technical workshop presented by @obilodeau and @alxbl_sec: https://t.co/ewP92R47a1
#pentest#rdp#redteam#honeypot
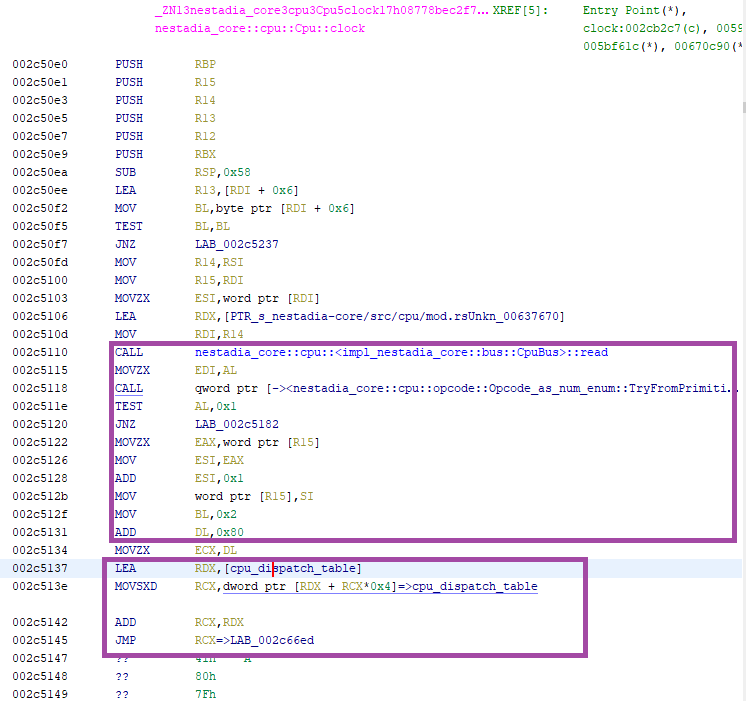
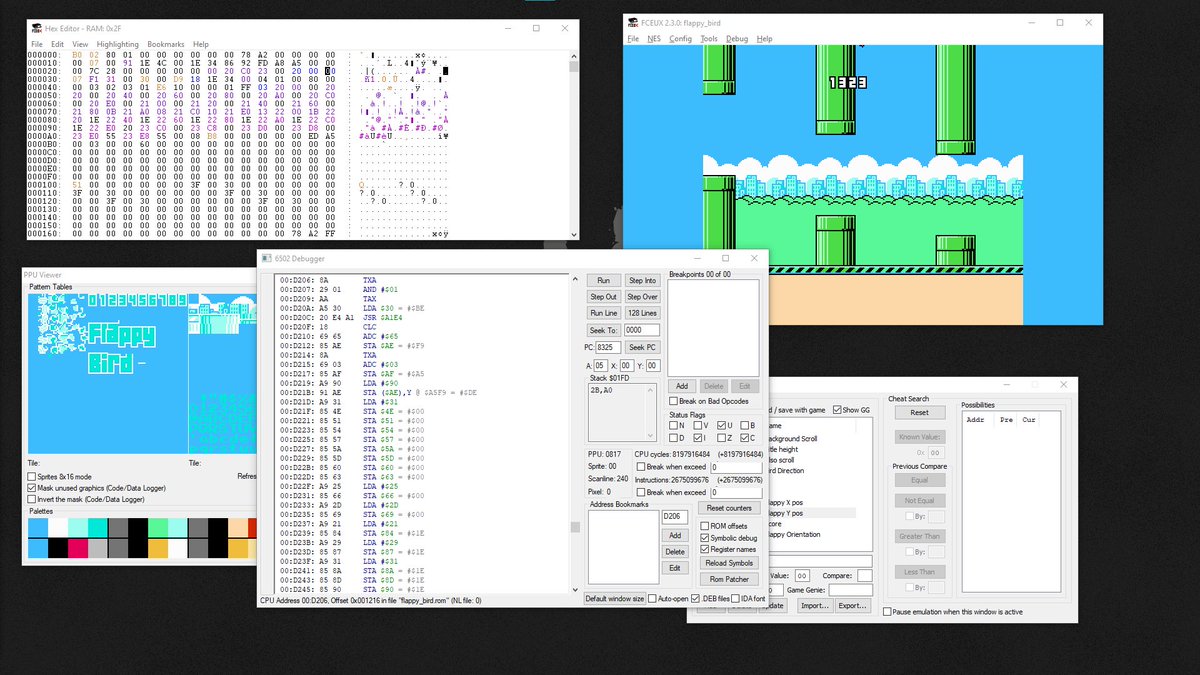
This week is season 18 episode 1: NorthSec CTF 2021's Nestadia! An in-browser NES emulator multi-flag track.
🌎 https://t.co/l40Gxvplc4
🗓️ Wednesday 7pm ET
📺 https://t.co/DlsTUbZjbs
💬 https://t.co/1SeKnBkGBp
#reverse#ctf#rust#assembly #6502 #x86#NES#TAS@NorthSec_io
We are thinking of stopping doing events every month and switch into a season mode. Meetups would have short names (ex: S12E3) and we would take breaks in summer and January to prepare content for the next season. h0h0h0 would stay. Still unsure online or in person. Thoughts?
@montrehack Season format sounds like a good idea, as it would let us plan the content ahead of time and have a complete schedule ahead of time. Easier for both advertising the event and scheduling for participants.
@Auroden@NorthSec_io Thanks for the kind words! I'm not convinced that 48 hours would've been enough to get all the track done. Even with no rabbit holes at all. I heard about flag 4 and I don't think we would've solved it within the time limits. I'm going to try to try it in the coming weeks :)
At last, here it is! Part 2 of my Nestadia writeup from @NorthSec_io 2021. In this one we capture the 3rd flag by crafting a malicious ROM to exploit a backdoor in the NES emulator. Check it out :) https://t.co/GMpUo03R2V
Good morning :) Post @NorthSec_io blues has got you down? Fear not! Here's a writeup for Flags 1 and 2 of the Nestadia Reverse Engineering Track. Flag 3 writeup is on the way and hopefully a bonus flag 4 if time allows! Cheers! https://t.co/FdRjvgKkCZ
Clutchest flag submission ever at 2:59:52 thanks to @yol0nline :) it would have been sad to miss the deadline after spending most of the CTF on that single flag! Great challenges again this year :) Thanks all for organizing such a wonderful event!!
Welp, Looks like we ran out of time on the workshop! Sorry for those who had questions, feel free to reach out to me by DM (or reply) and I'll try my best to answer them!