🚨 FDD identified 11 fake news and watchdog websites promoting Qatari interests and seeking to discredit the Qatargate investigation.
Their content was cited by major think tanks and AI tools.
Read the investigation 👇
The networks target at least 250 American individuals, organizations, and companies — including sitting senators and major think tanks — labeling critics as pro-UAE, pro-Saudi, or pro-Israel. Max Lesser & Maria Riofrio: https://t.co/j1raiaUU4B
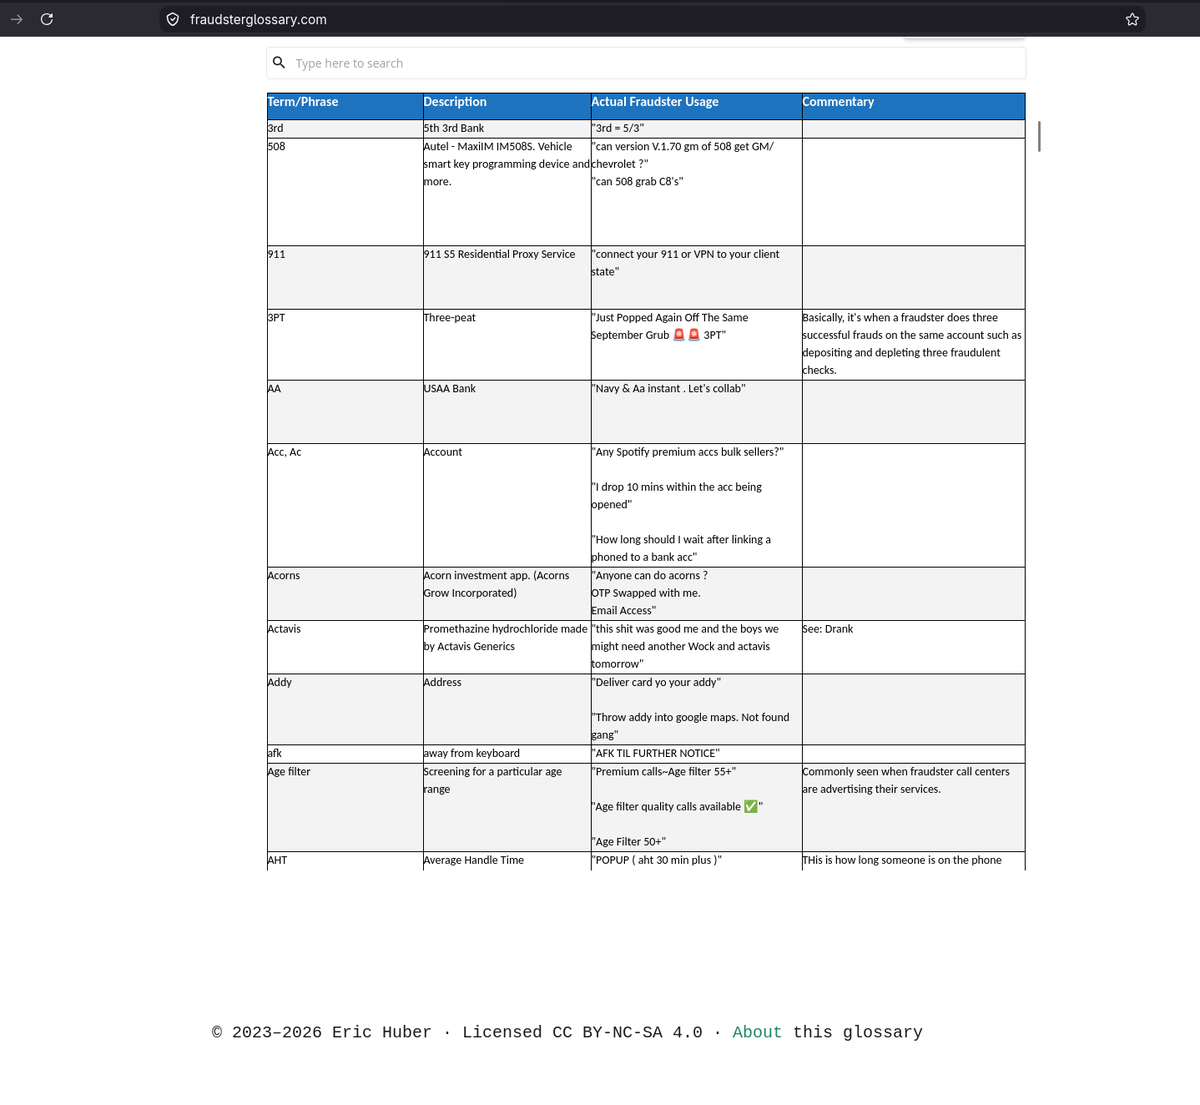
Using the new @OSINTindustries module with the Telegram Fraudster Glossary it becomes trivial to track criminal organisations and their TTPs.
https://t.co/h3kUrhMzXf
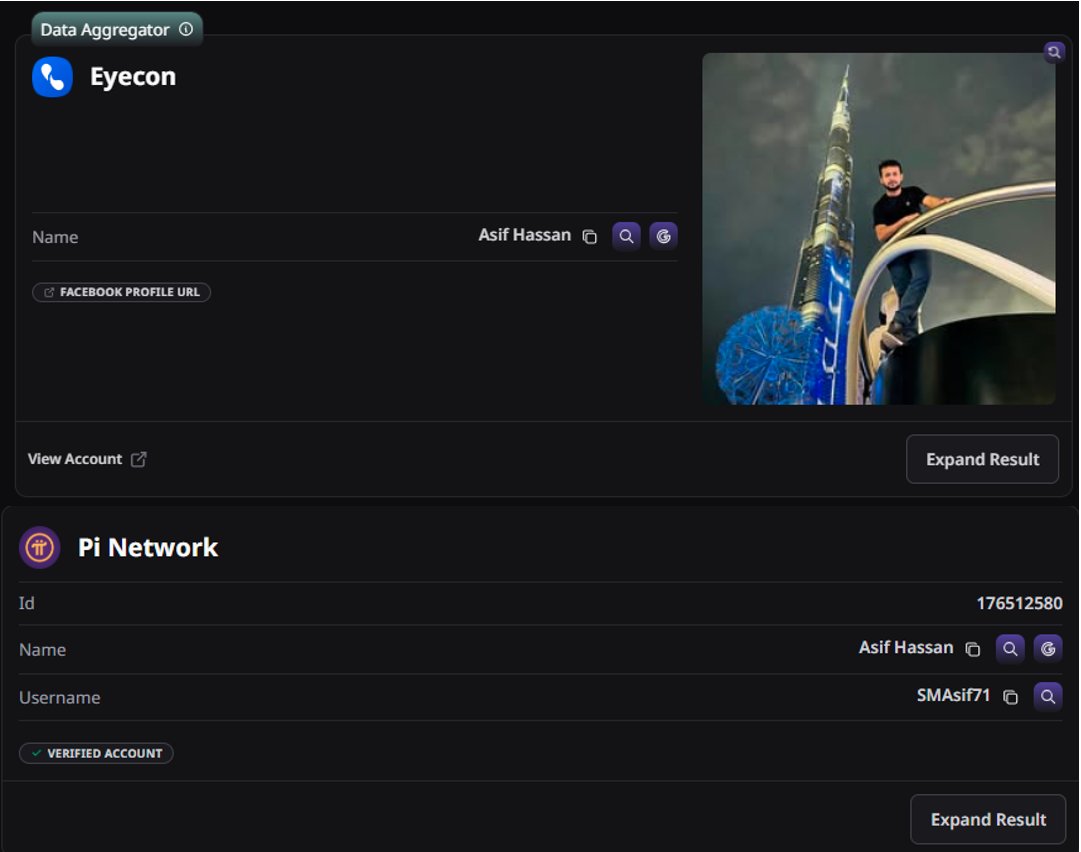
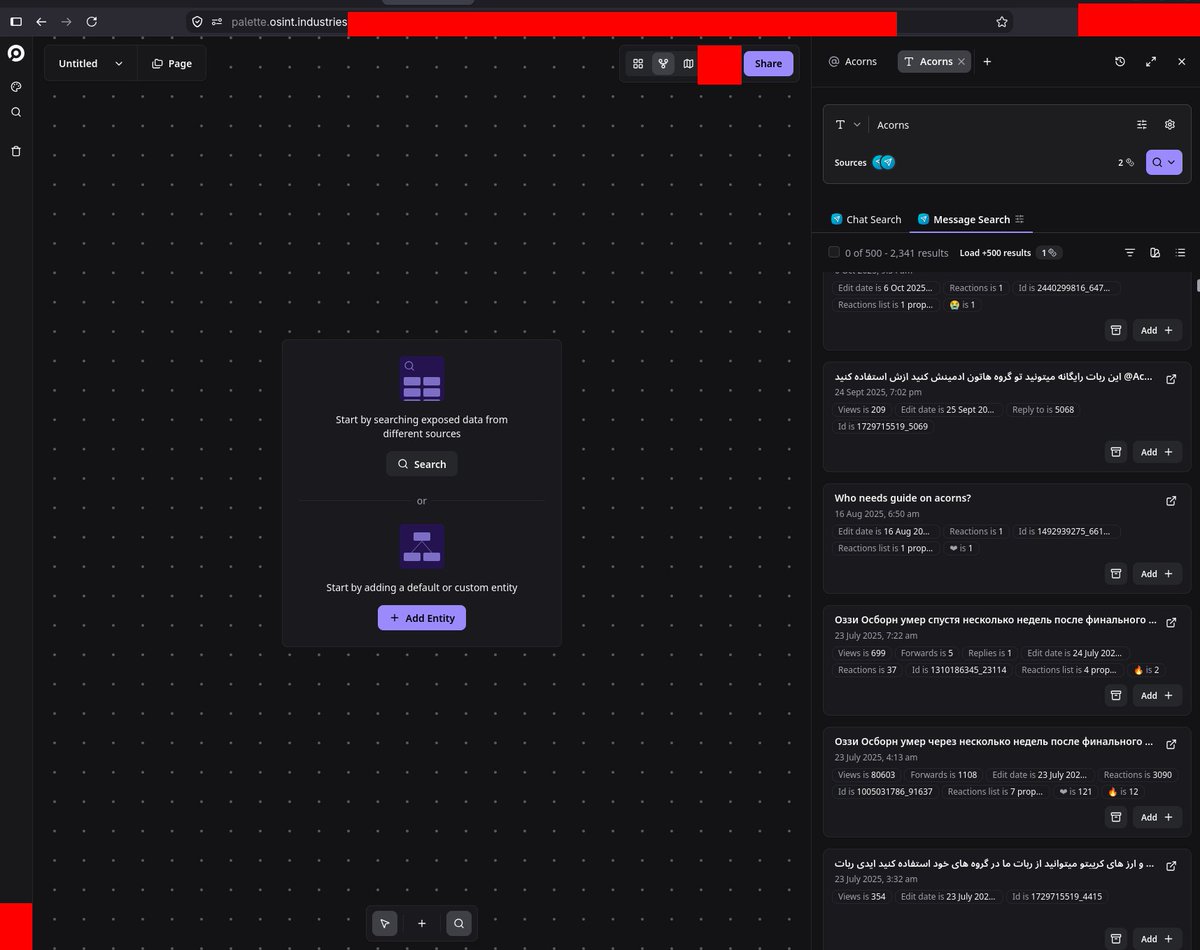
🚨 You can now search Telegram chats and messages, pull usernames, IDs, and channels, and map entire networks straight from your investigation canvas.
No exports. No jumping between tools.
Introducing Telemetry: Telegram Intelligence, built into Palette.
@capitalsitzoem@Yossi_eli האיראנים אז העלו לטלגרם ובכמה דומיינים, ממליץ לא לבדוק שם.
יש אתר שמופיע בסרטון עם הURL חשוף, אתה יכול לגלוש ולבדוק שם. לא הייתי מוטרד יותר מדי, זה גם ככה הוכן מהדלפות אחרות ואוסינט שהם אספו.
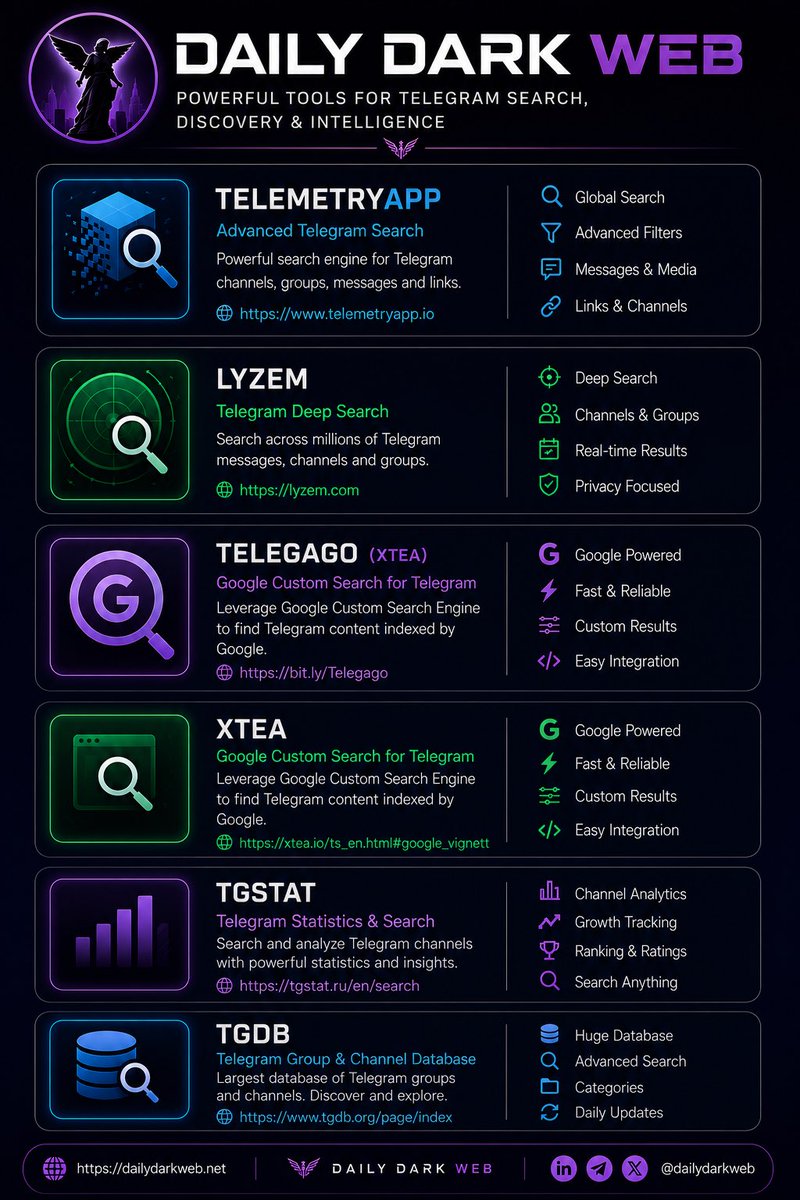
Telegram has quietly become one of the largest open-source intelligence environments on the internet.
From threat actor channels and leaked databases to malware distribution and underground communities, a significant amount of cyber threat activity now lives inside Telegram.
Here are some powerful Telegram search and discovery tools every OSINT analyst, threat hunter, researcher, and investigator should know:
* TelemetryApp
* LYZEM
* Telegago
* XTEA
* TGStat
* TGDB
These platforms help analysts search channels, messages, groups, media, and indexed Telegram content far beyond Telegram’s native search capabilities.
Most researchers only scratch the surface of what is publicly accessible.
Do you want more content like this? Please subscribe and support our work:
https://t.co/O5fslMgfuw
What do you use? Share 👇
#DDW #Intelligence #Telegram
Eekad claims to be an independent open-source investigation platform reaching millions in the Arab world. But analysis reveals significant ties to Al Jazeera, Qatari media & the Qatari government.
New FDD Memo by @ari_ben_am:
https://t.co/ebm3ybpBnA
Iranian Influence Operation Floods X With Anti-Protest Messaging
@FDD_CCTI has identified an influence operation likely linked to the regime that delegitimizes dissent, intimidates protesters, and reinforces regime narratives. https://t.co/lp0ql0WtAt
Israel is known worldwide as a cyber powerhouse, and yet, Iran-linked hackers have managed to pull off several successful breaches and leak sensitive data online.
@FDD_CCTI cyber expert @ari_ben_am quoted: https://t.co/Ub2bZpGL5B
👮🇷🇺 Yesterday @RecordedFuture published our latest report on Russian influence network CopyCop, also known as Storm-1516.
We identified over 200 new inauthentic websites linked to the network targeting the US, France, Canada, Armenia and Moldova peddling Russian narratives and targeting elections.
Report here: https://t.co/aXUAUeUenc
Important work done by Max Lesser and our team @FDD_CCTI Chinese malicious cyber activity is persistent and comprehensive - this is a skilled adversary who is not interested in cooperation they just practice exploitation and attack https://t.co/Mh0WDvmRp6
This analysis by @ari_ben_am examines three basic categories of Iranian influence operations:
1️⃣Cyber-enabled influence operations
2️⃣Online influence operations
3️⃣Physical influence operations
Read here 👇
https://t.co/YT5DYXn49C
Yesterday, CCTI released "A Year of Meming Dangerously: Iranian Influence Operations Targeting Israel Since October 7" by adjunct fellow @Ari_ben_am. Read here: https://t.co/f65xF799Ph
This new FDD Memo by @ari_ben_am examines three basic categories of Iranian influence operations: cyber-enabled influence operations, online influence operations, and physical influence operations.
📝 Read here: https://t.co/TyPagugXiC
This new FDD Memo by @ari_ben_am examines three basic categories of Iranian influence operations: cyber-enabled influence operations, online influence operations, and physical influence operations.
📝 Read here: https://t.co/6jgqZad2l2
Our team at Silent Push has been hard at work on the largest report we’ve ever made public – and along with Reuters – today we’re explaining how North Korean threat actors associated with the “Contagious Interview” subgroup created 3 front companies...🧵