🍎🐛 I got Claude making this, maybe it's useful for others as well.
Every Apple security advisory since 2002 - parsed, indexed, charted. With links to writeups, POCs and presentations.
https://t.co/aSv0PZpQj3
How does the new iOS inactivity reboot work? What does it protect from?
I reverse engineered the kernel extension and the secure enclave processor, where this feature is implemented.
https://t.co/VbdxhueXtL
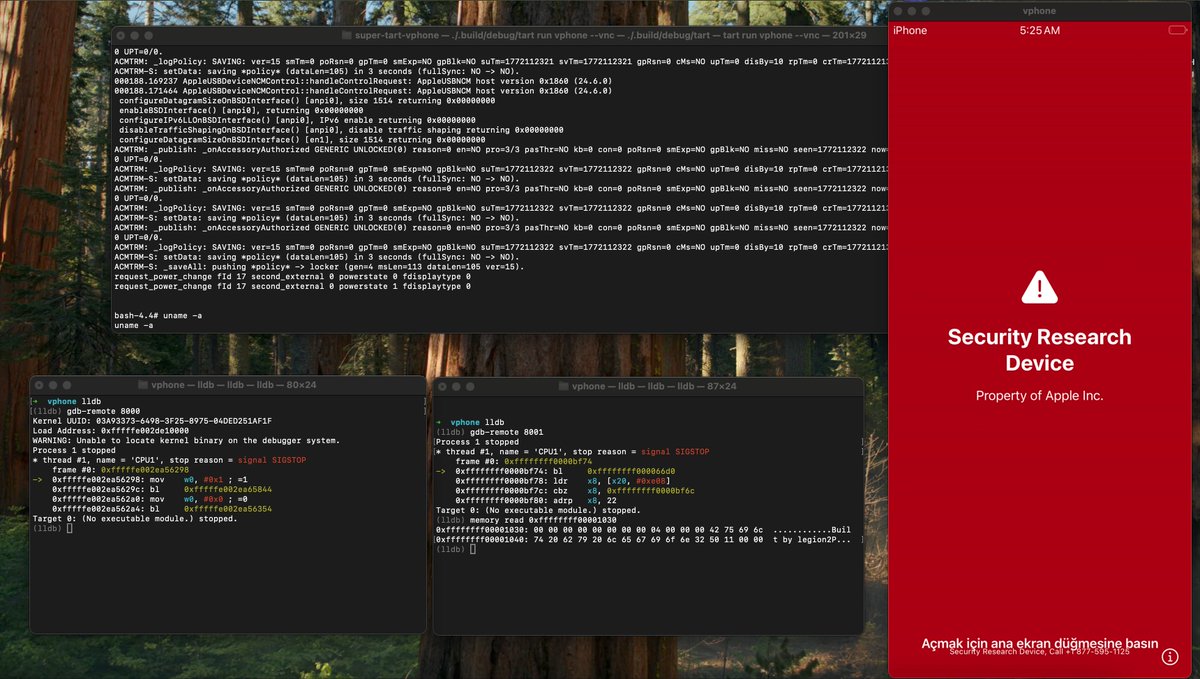
I have never seen a more infuriating, inconsistent and idiotic API than the lldb python API. Not only you have to code C++ in Python, nothing works how you expect it or how it would be even remotely reasonable
Even though they missed out on registration, @aahmad097, @Rembown, @m40282845, @0xShad3, @thegrandpew (@ht3labs) gave quite the demonstration of their exploit prowess against the QNAP TS-464 & the Synology BeeStation. We look forward to seeing their work in future competitions
Another amazing @0x41con! It is consistently the best con of the year for me, and the only one I really look forward to. See you all at the next one!
https://t.co/9ziUkgfubK
Fun Fact: I found those signal bugs (sendmail and openssh) while writing the chapter on signals for TAOSSA. Writing stuff you think you know well helps you to discover your blind spots, and also consider new ideas!
I like how digital nomadism leads to find the core of who you are and what you do. People worship "belonging" as a high goal but it's actually the opposite. By rejecting all ways of saying, "this is my country, my community, my family, my home", go deeper to learn what is "me/my". Find out that most identities are false identities and holding onto them is comfort, shedding them is... evolution, I guess? Like a butterfly hatching out of a chrysalis...
Congratulations to my @census_labs colleague Zisis Sialveras (@_zisis) for being accepted to present his amazing work on VMware vulnerability research and exploit development at Black Hat USA 2024: https://t.co/74q3KL0CaI
One of the most common tools that I need regularly that doesn't exist is a Linux command line tool to approximately port symbols from one ELF to a very related one.
A sort of command-line-bindiff-with-sym-porting.
All the details about this vuln and much more will be revealed tomorrow by us (me, @bzvr_, @kucher1n) during our talk “Operation Triangulation: What You Get When Attack iPhones of Researchers” at #37c3 (14:45 CET). There will also be a live stream. https://t.co/g5cQLf6za4
The optimal path to exploit development is:
1. Software engineering
2. Reverse engineering
3. Exploit development
And each of these areas build on and improve the others.
Being a software engineer part of an enormous monolithic project requires skills in reverse engineering to understand other people's code.
Being a reverse engineer requires software development if you want to make tools to improve / automate your process.
Being an exploit developer requires both to be able to locate a vulnerability and write a poc to take advantage of said vulnerability.
I want to recommend again the excellent "all things IDA" YouTube channel by my friend and former colleague Elias. Really terrific content which isn't usually available for free!
https://t.co/M38eCYb2fV
Me, starting to analyze a new piece of software: I basically know how this works already, I just need to learn a few of the finer details
Me, a week later: I don't know anything about this software, or computers in general.