The opinion is inherently flawed.
CTFs are great to develop problem solving, grinding, finding niche solutions of a particular problem. Which btw is one of the skill a good employer would look out for.
Personally, Im from bug bounty background but anyone saying CTFs are time waste triggers me. As auditing codebase Ive often referred to CTFers blog when there’s a niche problematic code I have found, my first instinct is to see if someone solved similar problem in form of CTF before putting hours into it.
OP also seems to confusing HackTheBox style CTF as primary type of CTF when in reality CTF have broad scale of different type of problems to solve.
Hiring is not just knowledge, it is networking, skills, you marketing yourself and what not. So no one approach is better than another. Its always mix of everything. Even then, a person who is a top notch CTF player would land a role which is generally requiring much more technical depth and grinding. The checklists you describe to learn could be read up in a month or two at max to prep for roles. For example: I hadn’t touched SAML for 5-6 years. Until I had to reverse SAML library bugs, it didn’t make me SAML expert but enough to find new 0days, answer an interview question and it took 1-2 days.
Do CTFs, read blogs/hacktivity, do bug bounties, more importantly do things rather than just reading. Getting hired is just by product of all that.
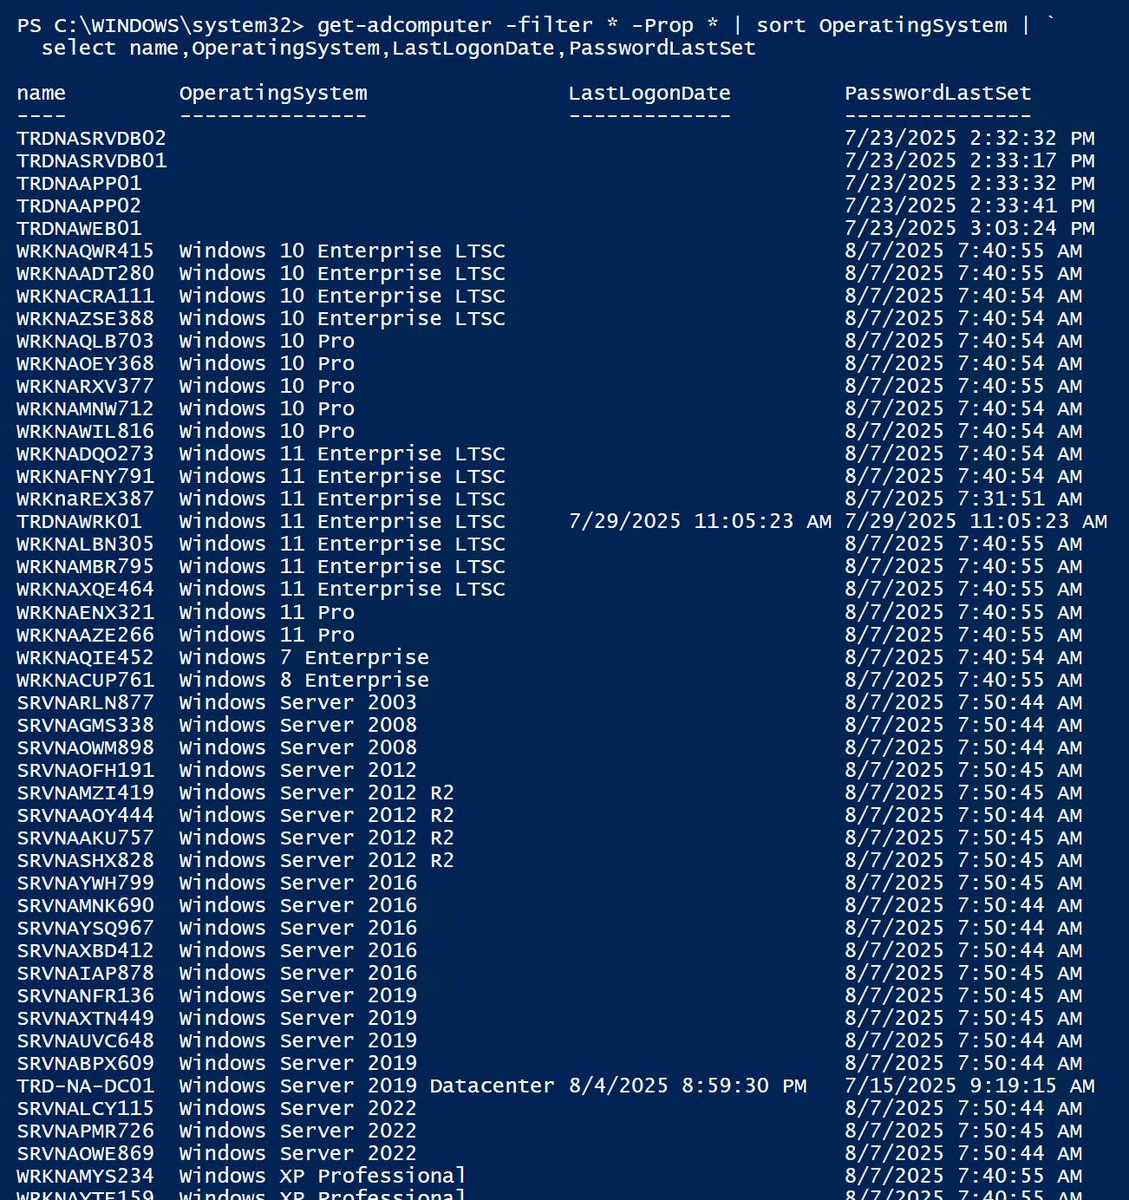
Active Directory computers should be reviewed about once a year. Old operating systems can hold back security progress like keeping SMBv1 and NTLMv1 active. Inactive computers should be discovered and disabled when no longer in use (and eventually removed).
The OperatingSystem & PasswordLastSet attributes are self-explanatory, though we can use the LastLogonDate which represents the last reboot of the computer. The computer password should change every ~30 days by default. We can correlate the PasswordLastSet & LastLogonDate attribute values to determine if a computer is active or not. A blank LastLogonDate value means the computer object is just that and not associated with an actual system.
PowerShell code:
get-adcomputer -filter * -Prop * | sort OperatingSystem | select name,OperatingSystem,LastLogonDate,PasswordLastSet
#ActiveDirectorySecurityTip
A system was completely locked up by malware. Antivirus failed. We had no access to the hard drive…
But we had one thing: a full packet capture.
Here’s how I used Wireshark to trace the infection, extract the malware, and analyze its behavior.👇
The Setup:
The infected host: 12.183.1.55
I had the full .pcap from the time of infection.
My goals:
Identify where the malware came from
Extract the file from the packet data
Analyze what the malware did
Look for signs of worm-like propagation
Targeted Timeroasting: Stealing User Hashes With NTP : https://t.co/cbNhA7zm2c
Ref :
TargetedTimeroastPublic :
Tamper Active Directory user attributes to collect their hashes with MS-SNTP : https://t.co/uUDb0TbCJ0
Shout out to this guy @MalwarePeter his influence has inspired countless individuals to pursue careers in cyber sec, significantly shaping the next generation of cybersecurity professionals. The scale of his contribution is truly extraordinary, it's so insane .
.@ArmanSameer95's script for automating the scanning of targets 💡
This script continuously monitors targets using Axiom and multiple @pdiscoveryio tools and even notifies you when it finds something!
Check it out 👇
anyone using @solana/web3.js, versions 1.95.6 and 1.95.7 are compromised with a secret stealer leaking private keys. if you or your product are using these versions, upgrade to 1.95.8 (1.95.5 is unaffected)
if you run a service that can blacklist addresses, do your thing with FnvLGtucz4E1ppJHRTev6Qv4X7g8Pw6WPStHCcbAKbfx
I was playing this CTF, I was number 1 at some point but couldn't maintain it.
Here's a writeup for the AD challenge.
https://t.co/zHRzAkOWPR
Good stuff @p3rf3ctr00t looking forward to the next one.
Congrats to the Winners.
uSiache chuo ili ukatrade FOREX
uSiache chuo ili ukatrade FOREX
uSiache chuo ili ukatrade FOREX
uSiache chuo ili ukatrade FOREX
uSiache chuo ili ukatrade FOREX
uSiache chuo ili ukatrade FOREX
uSiache chuo ili ukatrade FOREX 🫵🏾
#MadiniYaGaby
The countdown is on! Get your CTF arsenal ready and sharpen your skills—UrchinSec Aware CTF is just around the corner. This is your chance to showcase your talent, solve challenging puzzles, and compete against some of the best.
📆 6 days to go
Register at https://t.co/0rbplbToTM
A new module, that combines all the popular coercion techniques, has just been merged: coerce_plus🚀
The following techniques are available:
- DFSCoerce
- PetitPotam
- Printerbug
- ShadowCoerce
- MSEven
Thanks to @lodos2005 for the work, now you can coerce all servers at once🔥