Today I was laid off from Red Canary due to a 15% reduction in force. It sucks but I’m looking for my next position.
If you know of any roles I’d be a good fit for, please let me know! Thanks for all the support. Much ❤️
#opentowork#infosec
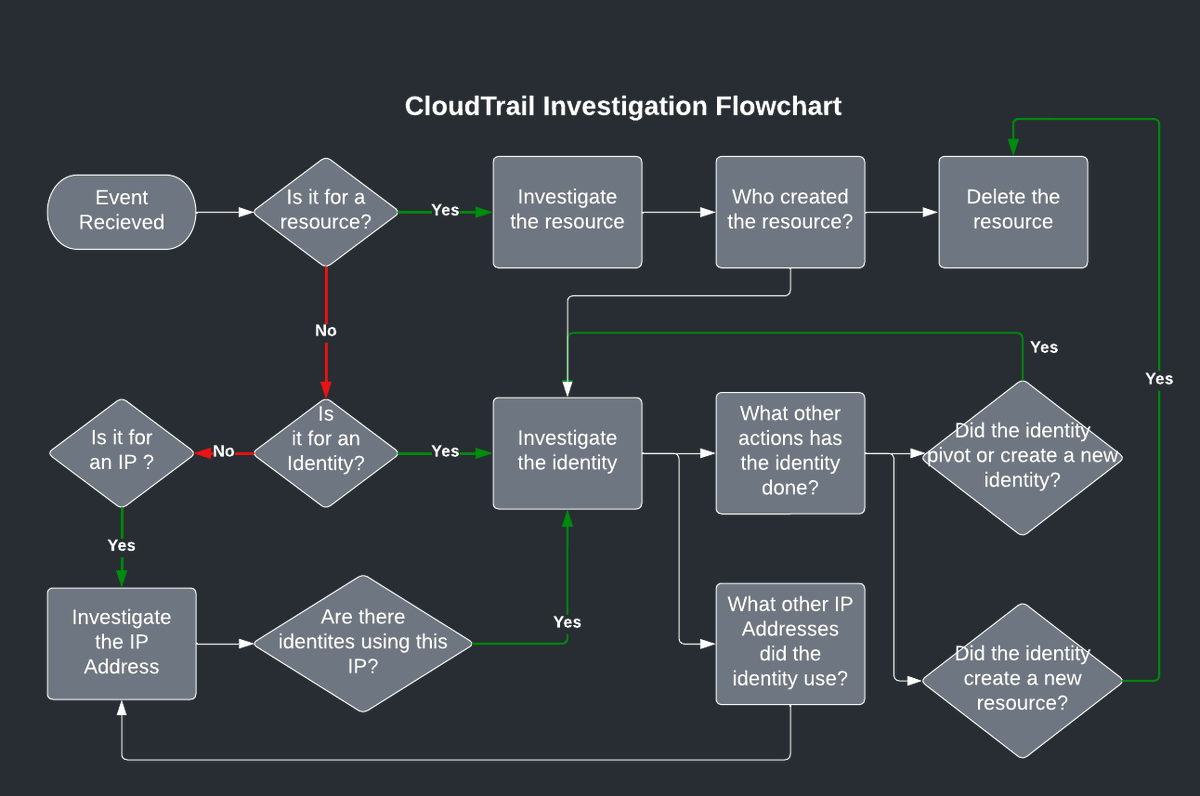
☁️ Incident Response in AWS
@jcfarris on prep to do before an incident so you can respond well, building detections, investigations, containment, and eradication
https://t.co/xyL0ynRJcD
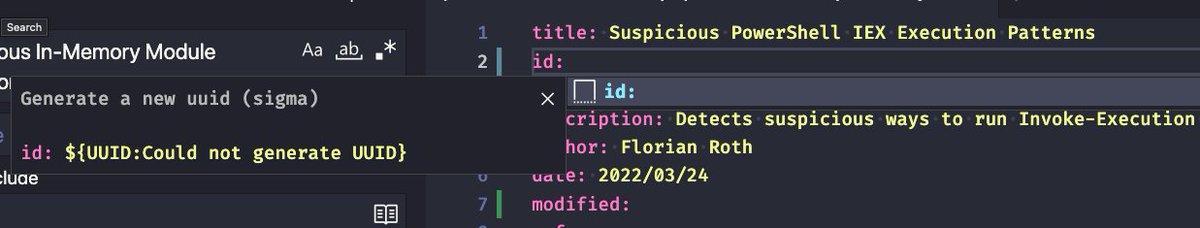
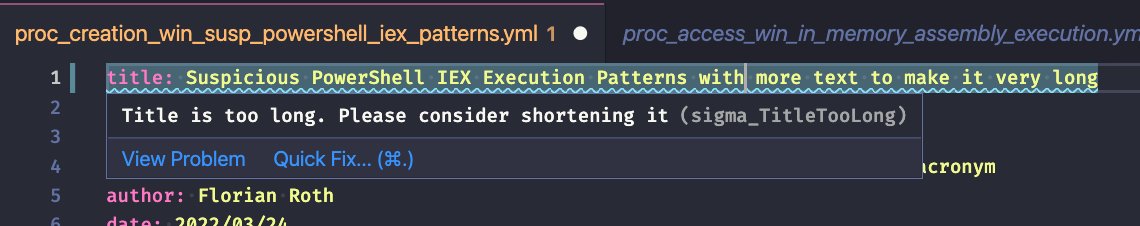
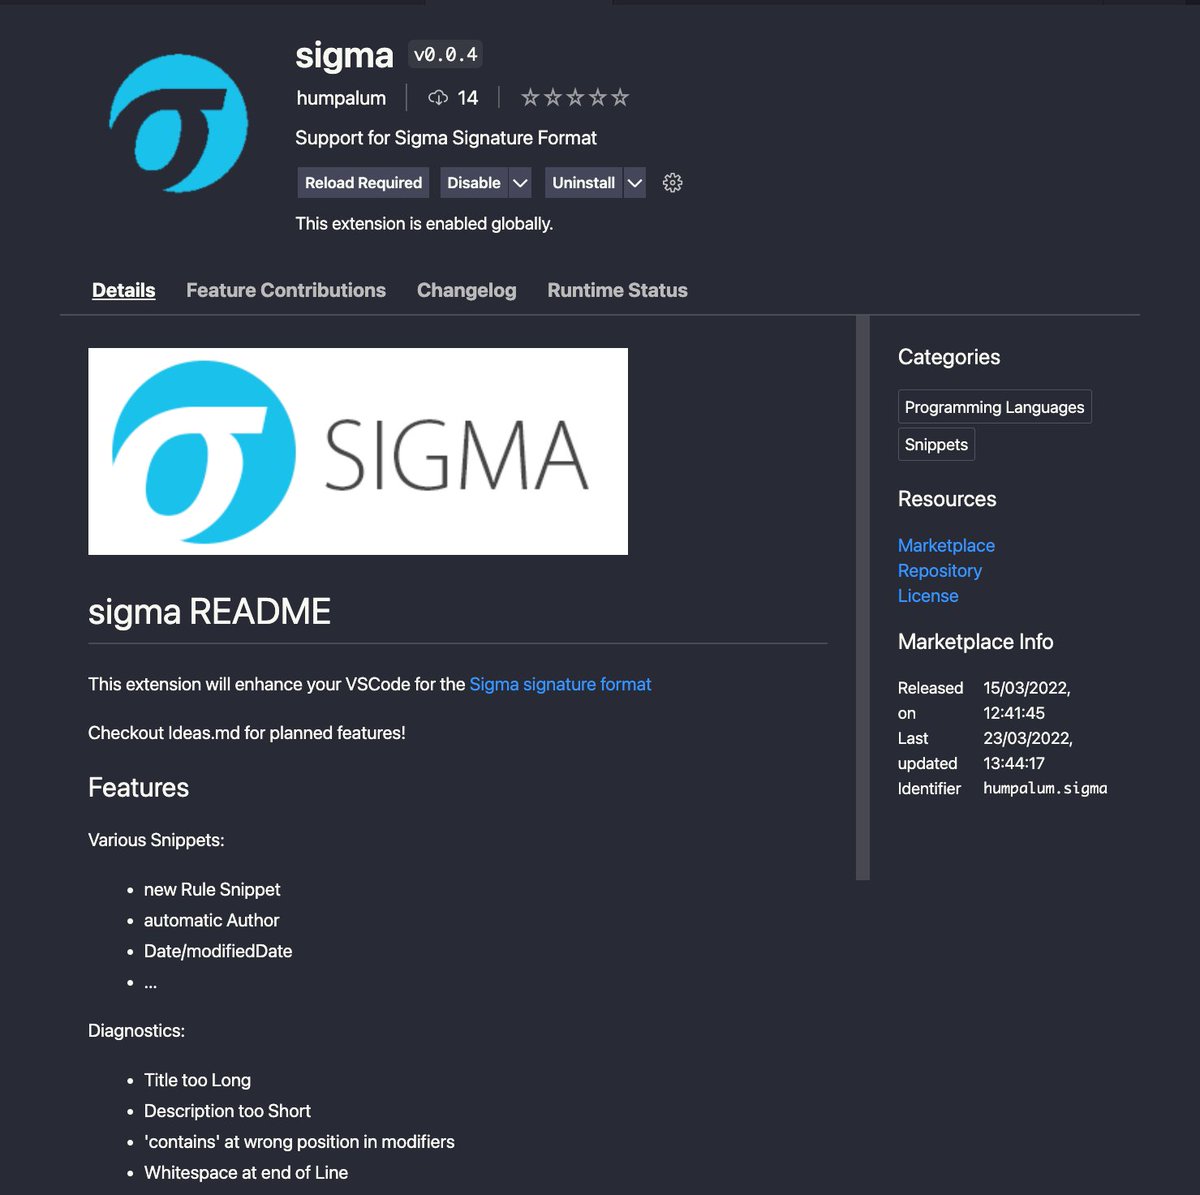
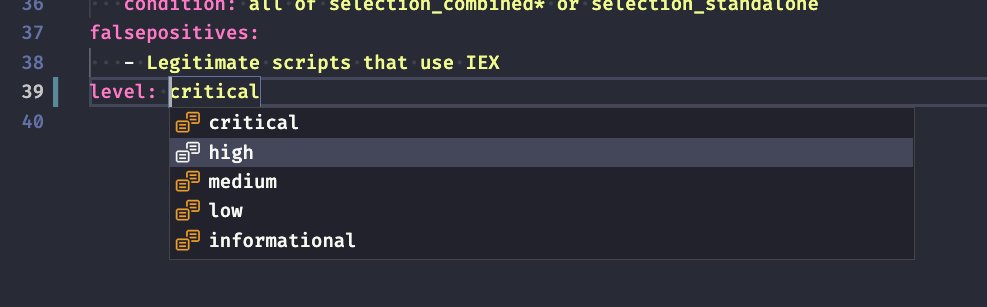
.@_humpalum from my team created a @sigma_hq extension for VS Code
It's in an early stage but already pretty useful and we've already discussed the cool functions and snippets that he's going to add
#Sigma#VSCode
https://t.co/qwN2owJ4Ca
Hundreds of security researchers have used our VSCode-ATT&CK plug-in to access the @MITREattack framework from the comfort of their code editor. Here are some new features that have been added to the tool over the last few months. (1/5) https://t.co/upy3D9JqIN
#DFIR. Know yourself. Know your system32. Enrich your process data with xCyclopedia! The machine-readable encyclopedia for executables. It’s free and open source. https://t.co/QM86PsVrfC. #hunt#lolbas#lolbin
Going to try and share a bit more on this #conti leak. I haven't seen much regarding the .cna released for #cobaltstrike. tldr; it's huge. I'll share more as I click buttons. 🧵
conti.cna
https://t.co/hltHSOCtBD
My team is hiring a Senior Intelligence Analyst! 🙂 Please check out the job description and apply if you're interested. Note that the preferred qualifications are **not required**! https://t.co/TwWQi8UHCt
You see a weird openssl command running on one of your Linux systems. Here's how to investigate whether it's a bindshell backdoor operating on the box and hiding traffic inside an encrypted tunnel. Thread. #DFIR
Introducing VSCode-ATT&CK, a new open source plug-in that lets you query the @MITREattack framework without clicking out of your code editor. https://t.co/2G3ijx6SIR
Our new Shell Activities functionality offers admins a single view of all shell commands run across all workloads that are managed by Red Canary CWP. https://t.co/6164VmKXXX
In part 2 of our blog series on Process Memory Integrity, we take look at how analysts can use PMI techniques to detect fileless or obfuscated malware on Linux systems. https://t.co/9tnxUxQMDY
Since elderly and citizens with health risks are scared to go into stores for groceries, I decided to do something about it in Lake Charles, LA. I started the all volunteer Cajun Grocery Army. Check out the news interview: https://t.co/sAlLztFMq9. #COVID19#volunteer
Starting April 6th, SpecterOps will be presenting a week of webinars while we collectively work from home in response to Covid-19. Each day is a different 30 minute talk given by one of our experts from our Adversary Simulation, Detection, and Adversary Resilience teams.