He who fights with cybers should be careful lest he thereby become a cyber. And if thou gaze long into the cybers, the cybers will also gaze into thee.
Using the existence of a side-channel attack pathway with incredibly low bitrate and requiring two compromised computers to be defeatist about airgaps is peak AI academic security-expert-larping
Using the existence of a side-channel attack pathway with incredibly low bitrate and requiring two compromised computers to be defeatist about airgaps is peak AI academic security-expert-larping
💥🌊BREAKING: The first naval battle in history between two unmanned surface vessels has taken place in the Black Sea.
A Ukrainian Navy Sargan 3000 USV, armed with a 12.7 mm Protector RWS, engaged and destroyed a Russian naval drone.
The engagement marks the first known combat between two uncrewed naval vessels at sea.
I recently went through a translation of Musashi’s Book of Five Rings.
The introduction chronicled the evolution of swordsmanship and martial arts in general from pragmatic battlefield necessities to sports, historical curiosities, and hobbies. It was interesting to hear how in the post-WW2 occupation when martial arts were banned, Judo was represented as equivalent to western wrestling, and Kendo later to western fencing.
The poignant undercurrent for me is that I can see many programming skills following that path.
There are probably dozens of people reading this that remember hand assembling opcodes to hex and still have some magic numbers burned into their memory, but even the small group of people still programming in assembly today (hey, @FFmpeg !) don’t work at that primitive level now.
AI is making many other programming skills much less critical. We aren’t there yet, but carefully writing code completely by hand is moving from a -jitsu to a -do. Code-do? Codo?
That’s ok! The retro computing scene is delightful, full of people building and exercising old skills for the love of it.
But don’t be the out of touch Kung Fu master, heir to lifetimes of tradition, that gets mauled by an amateur MMA fighter.
Musashi would probably have been pretty enthusiastic about assault rifles.
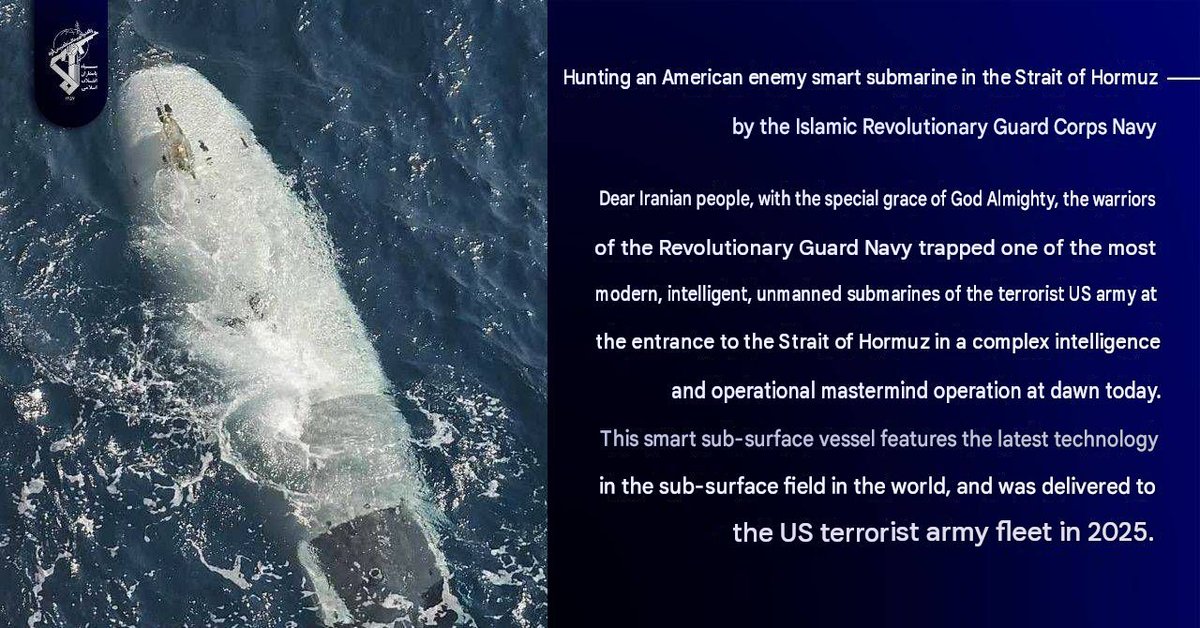
Everyone watching Iran's state-run TV news program probably noticed they picked up an Anduril Dive-LD, our mass-produced attritable submarine.
This particular vehicle has been swimming in CENTCOM for months, successfully operating in support of American forces for thousands of hours. It was explicitly designed to operate in environments too dangerous for humans where capture is an expected possibility. I can't get into the details, but it provided significant value for months before capture.
Rest in peace, little buddy.
This whole op is about to be instantiated as a scalable agentic workflow. (Maybe already is.) Will DoJ have it's own agentic seizures workflow to keep up?
🇺🇸🇨🇳 FBI MOVES TO SEIZE INFRASTRUCTURE LINKED TO CHINESE CYBER OPERATORS
A newly published U.S. Department of Justice court document reveals an FBI investigation into a China-based cyber threat group referred to as “QTFY.”
According to the FBI affidavit, the operators developed and used a vulnerability-scanning and exploitation platform called QScan alongside an IoT-based obfuscation network called QTRouter.
* FBI says QTFY actors are located in the People’s Republic of China
* The affidavit identifies the company behind the activity as Nanjing Xinjiewei Network Technology Co.
* FBI says the operators have relationships with the PLA and conduct malicious cyber activity on behalf of the PRC government
* QScan allegedly automates scanning and exploitation of vulnerable internet-facing devices
* QTRouter allegedly uses compromised IoT devices and proxy infrastructure to conceal the operators’ real IP addresses
* QTFY allegedly sold access to QScan and QTRouter to other customers
🎯 TARGETING
According to the FBI, infrastructure associated with QTFY has been used against sensitive networks including:
* NASA
* U.S. Department of Energy
* Department of Justice
* Department of Health and Human Services
* National Institutes of Health
* Federal Reserve
* Defense contractors
* Telecommunications providers
* Power companies
* Financial institutions
The affidavit says that in September 2024, QTFY actors compromised three DOE National Laboratories, NIH, an HHS agency and a U.S. security-device manufacturer using a zero-day vulnerability affecting Ivanti Cloud Services Appliance.
⚠️ SCALE
The FBI says QScan supported more than 200 proof-of-concept exploits.
During a single day in 2024, QScan allegedly processed more than TWO MILLION scanning/exploitation tasks.
Investigators also allege that exploitation of a Check Point Quantum Gateway vulnerability resulted in sensitive information being stolen from more than 300 organizations in the United States.
🌐 FBI SEIZURE TARGETS
The government sought seizure of:
* https://t.co/xC1JN3tOa5
* https://t.co/kokbGK6k5v
* https://t.co/UOR21xgcoi
The FBI says these domains supported QScan and the QTRouter obfuscation infrastructure.
⚠️ Analyst Note:
This case provides an unusually detailed look inside an alleged state-linked cyber exploitation ecosystem.
The important element isn't simply another botnet.
The FBI describes an operational stack combining automated vulnerability discovery, a large exploit library, compromised IoT infrastructure, residential/commercial proxy services and infrastructure specifically designed to obscure the operators behind attacks.
That effectively creates scalable exploitation infrastructure capable of scanning, compromising and routing attacks against targets worldwide while making attribution considerably more difficult.
Source: U.S. Department of Justice / FBI
Court affidavit filed August 24, 2026:
https://t.co/8qEofDJ2Ki
#DDW #China #CyberEspionage #FBI #DOJ #ThreatIntelligence #CyberSecurity #QTFY
Microsoft threat intel found SVR exploiting WiFi captive-portal ecosystem. It manipulates the shared management infrastructure enabling access. This means one compromise scales to every traveler who touches guest Wi-Fi at hotels, conference centers, and shared venues worldwide.
New test footage: first missile shot from YFQ-44A.
YFQ-44A executed an end-to-end, beyond-line-of-sight strike against a simulated target.
The test, executed out of @EdwardsAFB, represents an important step in turning CCA into an operational capability.
Anduril delivered a month’s worth of Pulsars in less than a week. These systems were immediately deployed in active operations.
Anduril builds with the knowledge that demand will not announce itself in advance. We win by absorbing surges at scale and growing output at speed. This same line once produced 500 Pulsars per year. Now it ships twice as many.
Deterrence is a production problem, and we're focused on the factory to solve it.