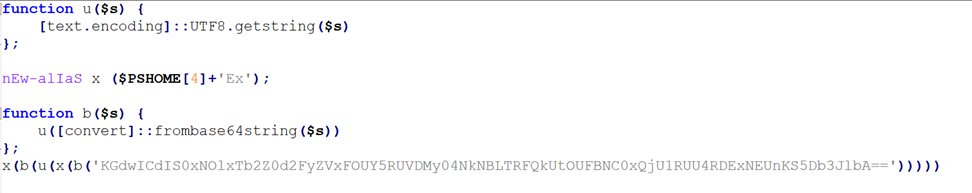
Imagine your #antivirus starts deploying malware after an update. This is exactly what happened with the eScan solution last week - the supply chain attack was discovered by @morphisec. We have analyzed the #malware used in this attack - and found lots of cool stuff! [1/7]
Monero appears to be in the midst of a successful 51% attack.
The privacy-focused blockchain, launched in 2014 and long targeted by governments and 3-letters agencies, is already banned from most major centralized exchanges.
The Qubic mining pool has been amassing hashrate for months and now controls a majority of the network. A major chain reorganization was detected this morning. With its current dominance, Qubic can rewrite the blockchain, enable double-spending, and censor any transaction.
Sustaining this attack is estimated to cost $75 million per day. While potentially lucrative, it threatens to destroy confidence in the network almost overnight. Other miners are left with no incentive to continue, as Qubic can simply orphan any competing blocks, effectively becoming the sole miner.
In effect, a $300 million market-cap chain is taking over a $6 billion one. Monero’s options for recovery are limited, and a full takeover is now possible and even likely.
So far, XMR has dropped only 13%.
Ucrania acaba de dar uno de los golpes mas letales de la guerra a Rusia al destruir a gran parte de la aviación estratégica rusa usada para bombardear sus ciudades. Sucedió horas atrás en la base de Olenya, óblast de Múrmansk, a 1800 km de Ucrania. Hay mas bases atacadas
Acabo de terminar de leer el informe oficial del Ministerio del Interior francés sobre los Hermanos Musulmanes.
Es una chapa de 84 páginas densas, técnicas y cargadas de información.
Ya que me lo he leído entero, voy a traducir los puntos clave, desglosarlo y explicar lo que dice lo mejor que pueda.
⬇️
I analyzed thousands of messages from 35+ suspected state-sponsored hacktivist groups using machine learning—uncovering hidden connections through writing styles, language and topics.
After a year of research, here’s what we found and how we did it. 👇
https://t.co/KUnIhAmuRa
1/
Vamos a repasar el secuestro del español en Argelia porque es de las cosas más estrafalaria que he visto en los últimos meses.
Disponemos de poca información, contradictoria en ocasiones y bastante surrealista. Va hilo🧵
La guerra de quinta generación es una acción militar no cinética basada en datos diseñada para aprovechar los sesgos cognitivos existentes y crear otros nuevos: la manipulación deliberada del contexto de un observador para lograr un resultado deseado
@wish_or_truth@psyacademy_
La radio pública estadounidense ha accedido a documentos internos de tiktok por un fallo de instrucción legal:
- Calculan que se tardan 260 videos en engancharse a tiktok (unos 35 minutos)
- El algoritmo amplifica a la gente guapa
(sigo)
https://t.co/1FQnju5RYc
The exploding Hezbollah pagers situation is an incredibly impressive supply chain attack by Israel (most likely). I am sure more details will come, but there are already some educated guesses to be made that narrow it down.
🧵1/n
📡📟🇱🇧
Here’s what we know:
• Israel likely planned this operation far in advance, in line with some of their most innovative actions this year.
• Evidence suggests Israel distributed pagers to Hezbollah members as part of a social engineering operation, with the devices entering circulation 3 months ago. Unconfirmed reports say many Americans replaced their pagers just two weeks ago, likely after receiving a tip off.
• Israel likely ensured operational security by distributing the compromised pagers to friendly individuals as well, with the plan to have theirs replaced weeks before the operation.
• The fact that Americans working in hospitals also received compromised devices suggests it was likely not an explosive device, as that would endanger innocent lives.
Instead, it may have been a device with exploitable electronics or batteries. If it were explosive, Israel likely knew these devices couldn't accidentally detonate. No reports of exploding pagers occurred in the last 3 months.
• Between 1,200 and 2,500 people have been reported wounded, with hundreds in critical condition.
• The attack occurred within 20 hours of the first USAF EC-130H Compass Call flight since October 2023. This aircraft has the capability to hack into wireless devices.
• This could be a preparatory strike aimed at weakening the enemy before a larger operation unfolds.
I don't do Windows but here are some (initial) details about why the CrowdStrike's CSAgent.sys crashed
Faulting inst: mov r9d, [r8]
R8: unmapped address
...taken from an array of pointers (held in RAX), index RDX (0x14 * 0x8) holds the invalid memory address
@_JohnHammond
Just throwing this out there:
https://t.co/oHsMJFTYlS
Around 2 years ago i got access to a pc with crowdstrike first time.
I quickly discovered that the minifilter did not catch when open file only with append access
-> This is also available to anyone that can trigger an XSS on any *.google.com site
Note that chrome.runtime is generally only available from within Chrome extension, the reason it's available in this case & why you won't see the Google Hangout extension listed under chrome://extensions is because of a few things:
- The Google Hangout extension is a "component extension", i.e. it's built-in and bundled with any Chromium based browser that has not explicitly removed it
- The manifest for the Google Hangout extension is using the "externally_connectable" key & matching https://*.google.com/
It has a number of interesting permissions enabled, such as system.cpu, desktopCapture, processes and webrtc related ones
For reference:
https://t.co/VjvqiTmHTV
Chrome extensions that are "externally connectable" will expose the chrome.runtime.sendMessage function that is normally only available to extensions
When the function is used from sites matching the "matches" section of the "externally_connectable" key in the manifest, the messages will be handled by chrome.runtime.onMessageExternal event listeners within the extensions service worker
This function is defined here:
https://t.co/Ps6PUnSsSt
As you can see, besides "cpu.getInfo" it also allows for starting/stopping WebRTC logging & to upload the collected logs. There's definitely some potentially interesting attack surface here
PS. In general, any Chrome extension defined as "externally connectable" & with chrome.runtime.onMessageExternal event listeners is something to take a closer look at... And of course, especially in cases when the extension is bundled with chromium by default as a "component extension" :P
Blogged about Chrome's strategy for authentication in HTTPS in a post-quantum world, given that post-quantum cryptography is considerably larger on the wire than traditional asymmetric cryptography https://t.co/kE30Van9OF
La irrupción de la policía en la embajada de México en Quito sin consentimiento violaría principios fundamentales del derecho internacional, específicamente la Convención de Viena sobre Relaciones Diplomáticas de 1961.
Esta convención establece la inviolabilidad de las misiones diplomáticas, considerando sus instalaciones como territorio soberano del estado representado, no del país anfitrión. Una acción así provocaría una grave tensión diplomática, al infringir la soberanía del país que la embajada representa.
La extraterritorialidad de las embajadas asegura que solo pueden ser ingresadas con permiso del jefe de la misión. Por tanto, cualquier entrada no autorizada por las fuerzas del país anfitrión se considera un acto de agresión y una violación grave de los tratados internacionales.
En conclusión, bajo el derecho internacional, la policía no tiene la autoridad para irrumpir en una embajada sin la aprobación explícita de su liderazgo diplomático.
Visita nuestro perfil, lee nuestra bio y si te identificas, síguenos!
Inicia otra ronda de patrocinios y te traemos a los gigantes 🪙@QuoIntelligence🔙: el dream team contra riesgos cibernéticos y geopolíticos. 🧭Inteligencia de élite, informes custom para decisiones sólidas, seguridad 🔒 y anticipación a amenazas. Info ➡️ https://t.co/0eaOREixRi
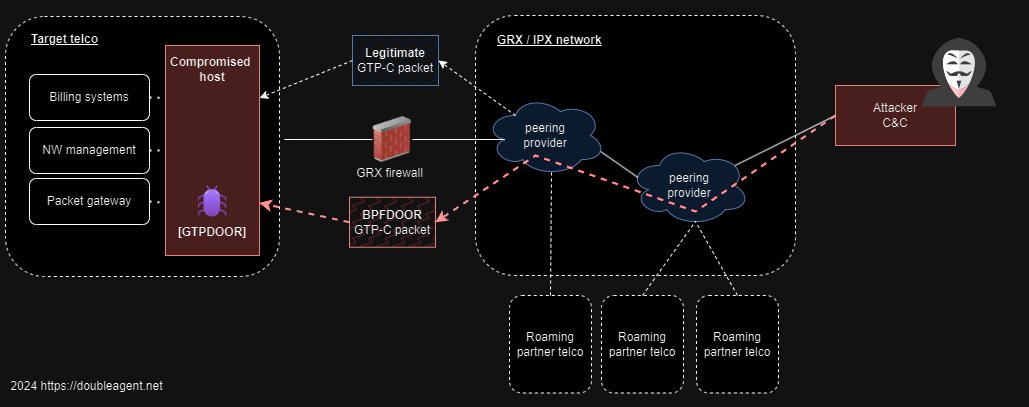
I recently found two very interesting Linux binaries uploaded to Virustotal.
I call this malware 'GTPDOOR'.
GTPDOOR is a 'magic/wakeup' packet backdoor that uses a novel C2 transport protocol: GTP (GPRS Tunnelling Protocol), silently listening on the GRX network (1/n) 🧵