As a hacker / security researcher (pick ur title), if you feel a desire / want / need to help the Ohana in Maui @Hacker0x01 has temporarily hooked u up - https://t.co/rZzXMjBdDU Thank you H1
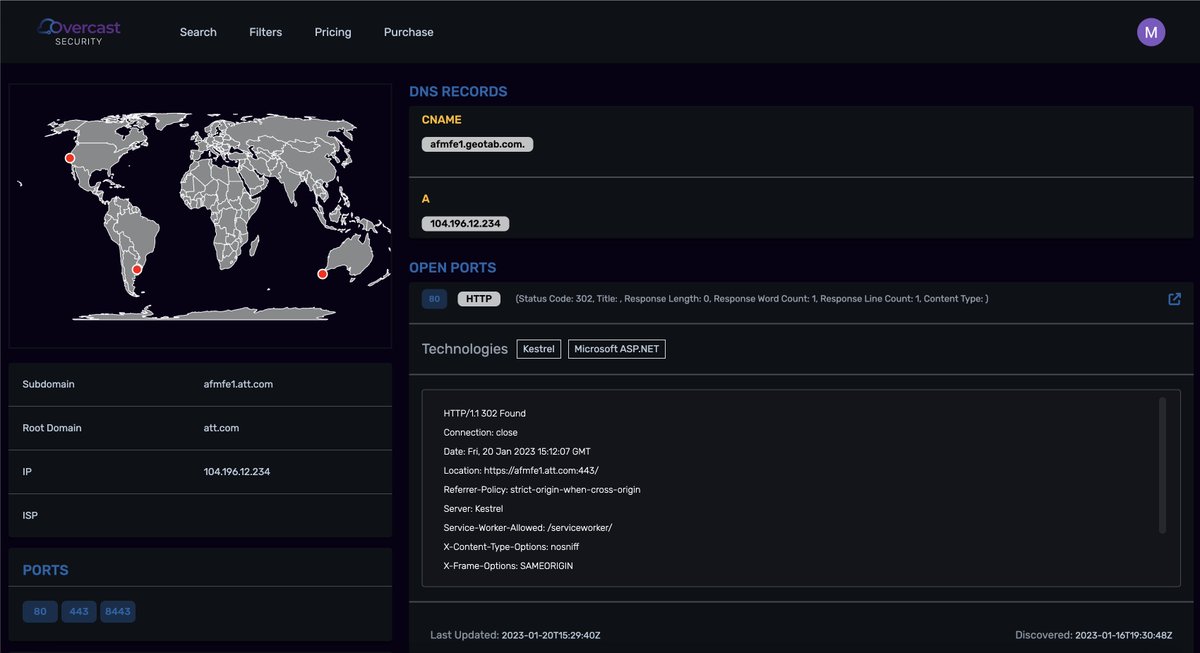
Really excited to release the Bug Bounty Attack Surface Search Engine that the Overcast team have been working on. The goal is to provide the ability for hunters to approach their favourite programs and filter out the data they need with easy to use filter queries.
New blog post on a recent collab with @UsmanMansha420 where I bypassed Akamai WAF to get RCE on a Java application with Spring EL injection. Spent some time writing about the process of constructing the custom payload. Hope you enjoy! https://t.co/hsuRmM3fx6
I got permission to repost this from 🔒 @TheXcellerator (follow them)
Almost a #BGGP3 entry: Remote Code Execution on a GameBoy Colour 22 years later with the Mobile Adapter GB: https://t.co/YCXYSpI78E Was a tonne of fun figuring out and my first time screwing with GameBoy stuff
Successfully reproduced the Gitlab Project Import RCE (CVE-2022-2185)
Got headache while reading Ruby for last 2 weeks, but it worth definitely digging in
Have good read!
https://t.co/MDWcIMfxTh
💥 New attack! Our researcher Arseniy Sharoglazov discovered a PHP's Arbitrary Object Instantiation with no user-defined classes. It was turned to RCE!
Read the research: https://t.co/PJZHLRM8xq
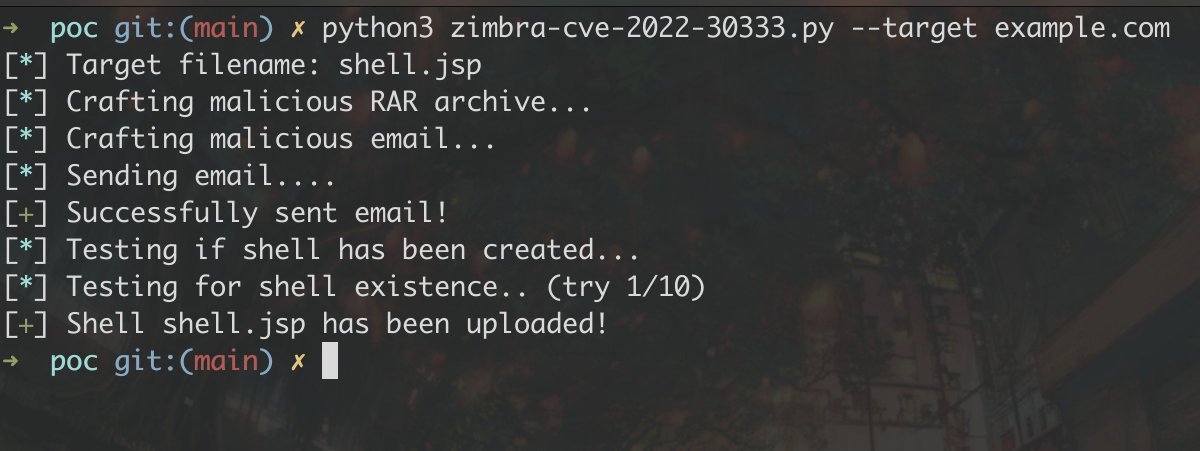
⚠️ Zimbra Mail pre-auth RCE via Path Traversal bug in unrar (CVE-2022-30333). This is probably my most impactful bug so far, especially after Zimbra has been the target of a 0day campaign likely conducted by a state actor. More details in this blog post: https://t.co/8v0ujC1Nyl
Today, we are dropping this repo
https://t.co/sV94Jz1CxQ
Basically all the bugs in the repo are either ignored or not fixed at all even after vendors acknowledged
We hope we will not need to drop in the future
Today's bugs are brought to you by
@daniellimws
Bypassing .NET Serialization Binders: case studies for DevExpress (CVE-2022-28684) and Microsoft Exchange (CVE-2022-23277) by @mwulftange https://t.co/G90Qg7gQ9m
From SQLi to RCE - as root! Grab a glass of Pinot and read all about the amazing new @viiiSR research from the @Doyensec team!
https://t.co/lA07u1n7MX
#AppSec#Doyensec